
drAFL
 mxmssh/drafl
AFL + DynamoRIO = fuzzing binaries with no source code on Linux
binary-analysisdynamic-analysis-sandboxingexploitation+1
mxmssh/draflAFL + DynamoRIO = fuzzing binaries with no source code on Linux
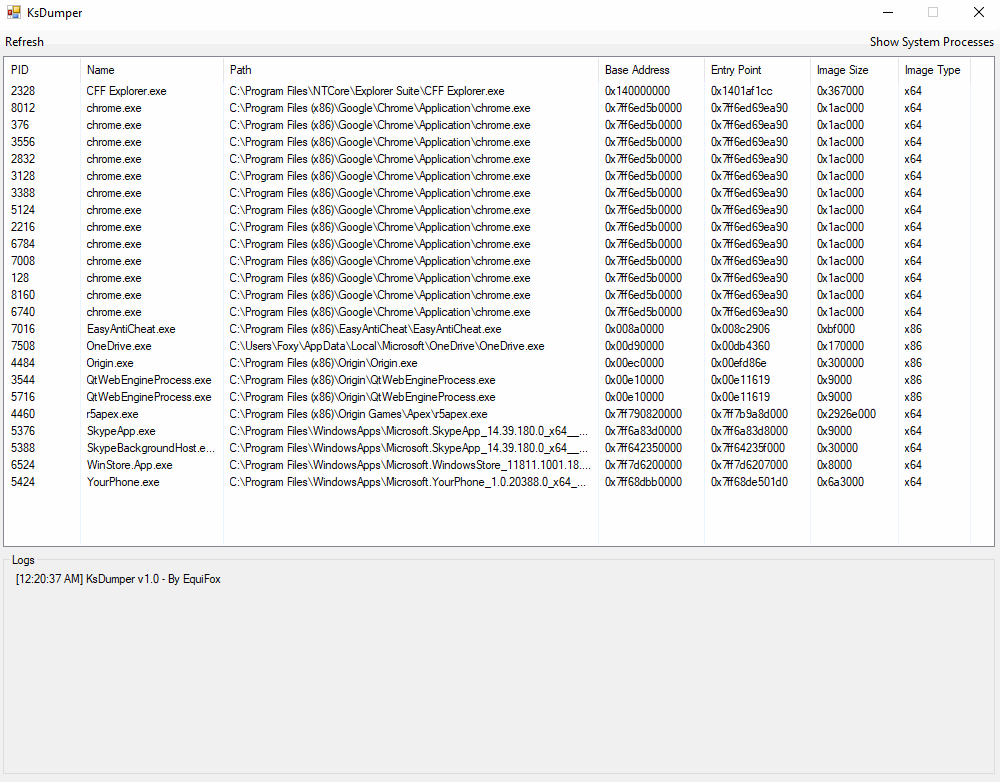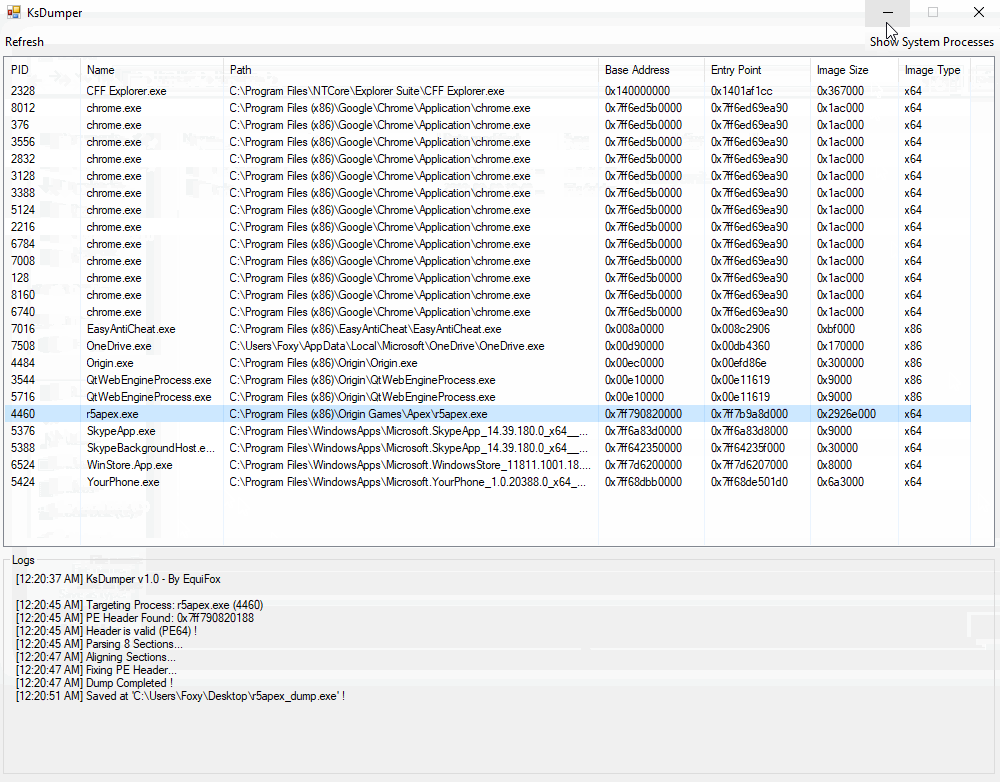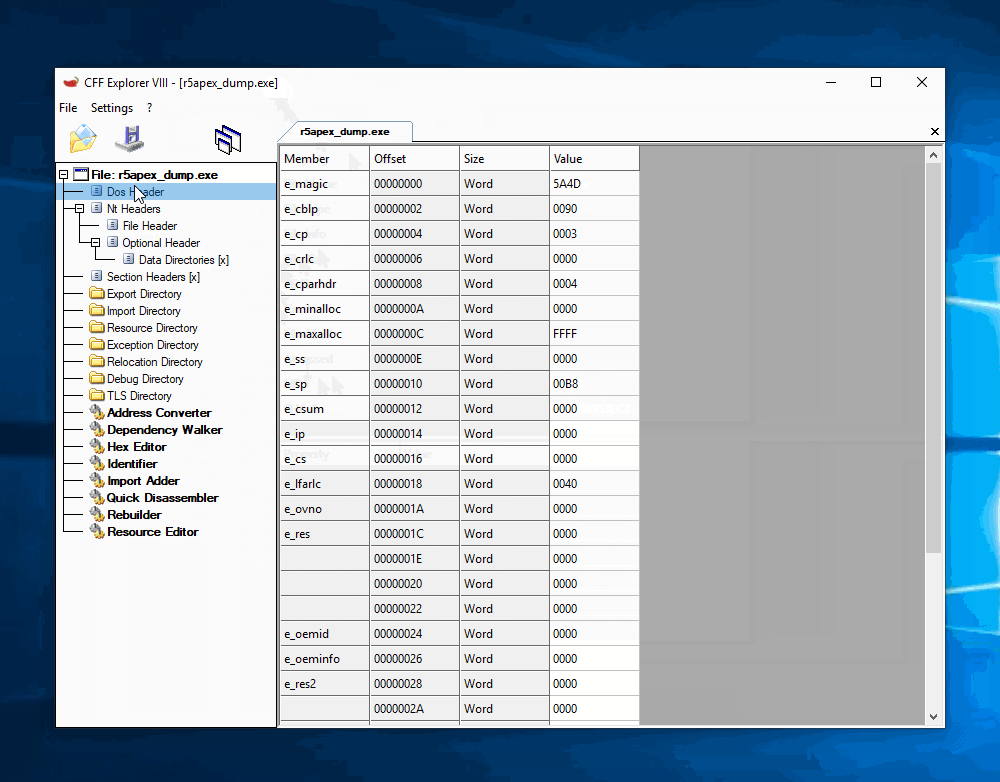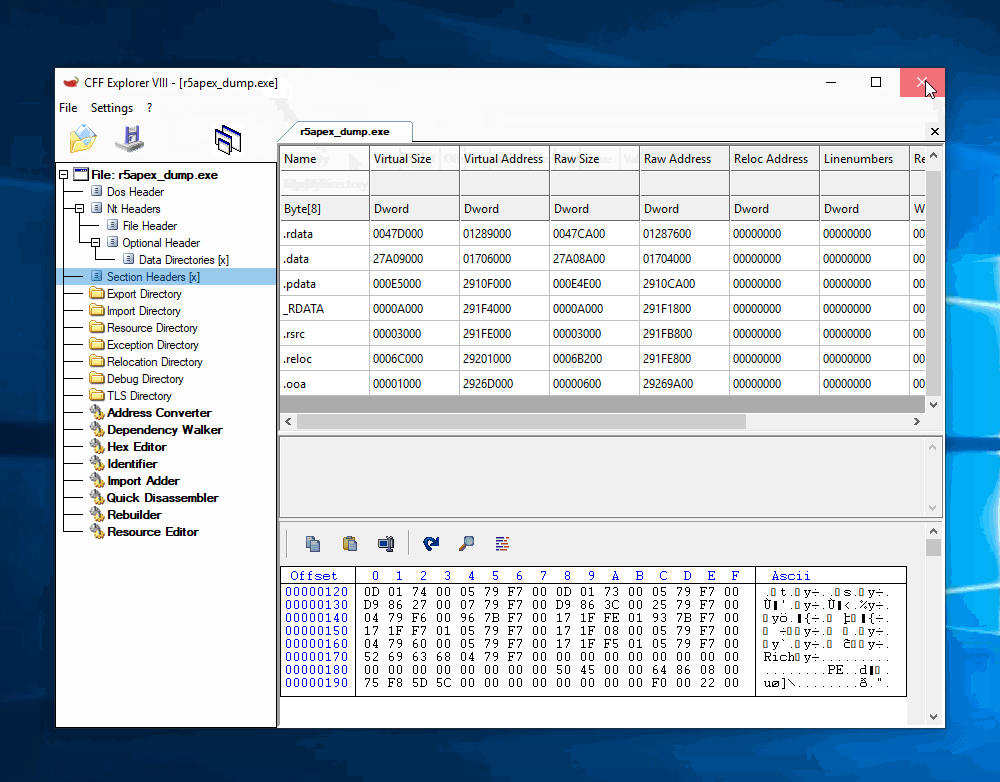 equifox/ksdumper
Dumping processes using the power of kernel space !
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
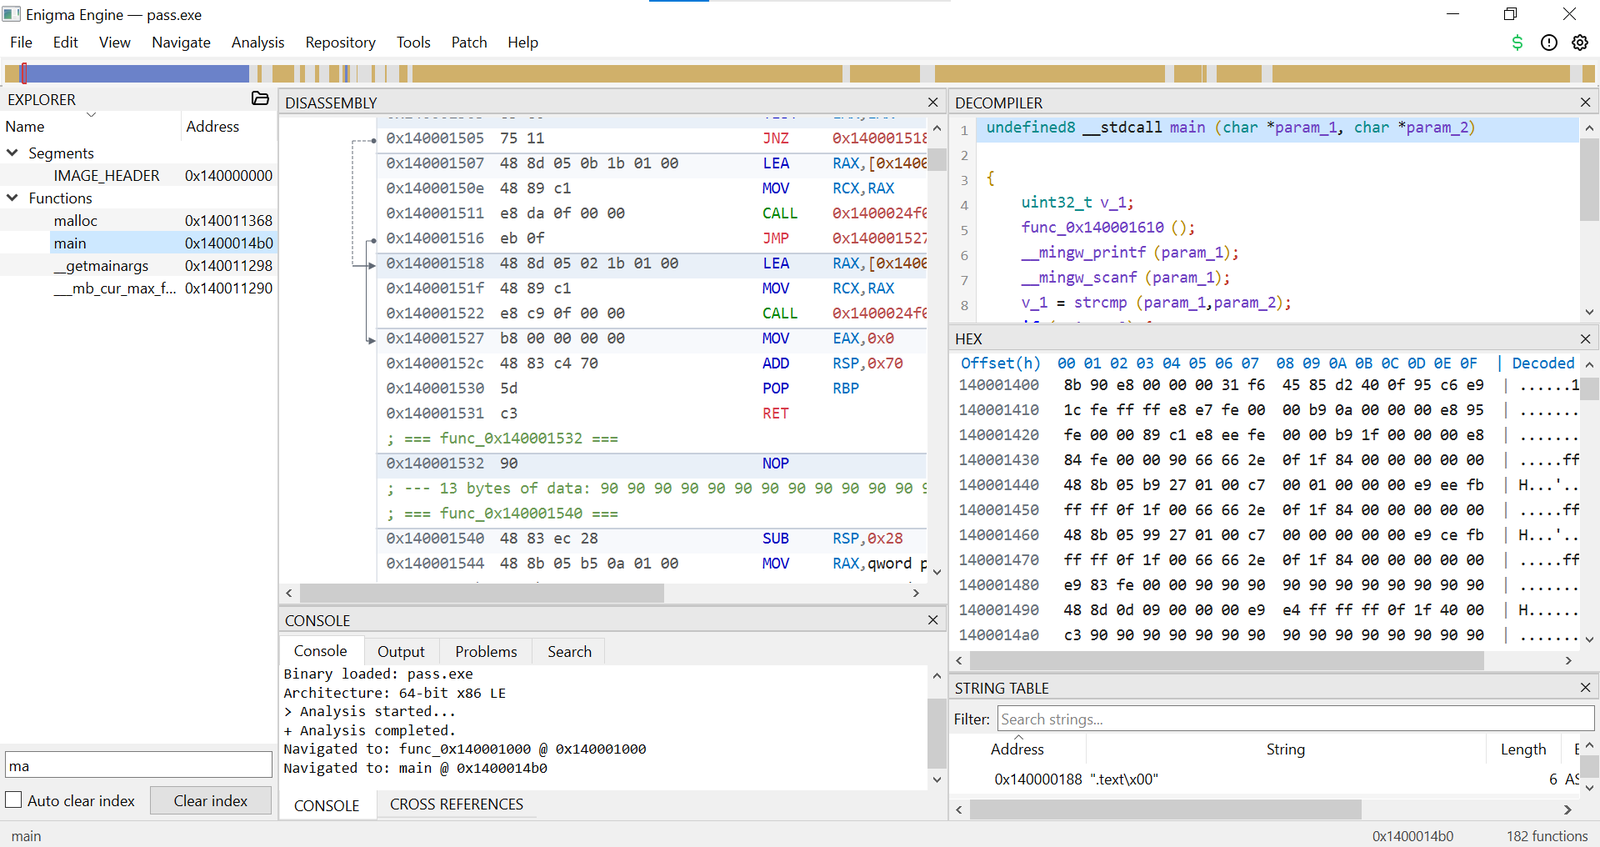 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
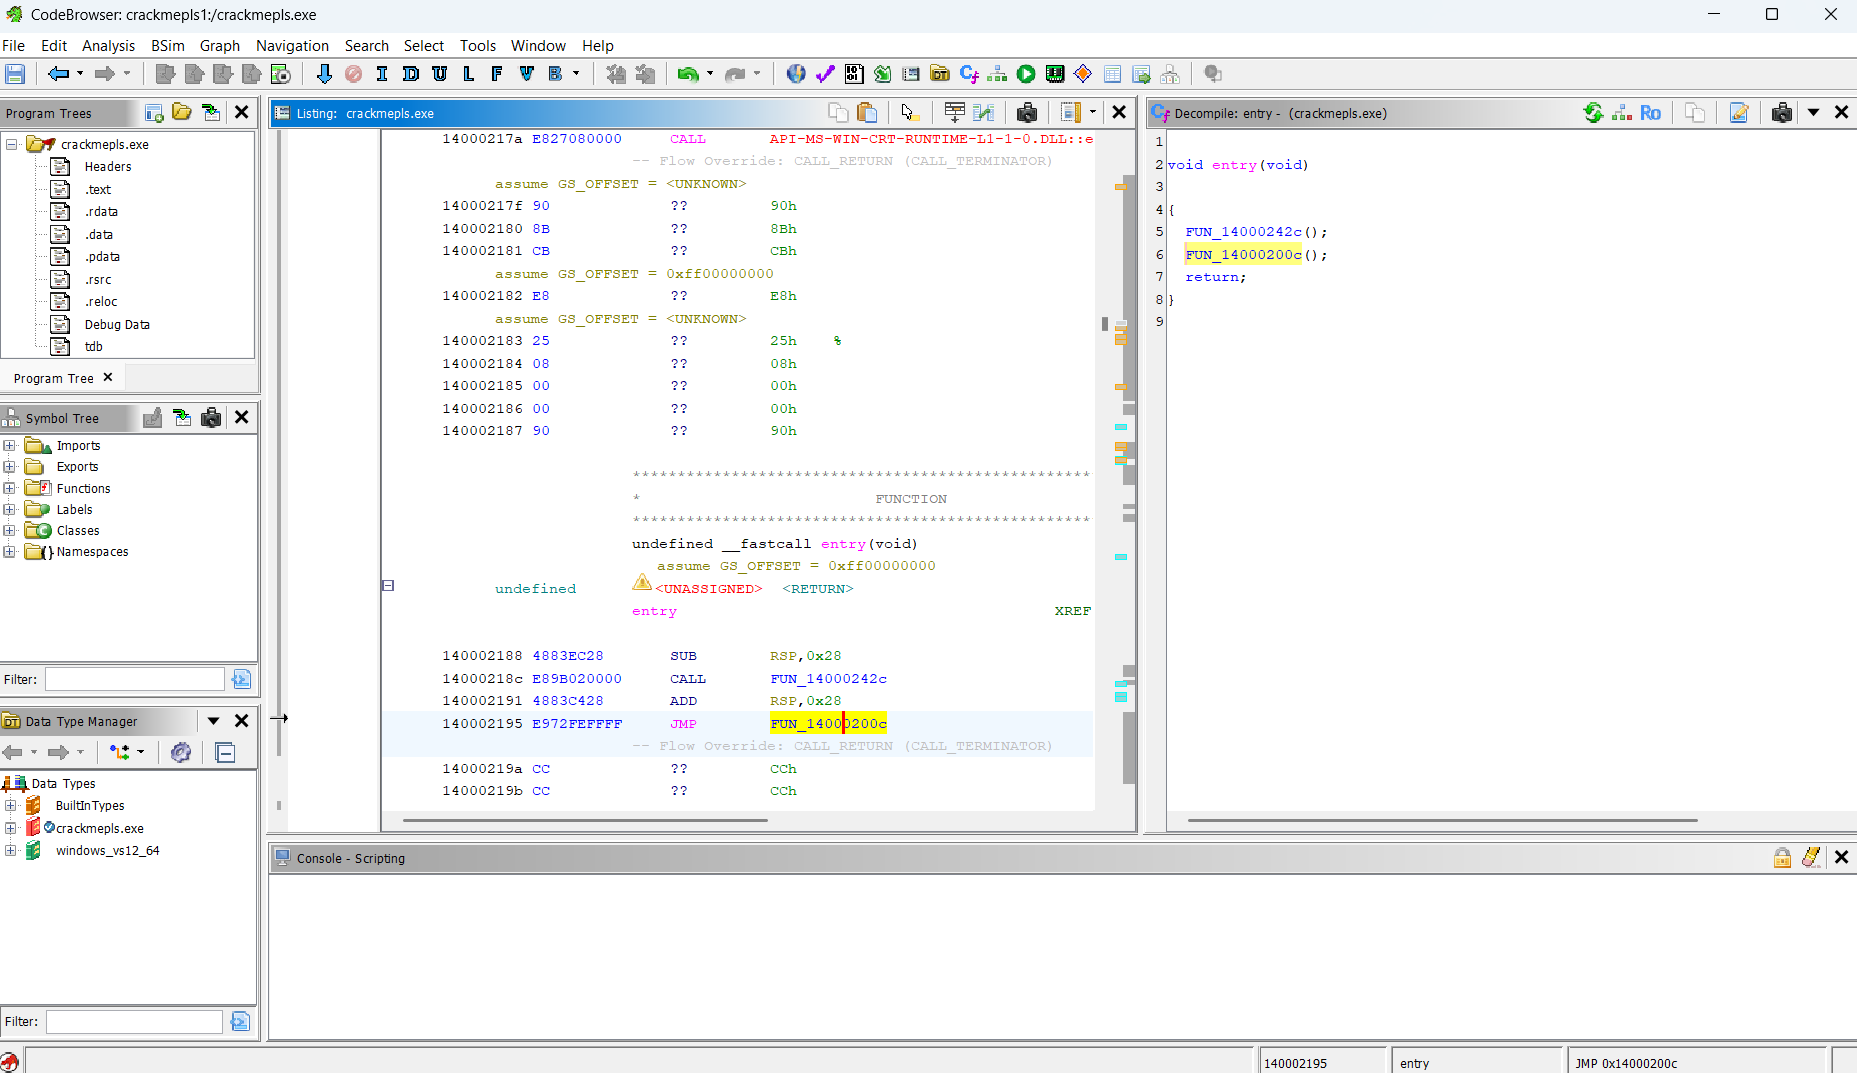 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
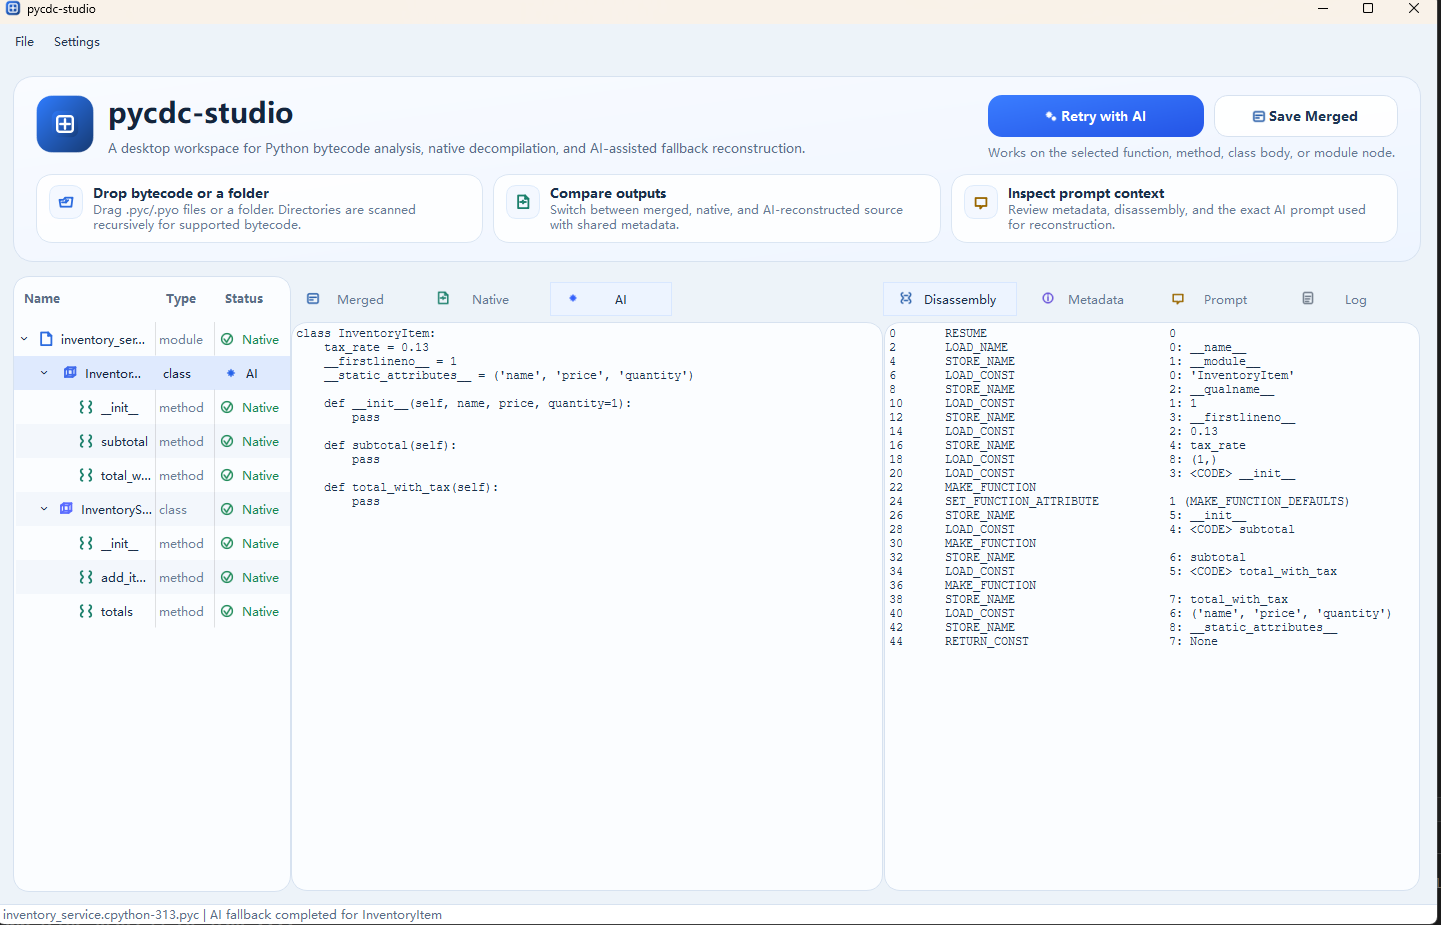 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
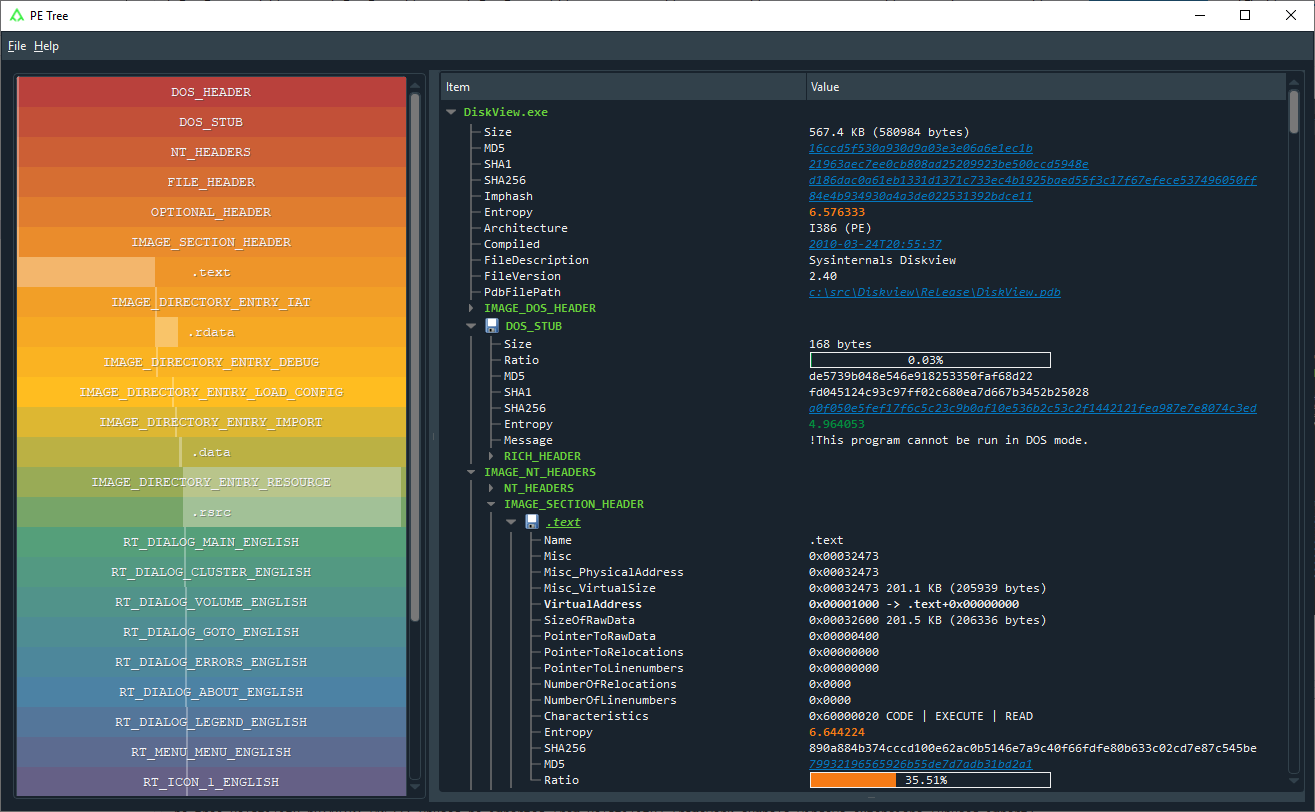 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C