
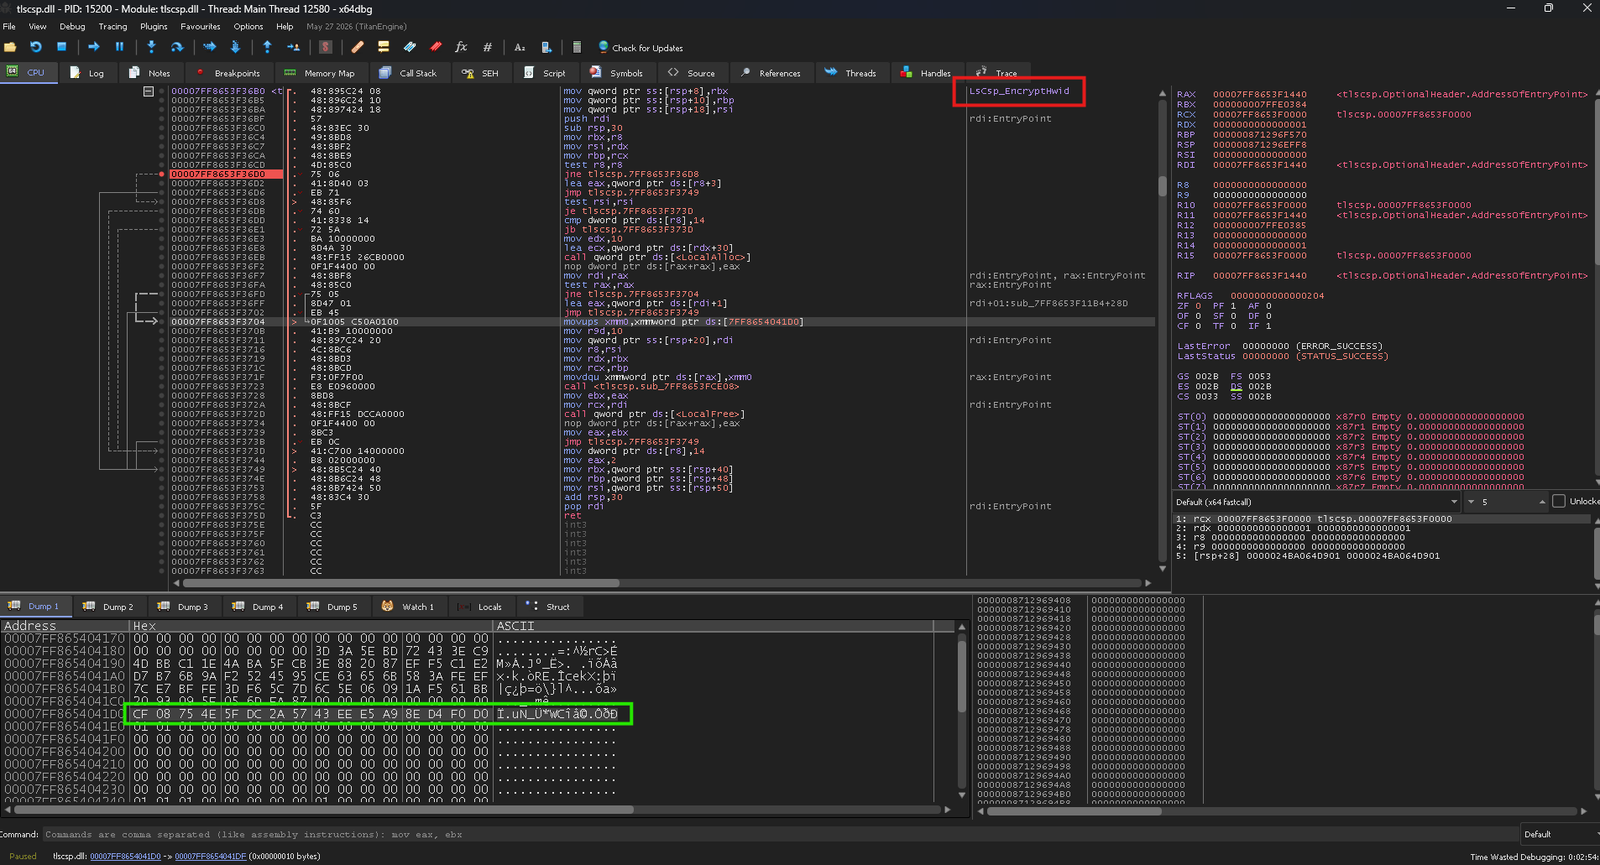
RC4Decryption
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
37
weedhashpeddler/rc4decryptionAbuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
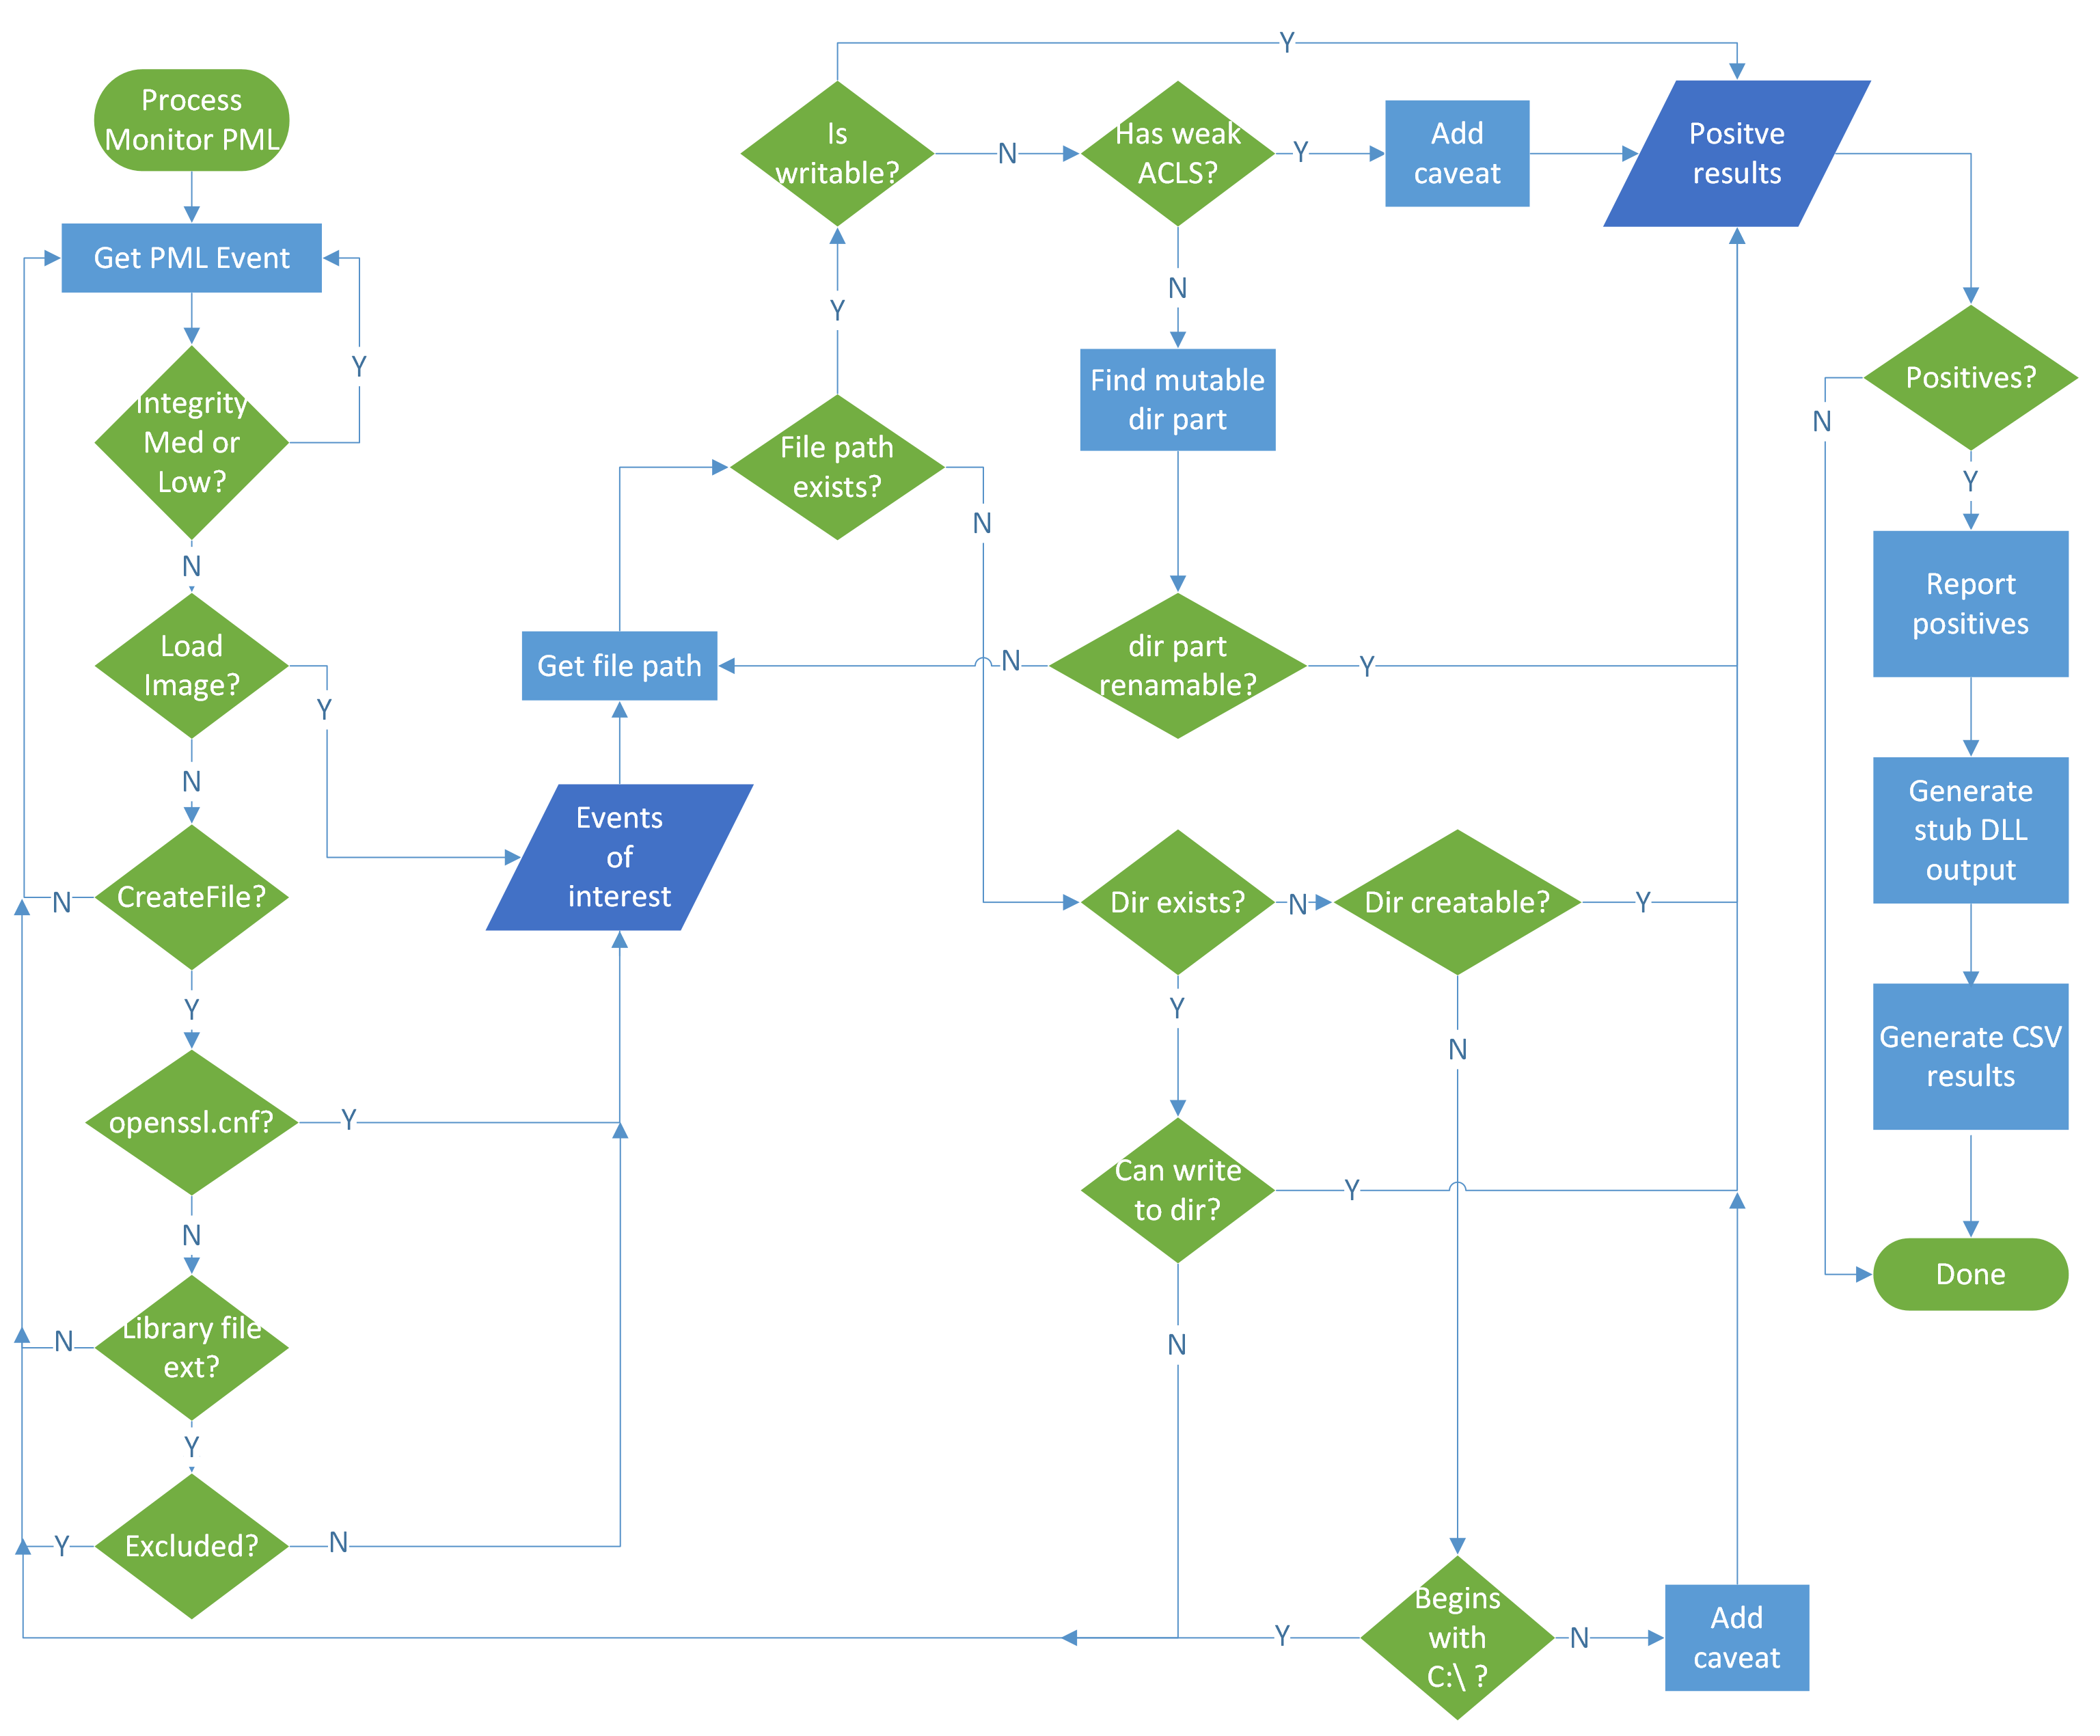 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
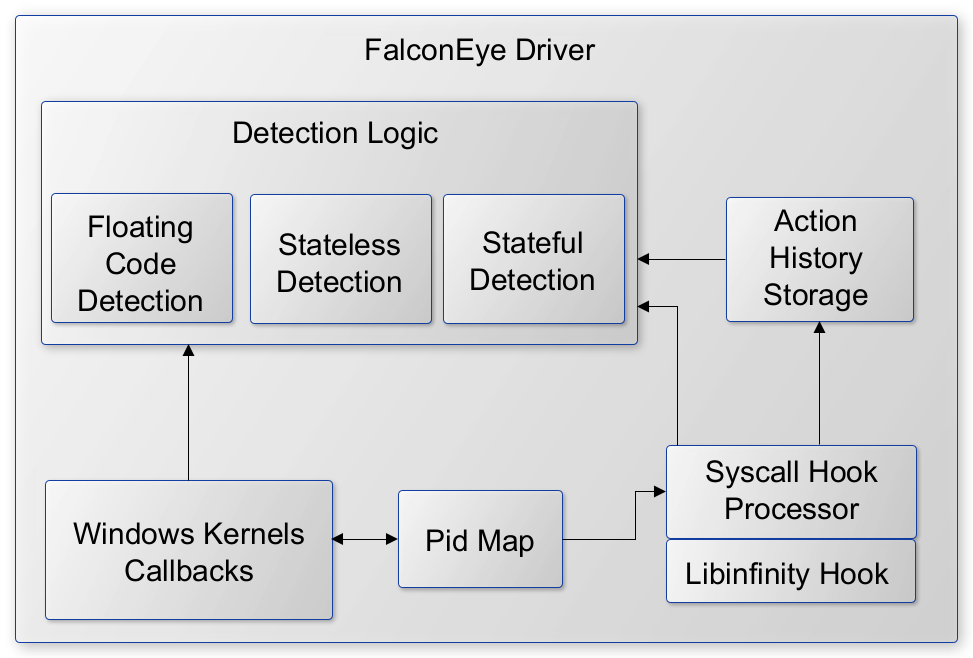 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
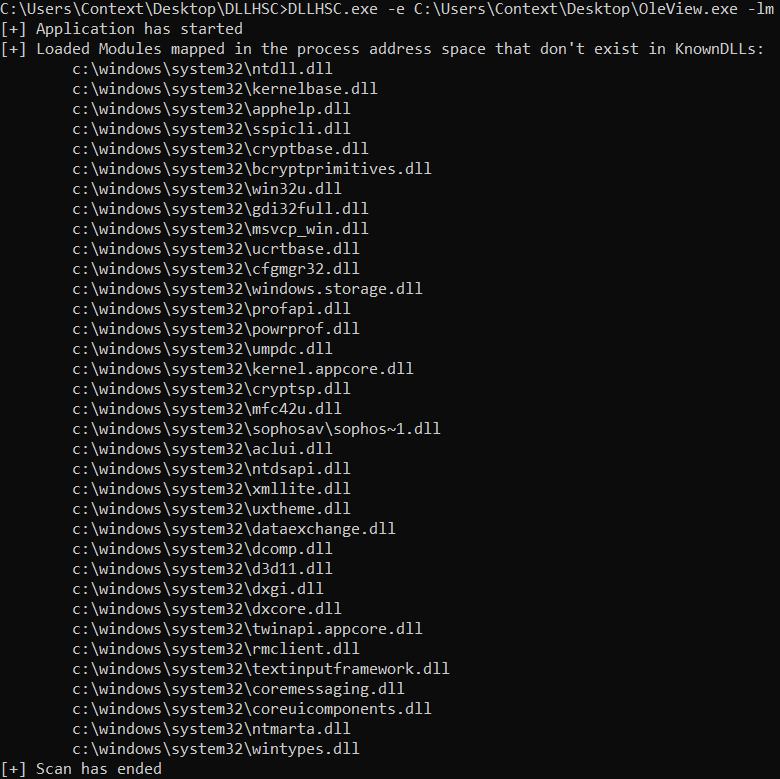 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
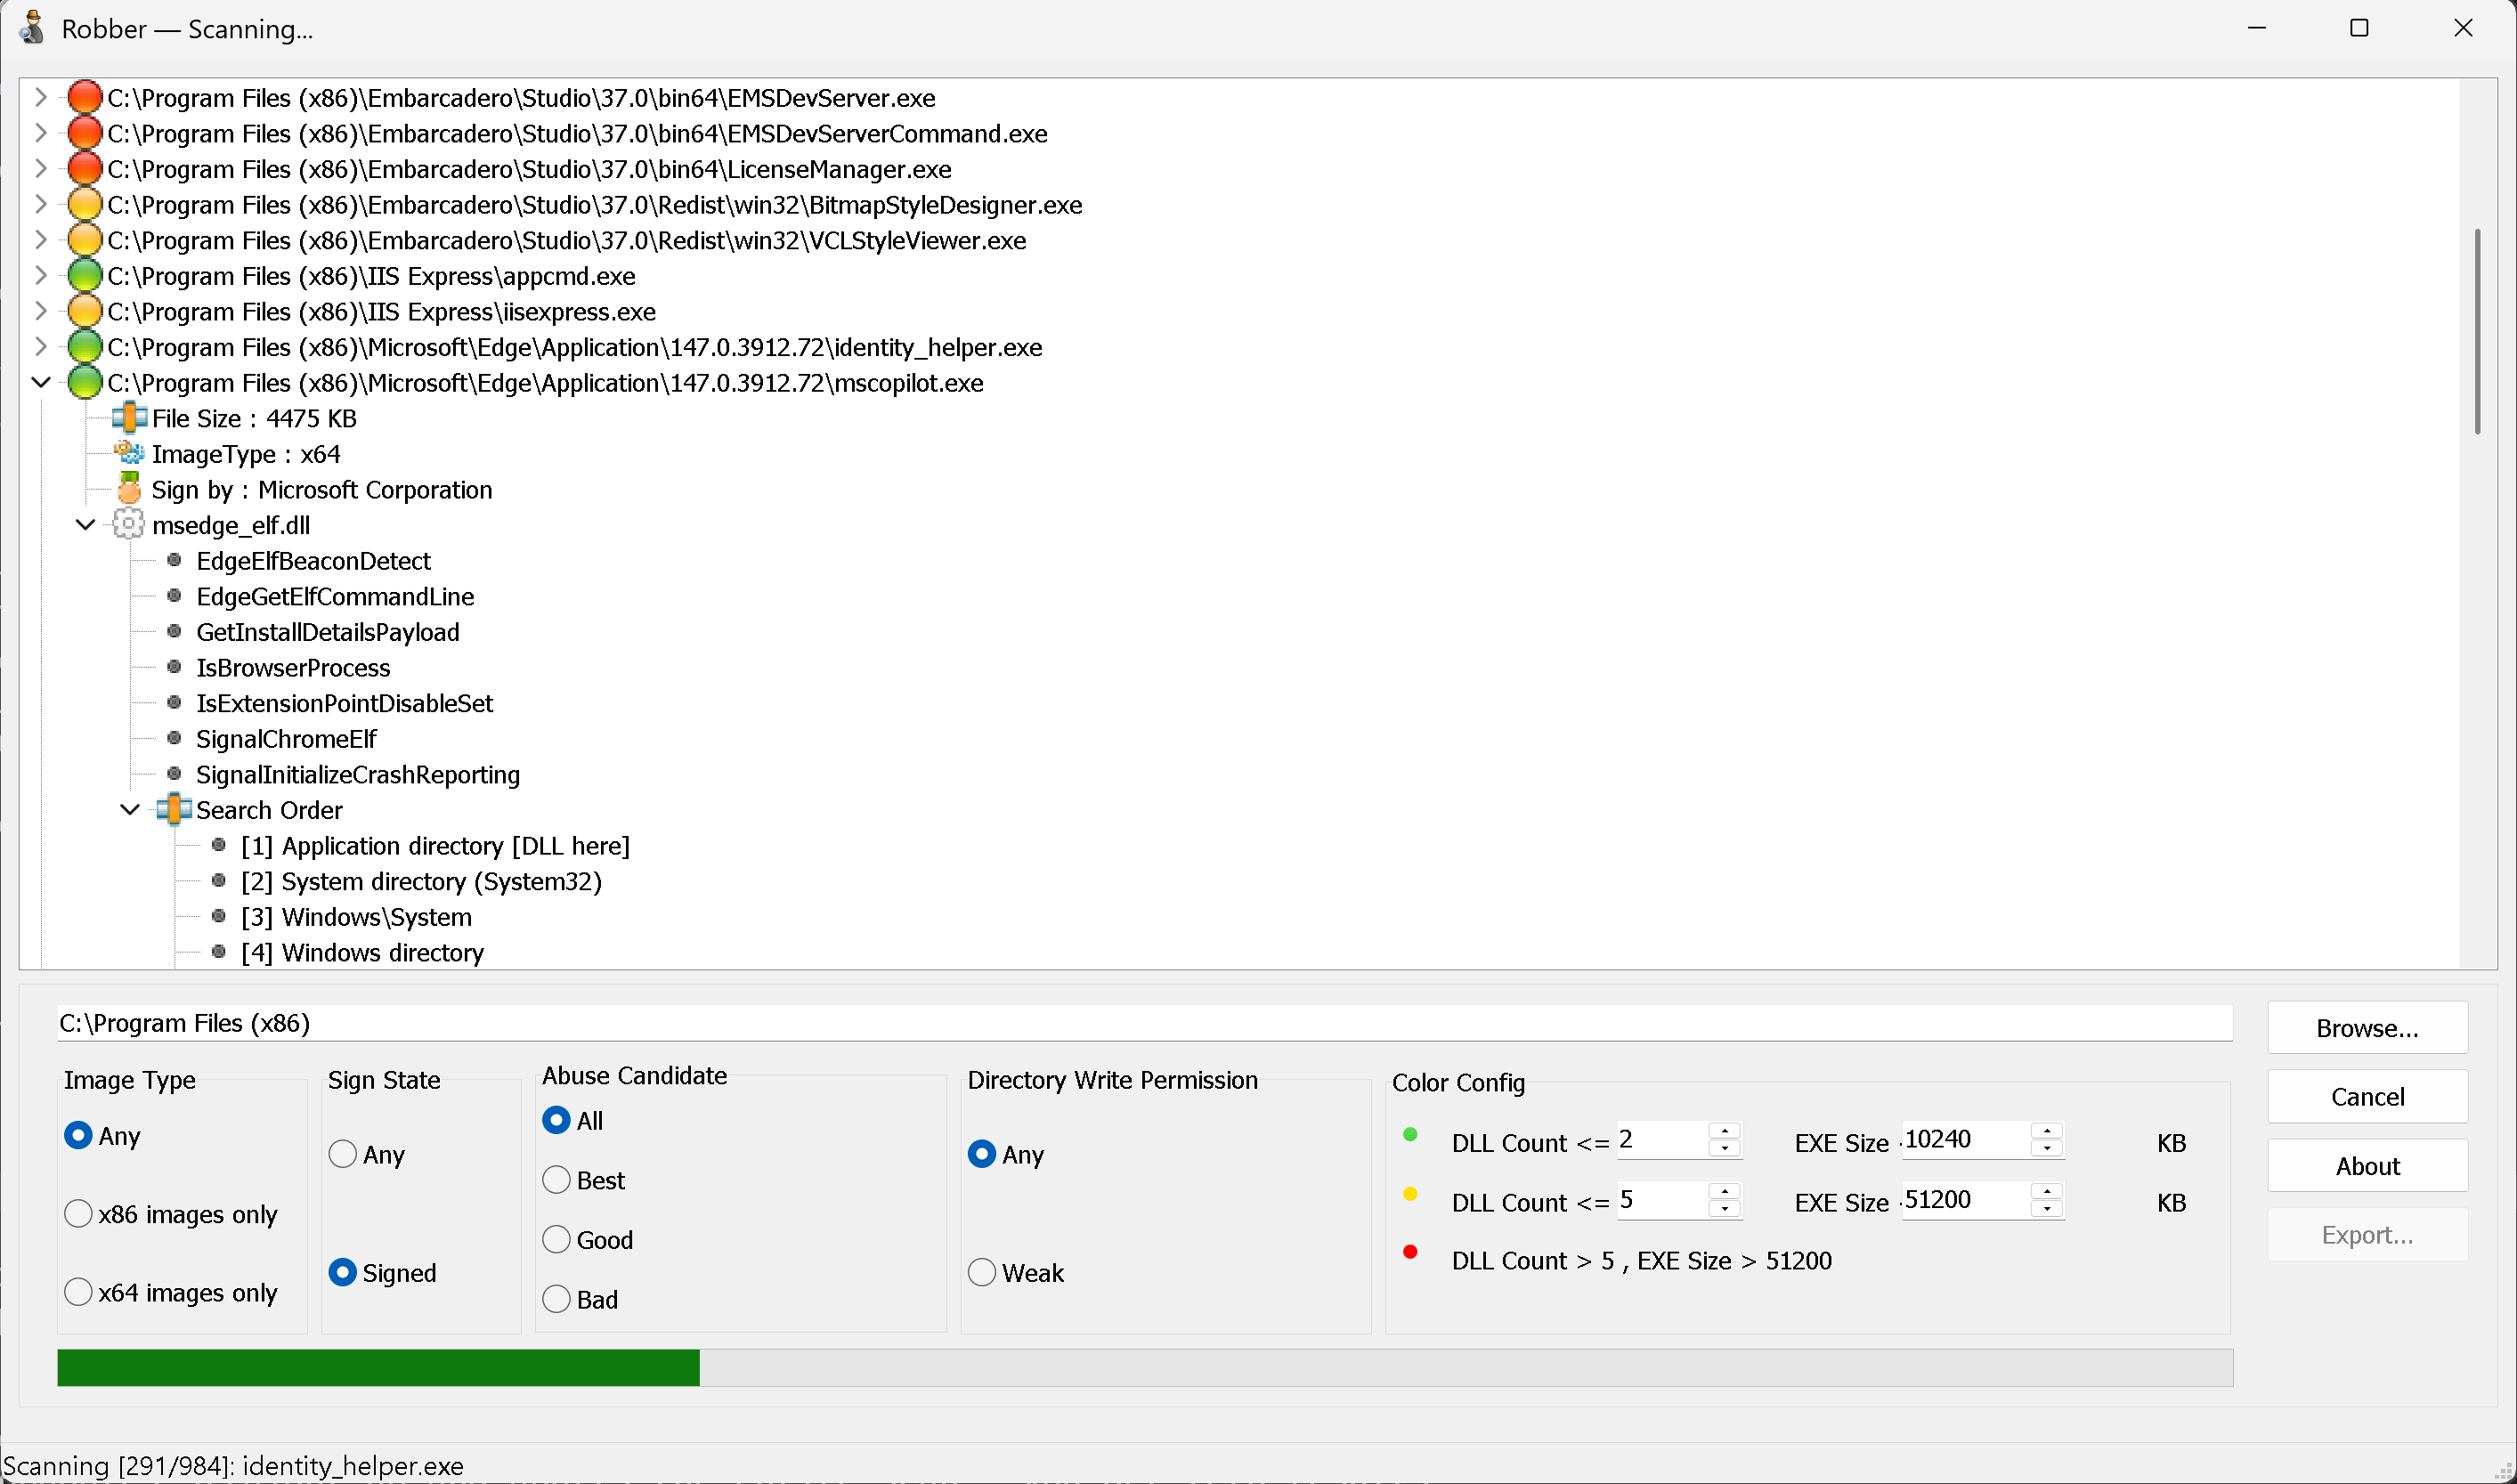 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
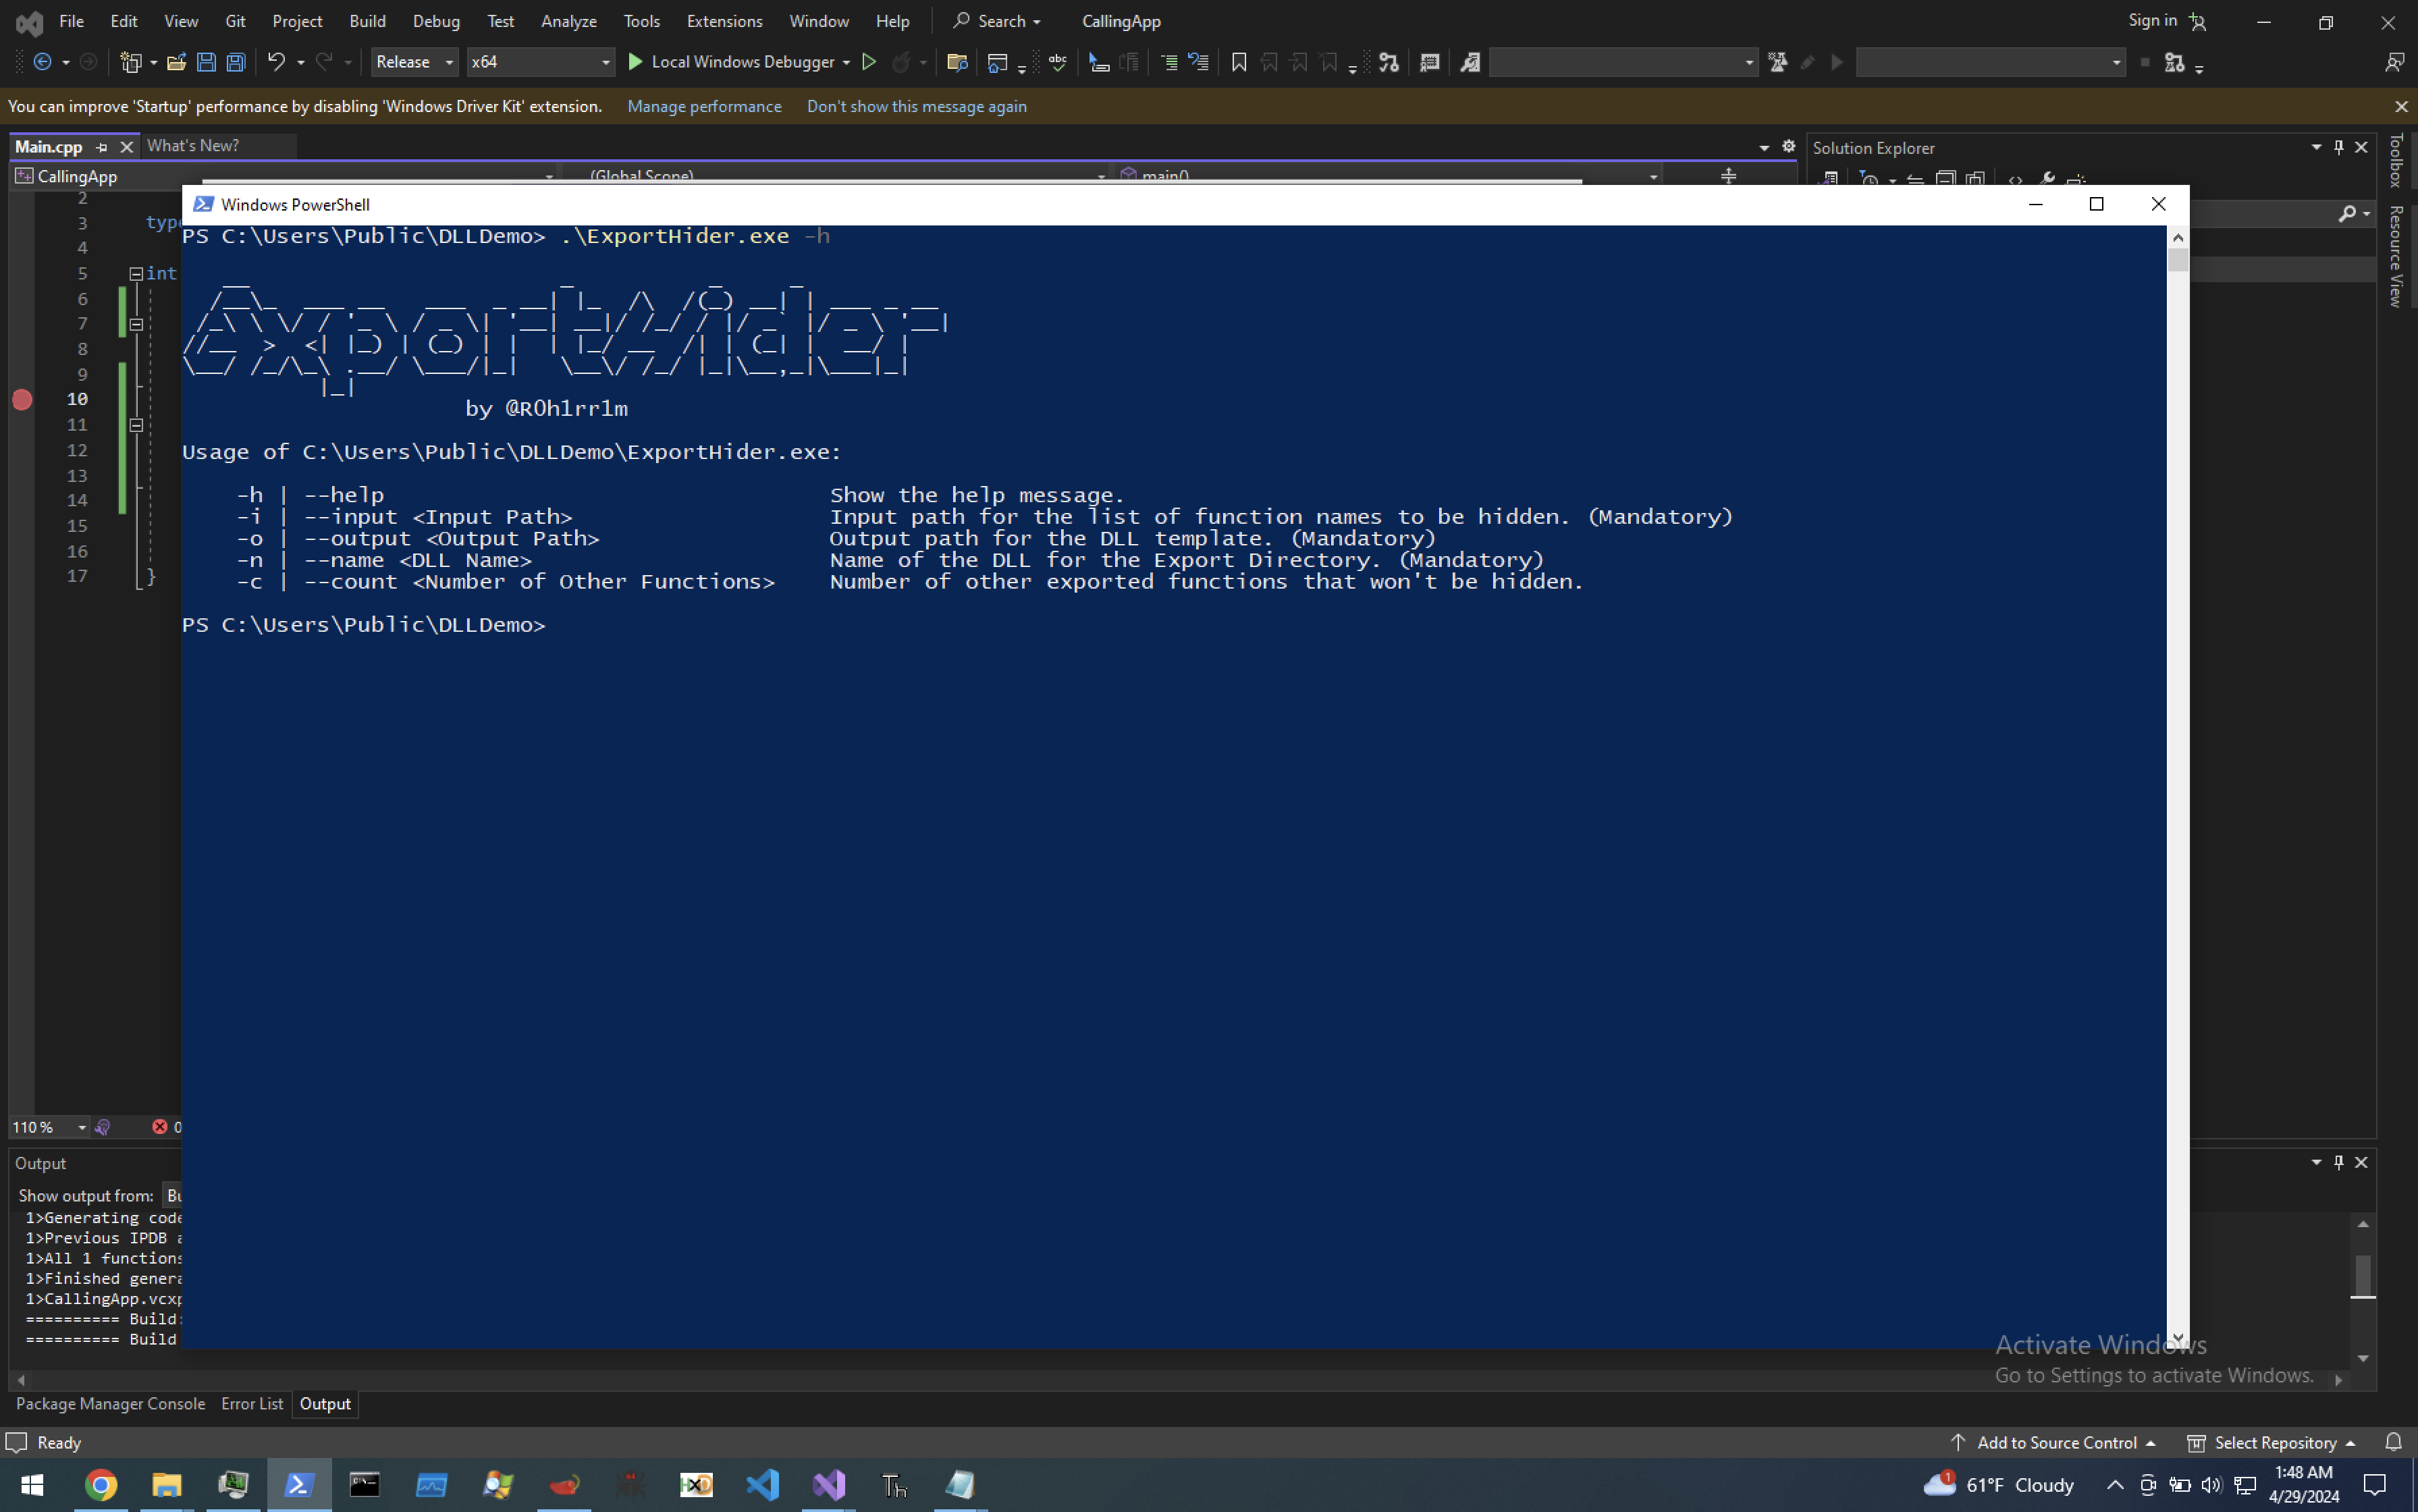 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk