
Archived
de4dot
 de4dot/de4dot
.NET deobfuscator and unpacker.
binary-analysisdynamic-code-analysismalware-analysis+2
7.4k
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
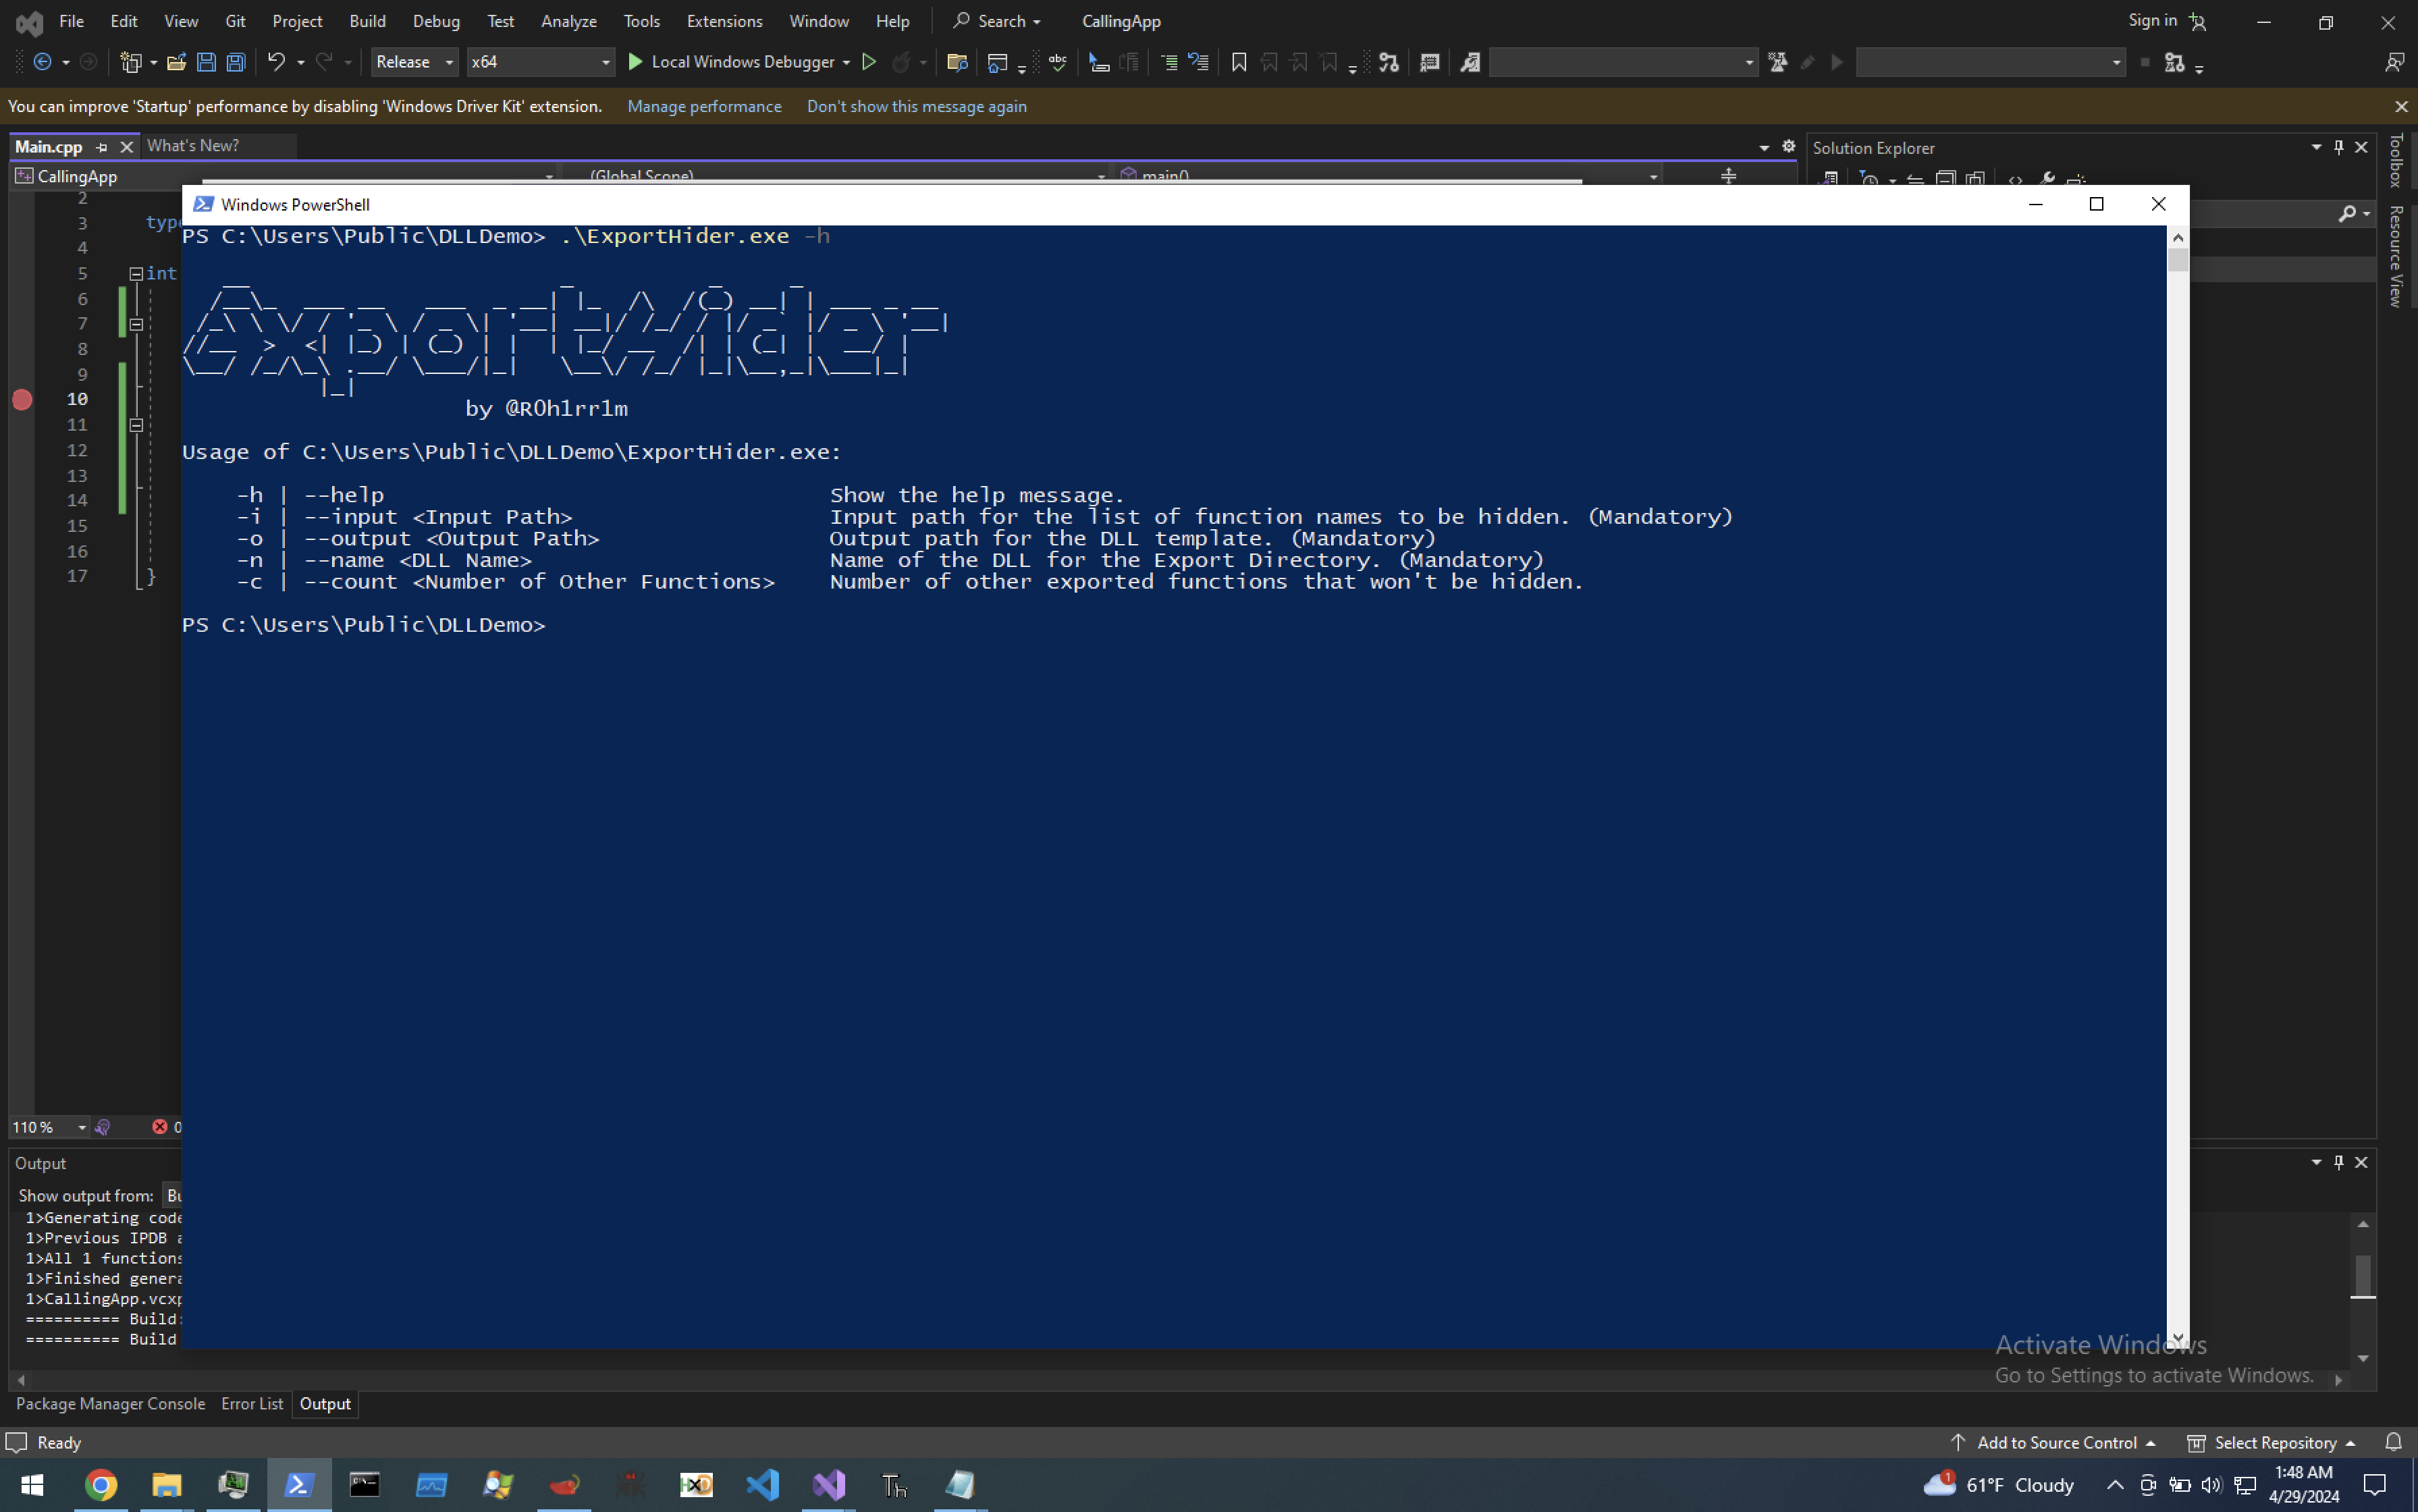 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
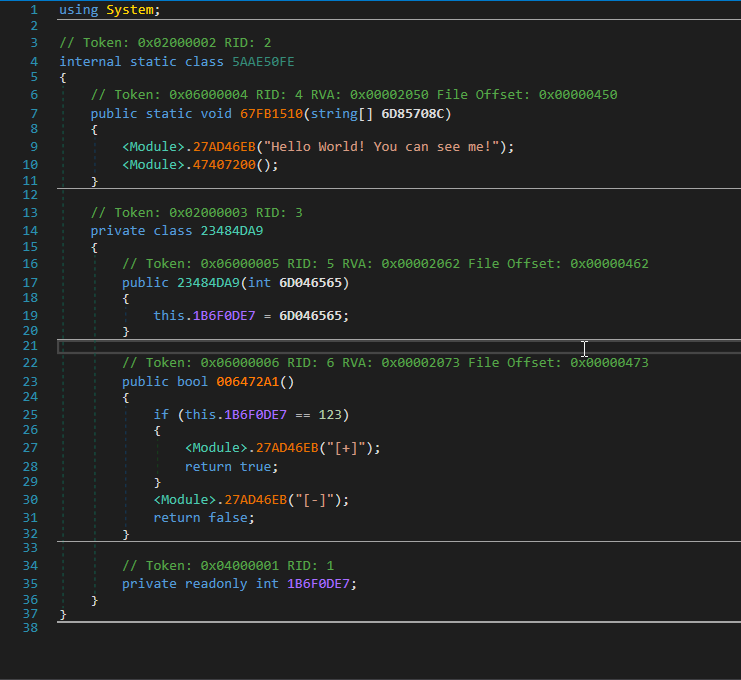 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
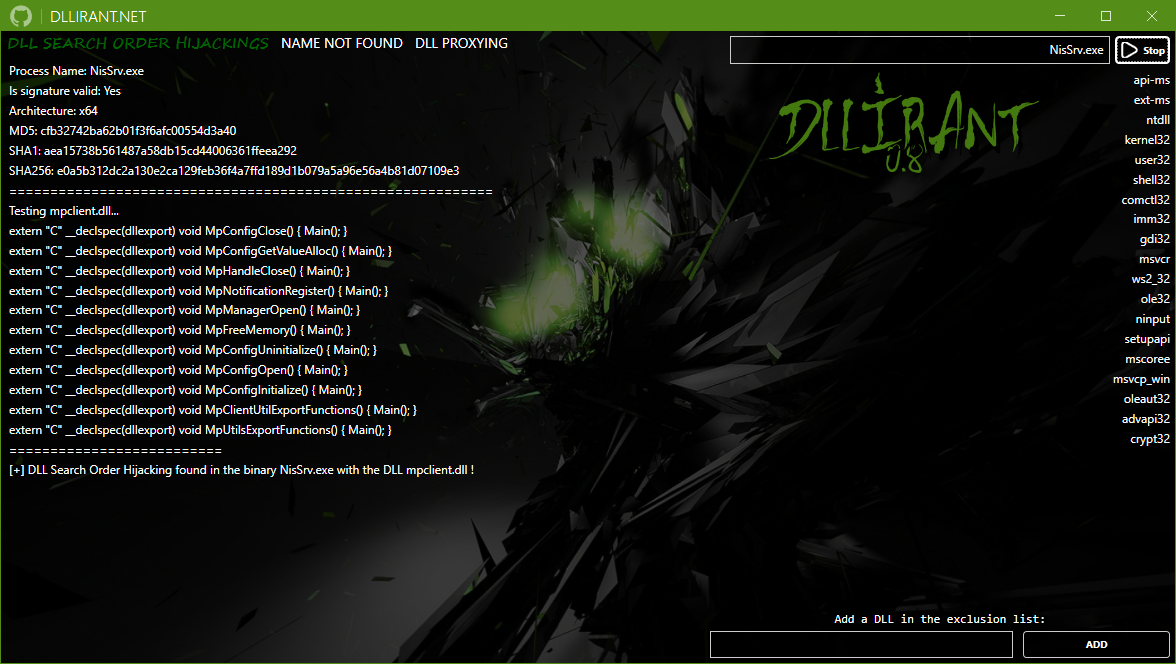 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
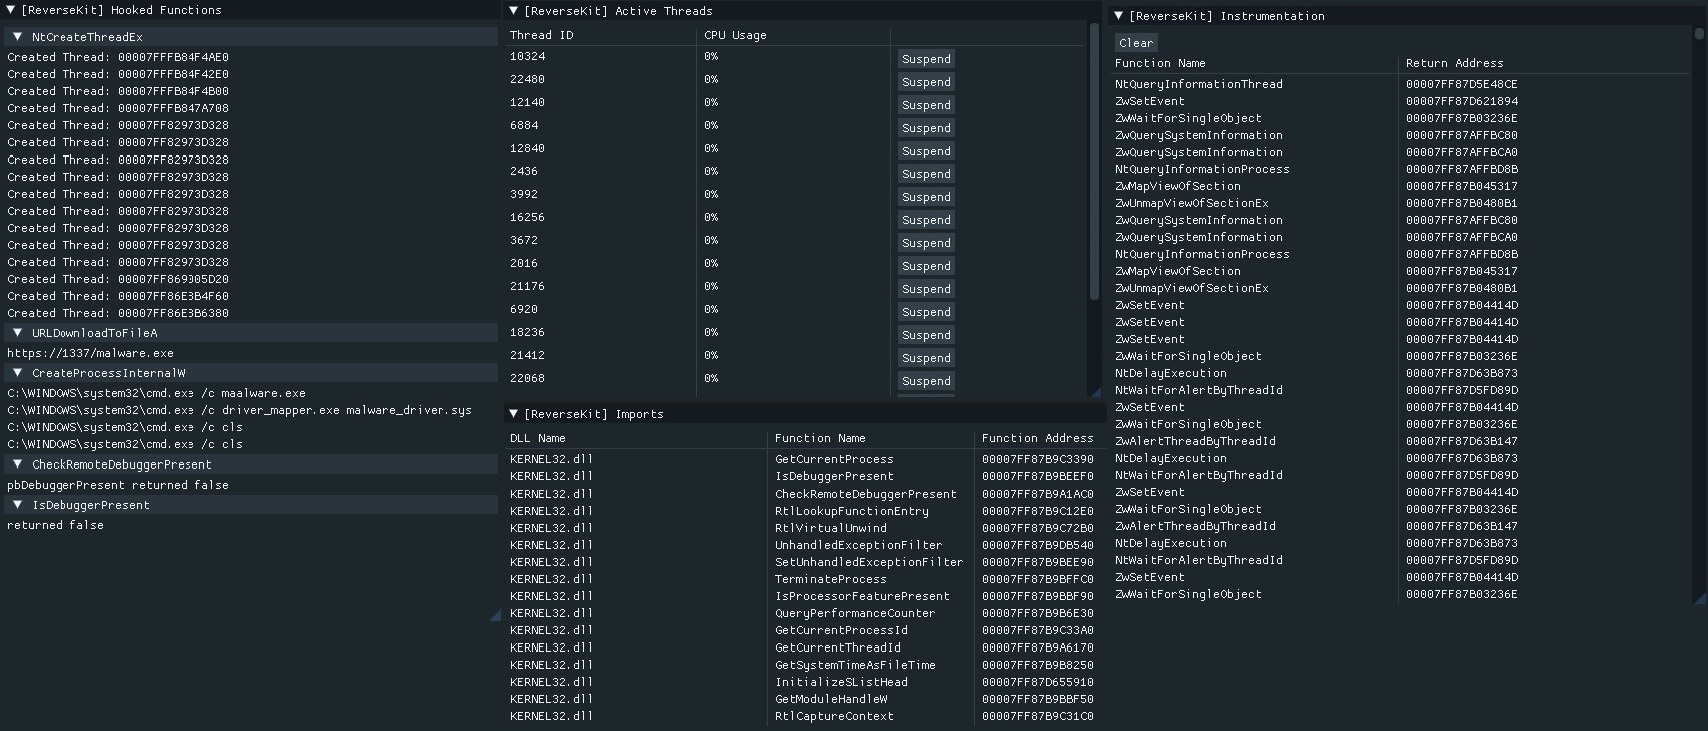 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
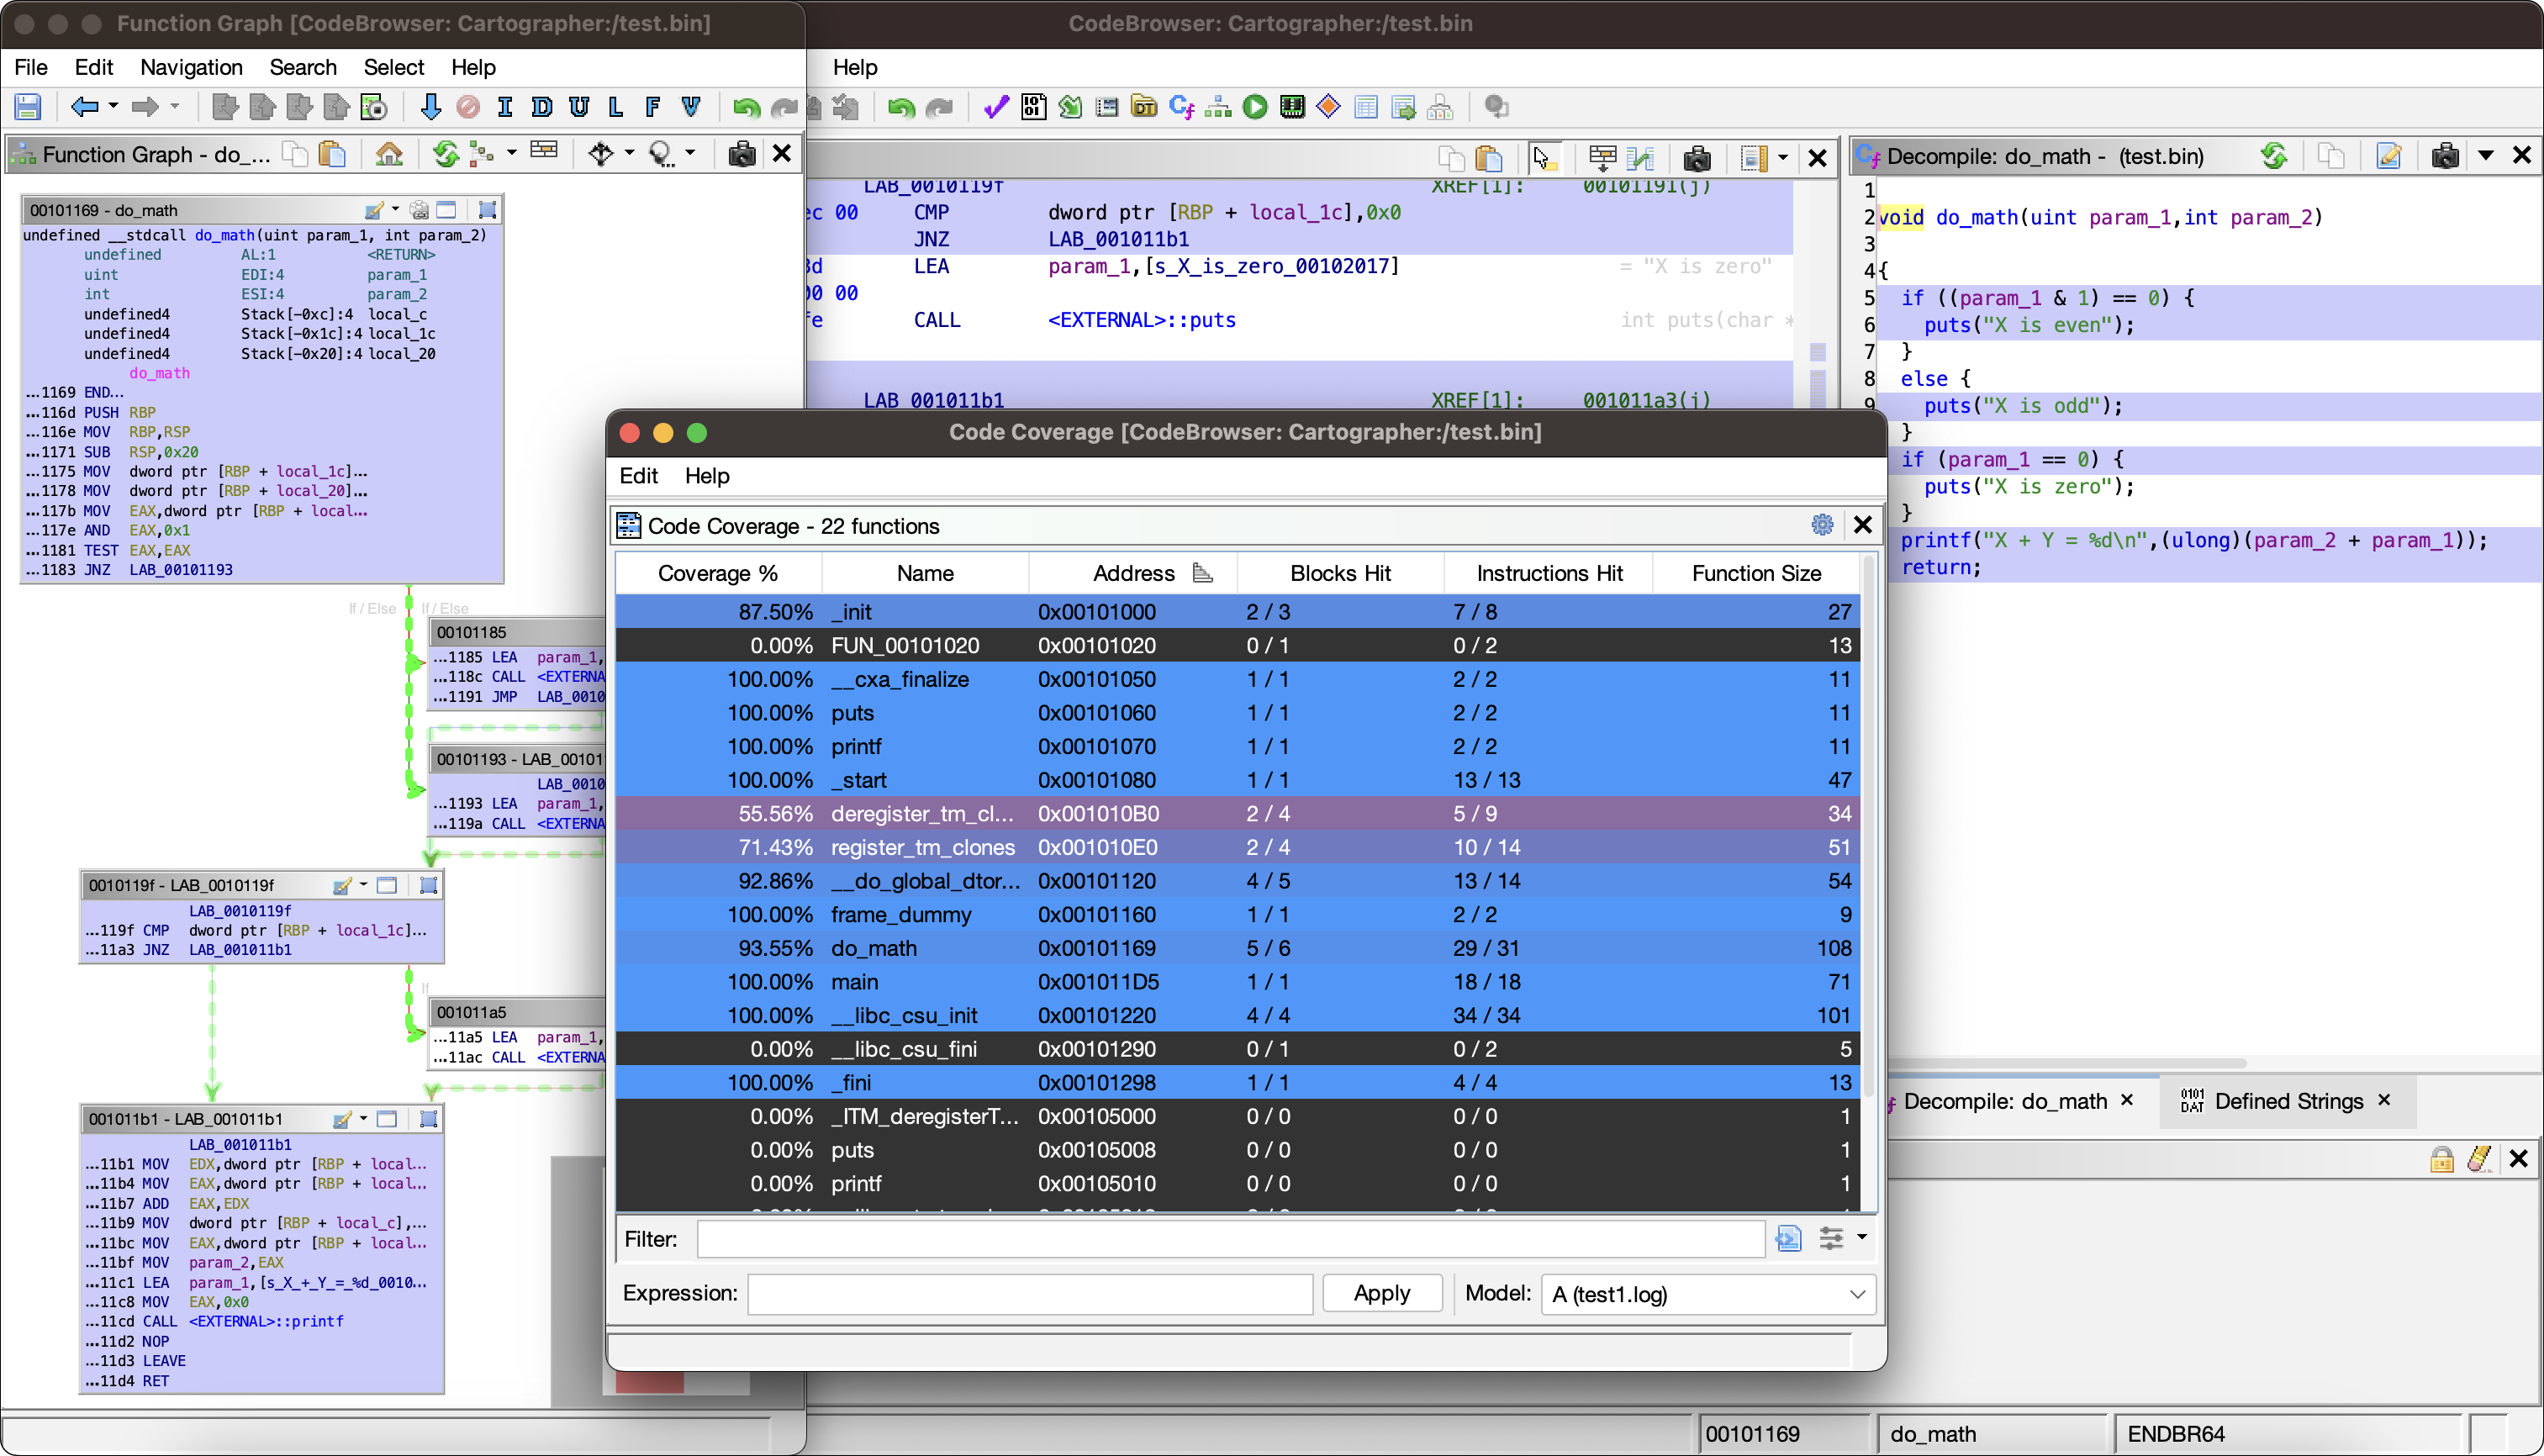 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
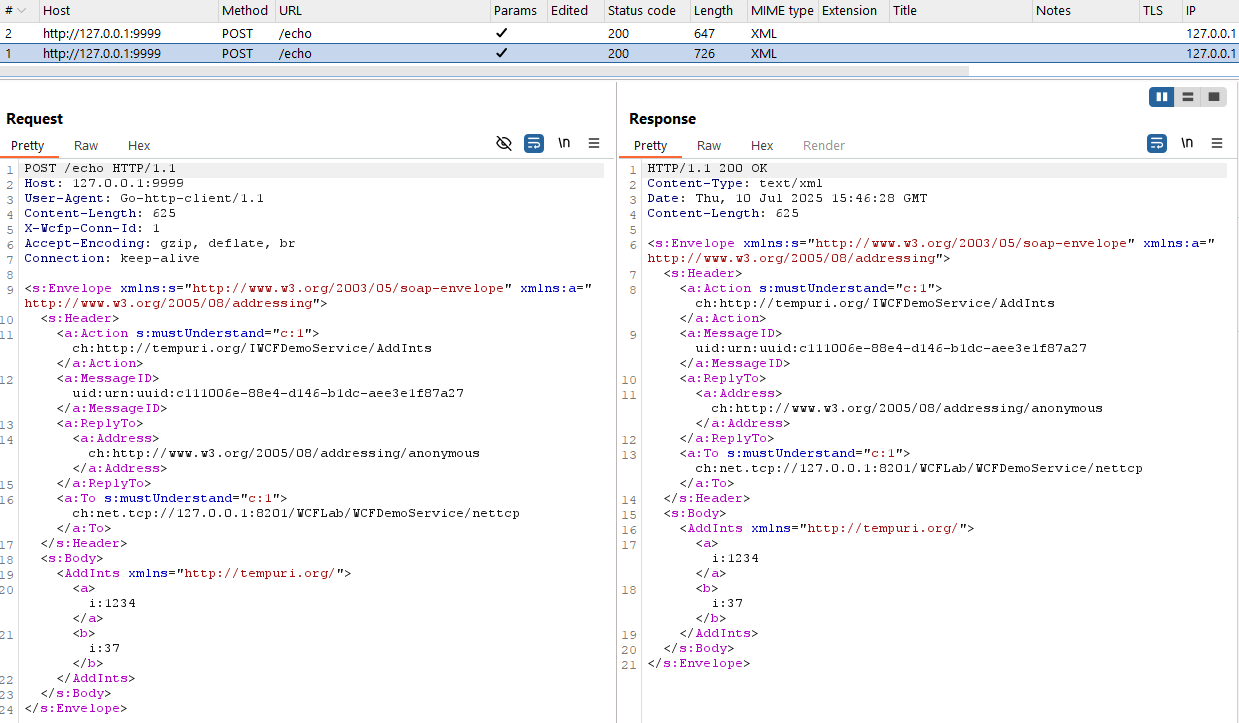 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages