
upx
 upx/upx
UPX - the Ultimate Packer for eXecutables
binary-analysisgeneral-purpose-utilitiesreverse-engineering
upx/upxUPX - the Ultimate Packer for eXecutables
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
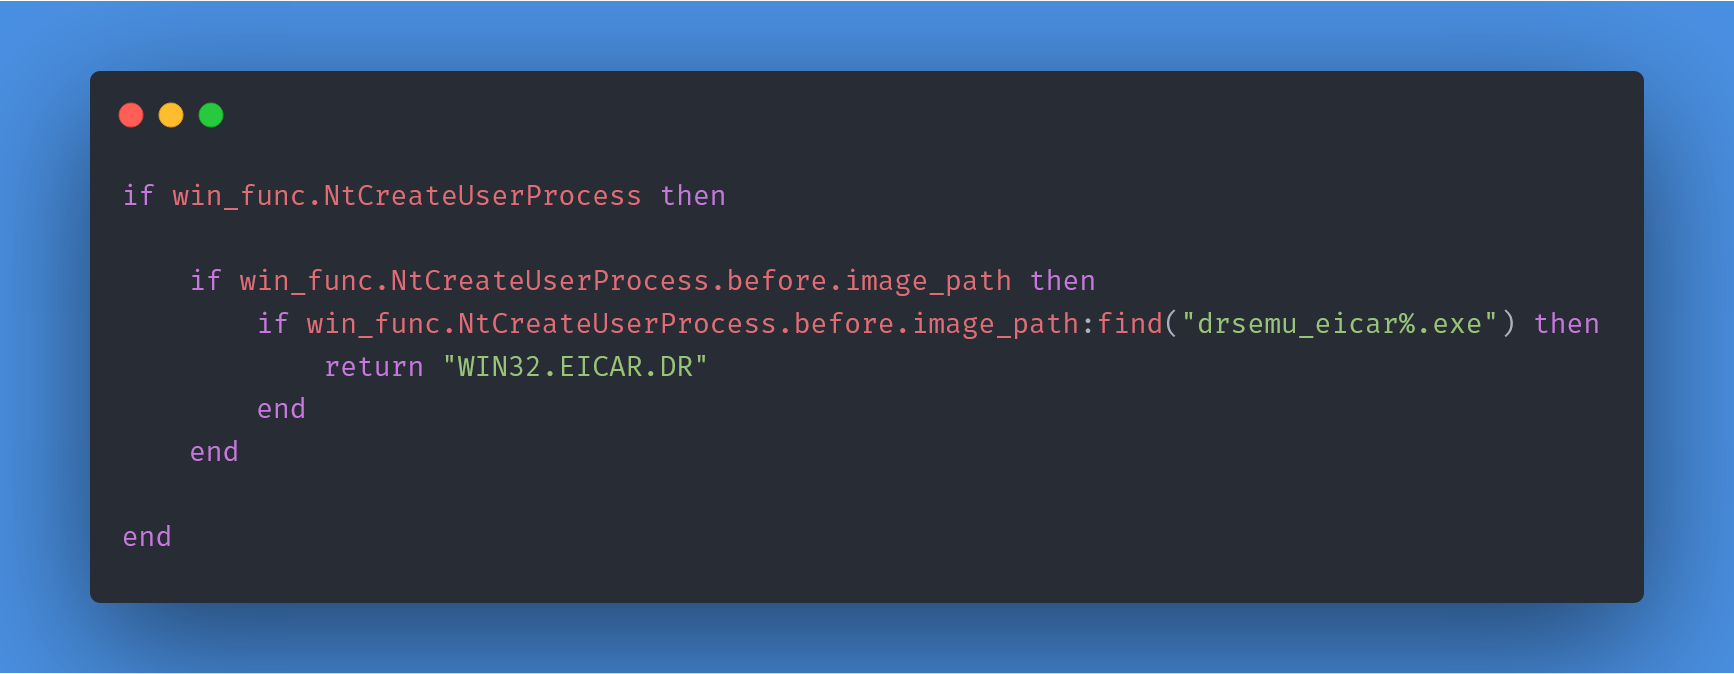 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
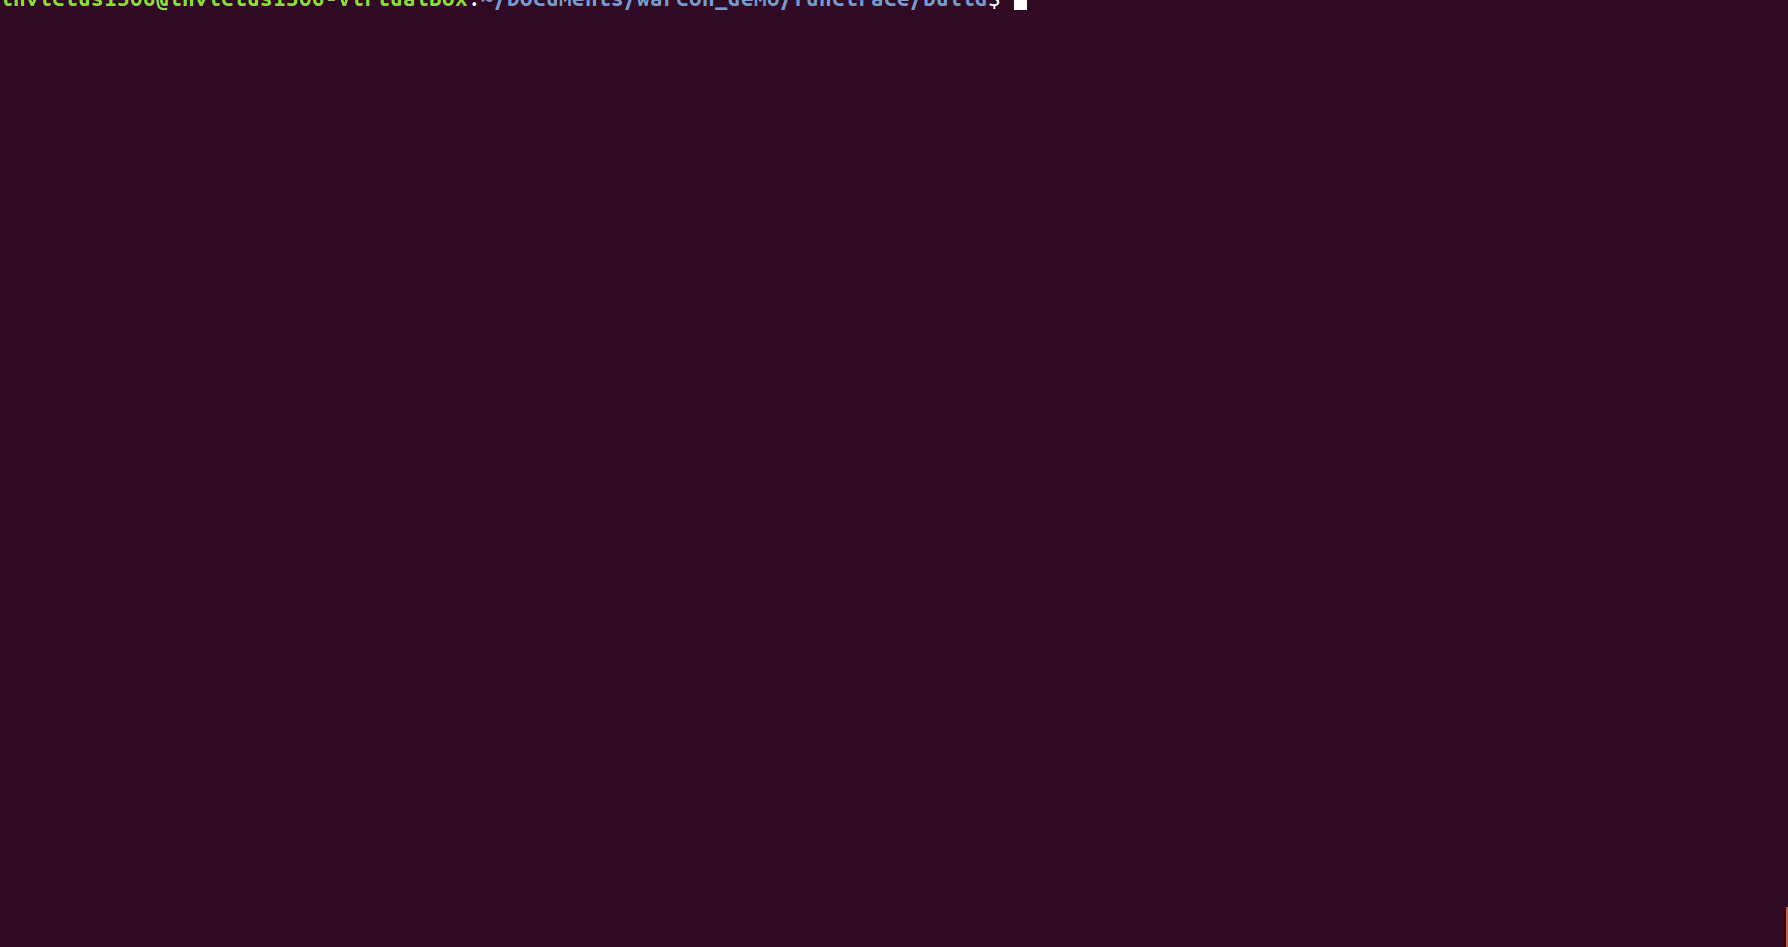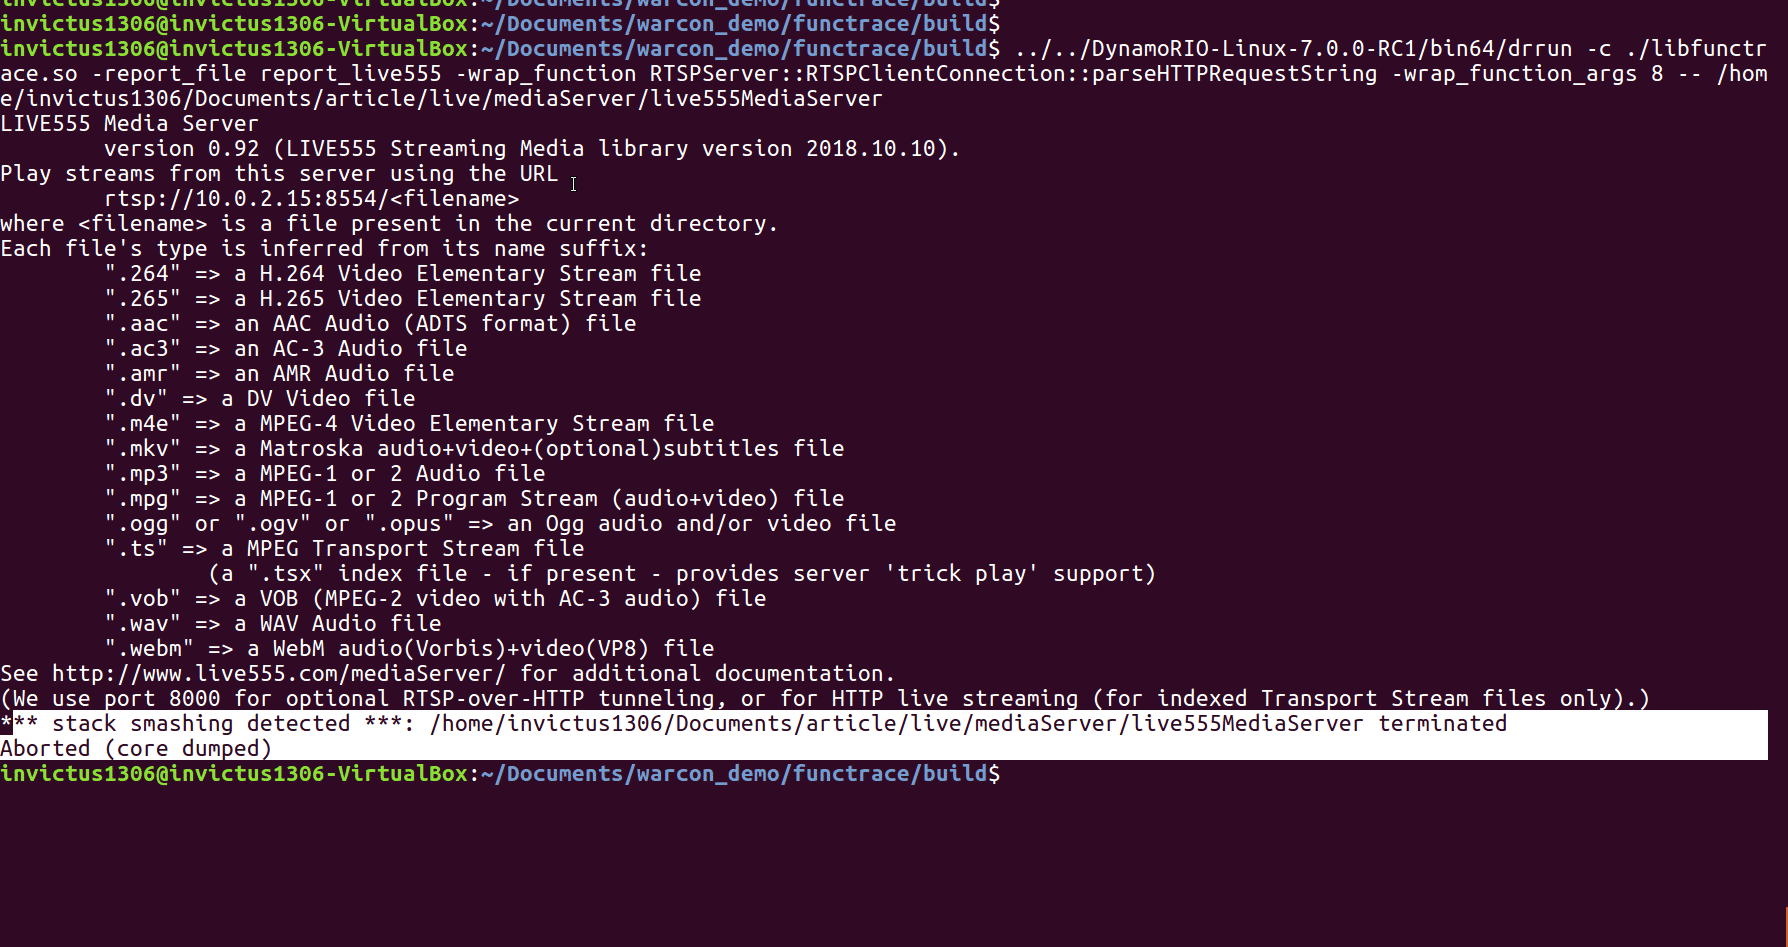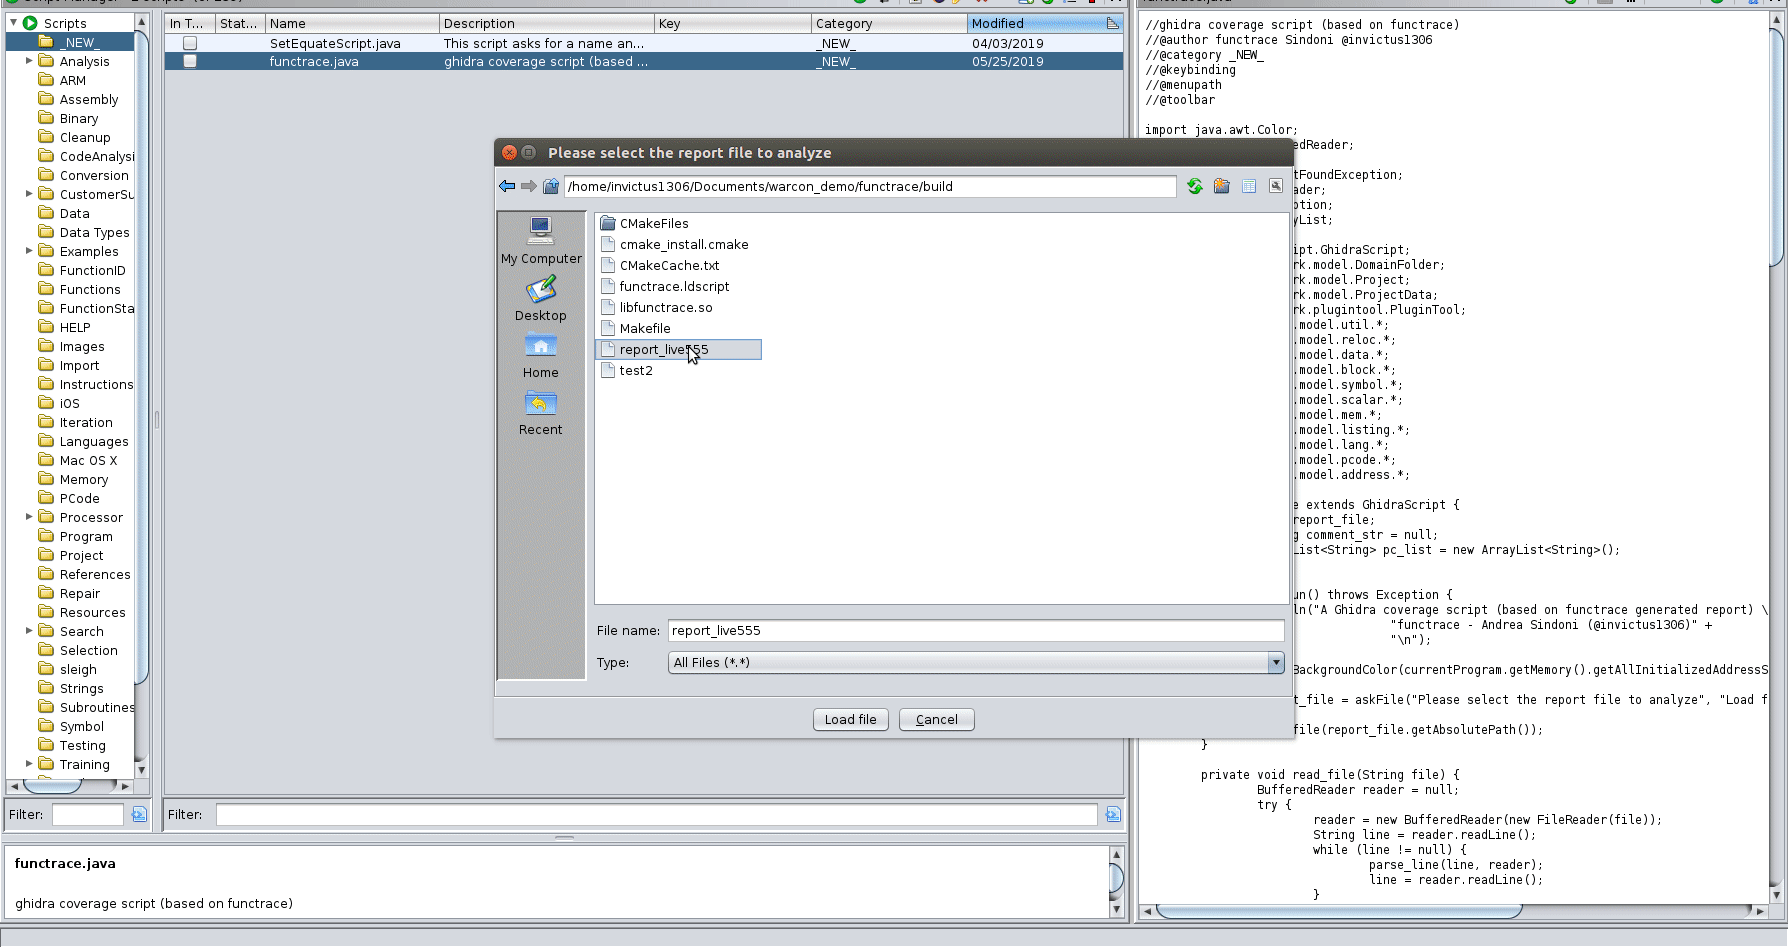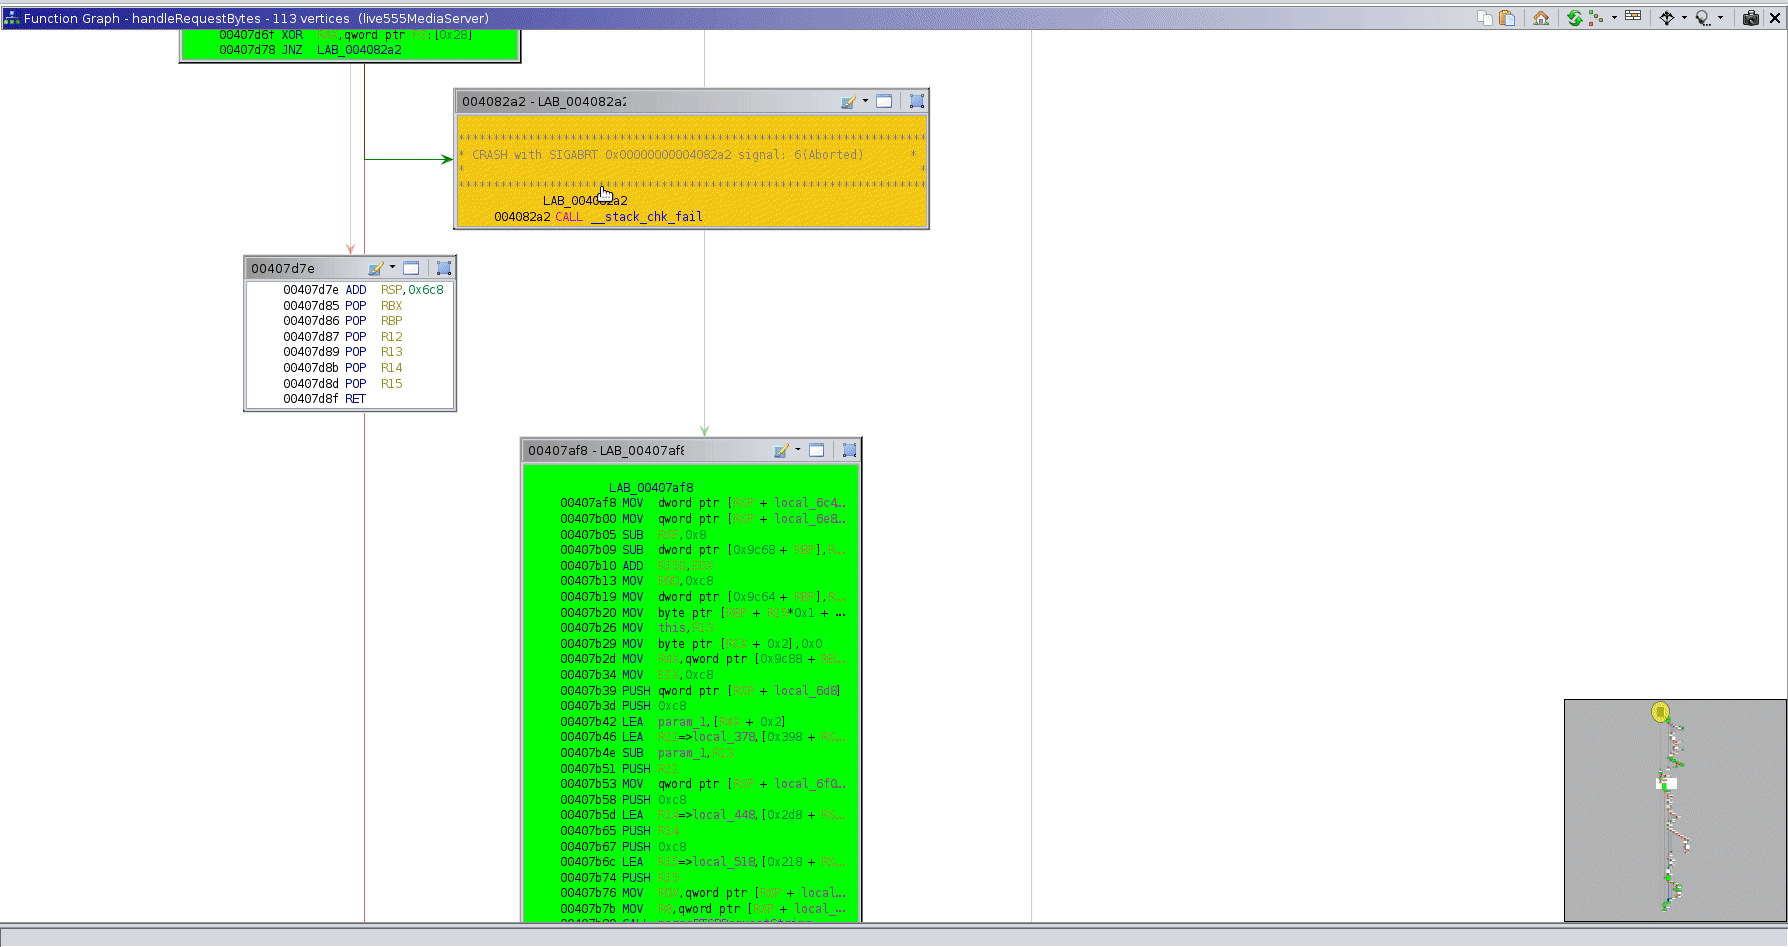 invictus1306/functrace
A function tracer
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…