

CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
8.2k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 kaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis
Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 vahpem/rust-deobf
Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
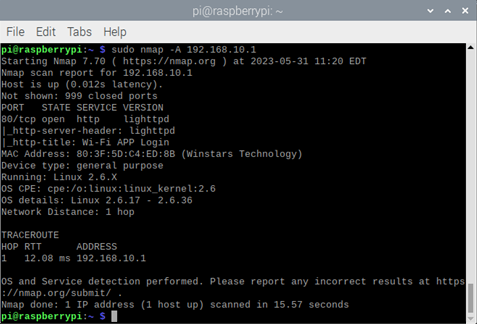 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
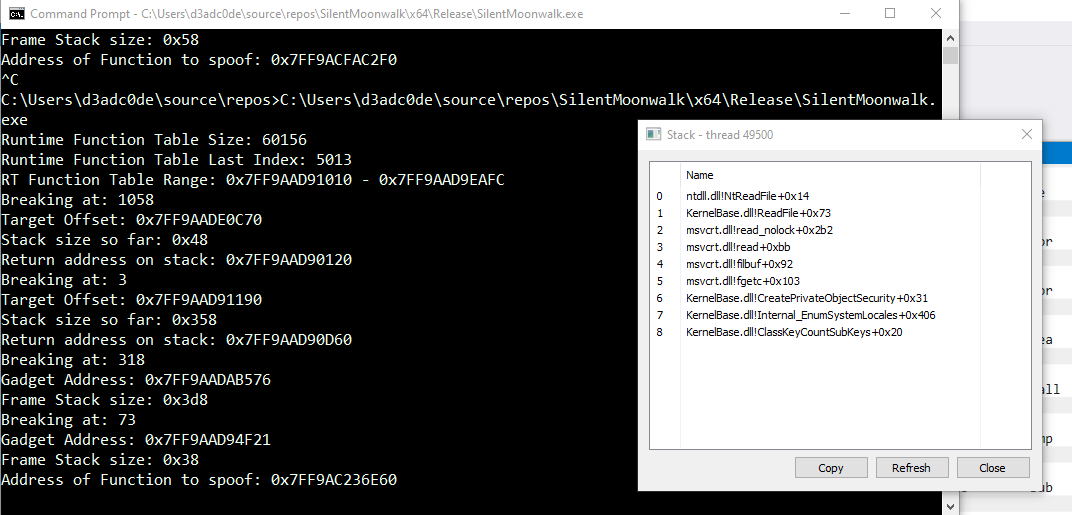 klezvirus/silentmoonwalk
PoC Implementation of a fully dynamic call stack spoofer
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
 zeoday/cobaltstrike4.5_cdf-1
cobaltstrike4.5版本破/解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等