

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
202
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 darthton/blackbone
Windows memory hacking library
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
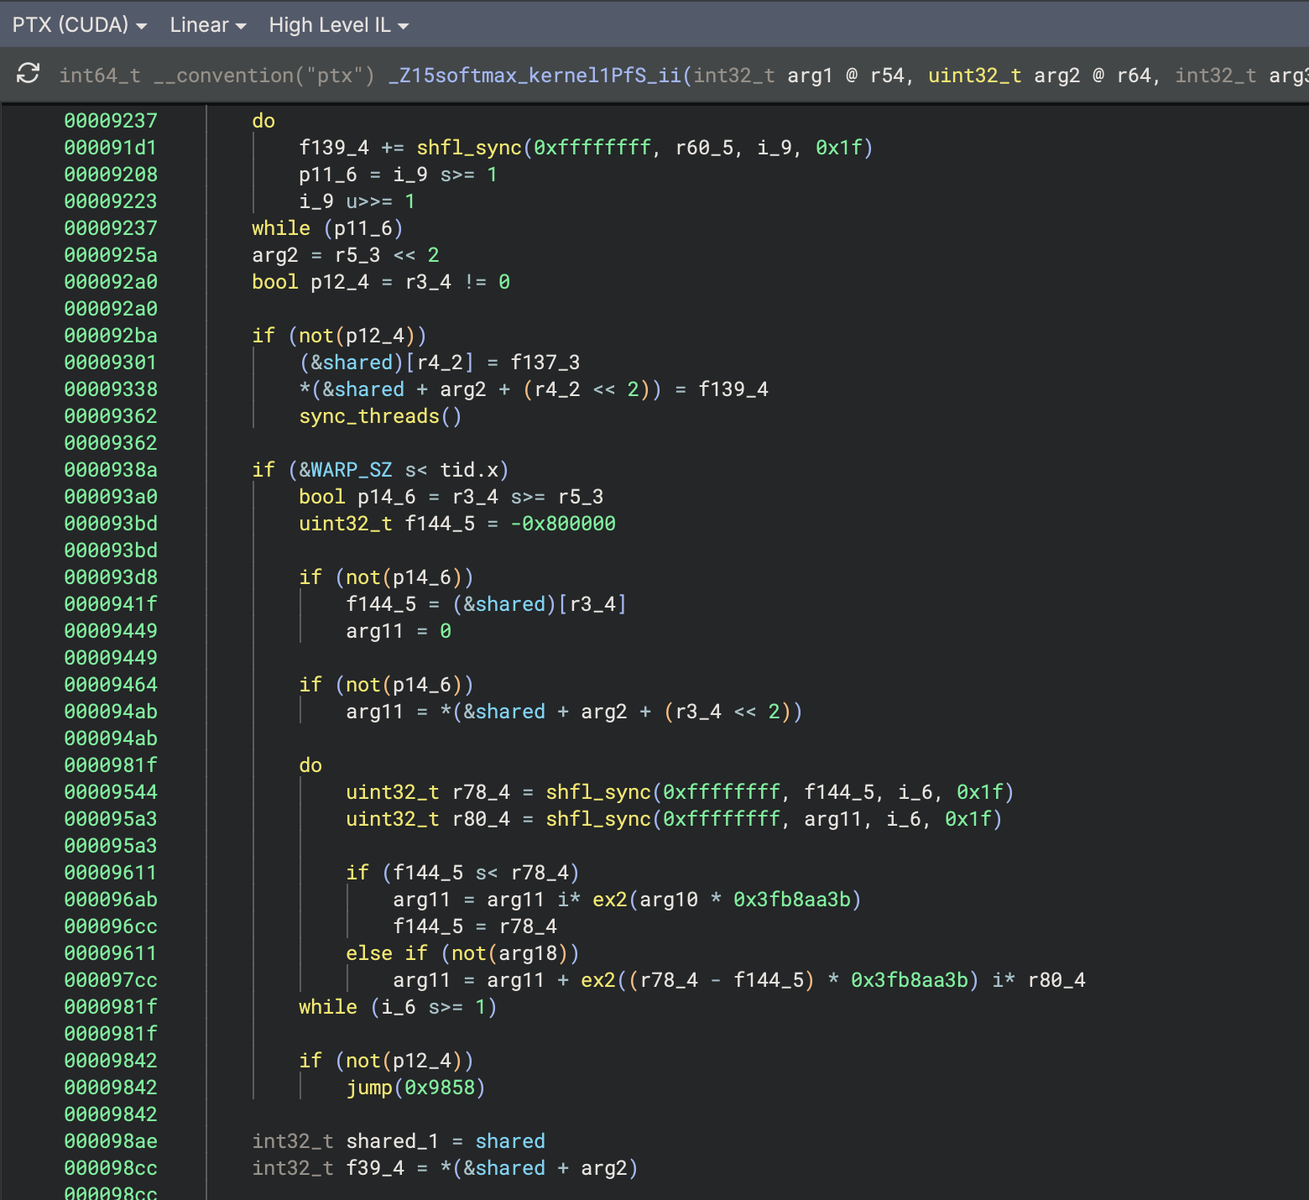 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
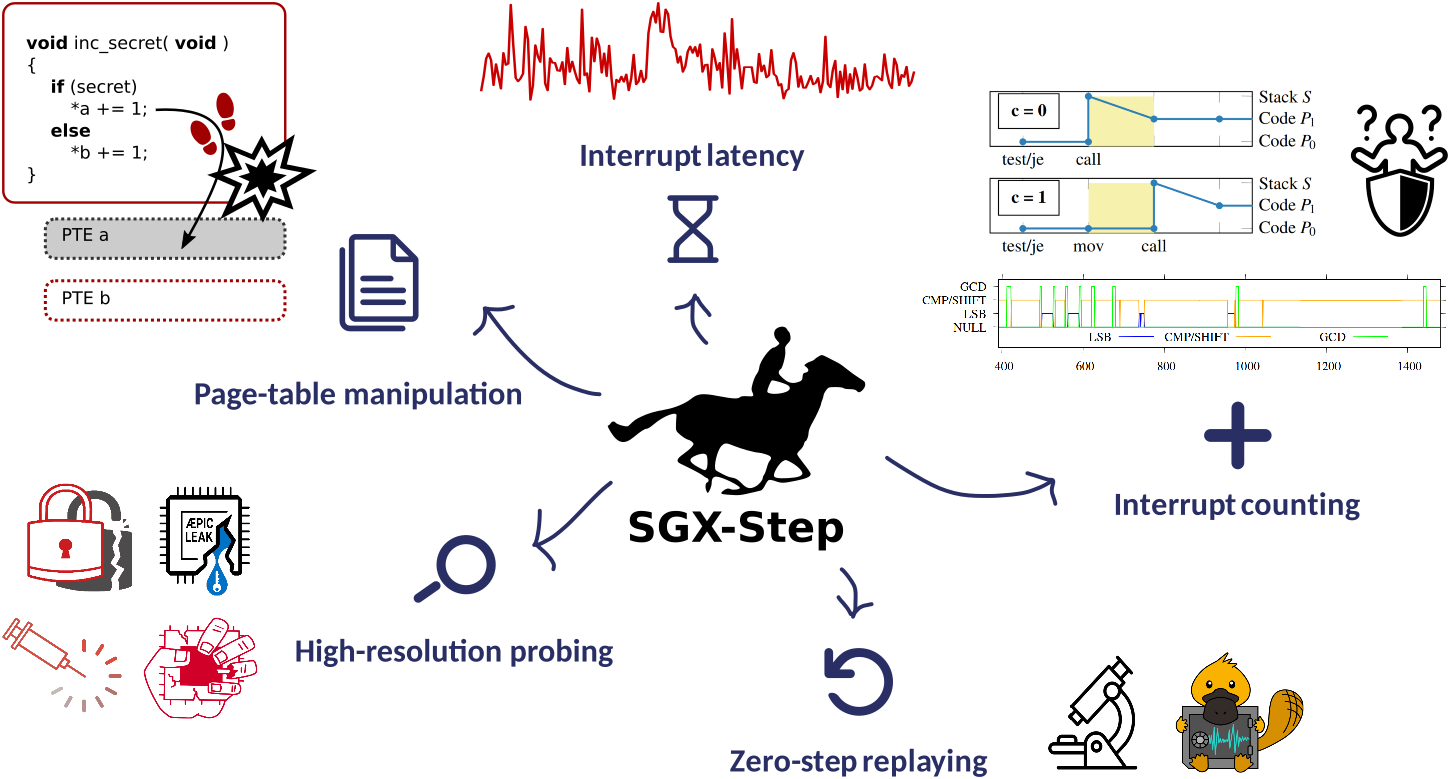 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
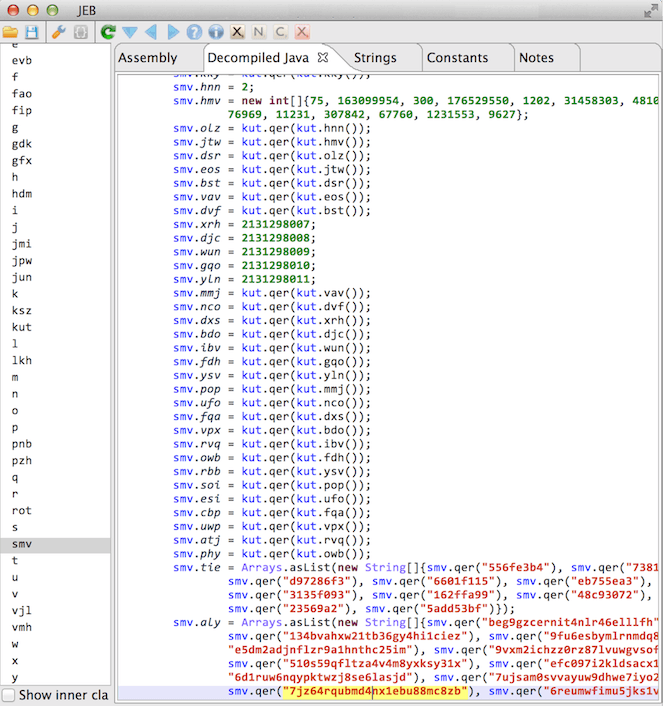 calebfenton/simplify
Android virtual machine and deobfuscator
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
 allthingsida/idasql
Vibe Reverse Engineer with IDA Pro: An interface for IDA in SQL via live virtual tables. Don't let appearances deceive you! :)
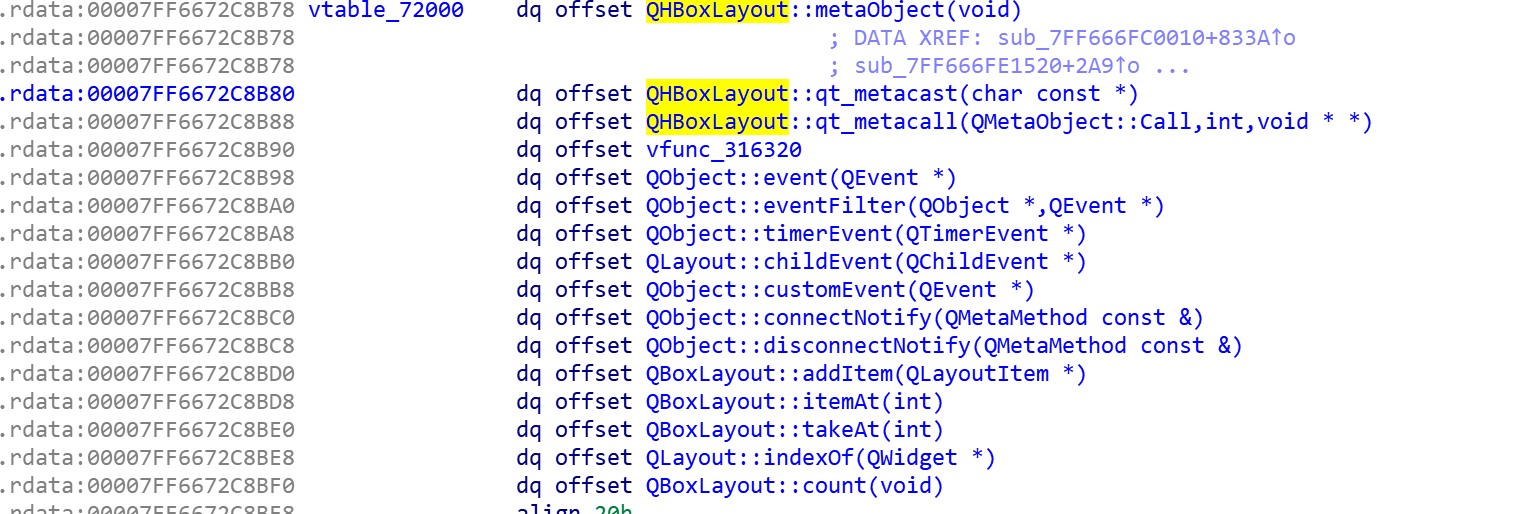 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 eset/wslink-vm-analyzer
WslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware
 snowsnowsnows/eaglevm
Native code virtualizer for x64 binaries
 mrakovic-org/nashavm
Nasha is a Virtual Machine for .NET files and its runtime was made in C++/CLI
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python
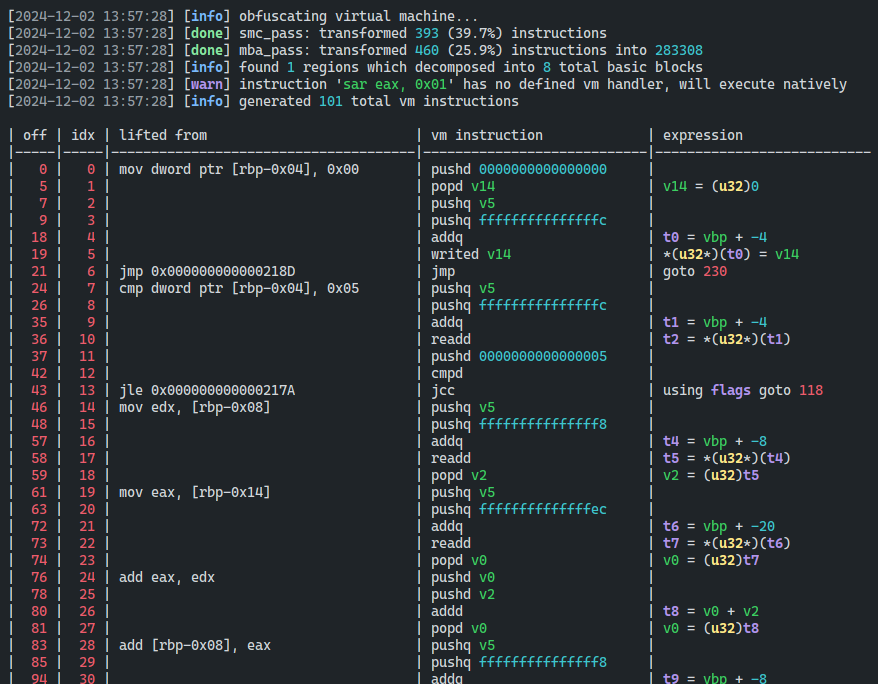 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…