
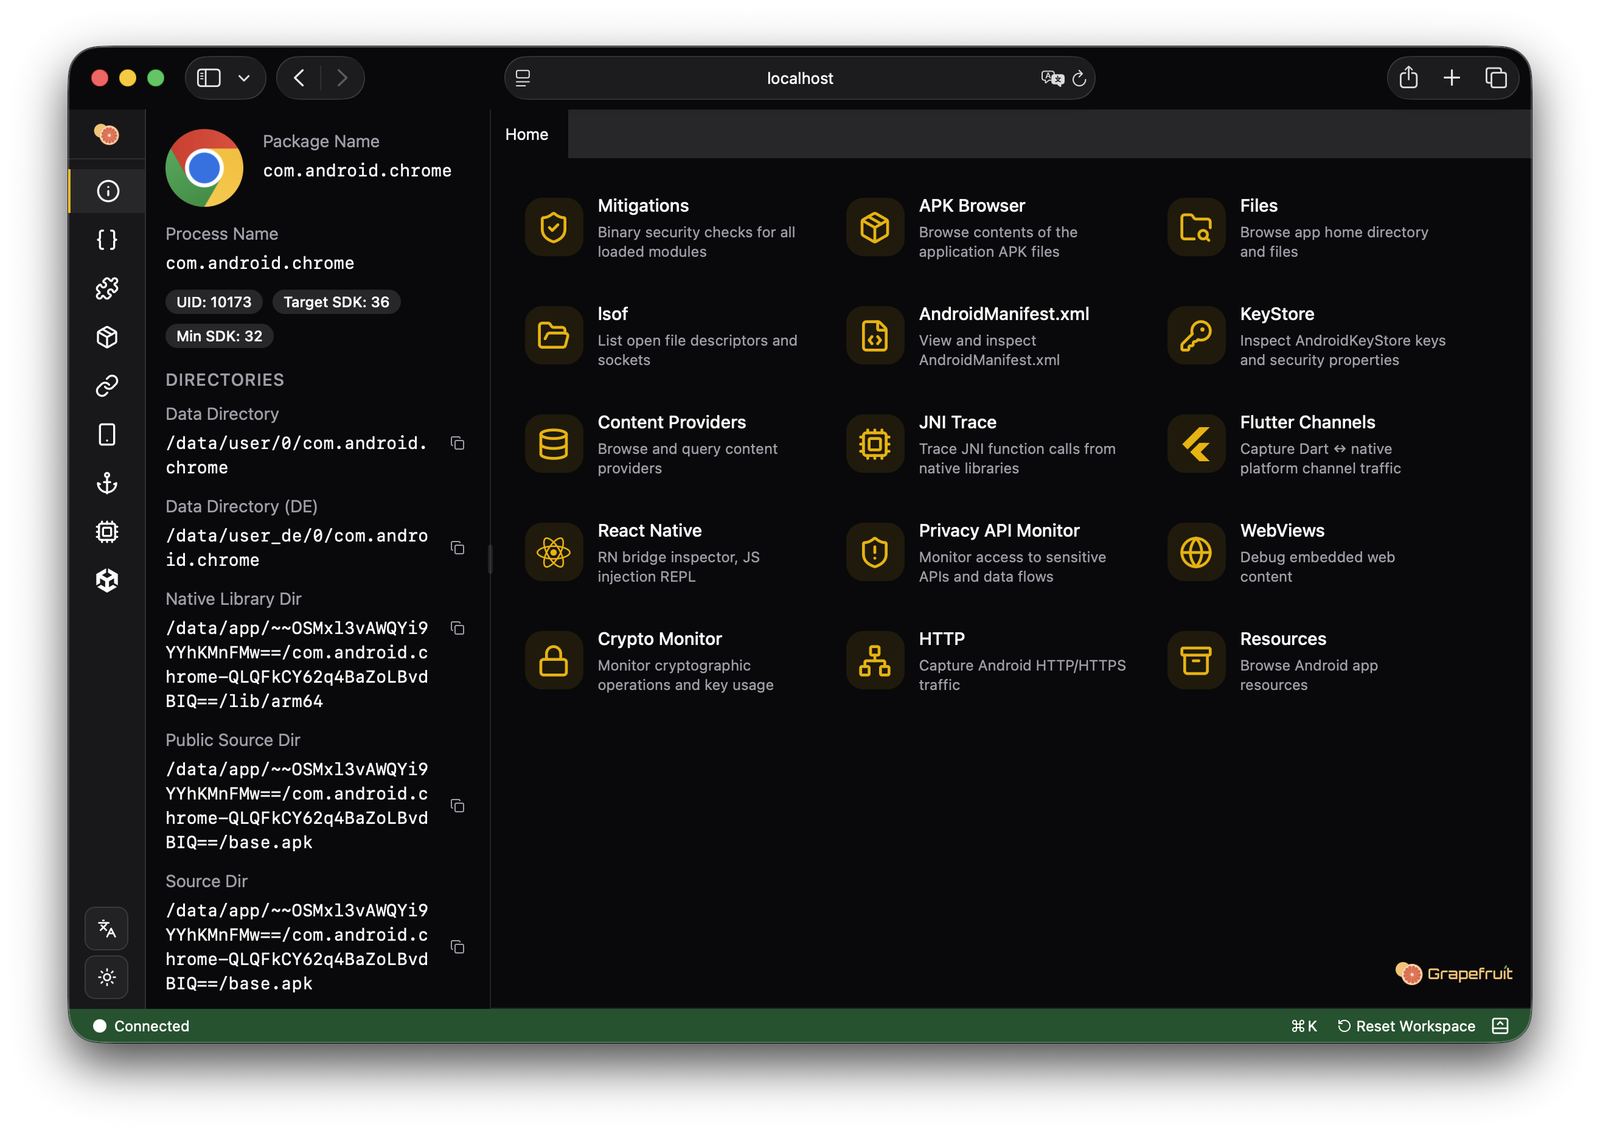
grapefruit
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k
chichou/grapefruitOpen-source mobile security testing suite for iOS and Android. Previously Passionfruit
 de4dot/de4dot
.NET deobfuscator and unpacker.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
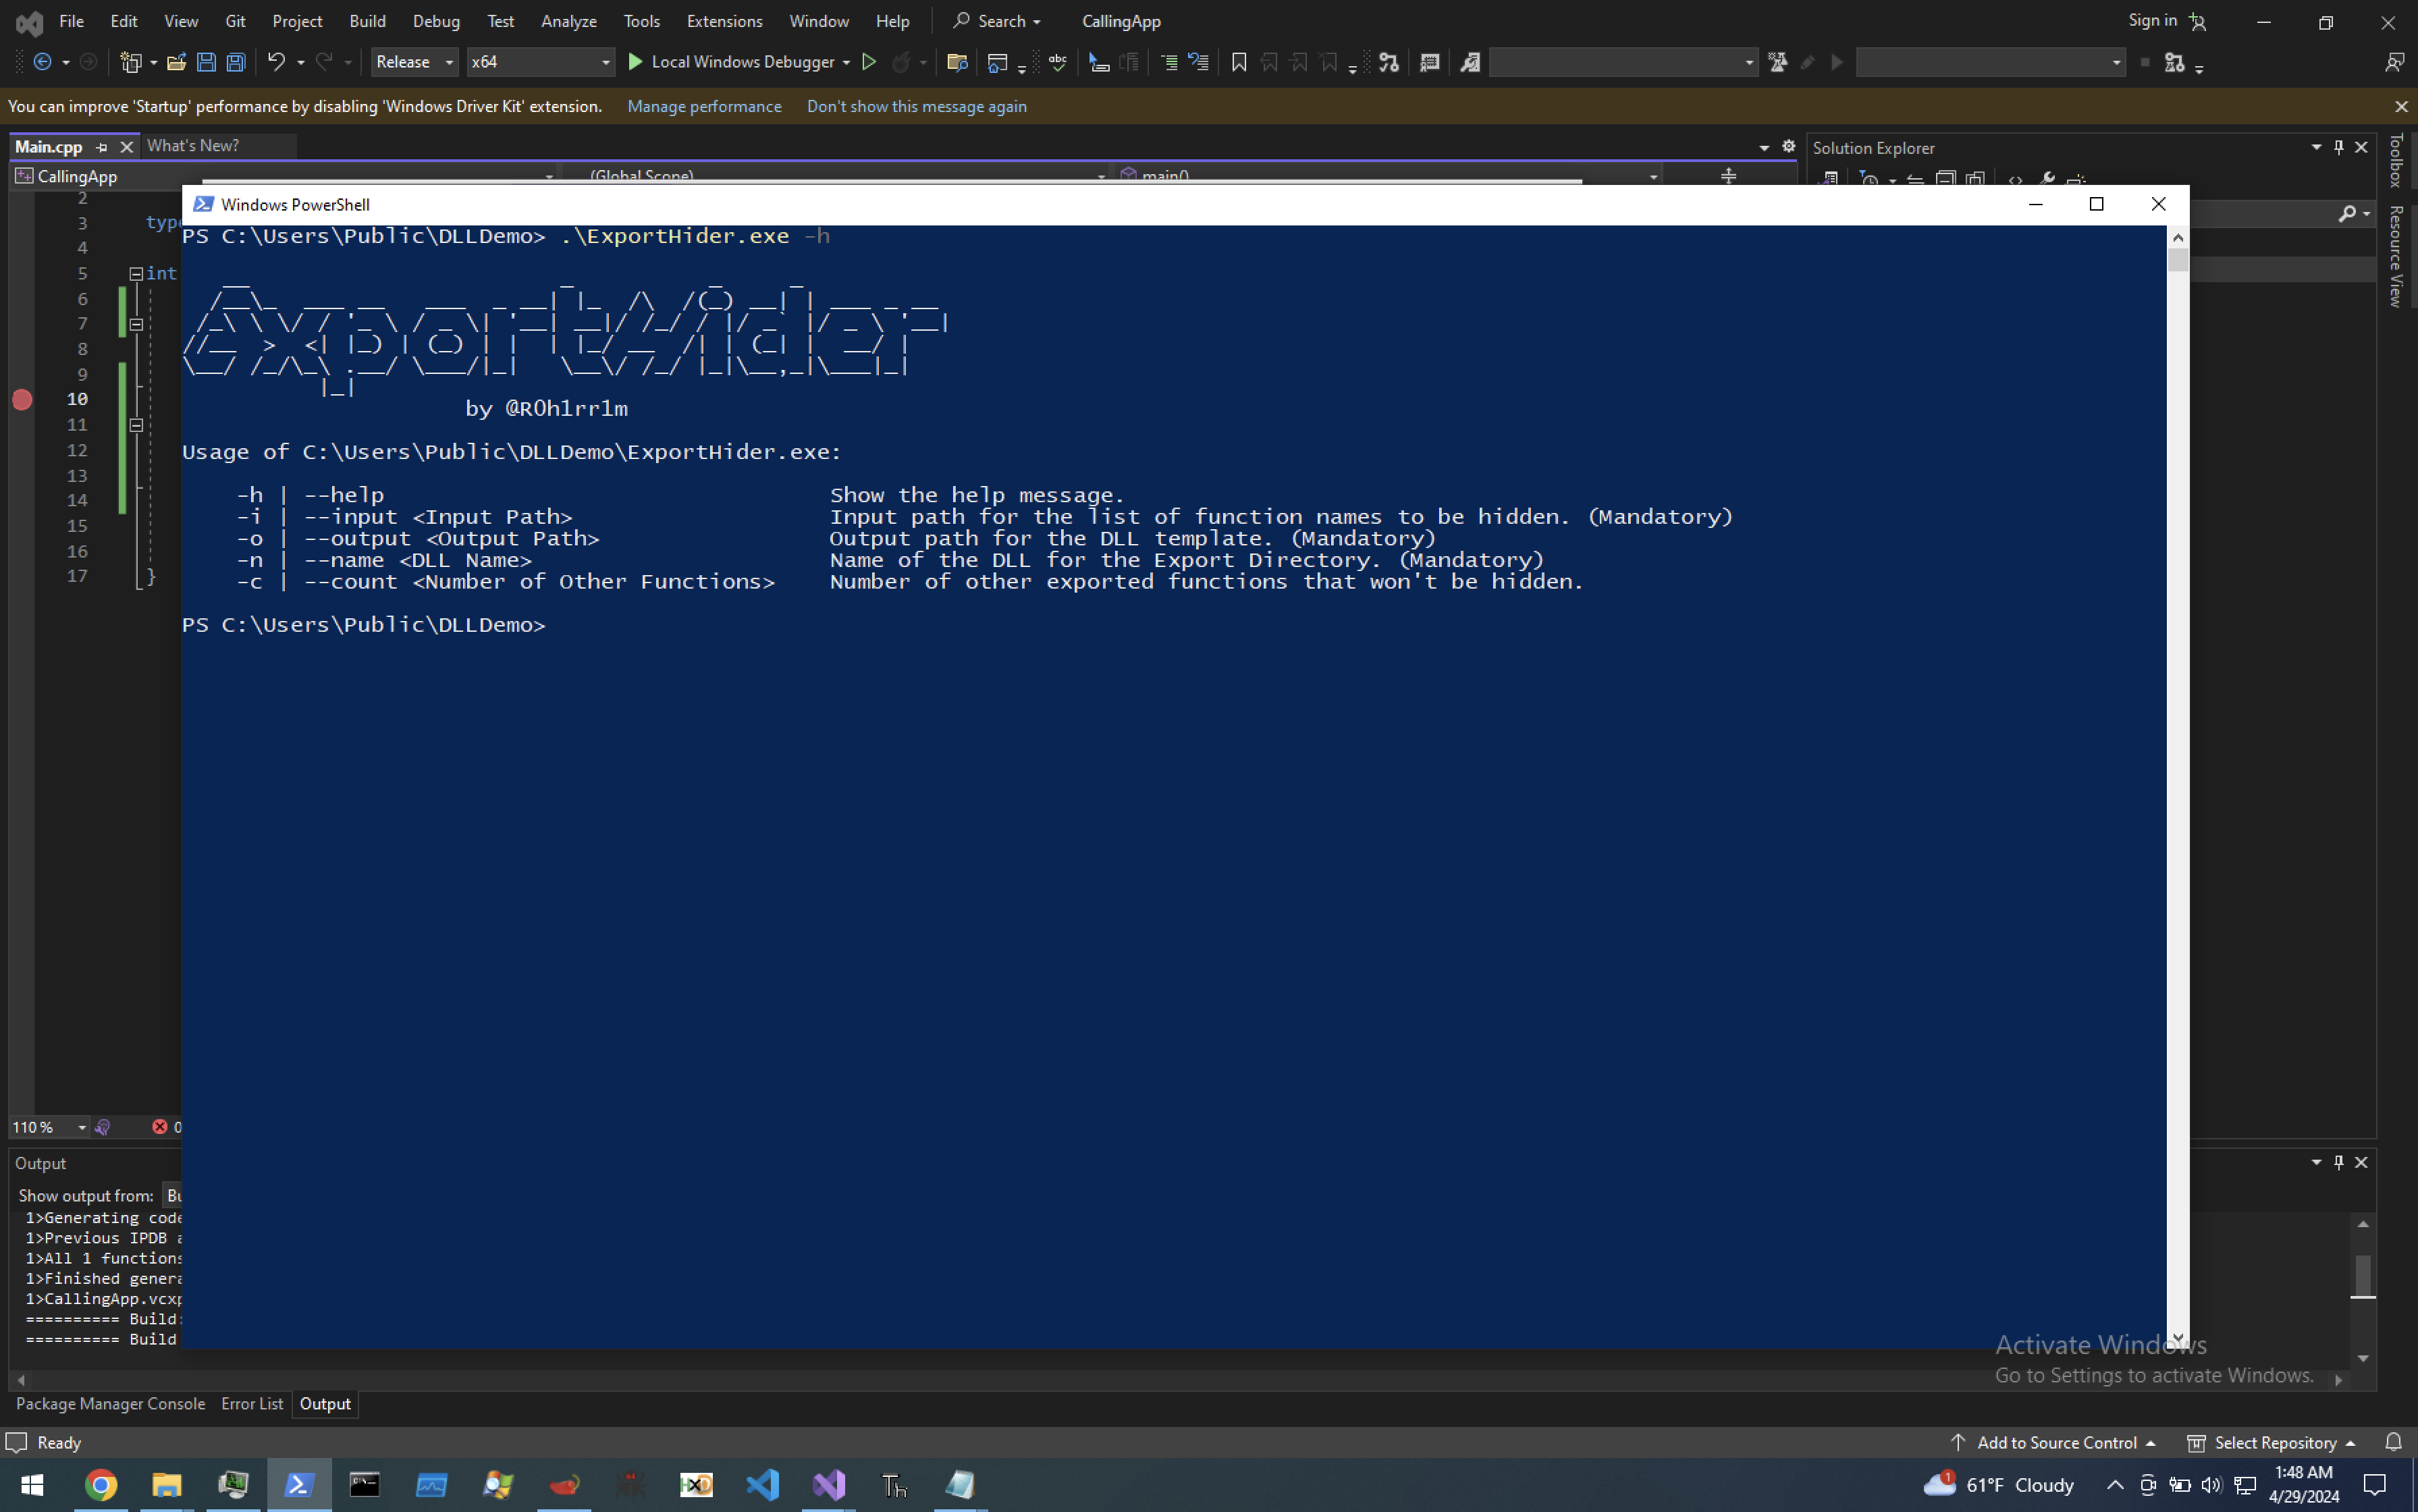 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
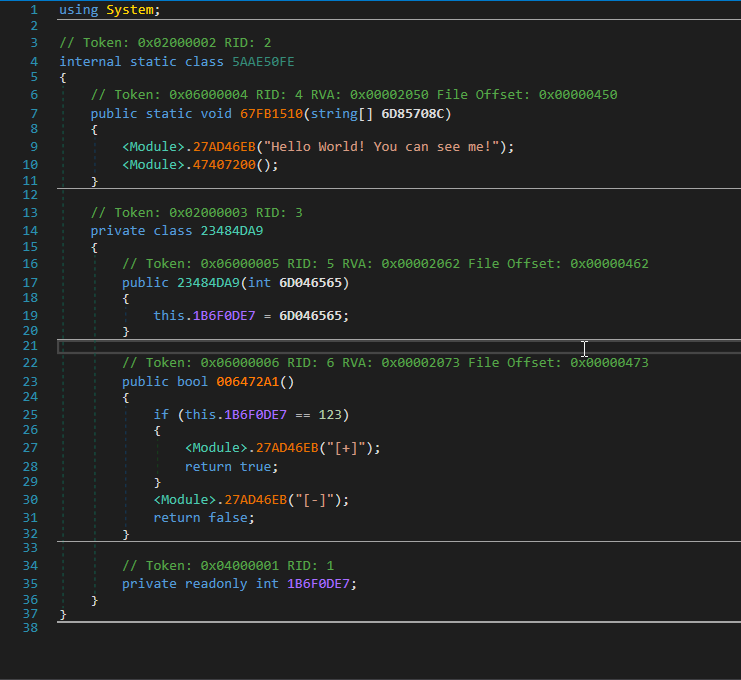 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
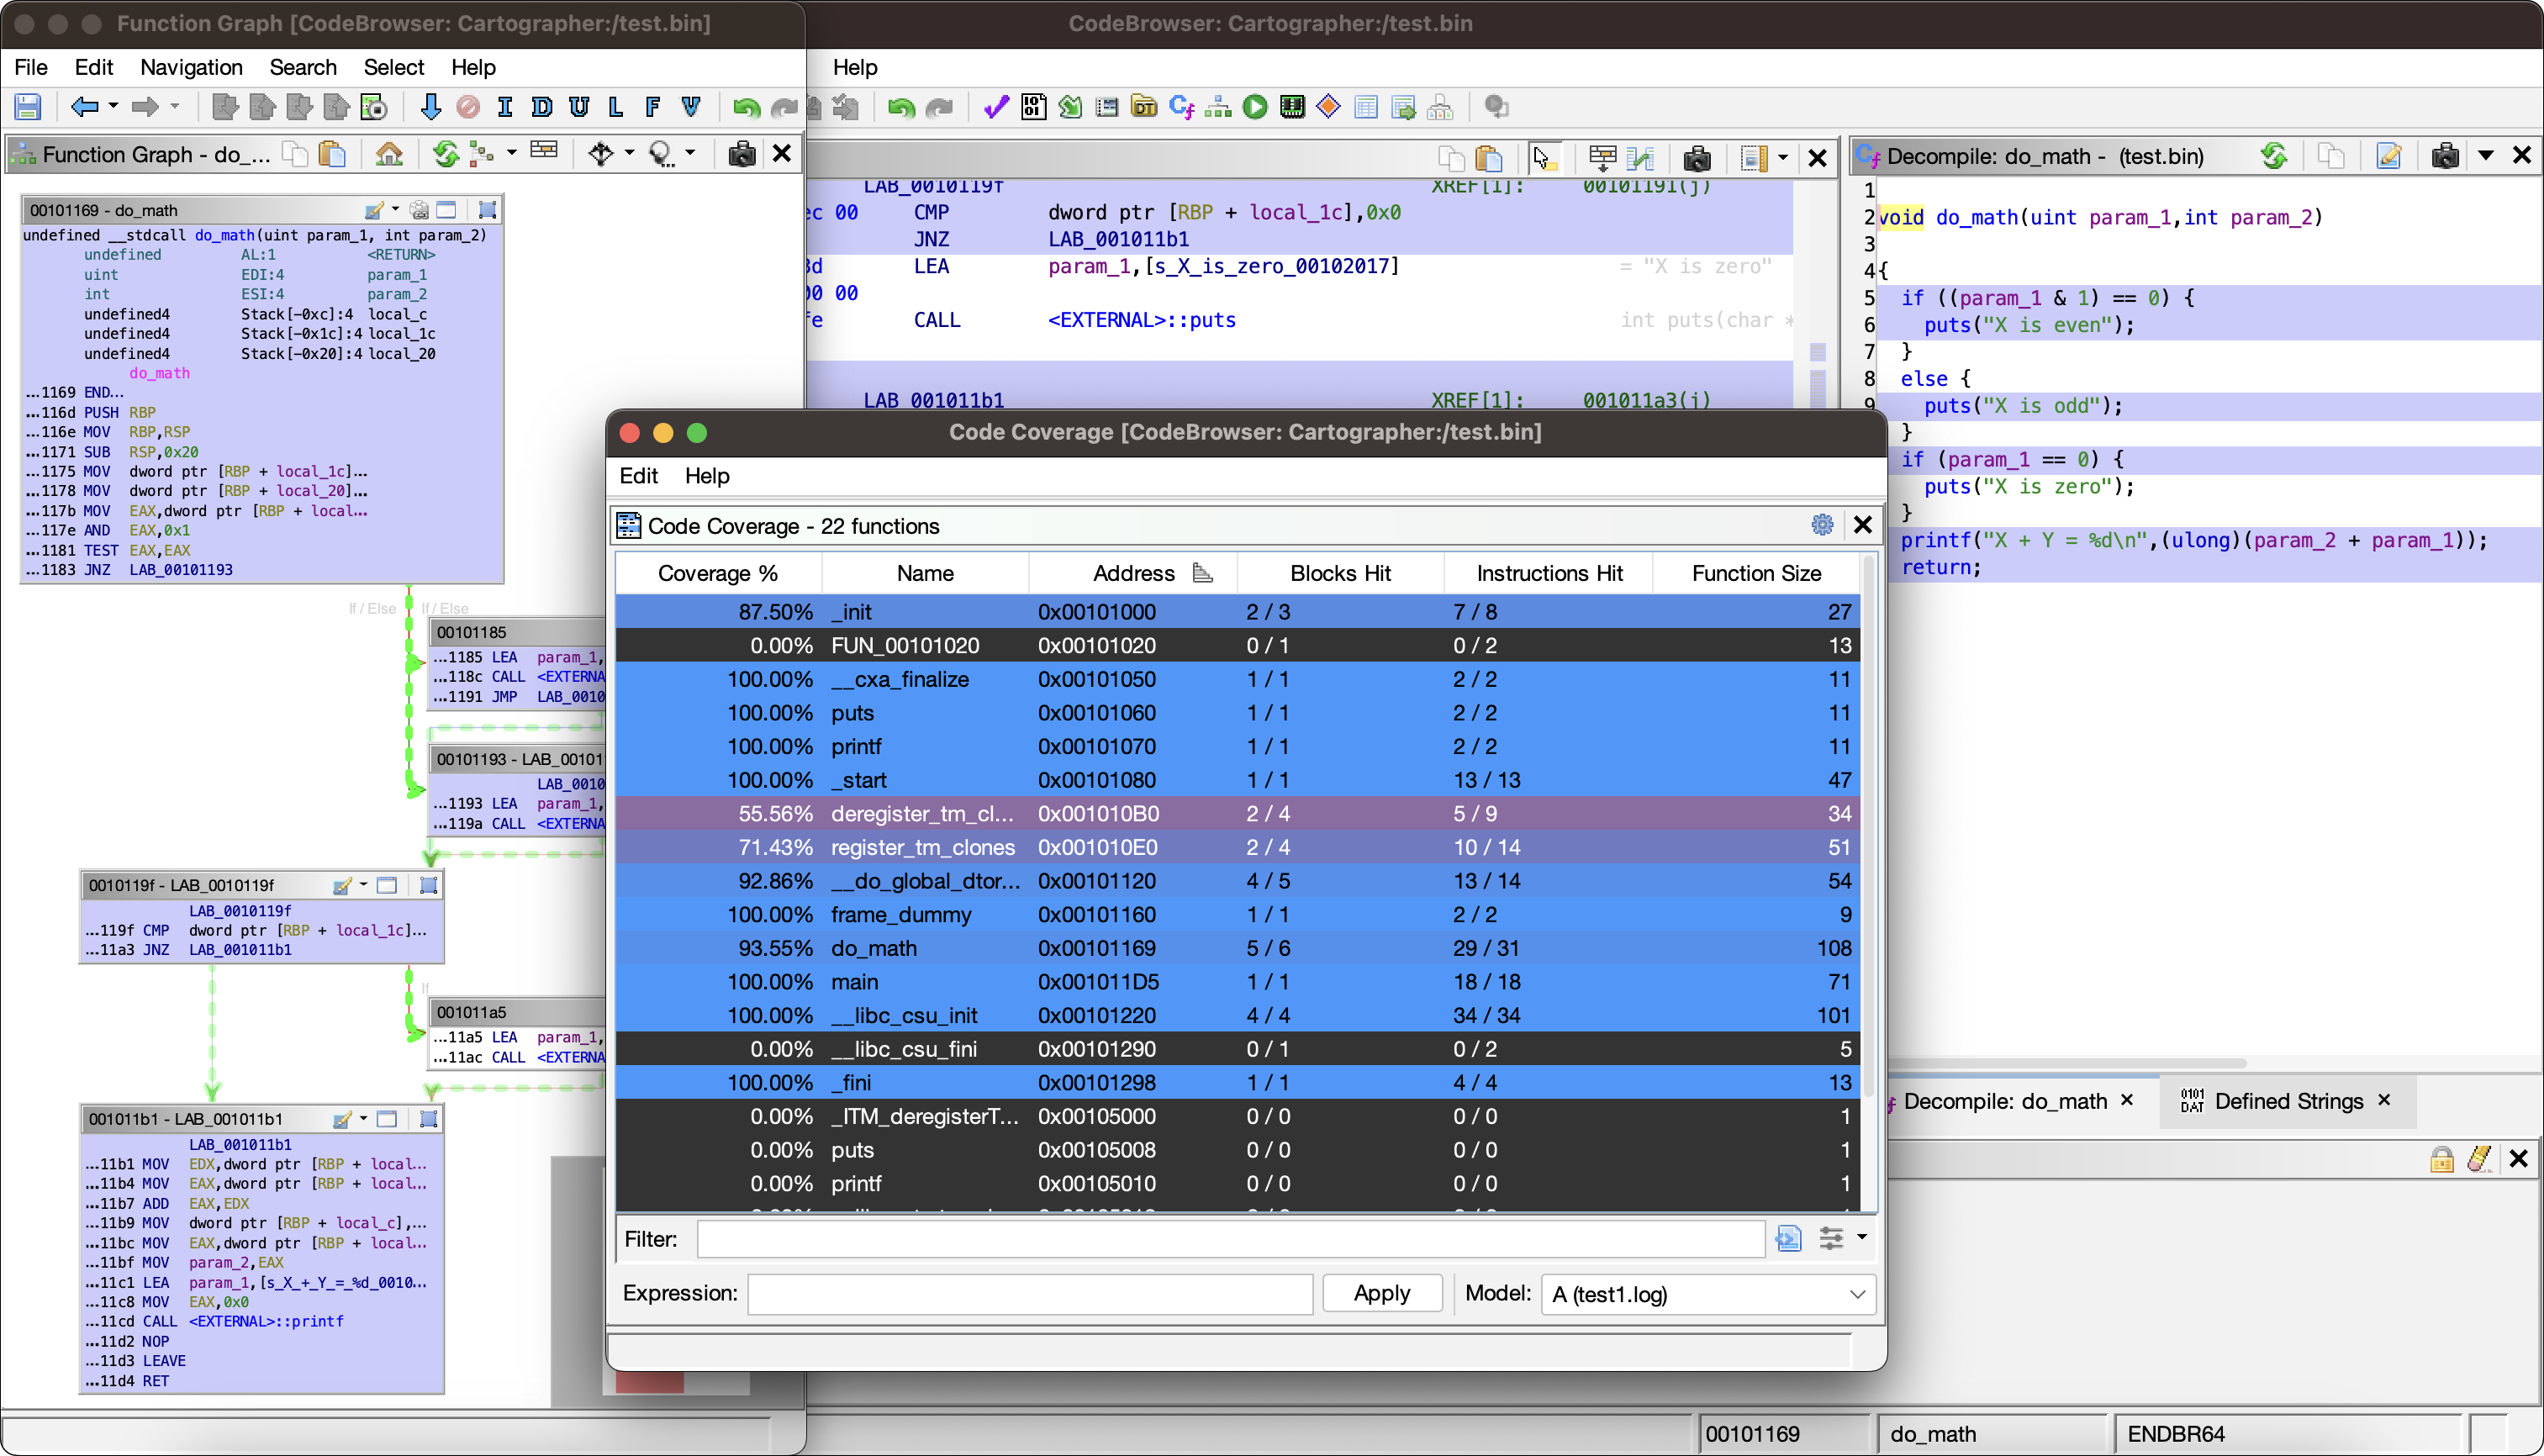 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
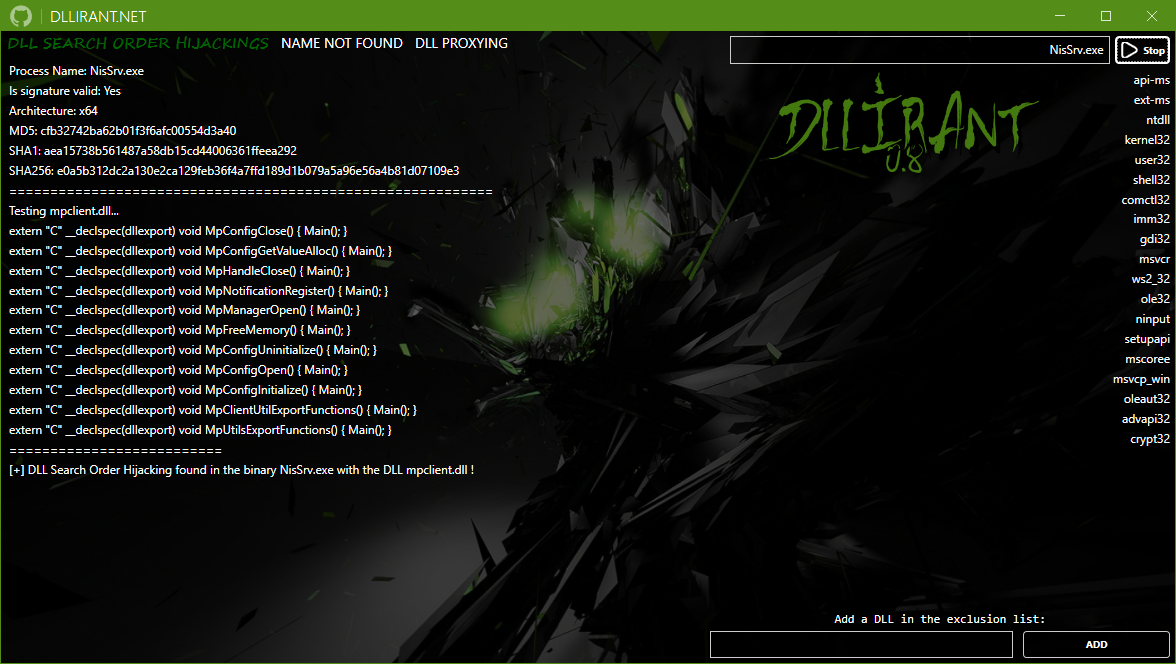 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
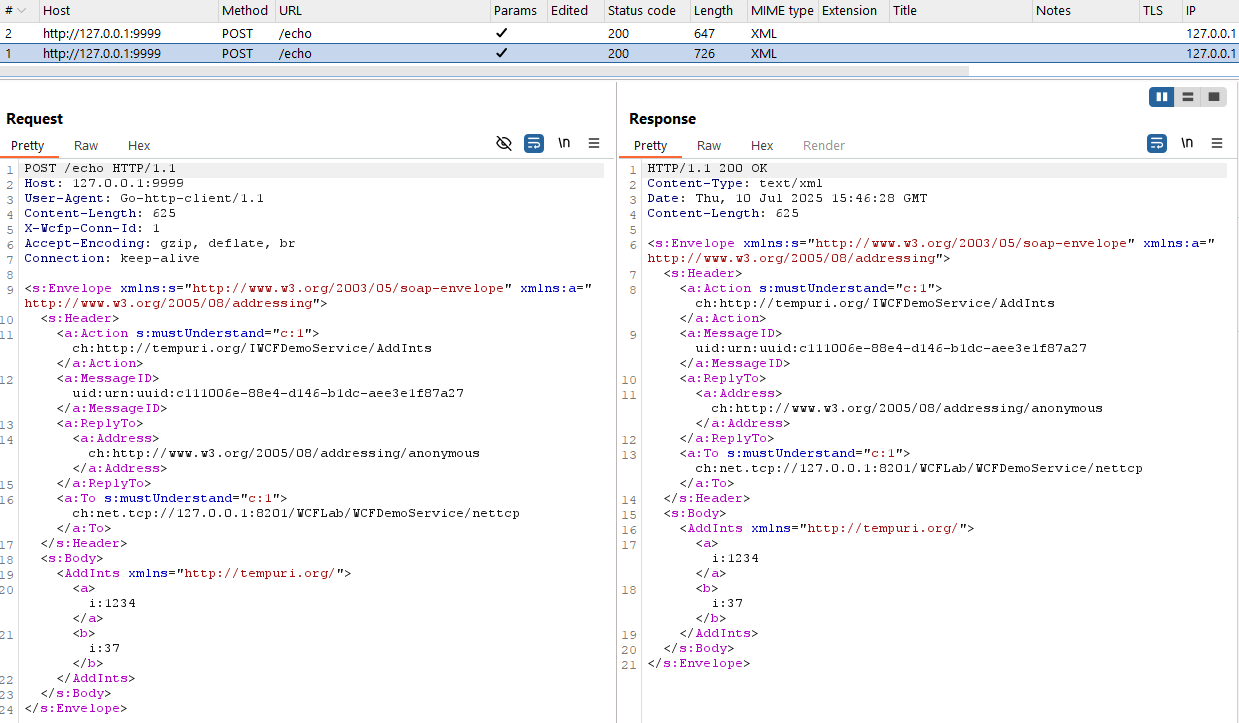 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…