ghidra-firmware-utils

Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…

Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…

IoT firmware identification and extraction

Extract files from any kind of container formats

Reverse-engineered docs and tools for 8BitDo firmware encryption methods

Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

An impish, cross-platform binary parsing crate, written in Rust

idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro

Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…


Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…

DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.

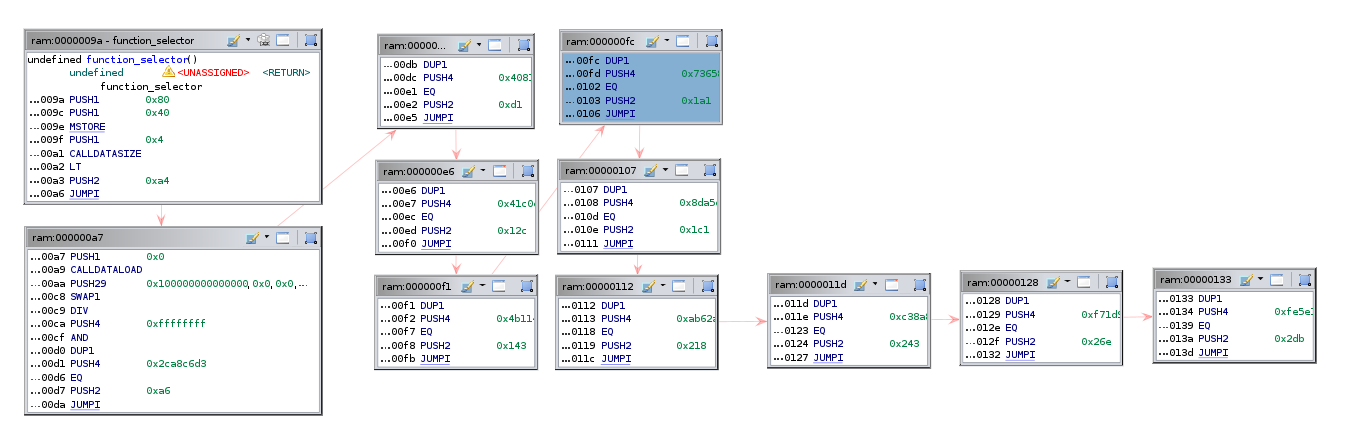
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…

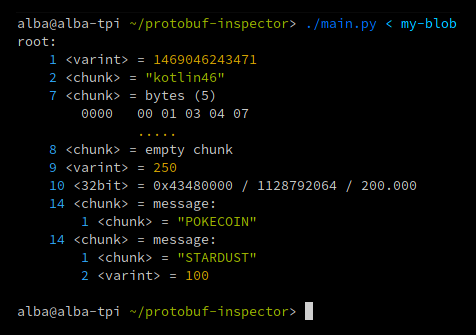
🕵️ Tool to reverse-engineer Protocol Buffers with unknown definition

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.