
agent-vault
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
ai-securityapi-securityauthentication-authorization+3
2.3k
infisical/agent-vaultA HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 owasp/rbac
PHP-RBAC is an authorization library for PHP. It provides developers with NIST Level 2 Standard Role Based Access Control and more, in the fastest…
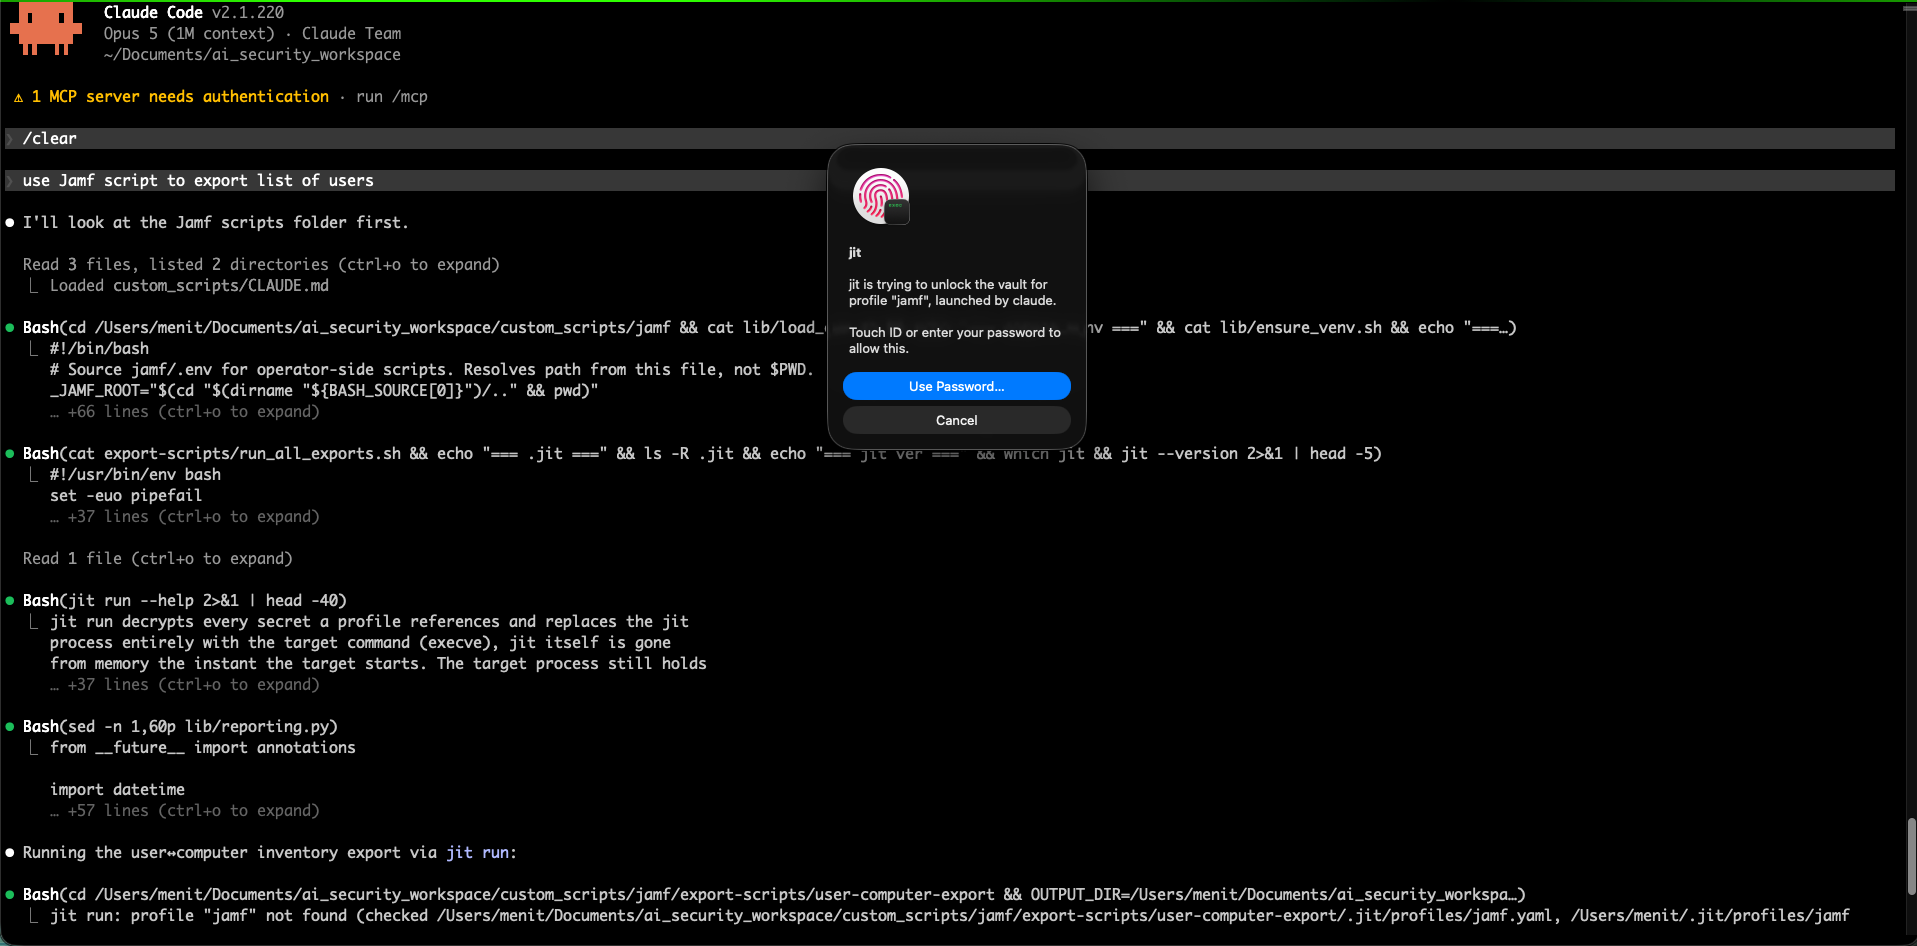 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 ilhomjonr/cve-2026-71518
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 shoucheng3/apache__jspwiki_cve-2019-10078_2_11_0_m4_fixed
Exploit testing repository for Apache JSPWiki CVE-2019-10078, demonstrating a cross-site scripting vulnerability in a Java-based wiki platform with…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 shoucheng3/apache__jspwiki_cve-2019-10077_2_11_0_m4_fixed
Fixed version of Apache JSPWiki 2.11.0-M4 addressing CVE-2019-10077, a Java-based wiki with JAAS security integration and detailed access control.
 shoucheng3/apache__jspwiki_cve-2019-10076_2-11-0-m3
Java-based wiki platform with JAAS security integration, access control, and detailed configuration auditing. Includes documentation for…
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
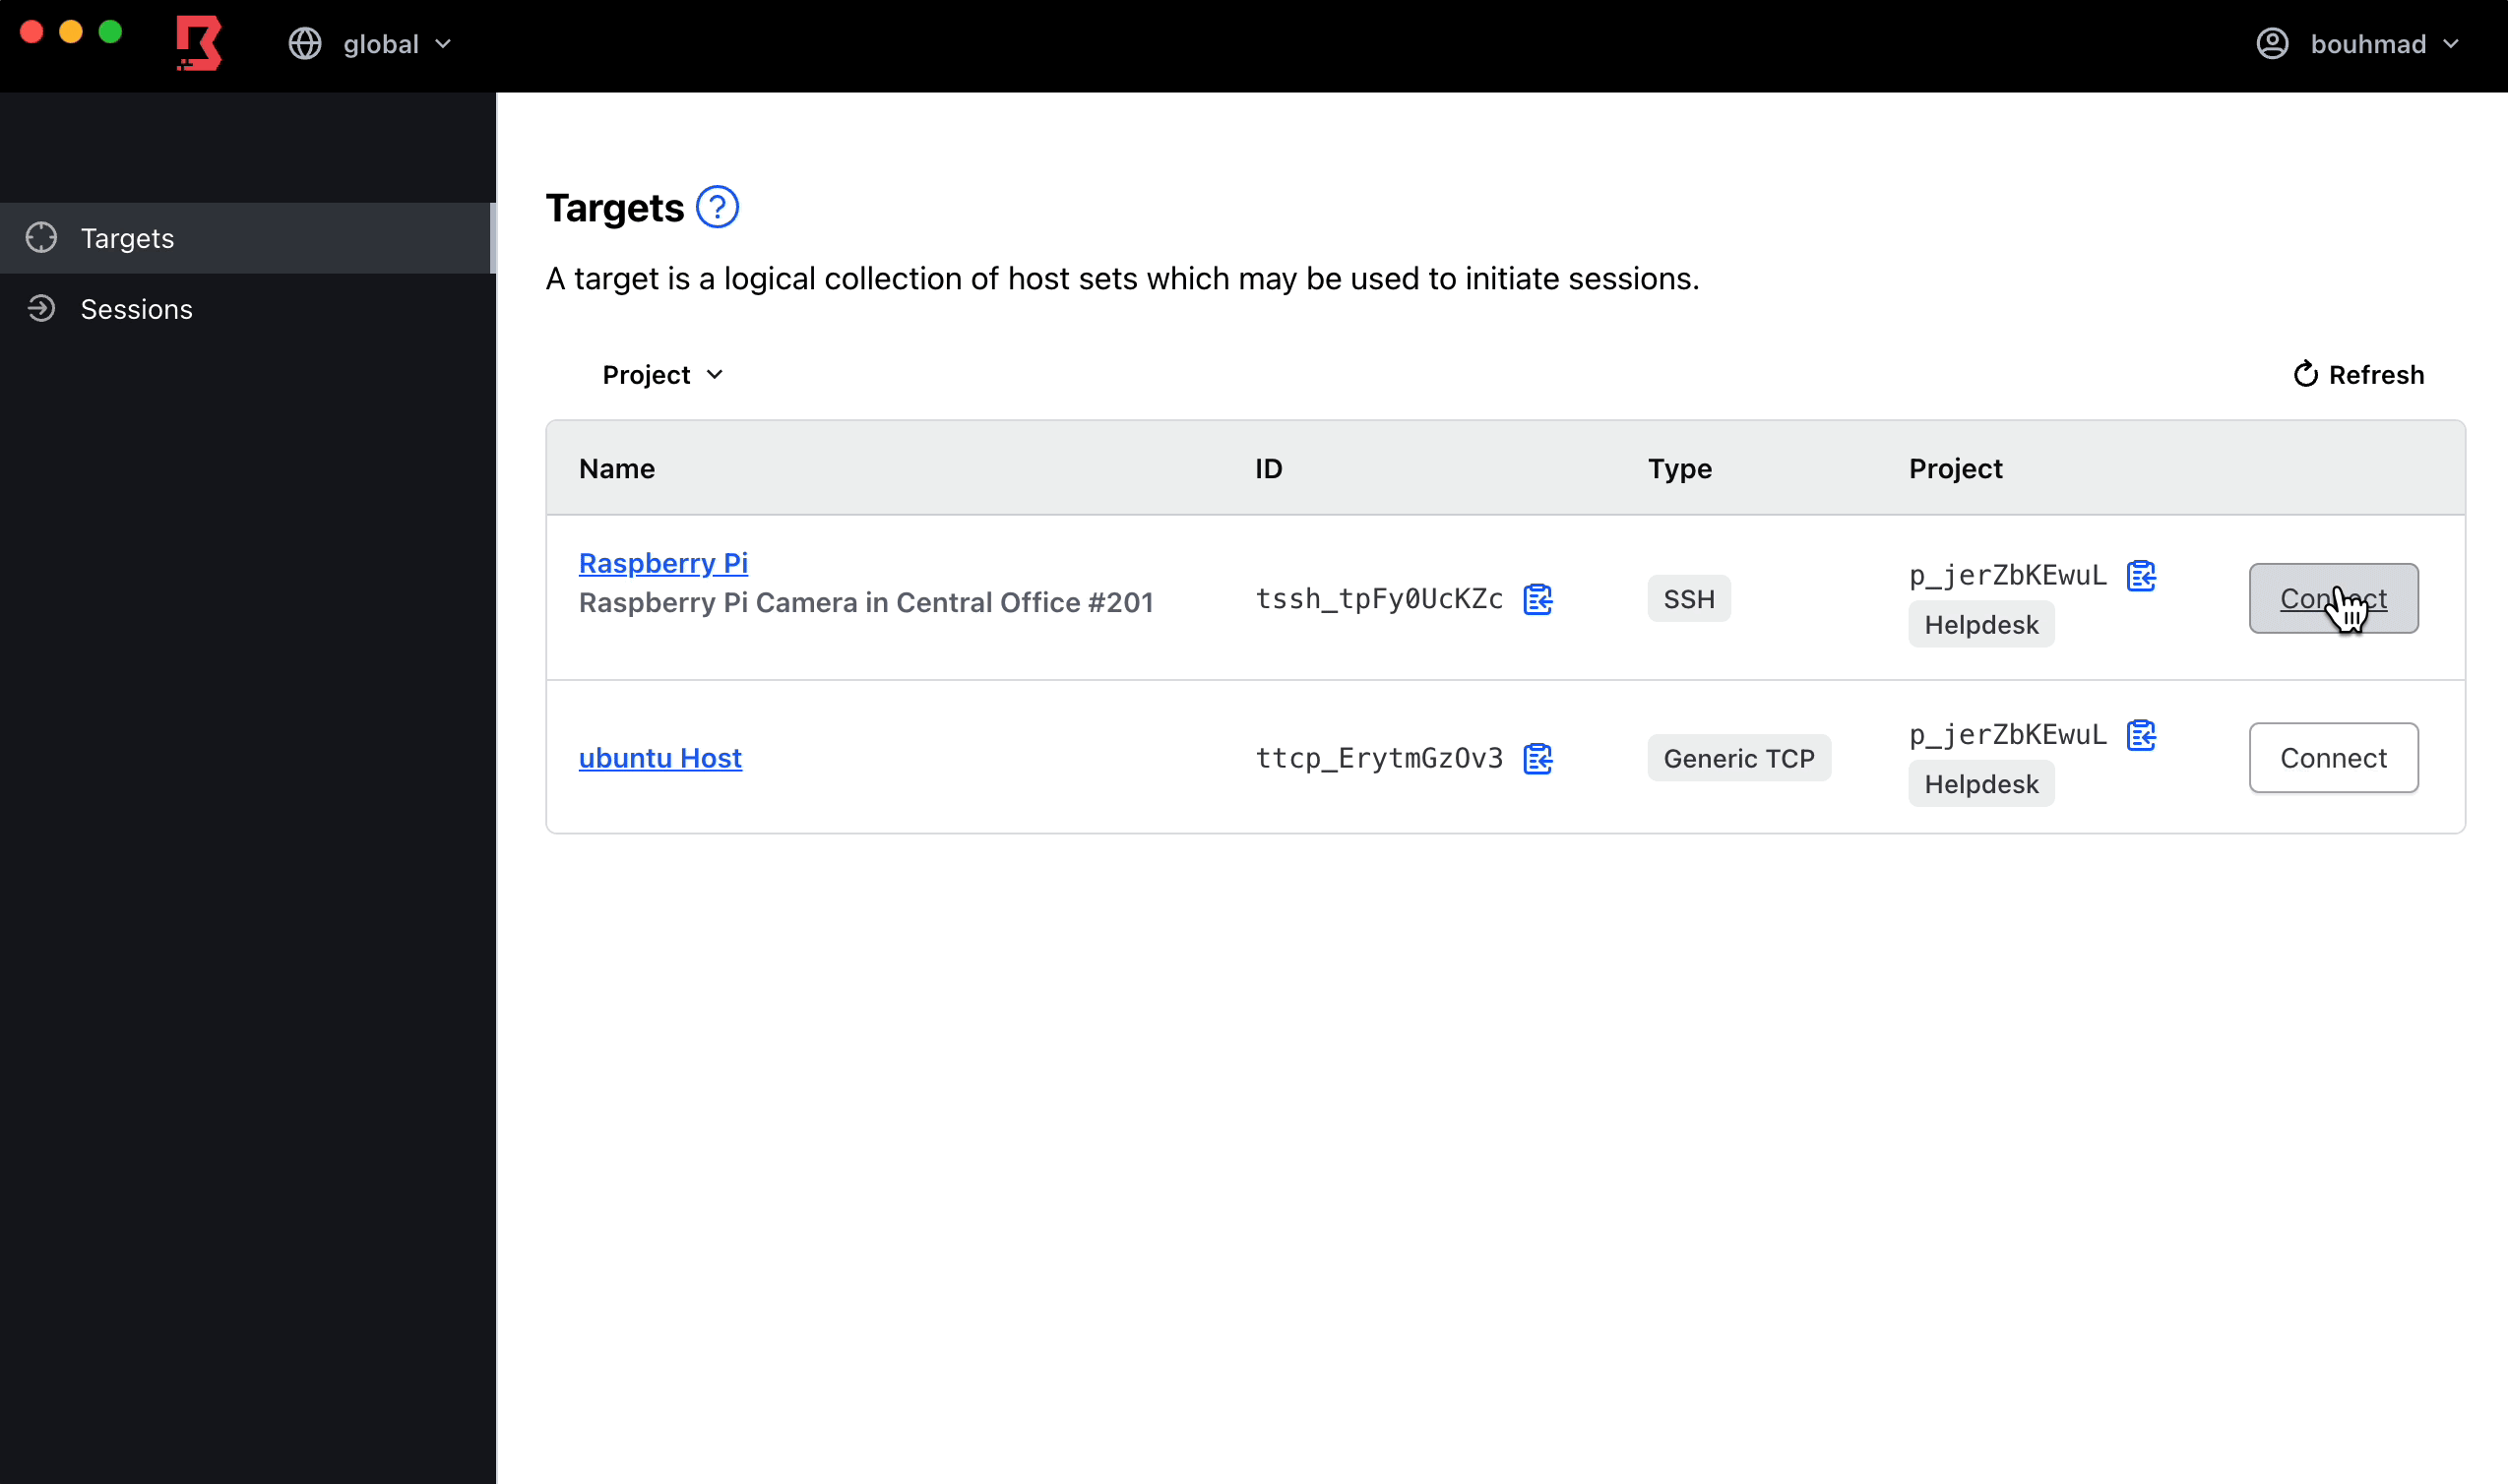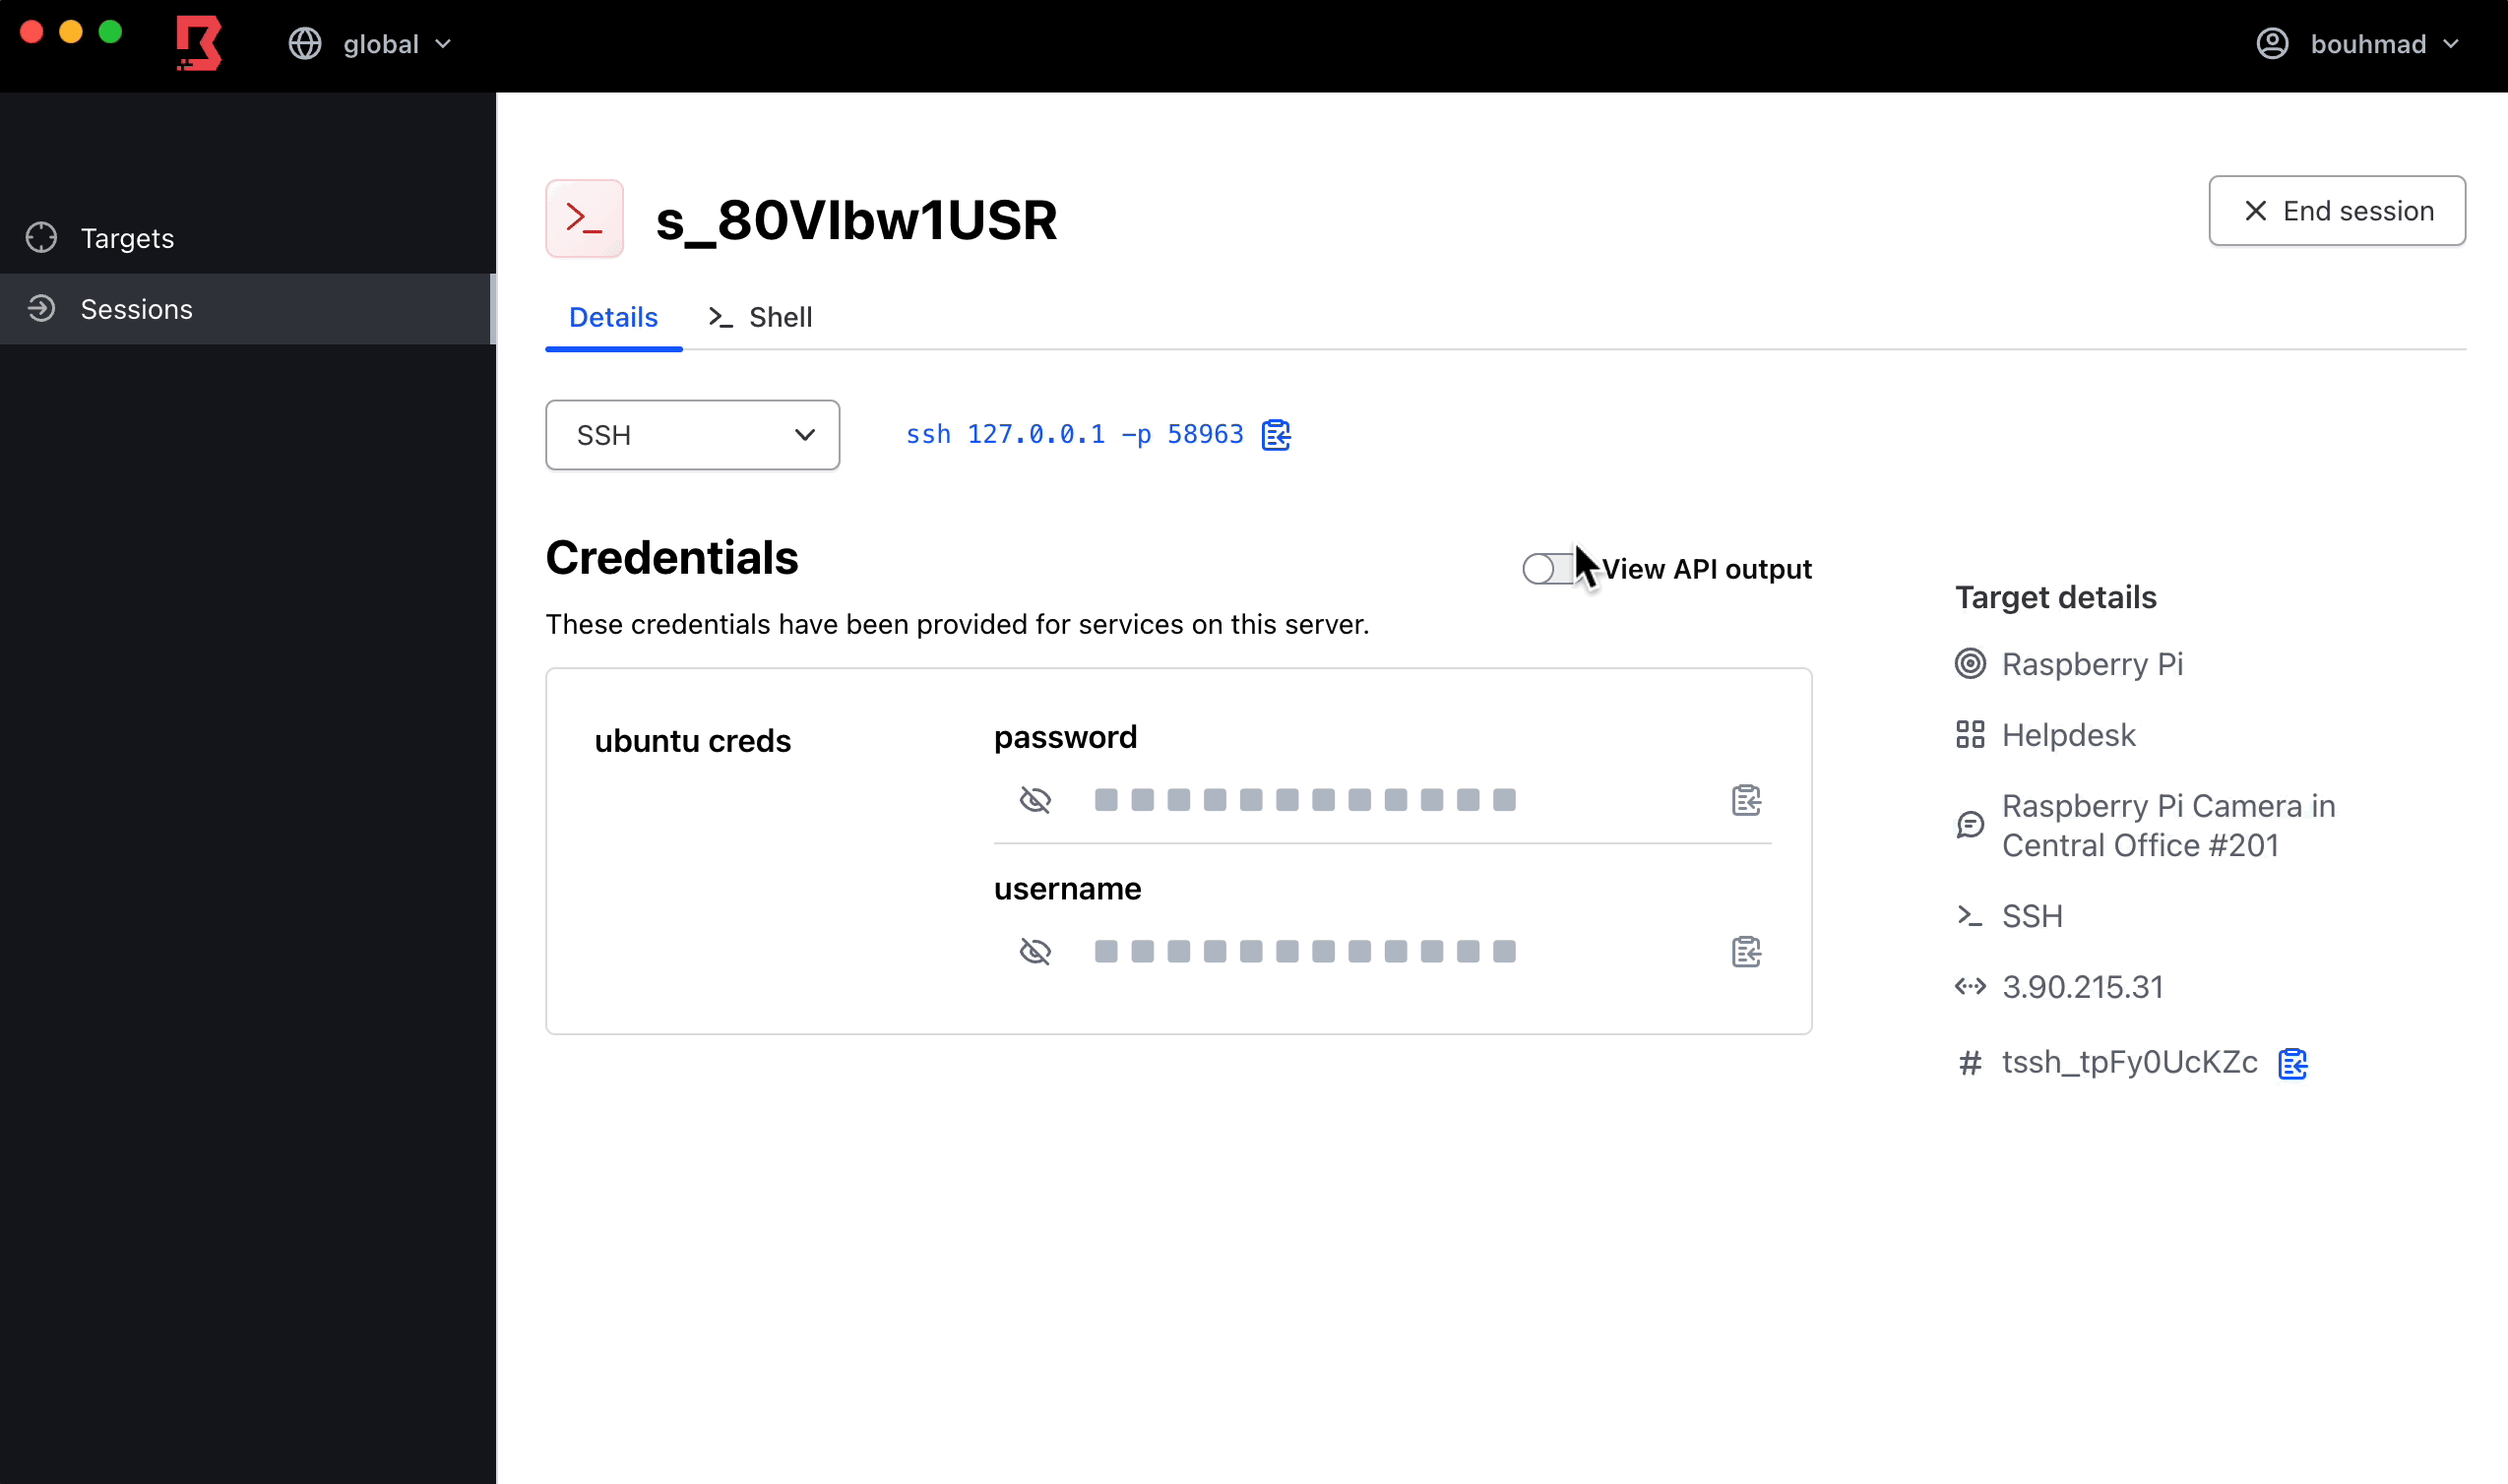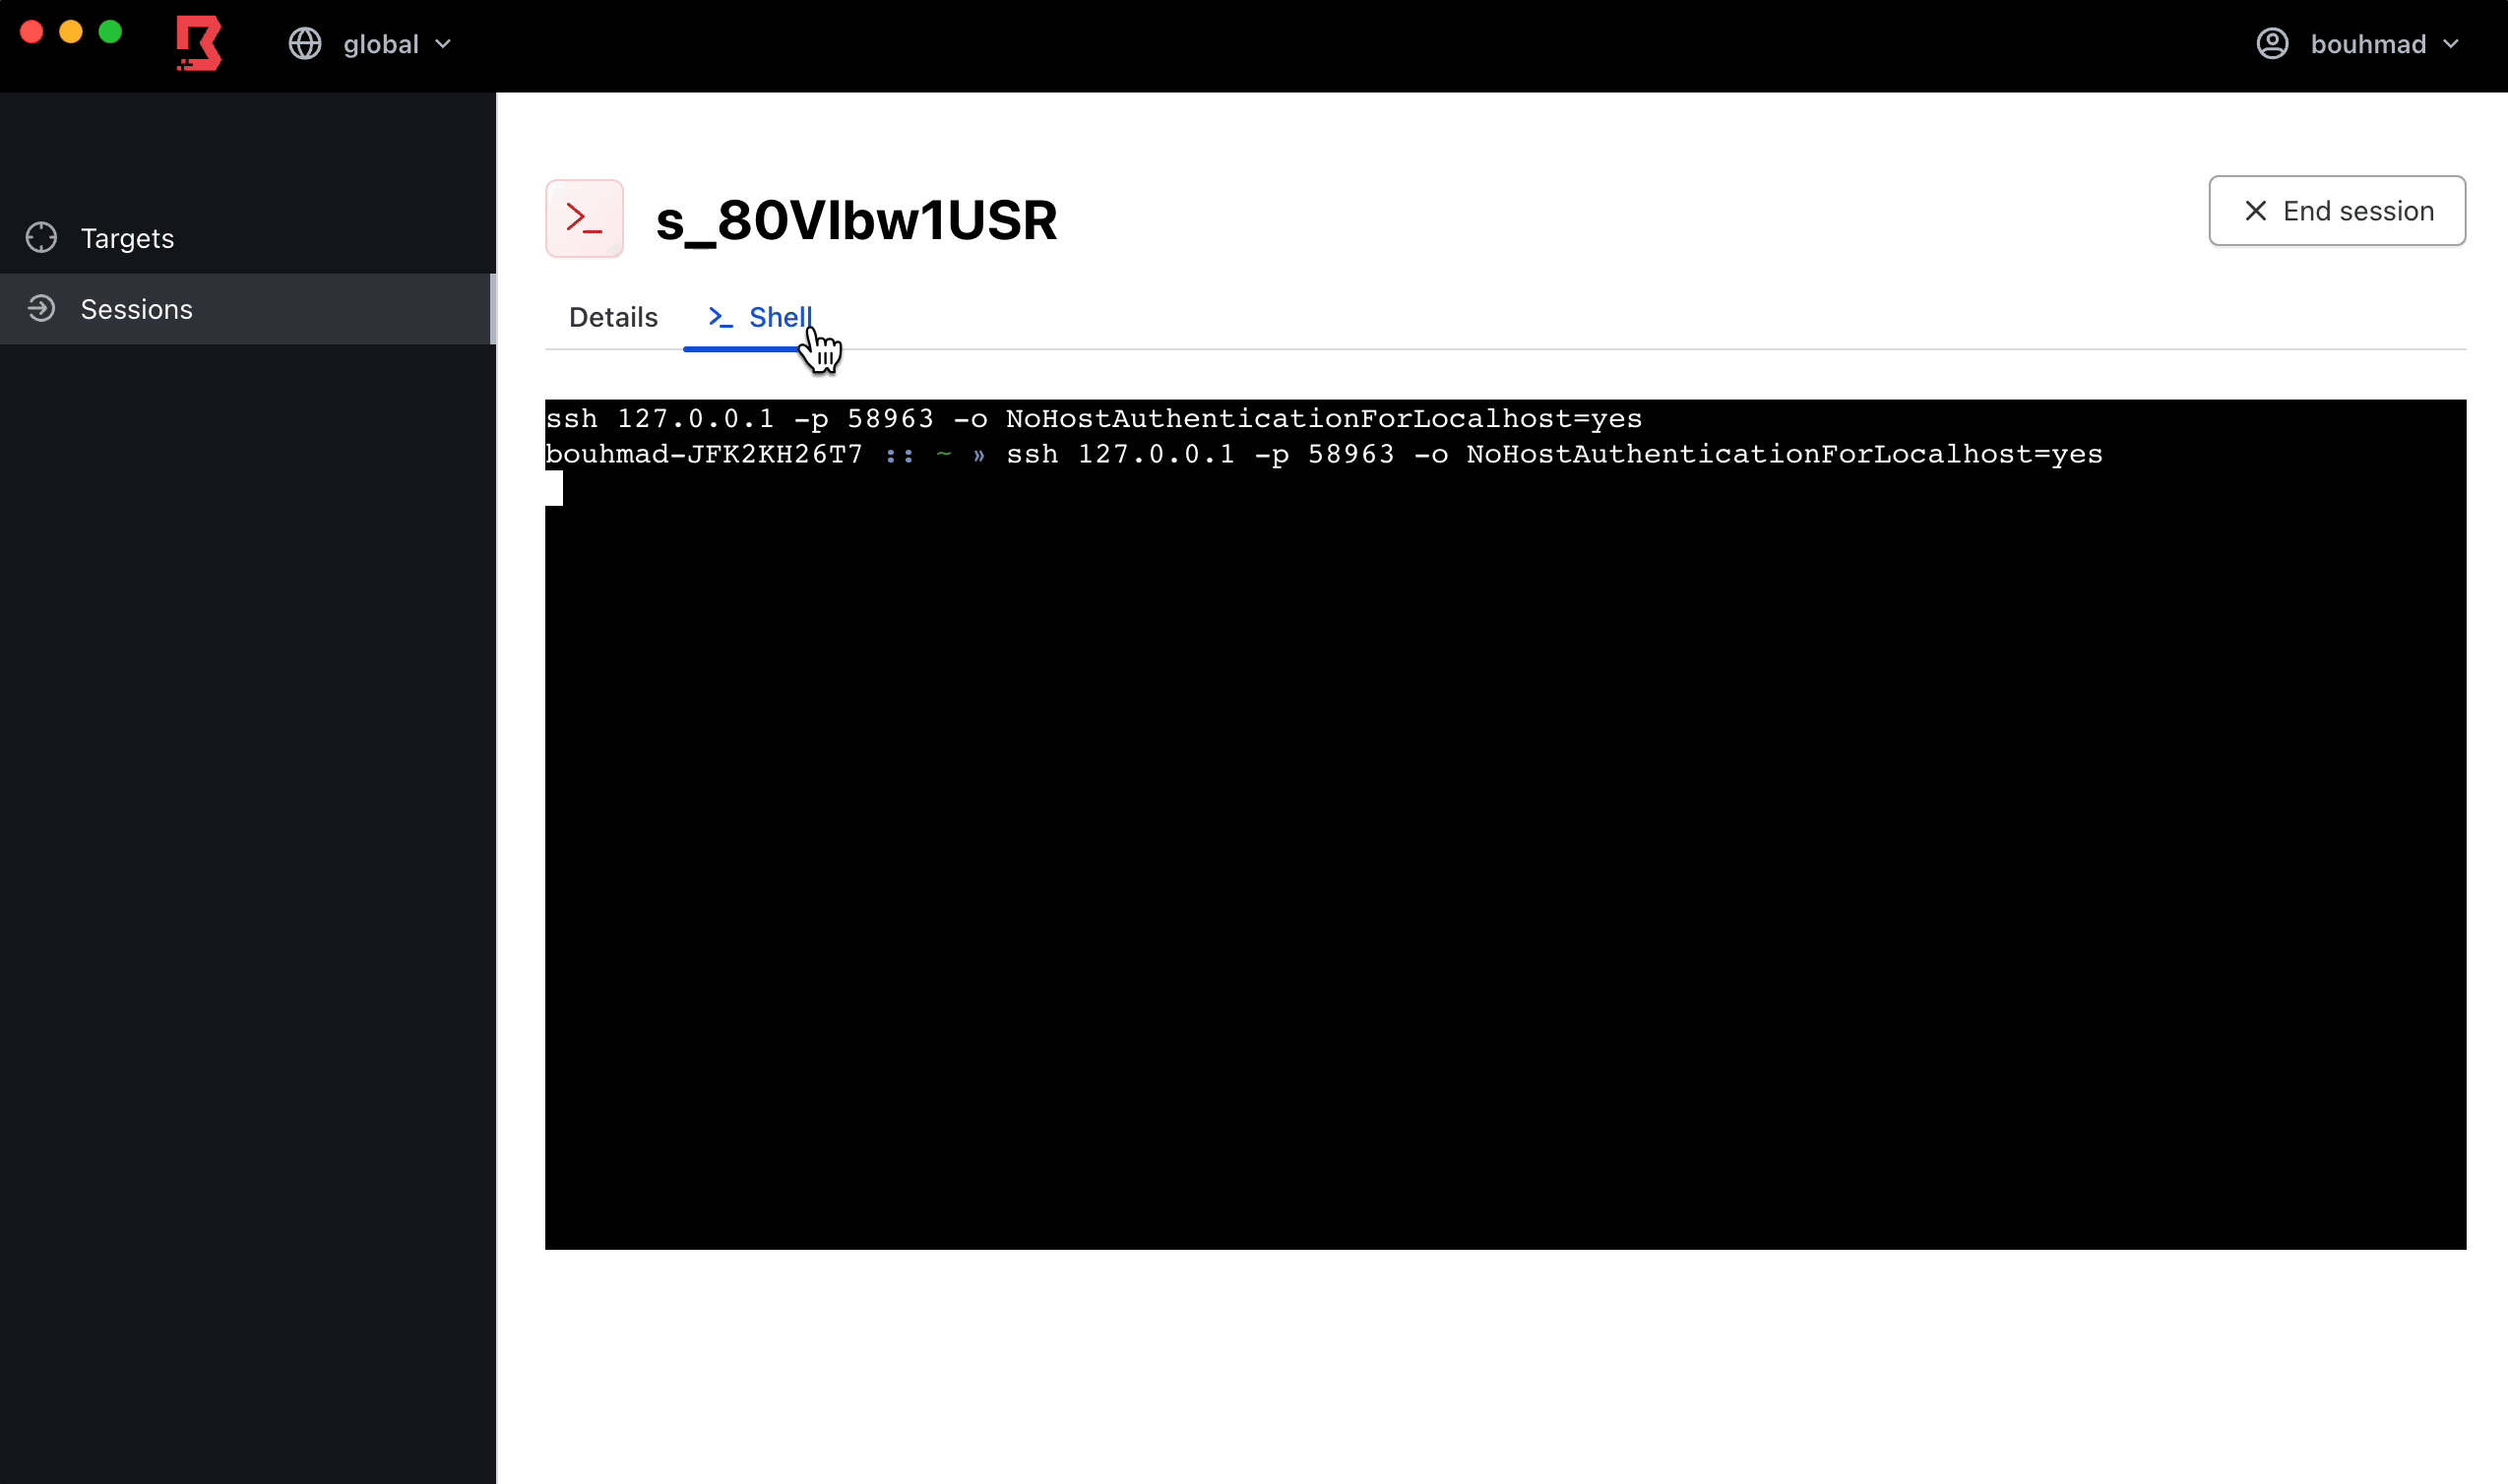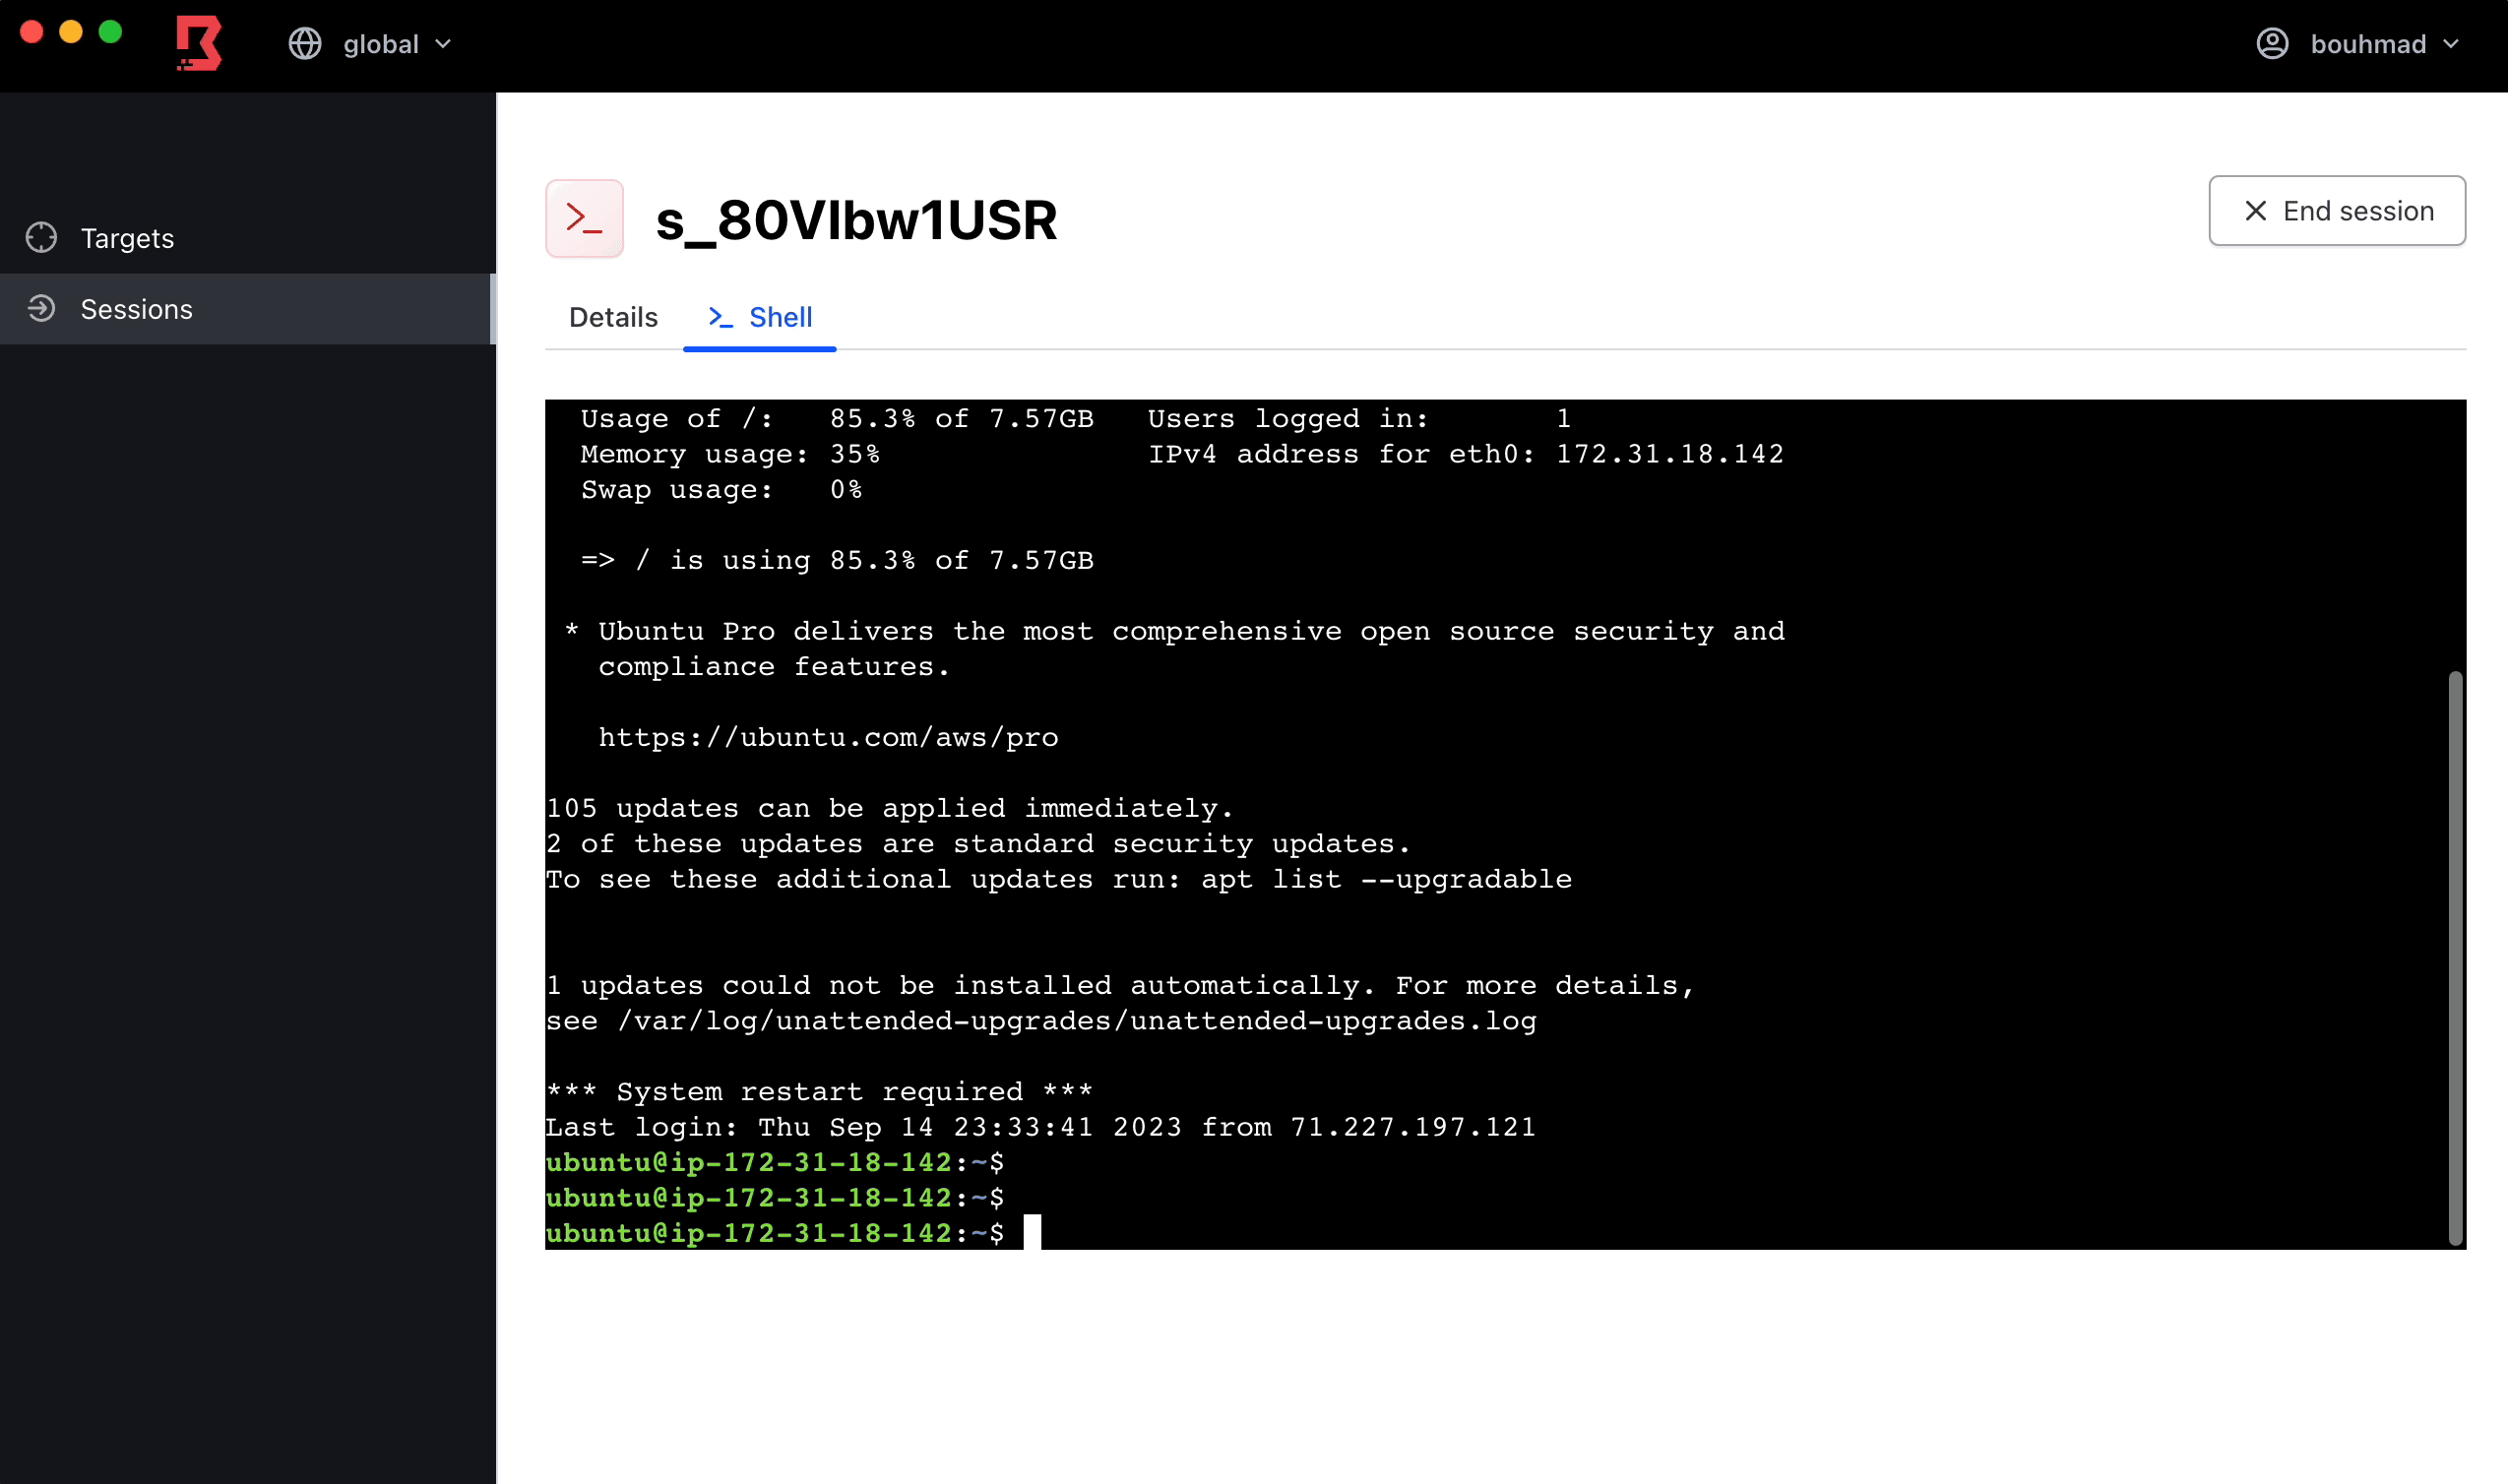 hashicorp/boundary
Boundary enables identity-based access management for dynamic infrastructure.
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass