
jwt-spoof-tool
 amr9k8/jwt-spoof-tool
Automate JWT Exploit (CVE-2018-0114)
authentication-authorizationeducationexploitation+3
amr9k8/jwt-spoof-toolAutomate JWT Exploit (CVE-2018-0114)
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 aliyabuz25/cve-2025-49173
Security research — PoC for local root privilege escalation on macOS Mavericks 10.9.
 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
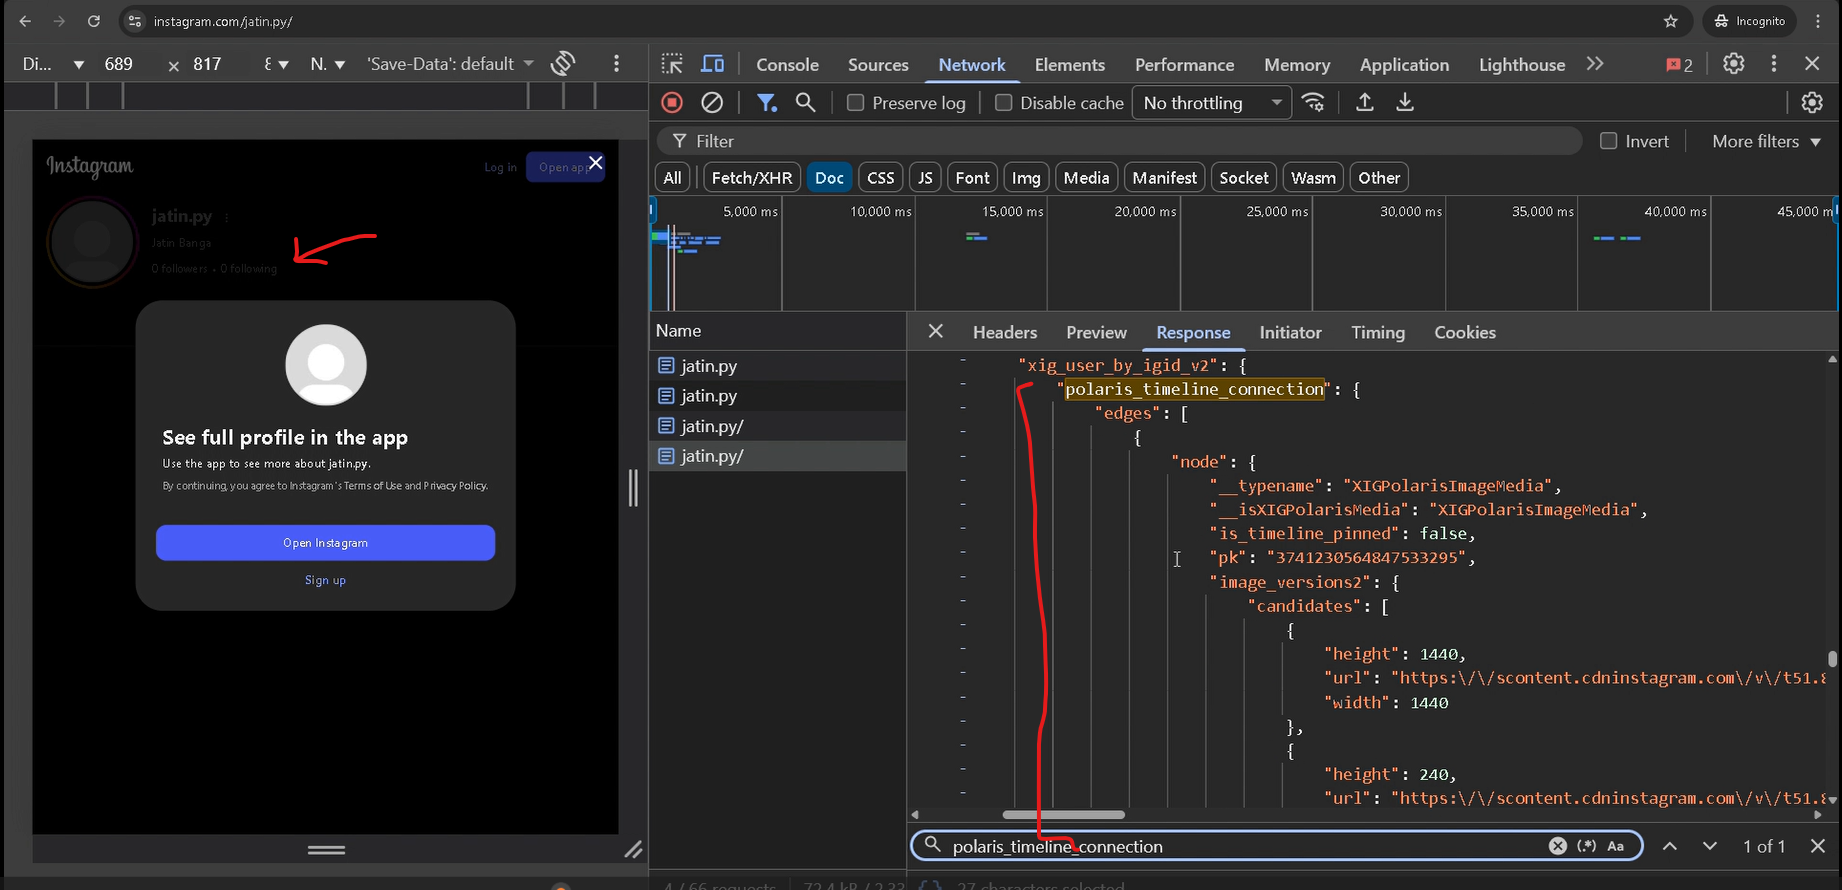 jatin-dot-py/instagram-private-bypass
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…
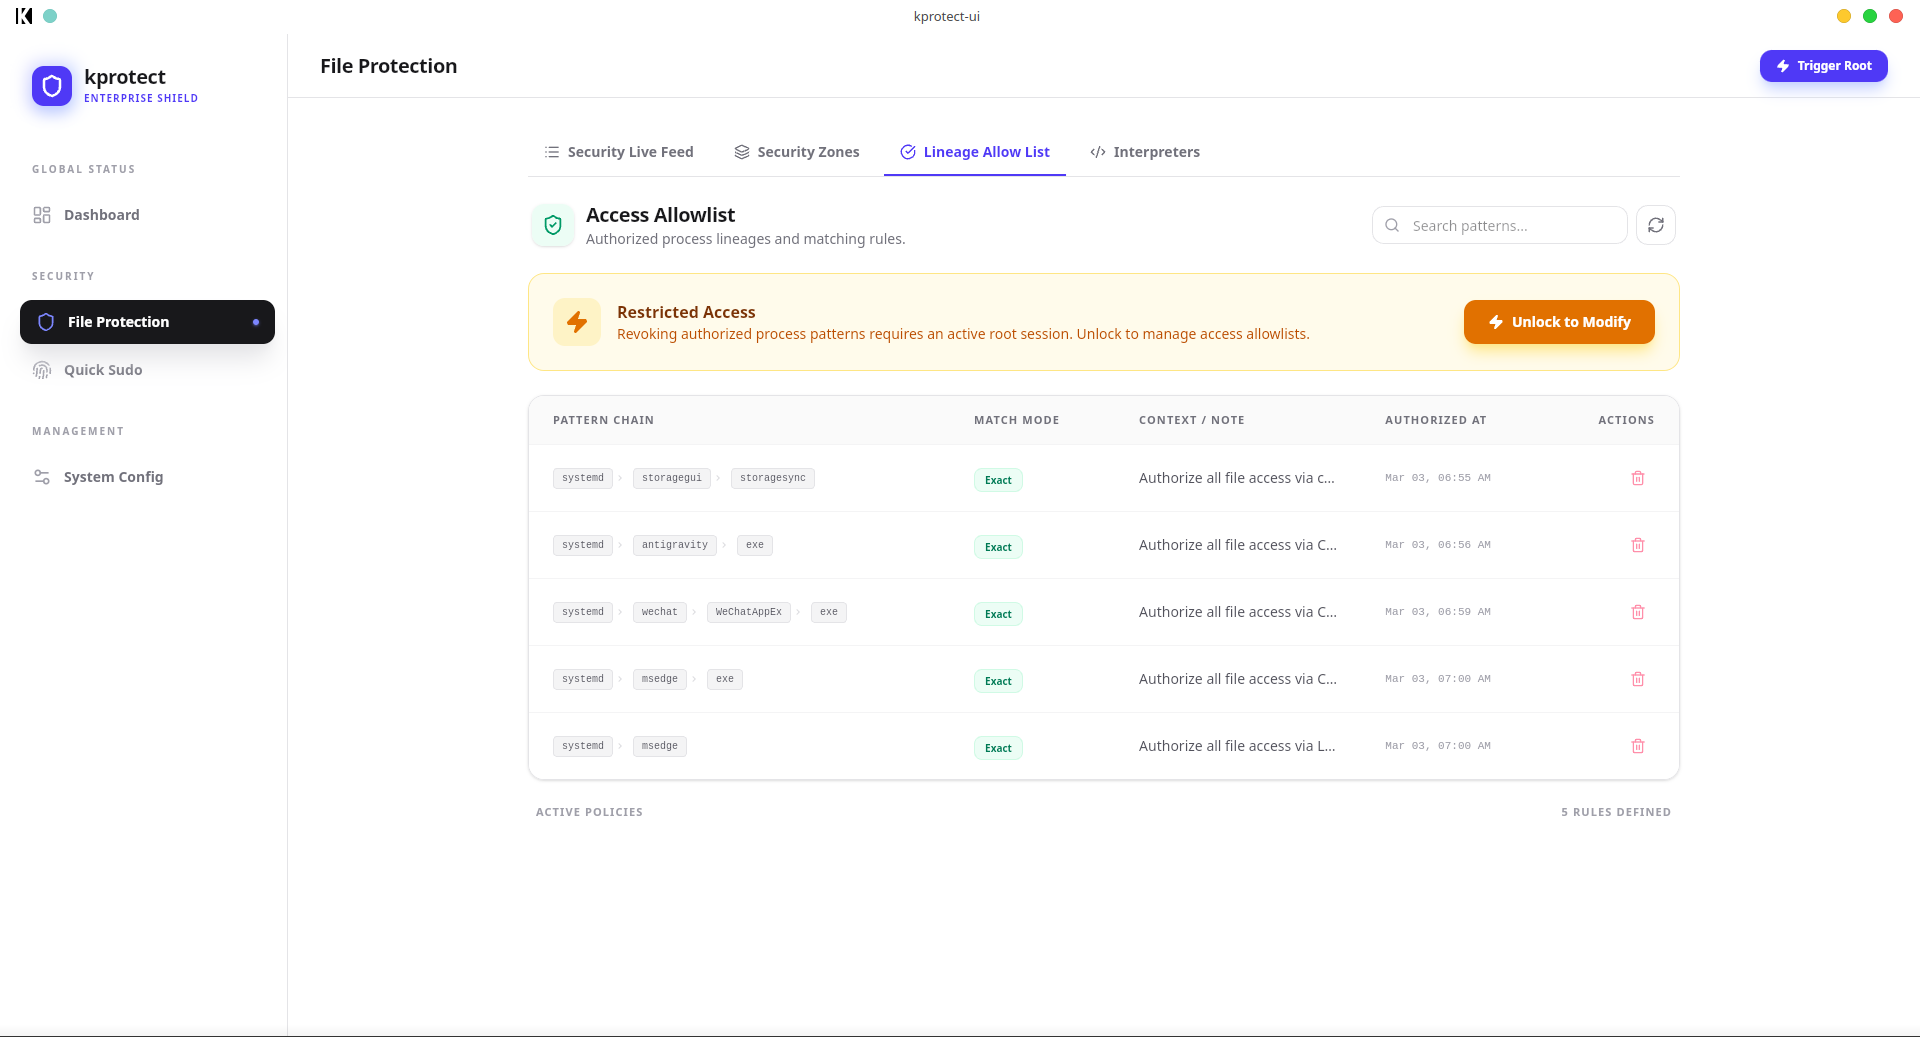 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 zs1n/cve-2025-29927
PoC | NextJS Middleware 15.2.2 - Authorization Bypass