CVE-2022-36537
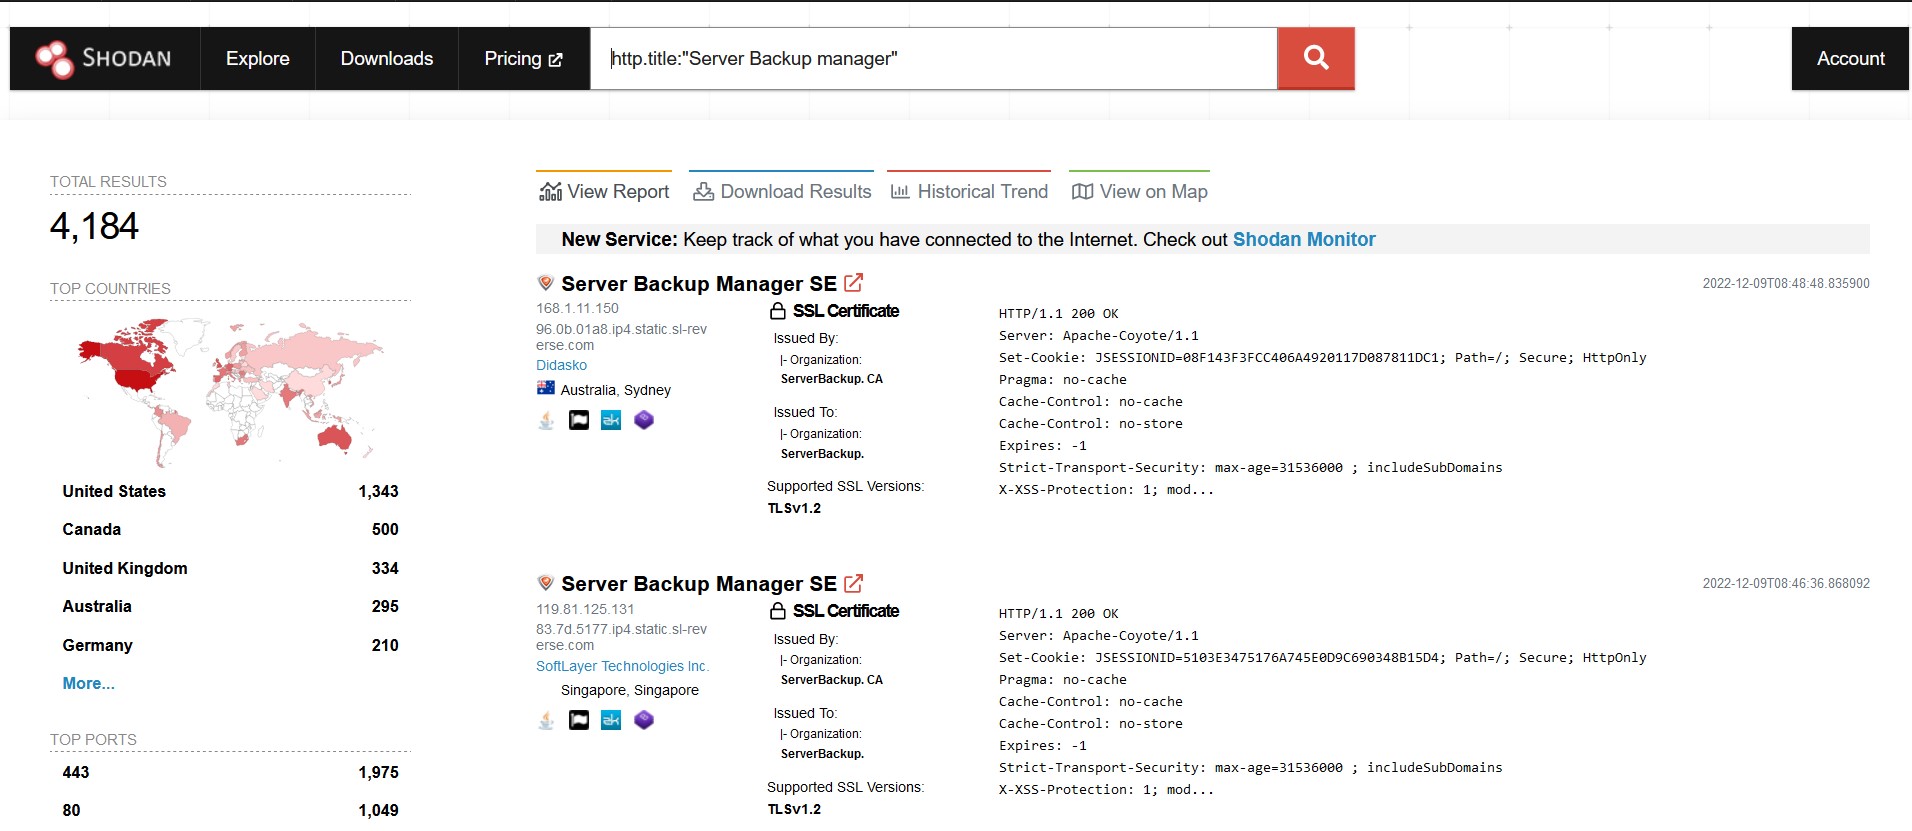
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…

Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…

POC of CVE-2022-36537

CVE-2022-36537

Documentation of CVE-2026-26418, a missing authentication and authorization vulnerability in TCS Cognix Recon Client v3.0 Web API, including affected…

Squid Web Proxy Cache - Source Code

Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…

Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams

KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…

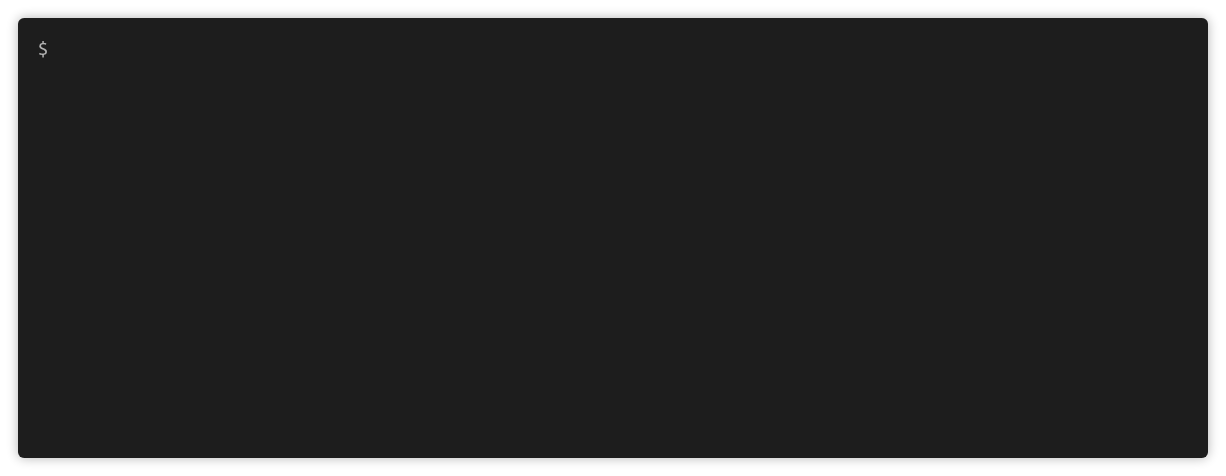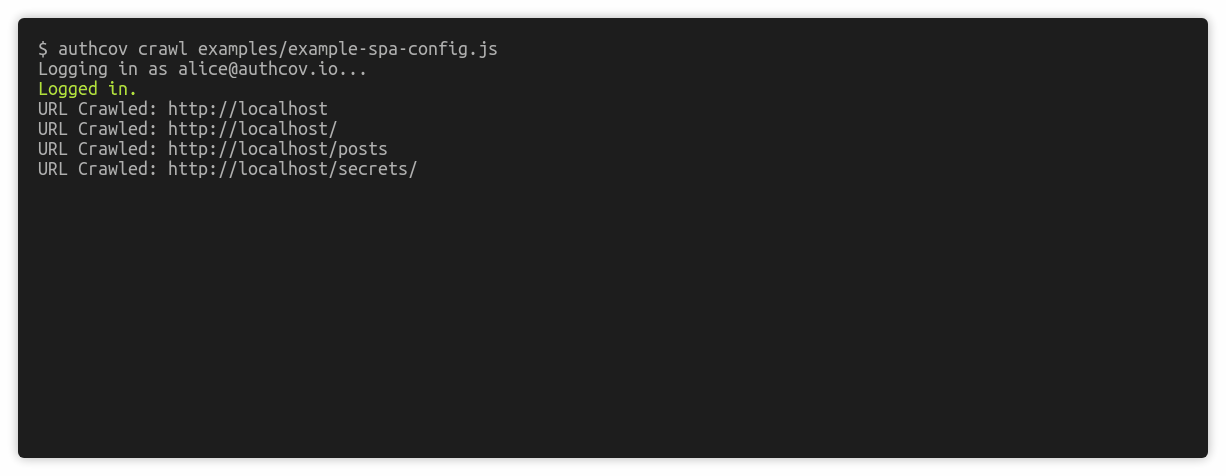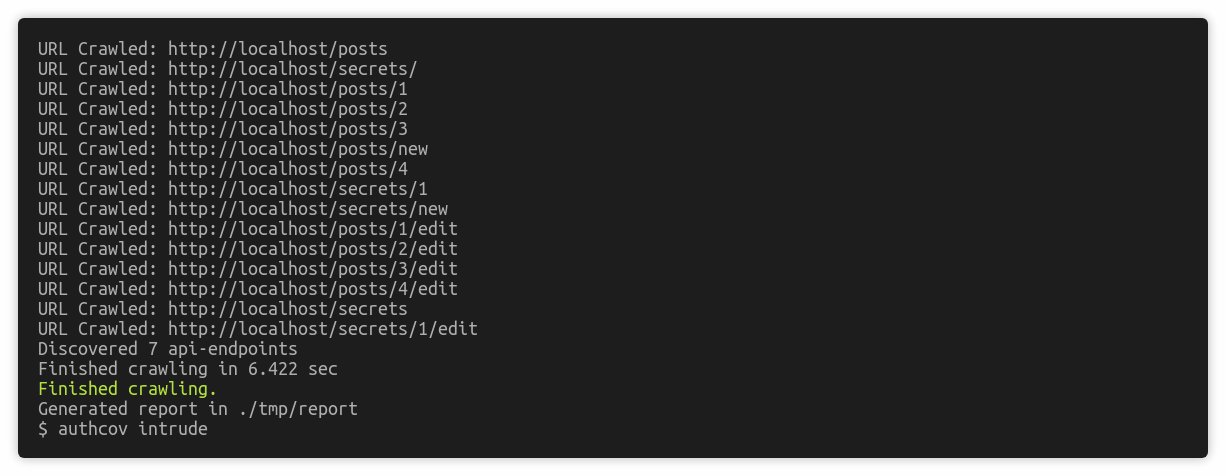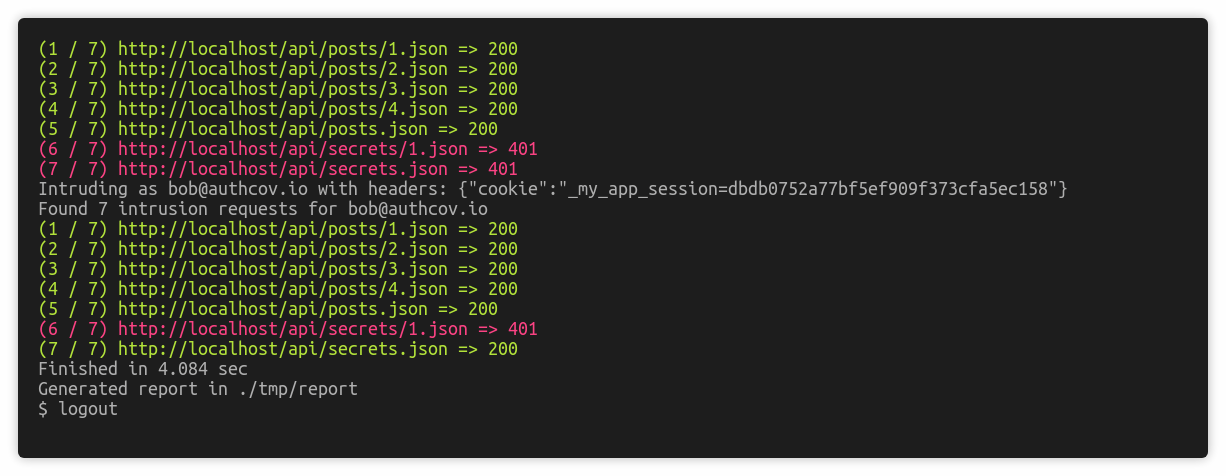
Web app authorisation coverage scanning

The full repo of all the labs available as part of the benchmark

A tool to scan Kubernetes cluster for risky permissions

SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…

In-depth ldap enumeration utility

Dahua Console, access internal debug console and/or other researched functions in Dahua devices. Feel free to contribute in this project.

SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.

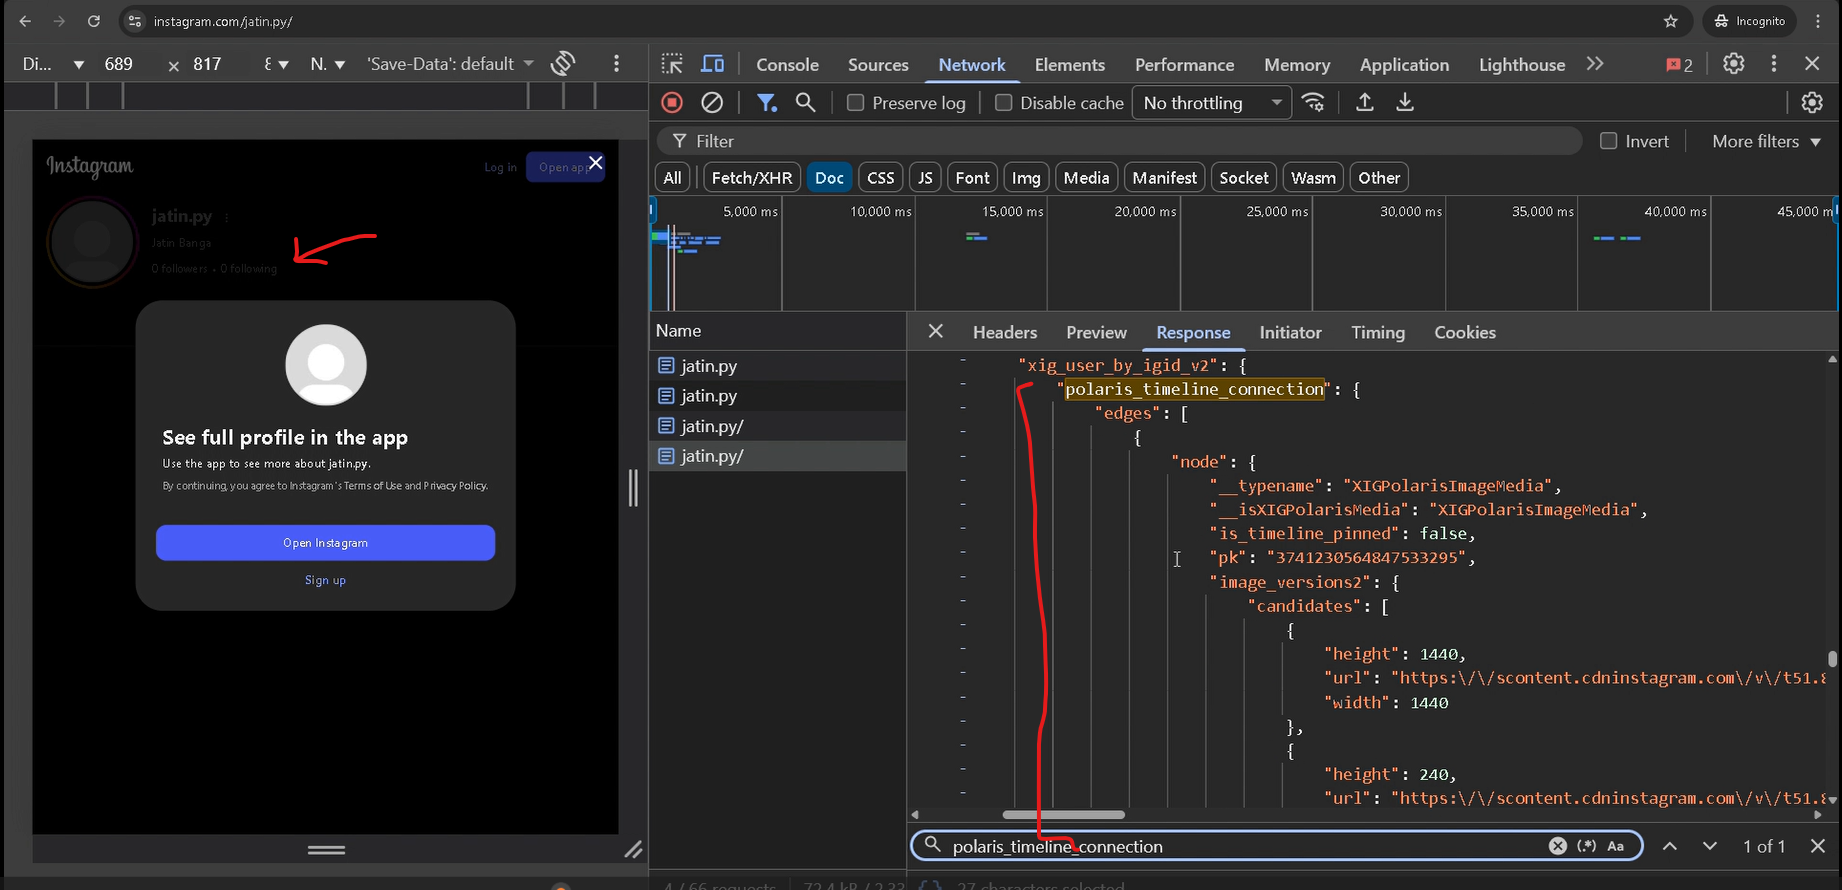
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…