ESAPI__esapi-java-legacy_CVE-2022-24891_2-2-3-1

OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…

OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…

Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…

Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…

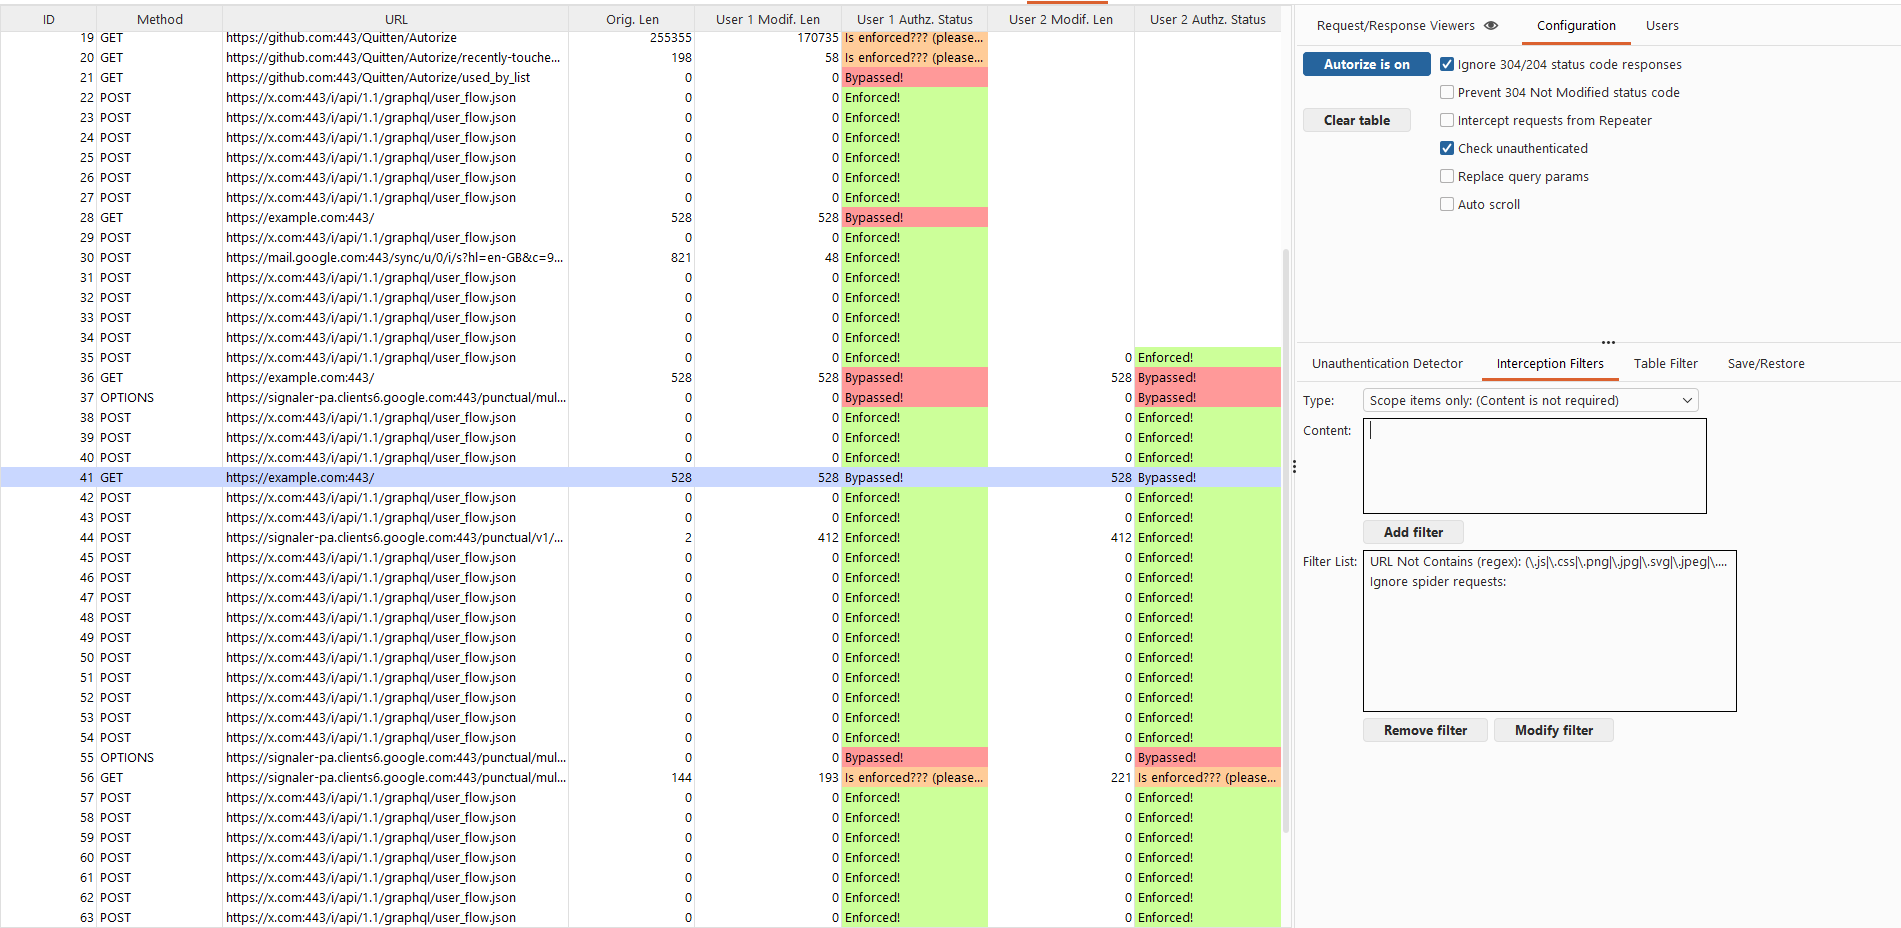
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…

Ultimate Gift Cards for WooCommerce <= 3.0.6 - Missing Authorization to Infinite Money Glitch

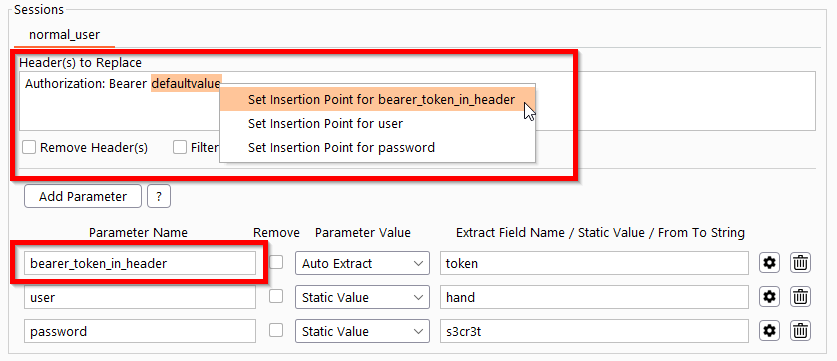
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.

OAuth Request Crafter

Detection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI

🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…

PHP-RBAC is an authorization library for PHP. It provides developers with NIST Level 2 Standard Role Based Access Control and more, in the fastest…

The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP

Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…

CVE-2024-27198 & CVE-2024-27199 PoC - RCE, Admin Account Creation, Enum Users, Server Information

Automated HTTP Request Repeating With Burp Suite

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…