
CVE-2022-22978
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
authentication-authorizationeducationexploitation+3
raghvendra1207/cve-2022-22978Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 tomasz-lisowski/swicc
A framework for creating smart cards (ICC-based cards with contacts).
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 ducluongtran9121/cve-2022-22978-poc
PoC of CVE-2022-22978 vulnerability in Spring Security framework
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 masa42/cve-2024-38821-poc
Proof-of-concept exploit for CVE-2024-38821, demonstrating authentication bypass in Spring Framework via path traversal to access restricted…
 moften/cve-2024-51996
CVE-2024-51996 es una vulnerabilidad crítica que afecta al componente security-http del framework Symfony.
 ethan-repo-lab4b6/cve-2022-36537
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…
 shoucheng3/asf__cxf_cve-2019-17573_3-2-11
Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.
 shoucheng3/asf__cxf_cve-2016-6812_3-0-11
Open-source services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, JAX-WS, and JAX-RS APIs.
 shoucheng3/ff4j__ff4j_cve-2022-44262_1_8_13_fixed
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
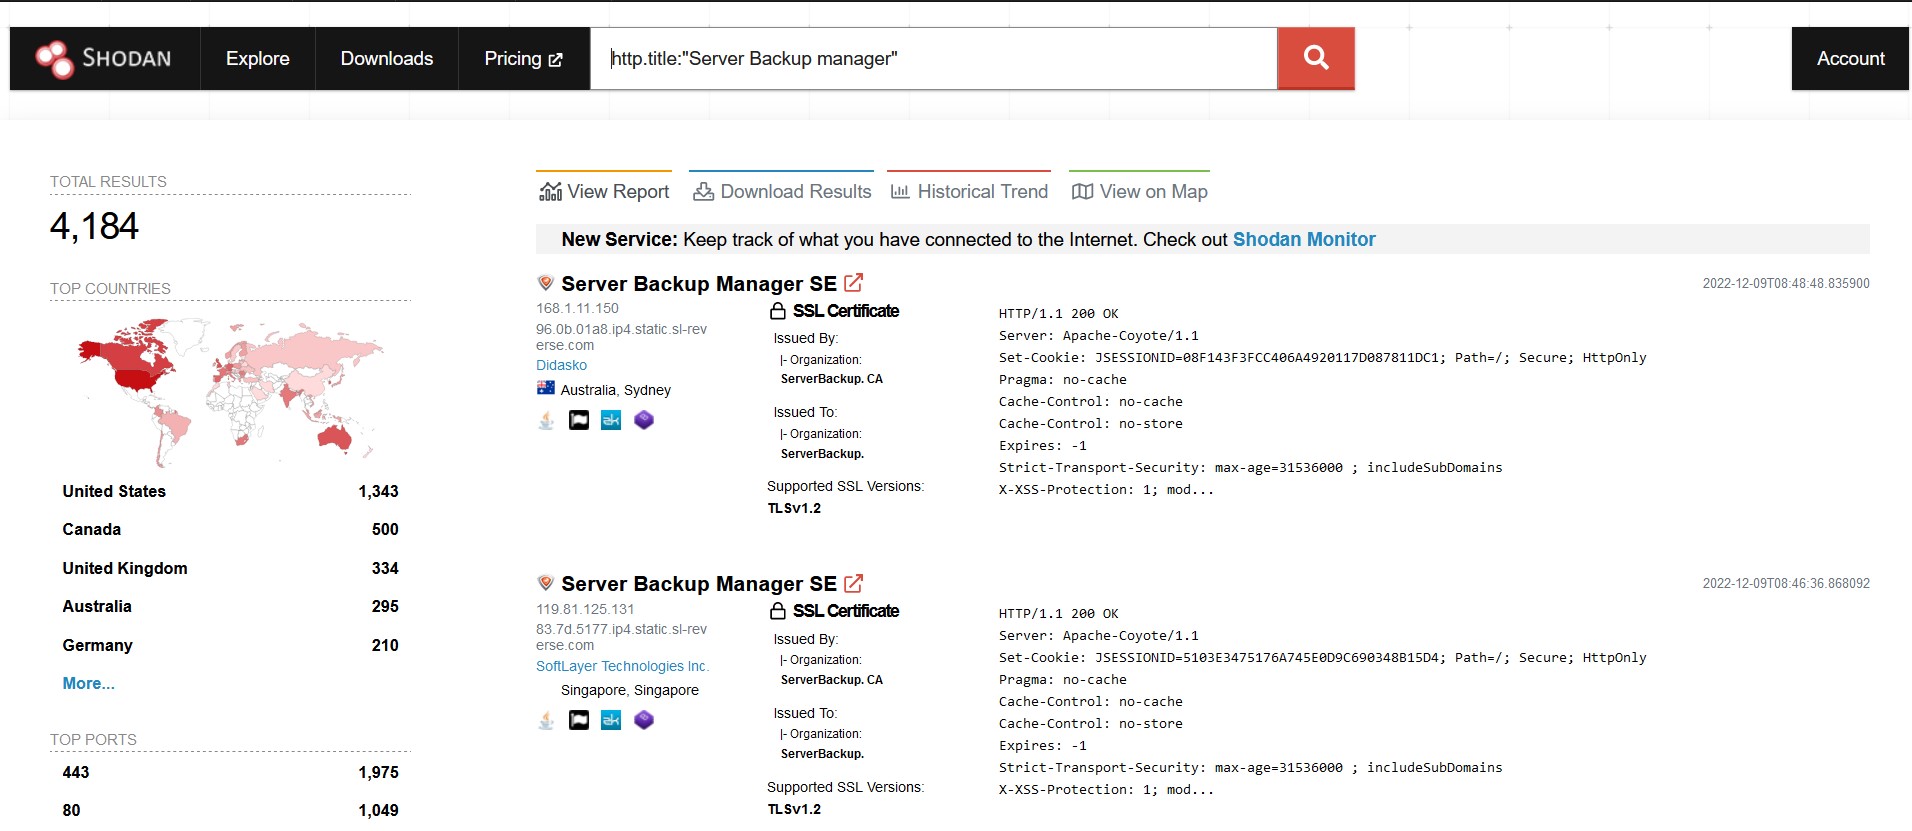 malwareman007/cve-2022-36537
POC of CVE-2022-36537
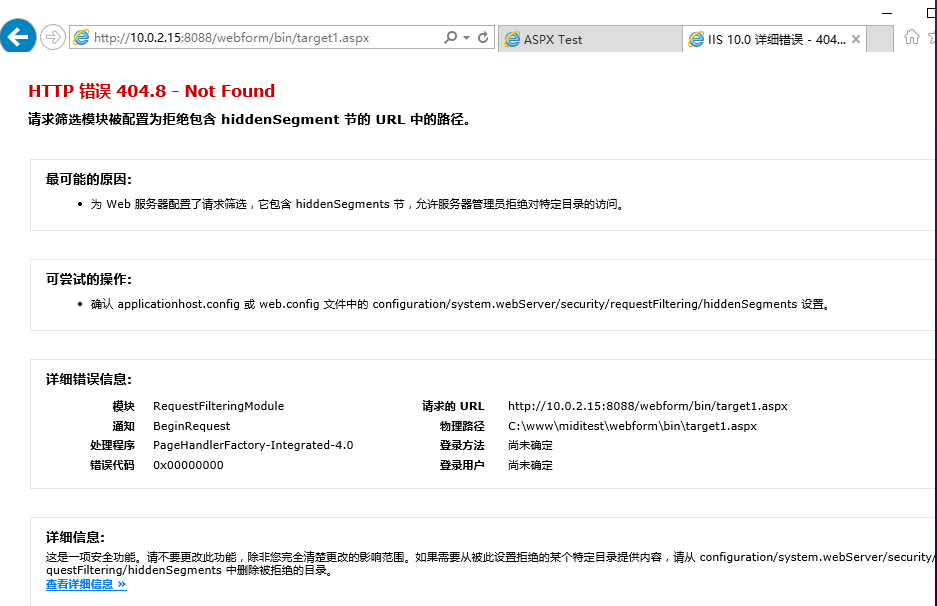 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 agnihackers/cve-2022-36537-exploit
CVE-2022-36537