
cve-2020-1764-poc
 jpts/cve-2020-1764-poc
Proof-of-concept exploit for CVE-2020-1764 authentication bypass in Kiali 0.4.0–1.15.0, enabling unauthorized API access via crafted JWT tokens.
authentication-authorizationexploitationpenetration-testing+2
1
jpts/cve-2020-1764-pocProof-of-concept exploit for CVE-2020-1764 authentication bypass in Kiali 0.4.0–1.15.0, enabling unauthorized API access via crafted JWT tokens.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 7hepr0fess0r/adcsdevilcom
A C# tool for requesting certificates from ADCS using DCOM over SMB. This tool allows you to remotely request X.509 certificates from CA server using…
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…
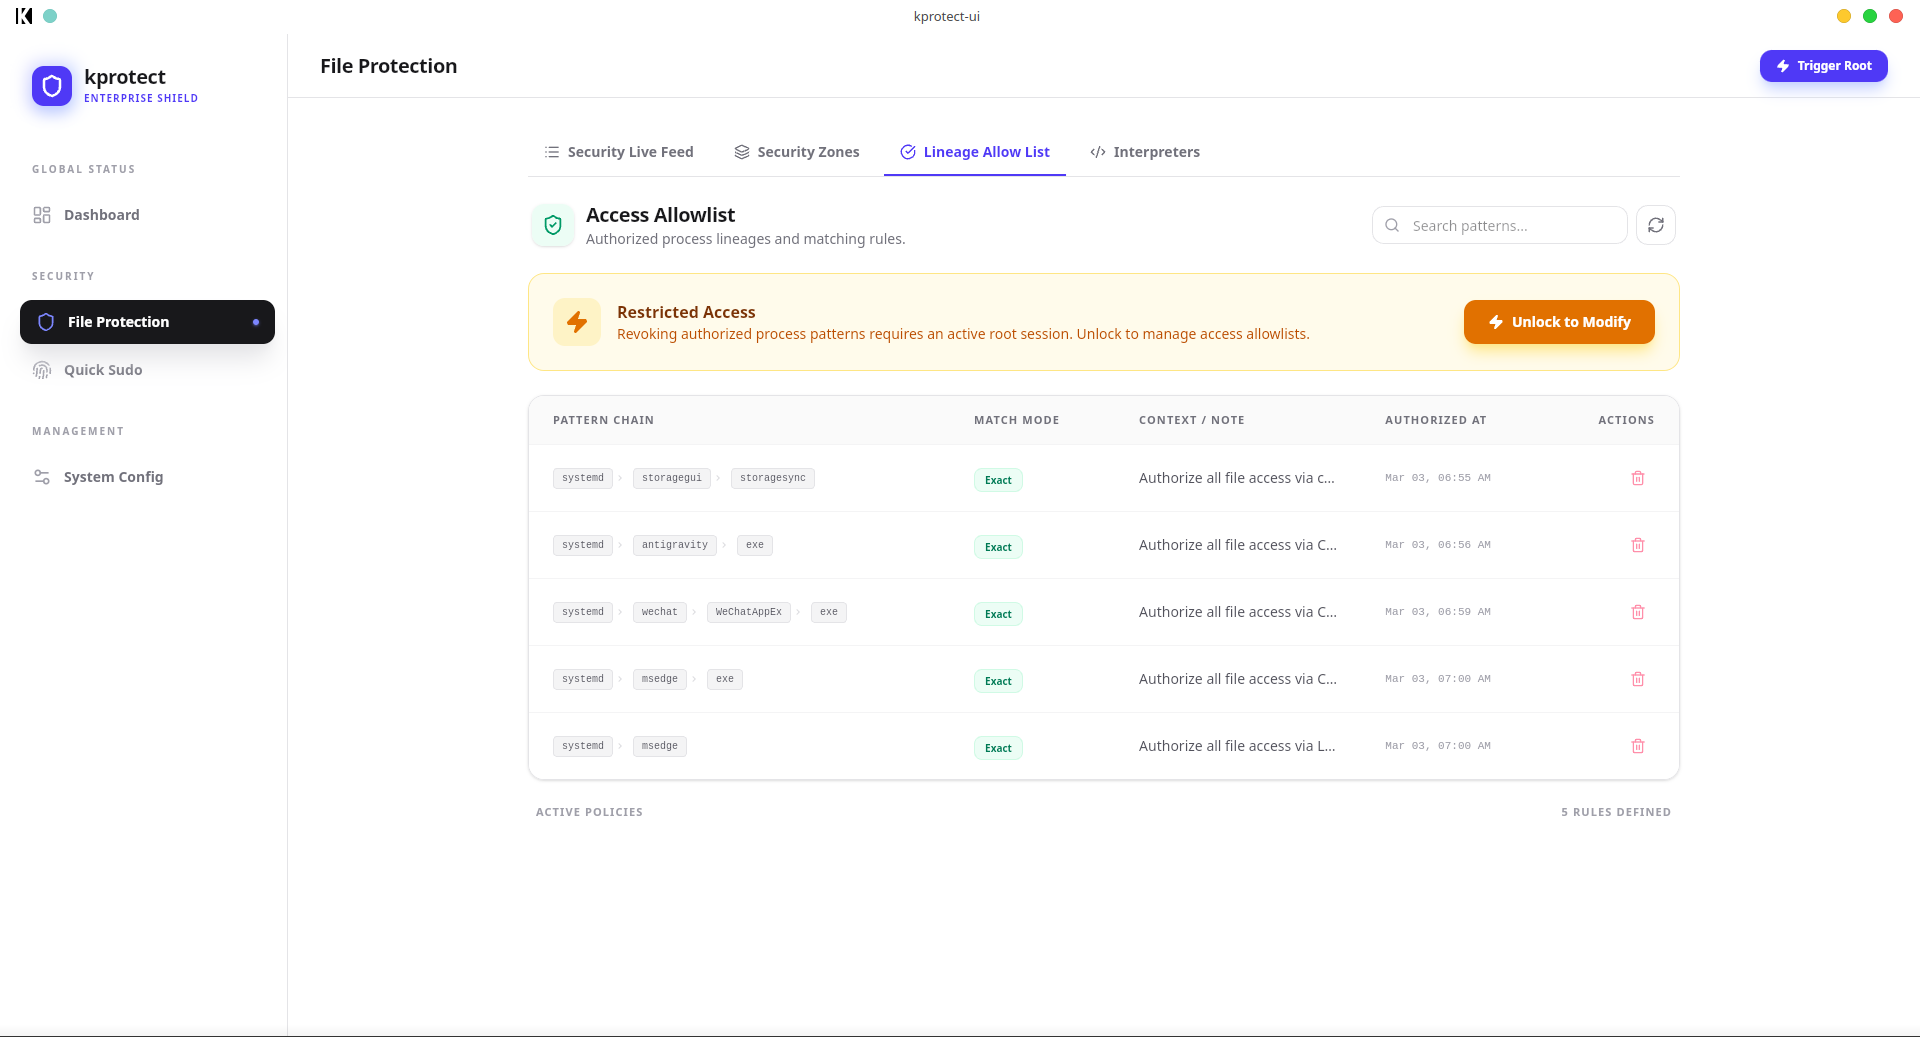 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 sfewer-r7/cve-2026-16232
A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.
 fengchenzxc/cve-2020-28148
Wi-Fi portal authentication bypass exploit using MAC address spoofing to gain unauthorized network access, demonstrated on enterprise AC and AP…
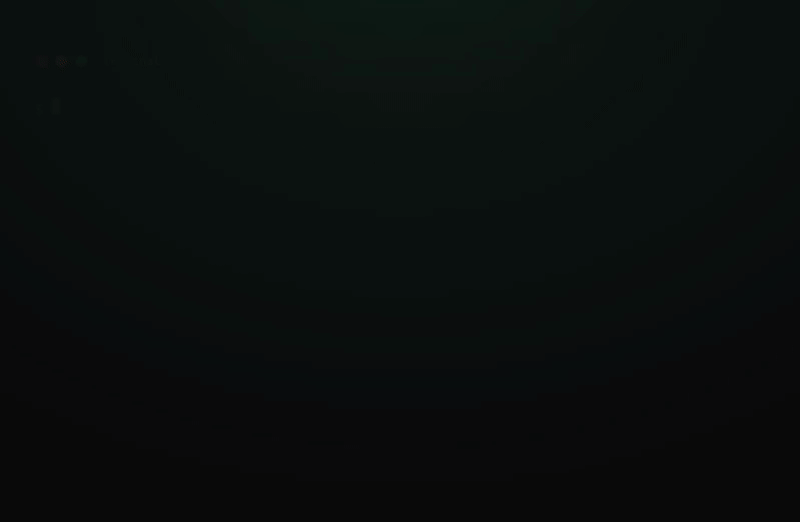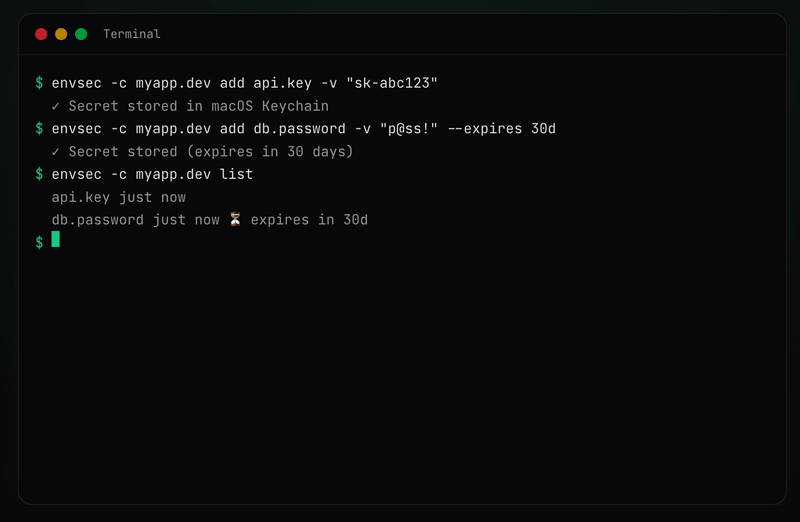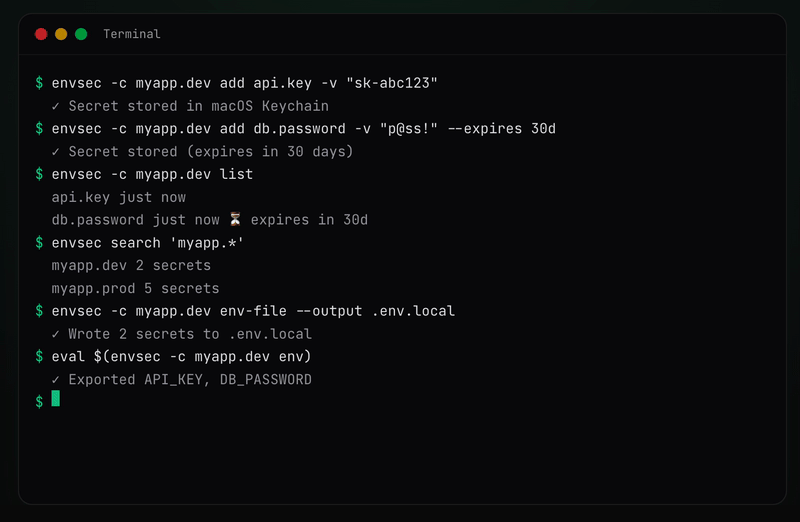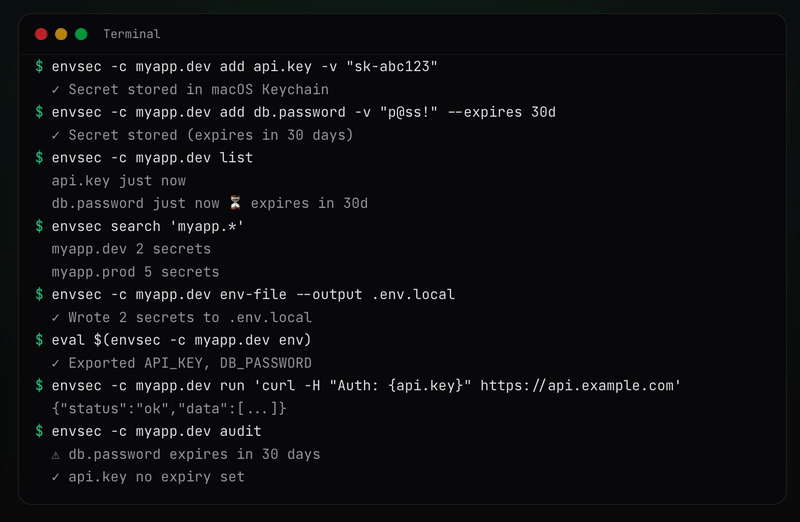 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 virgula0/poc-cve-2018-10933
LibSSH Authentication Bypass Exploit using RCE
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
 corelight/go-zeek-broker-ws
A Go library for using zeek broker's websocket API
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 watchtowrlabs/kentico-xperience13-authbypass-wt-2025-0006
Authentication bypass detection script for Kentico Xperience 13 CMS Staging Service using a single POST request to verify vulnerability.
 george0papasotiriou/cve-2026-21003-jwt-none-algorithm-bypass-via-kid-header-omission
Proof-of-concept exploit for CVE-2026-21003 demonstrating JWT authentication bypass by omitting the kid header and using the 'none' algorithm to…