

AutoRepeater
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
api-security-testingauthentication-authorizationpenetration-testing+4
894
nccgroup/autorepeaterAutomated HTTP Request Repeating With Burp Suite
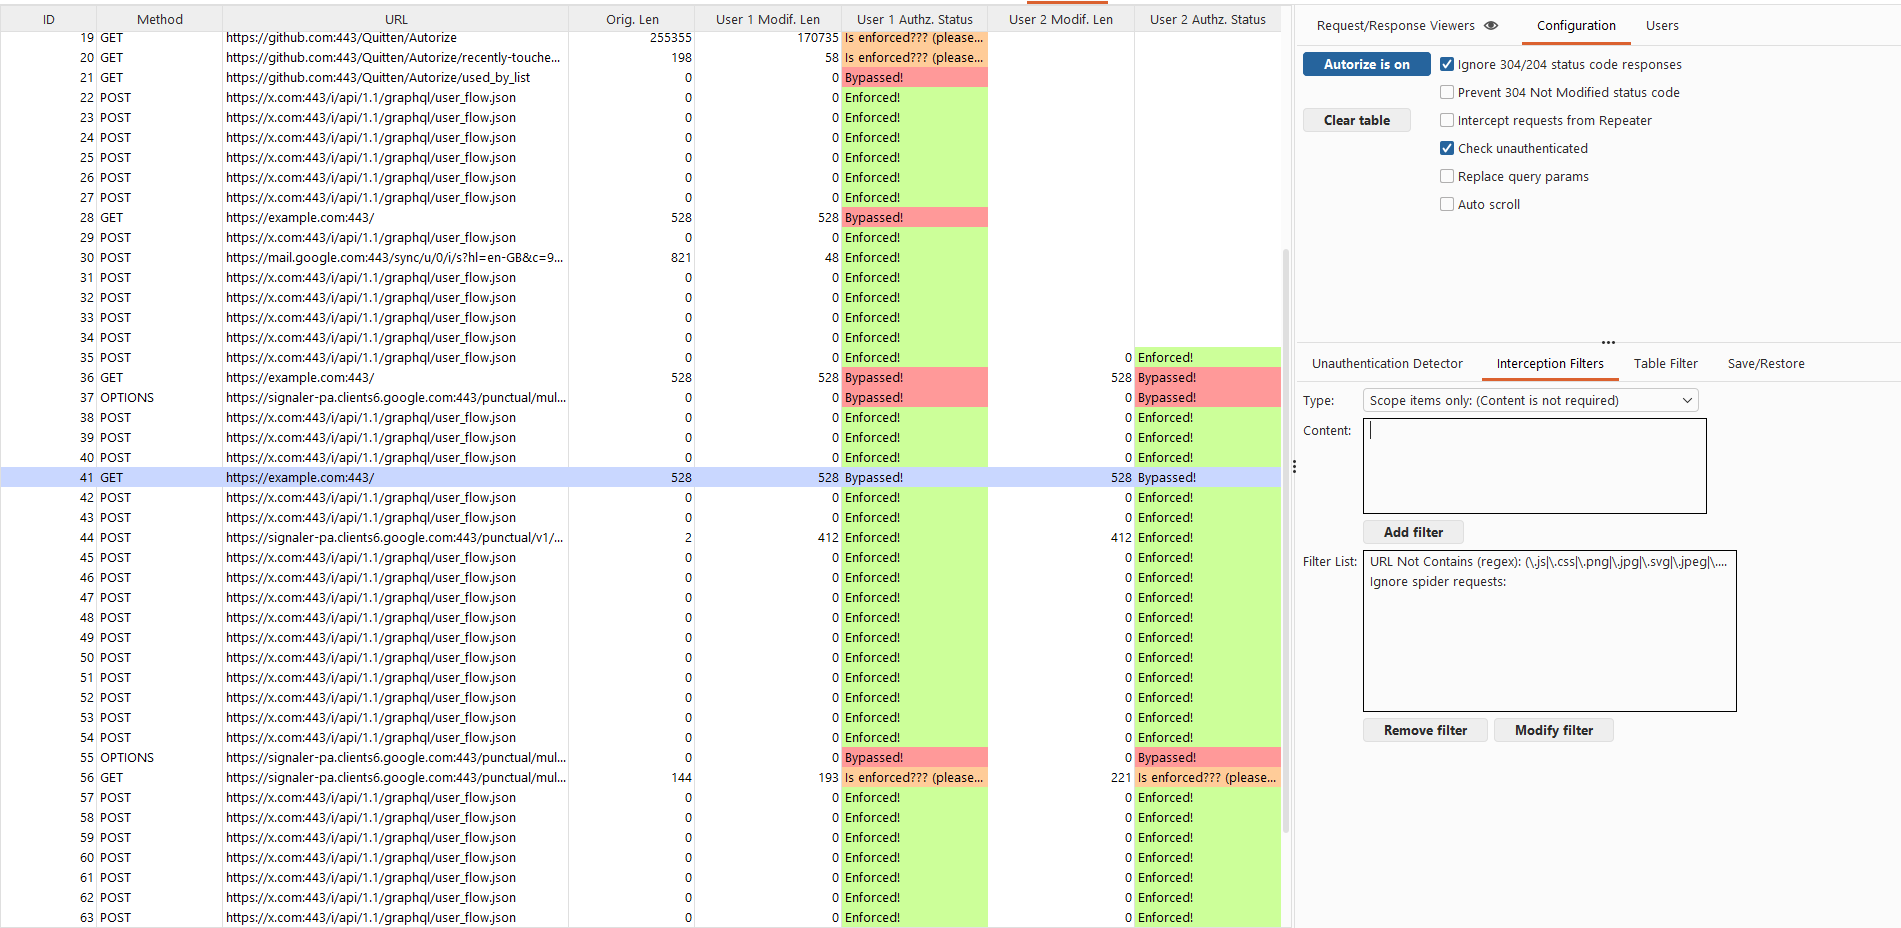 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
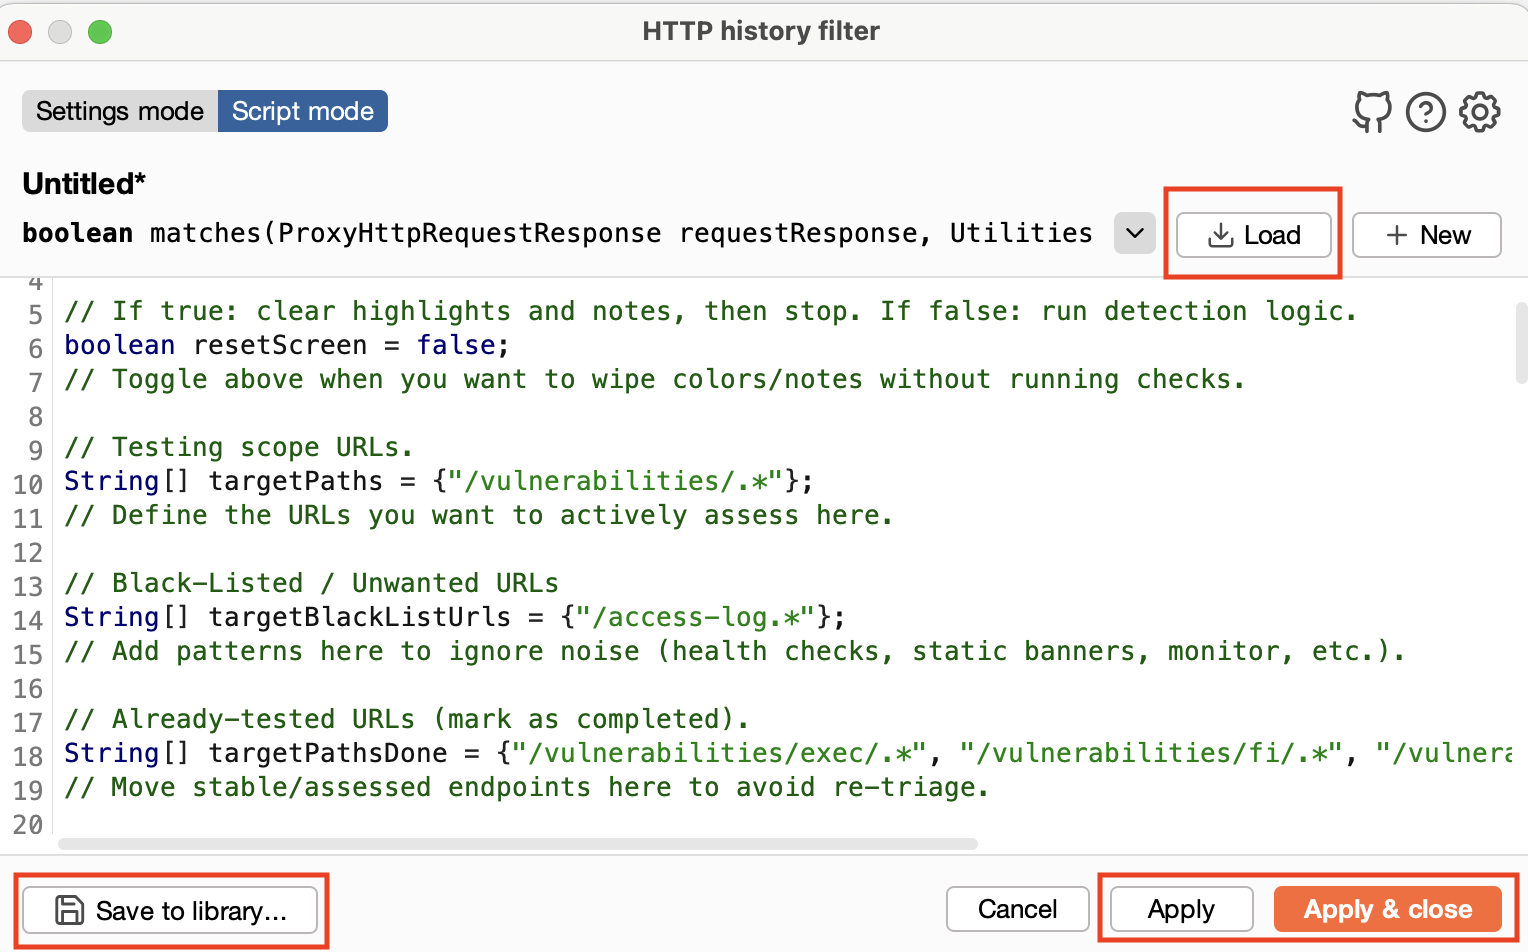 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
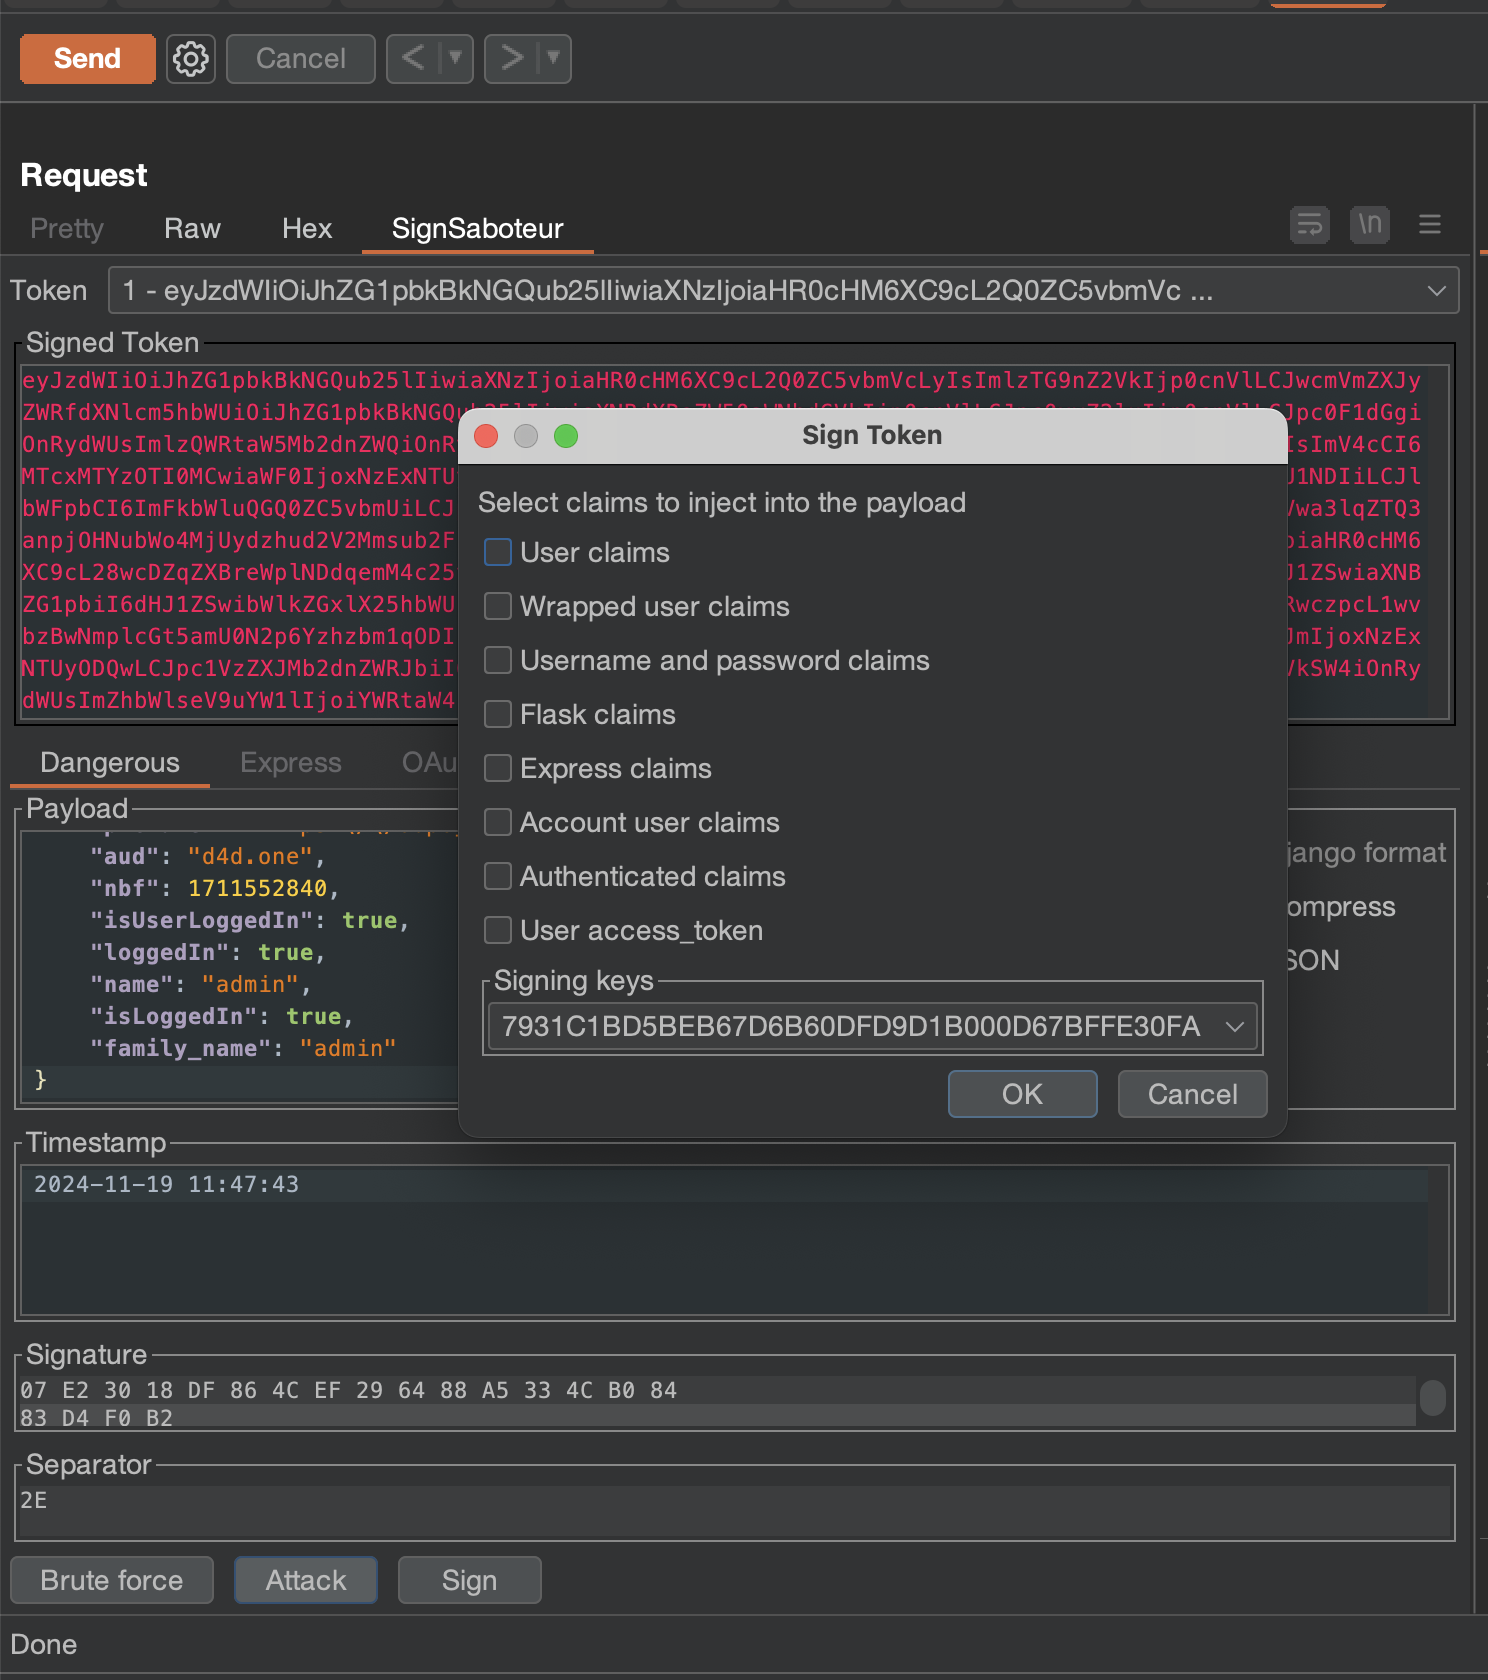 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 portswigger/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 berraesen/nextjs-middleware-auth-bypass-lab
Bu laboratuvar ortamını sıfırdan kendim oluşturdum. Next.js uygulaması içerisinde giriş, ana sayfa ve admin sayfalarını hazırladım. Middleware ile…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
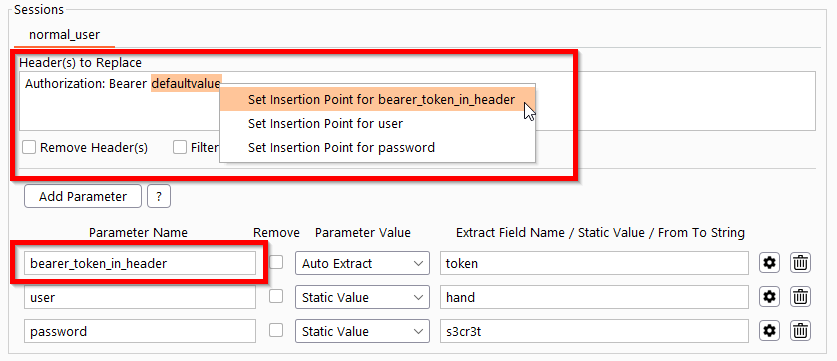 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 manuelberrueta/flowanalyzer
FlowAnalyzer is a tool to help in testing and analyzing OAuth 2.0 Flows, including OpenID Connect (OIDC).
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 randomrobbiebf/cve-2024-11423
Ultimate Gift Cards for WooCommerce <= 3.0.6 - Missing Authorization to Infinite Money Glitch
 foxer131/cve-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…