GSSC-CVE-2022-41923
Workaround guide for CVE-2022-41923 privilege management vulnerability in Grails Spring Security Core plugin, providing patched filter definitions…

Workaround guide for CVE-2022-41923 privilege management vulnerability in Grails Spring Security Core plugin, providing patched filter definitions…

Burp plugin which supports in finding privilege escalation vulnerabilities

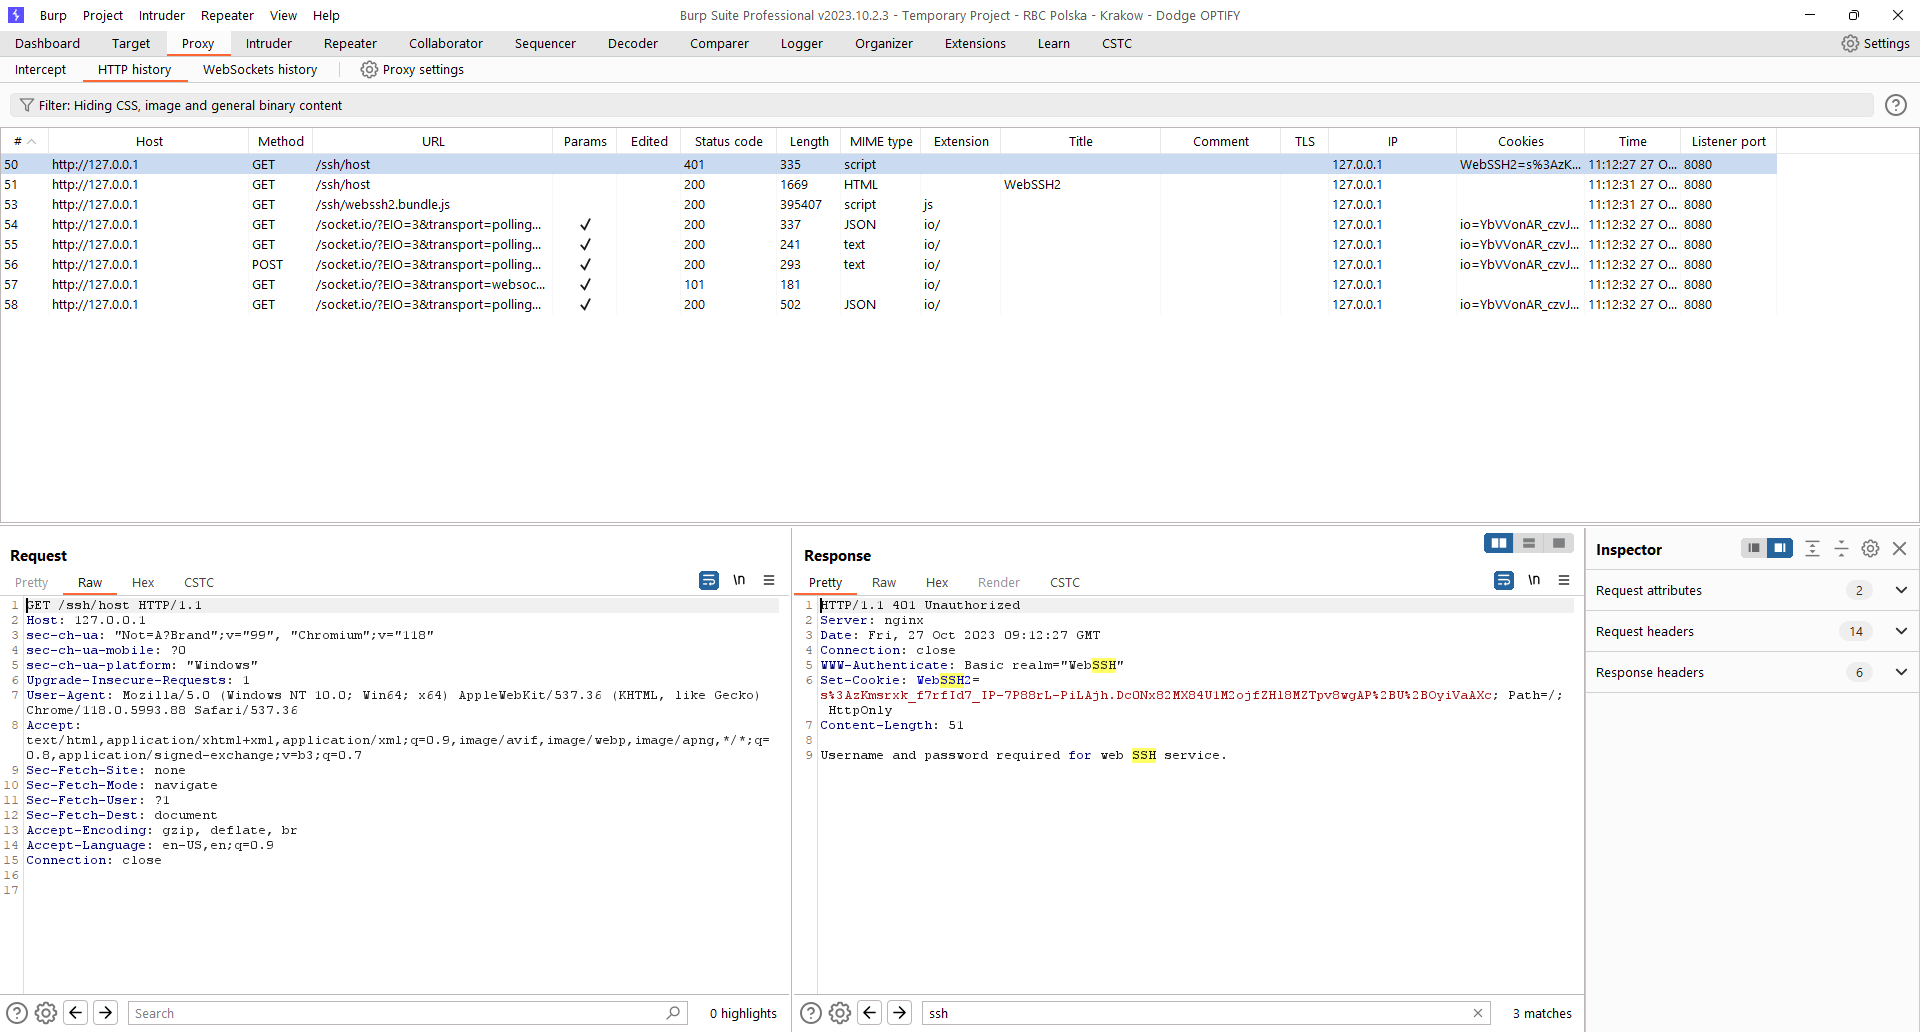
Repository contains description for CVE-2023-35794 discovered by Dodge Industrial Team for Dodge OPTIFY platfrom.

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Python CLI that detects and exploits CVE-2026-90907, a Joomla! com_users authorization bypass enabling unauthenticated account creation;…

Hardened PHP replacement handlers for PeachPay Stripe capture and void AJAX endpoints, adding nonce verification, capability checks, and strict order…

Reproducible Docker lab + PoC: Keycloak manage-users -> realm-admin escalation via composite roles (CVE-2026-94000 variant). Validated on 26.8.1.

The authorization layer CVE-2026-93328 was missing: scoped grants, path confinement, and signed receipts in front of MCP storage tools. CVE…

Keycloak 26.8.1 Medium 6.6 Remote authenticated auth leftover. A help-desk admin with manage-users can pin a pre-built composite of manage-realm onto…