
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-22978 — Reproducible lab environment demonstrating CVE-2022-22978 Spring Security authorization bypass via encoded newline characters in RegexRequestMatcher. | Kitploit
Tools/GitHubGitHub/he-ewo/cve-2022-22978
Authentication & AuthorizationVulnerability AnalysisExploitationWeb Application ExploitationLearning & EducationLabs & Practice
GitHubhe-ewo/cve-2022-22978

CVE-2022-22978

Reproducible lab environment demonstrating CVE-2022-22978 Spring Security authorization bypass via encoded newline characters in RegexRequestMatcher.

View Repository
381 year agoNot yet reviewed
Share

CVE-2022-22978: Spring Security Authorization Bypass

Summary

  • Spring Security framework is a security framework that provides authentication and authorization functions in Spring-based applications.
  • In Spring Security versions 5.5.6, 5.6.3 and earlier, when using RegexRequestMatcher, a function that grants permissions using regular expressions, an authorization bypass may occur if the request URL contains newline characters.
  • An attacker can bypass access to the admin page (/admin) by using encoded newline characters such as %0a, %0d.

Environment Setup and Execution

  • The test environment was prepared by running docker compose up -d.
  • Run http://localhost:8080/admin to verify that access to the admin page is blocked.
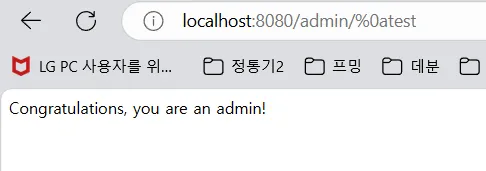
  • Run http://localhost:8080/admin/%0atest to access the admin page.
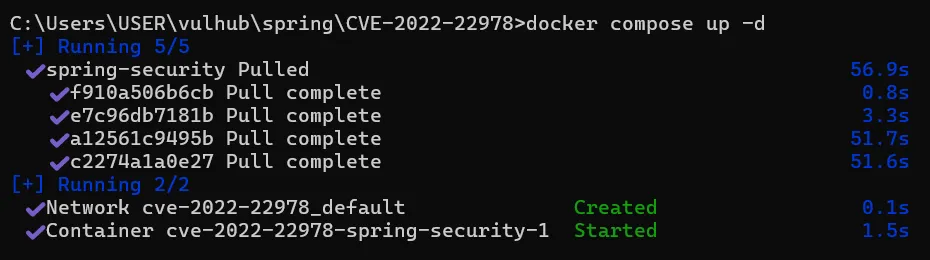
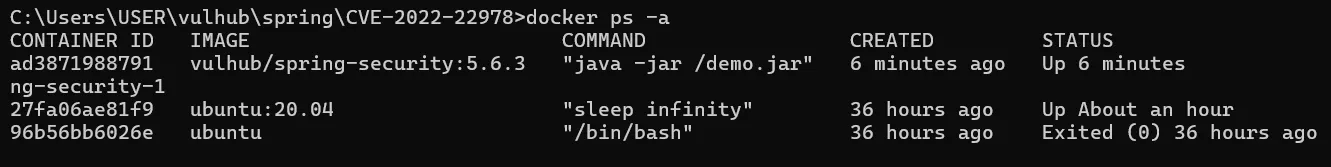
image image A vulnerable environment was configured.

Results

image

Access to the admin page is blocked.

image image

%0d represents '\r' and %0a represents '\n', both newline characters. Sending requests using %0d or %0a allows bypassing access permissions.

Conclusion

If newline characters such as %0a or %0d are included in the URL, the RegexRequestMatcher processes the request path without handling newline characters, enabling permission bypass. Attackers can access the admin page via permission bypass and steal sensitive information there, so caution is required.

GitHub address: https://github.com/he-ewo/CVE-2022-22978.git

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    516
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    355
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    315
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    303
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    285

Explore all tools

Browse our collection of tools

View all tools →