
CVE-2024-10924-PoC
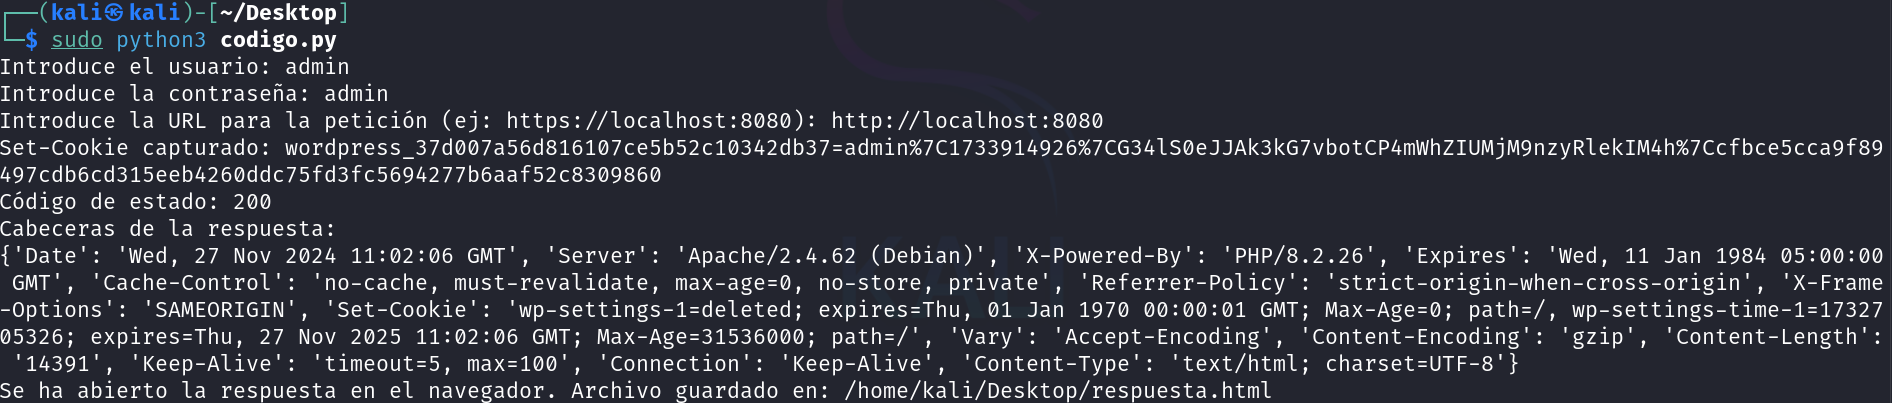
Proof-of-concept exploit for CVE-2024-10924, an authentication bypass vulnerability in the Really Simple Security WordPress plugin, enabling MFA…

Proof-of-concept exploit for CVE-2024-10924, an authentication bypass vulnerability in the Really Simple Security WordPress plugin, enabling MFA…

Checklist of the most important security countermeasures when designing, testing, and releasing your API


Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

Runtime security for AI agents: discover agents, map their permissions, and enforce what they can do.

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…

Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…

MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…

Password Strength Evaluator is a tool to evaluate the strength of passwords and provide recommendations to improve their security.

Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…

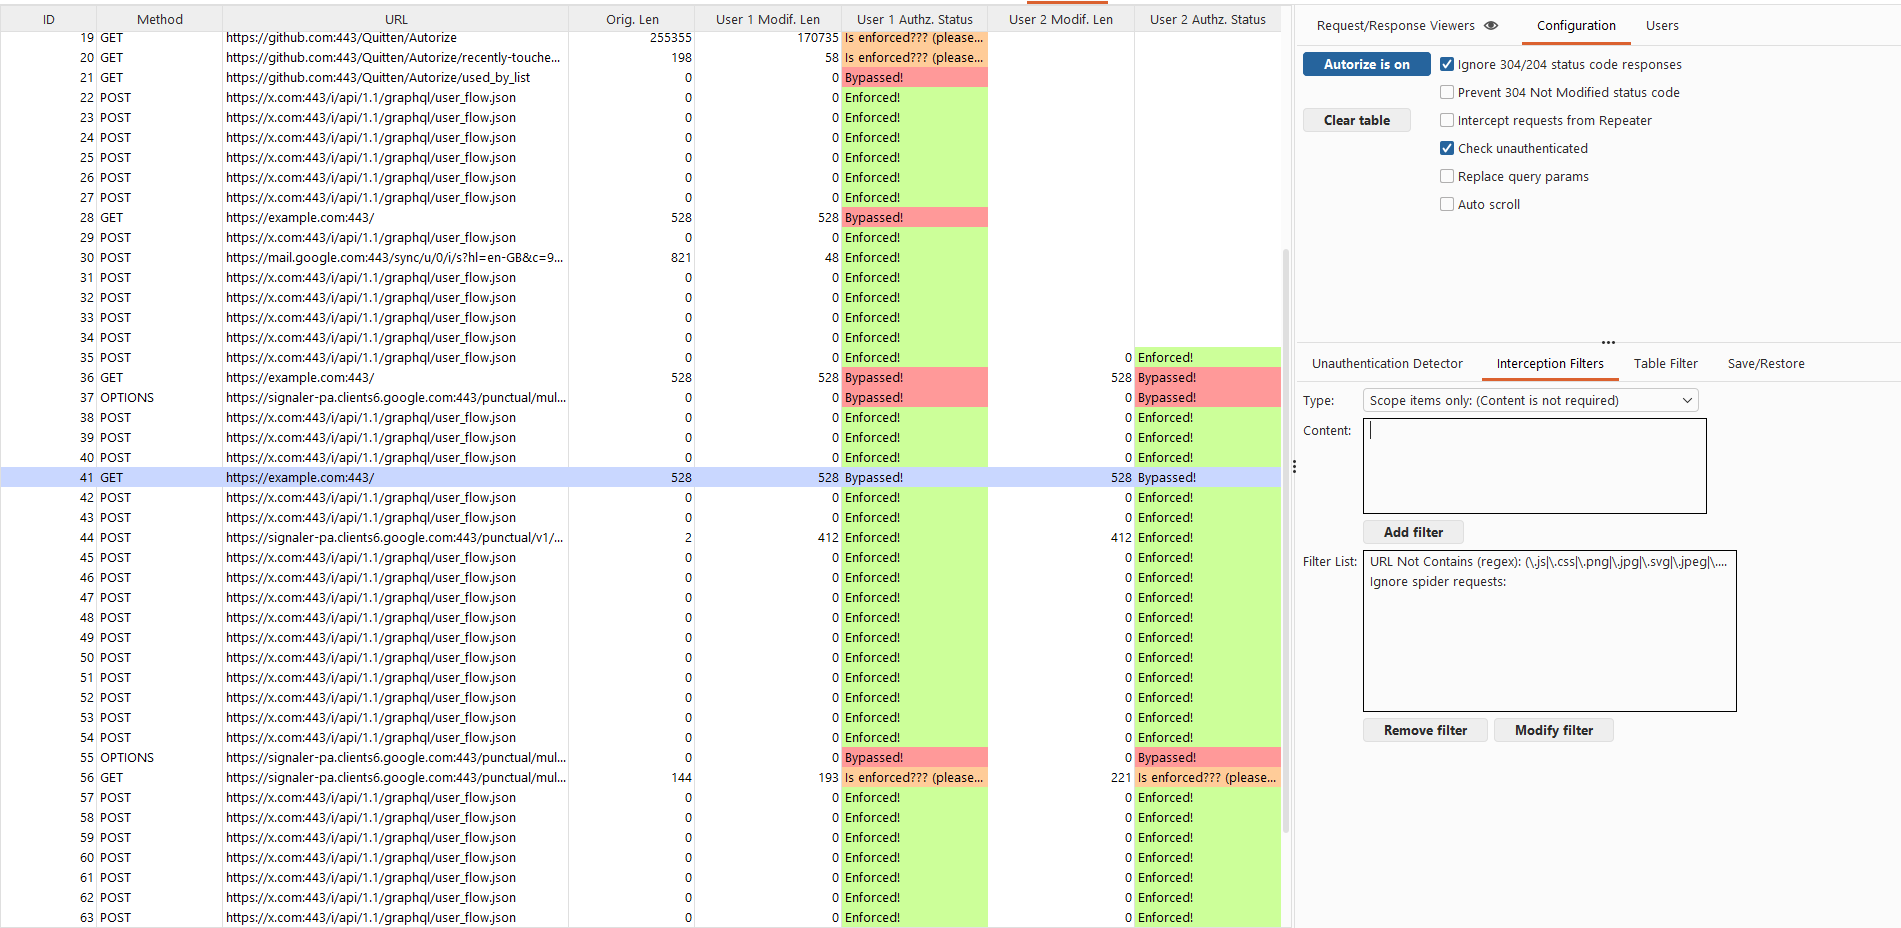
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…

An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

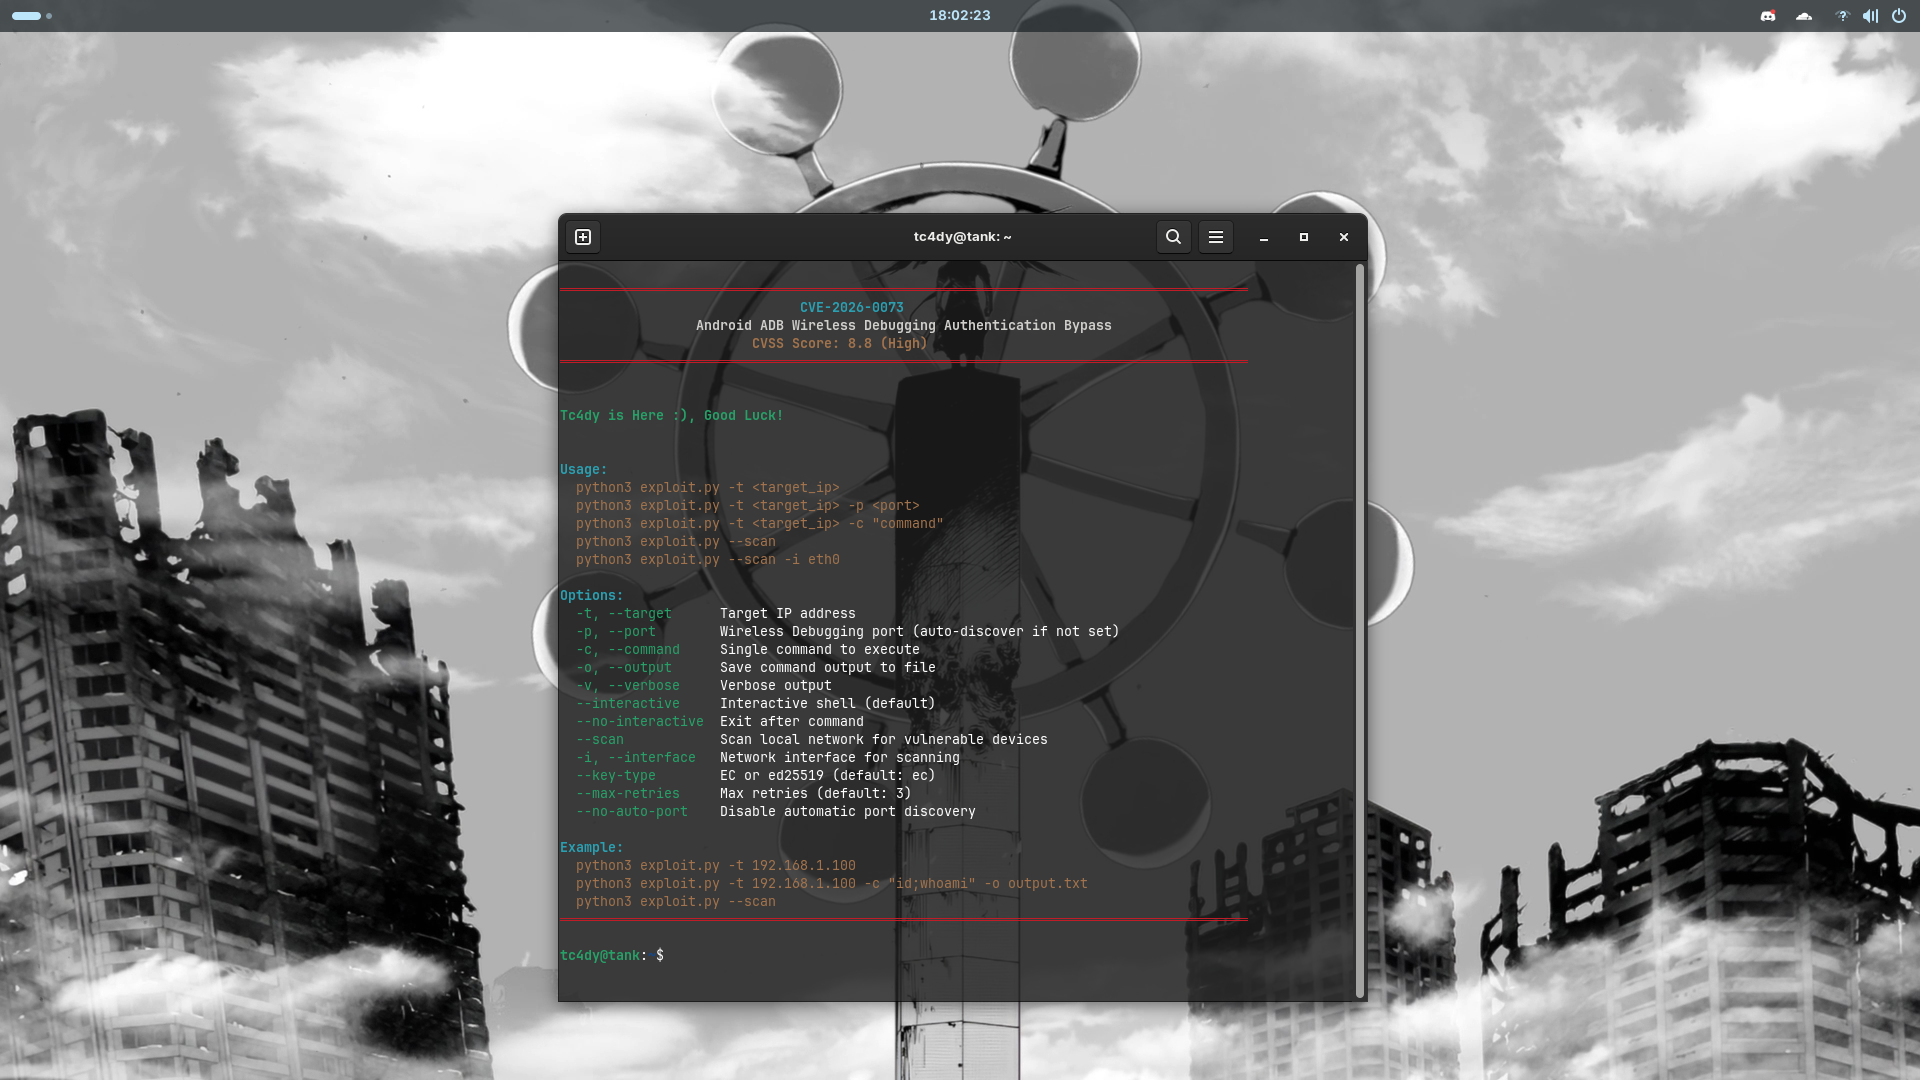
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…

A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…

PHP 8.4+ security library (mirror)