
kit-policy
 kit-lang/packages/kit-policy
A flexible, composable authorization framework for Kit (inspired by Action Policy)
authentication-authorizationutilities-frameworks
kit-lang/packages/kit-policyA flexible, composable authorization framework for Kit (inspired by Action Policy)
 ethan-repo-lab4b6/cve-2022-36537
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…
 shoucheng3/apache__shiro_cve-2023-34478_1-11-0
Java security framework providing authentication, authorization, cryptography, and session management APIs to secure any application from mobile to…
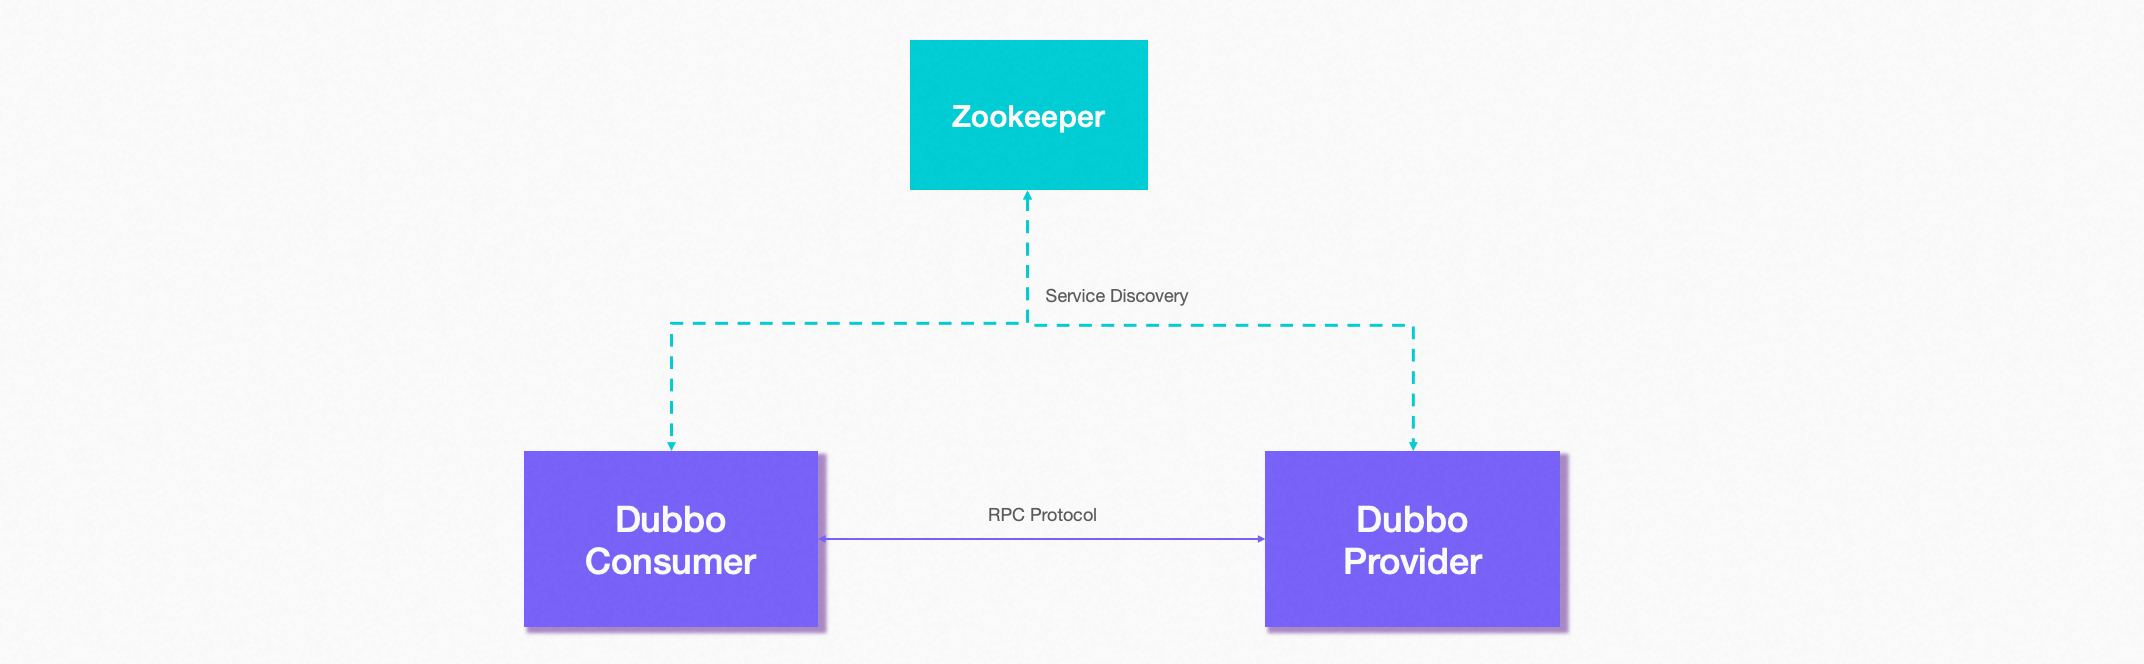 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 shoucheng3/ff4j__ff4j_cve-2022-44262_1-8-13
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
 shoucheng3/ff4j__ff4j_cve-2022-44262_1_8_13_fixed
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
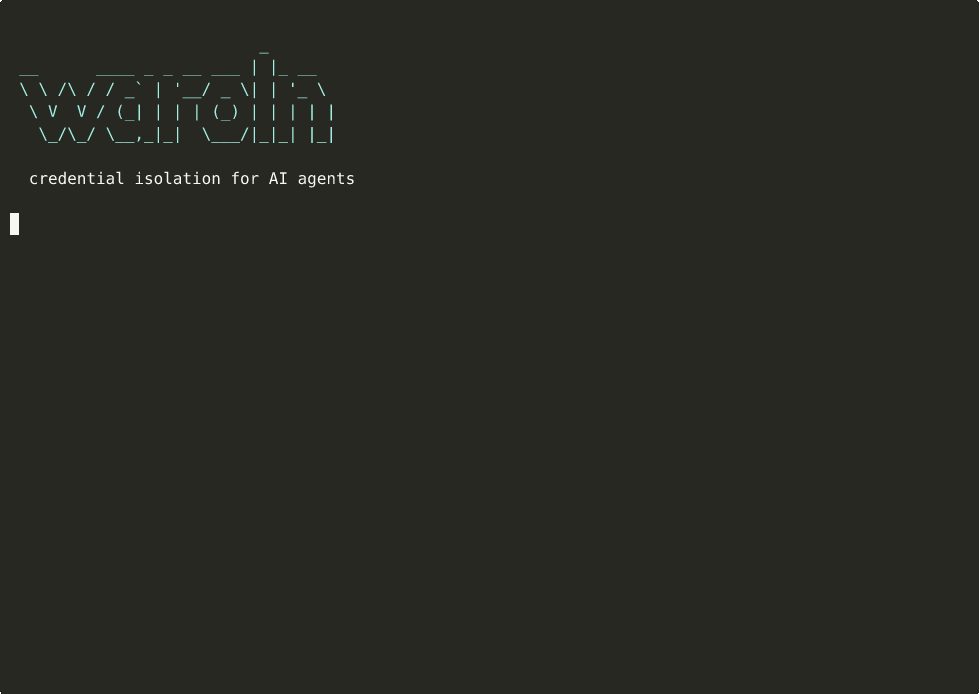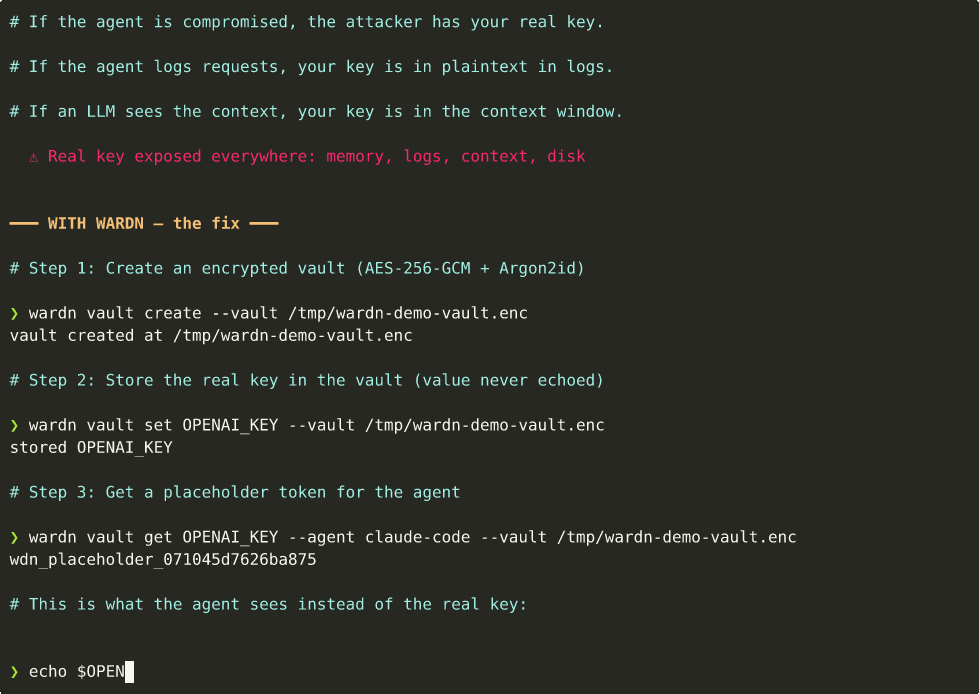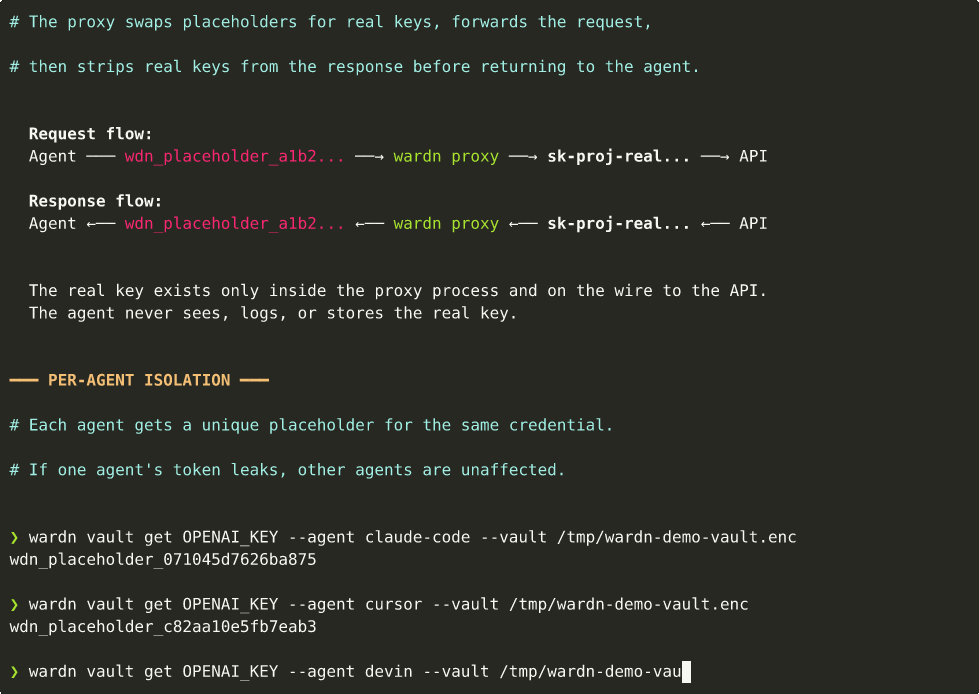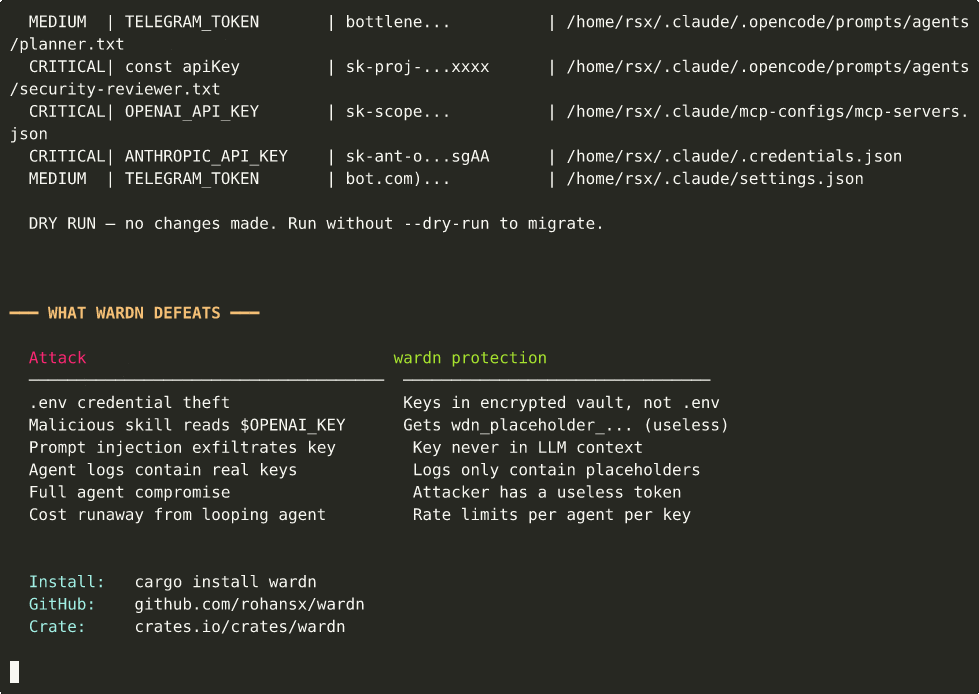 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
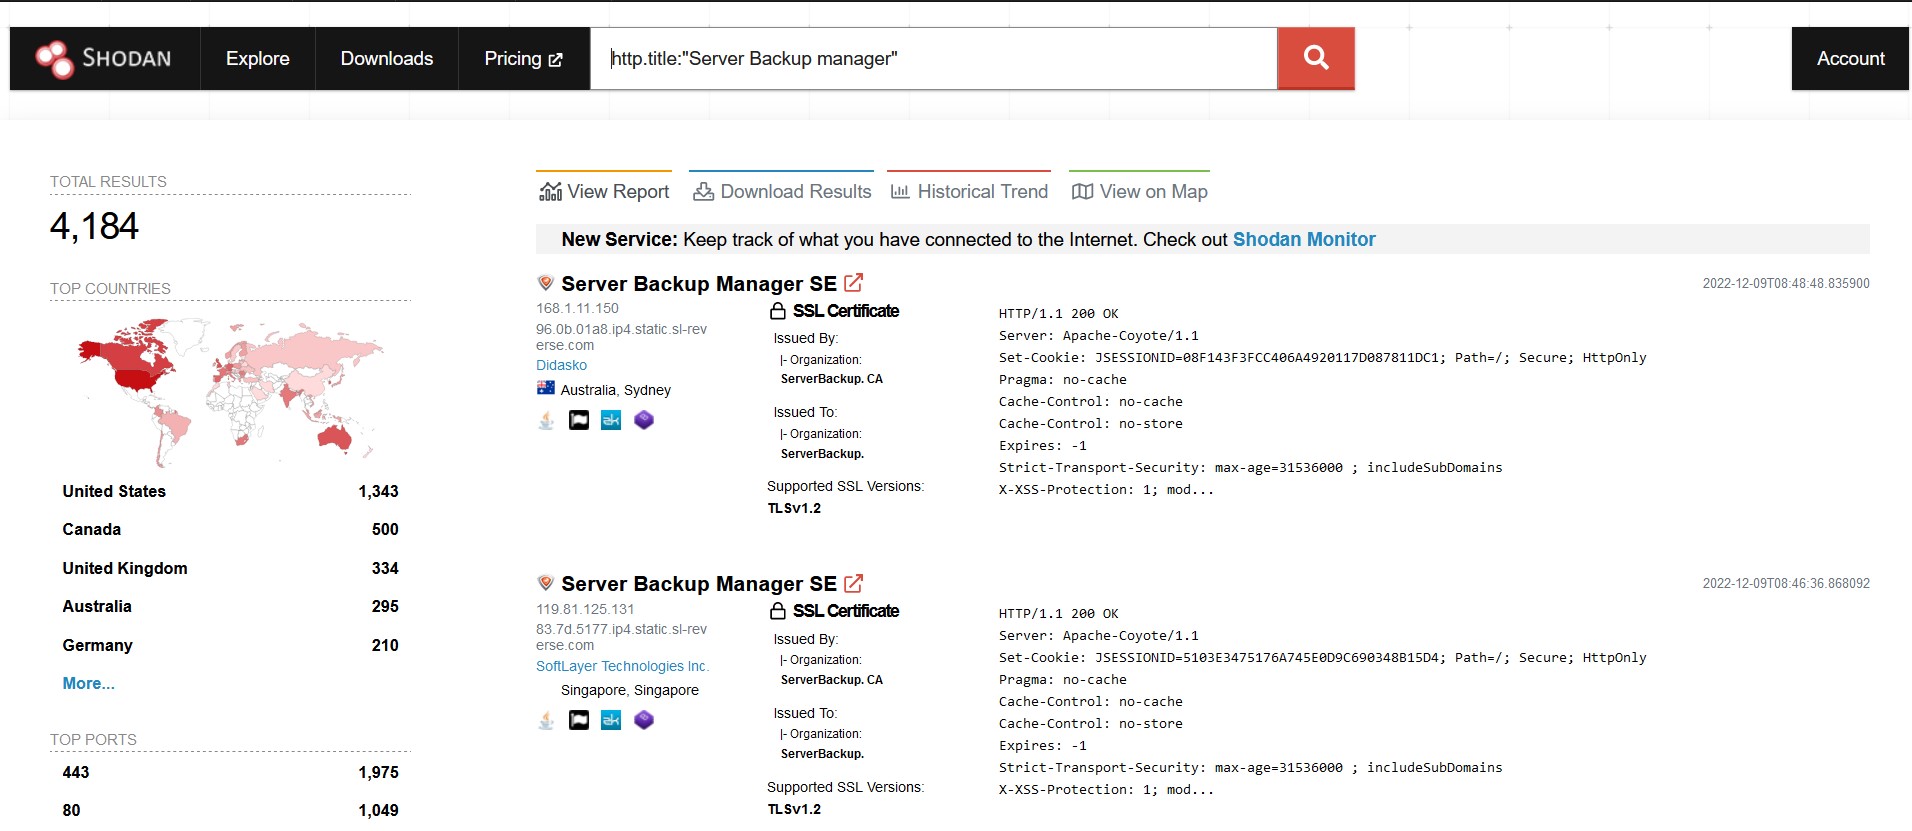 malwareman007/cve-2022-36537
POC of CVE-2022-36537
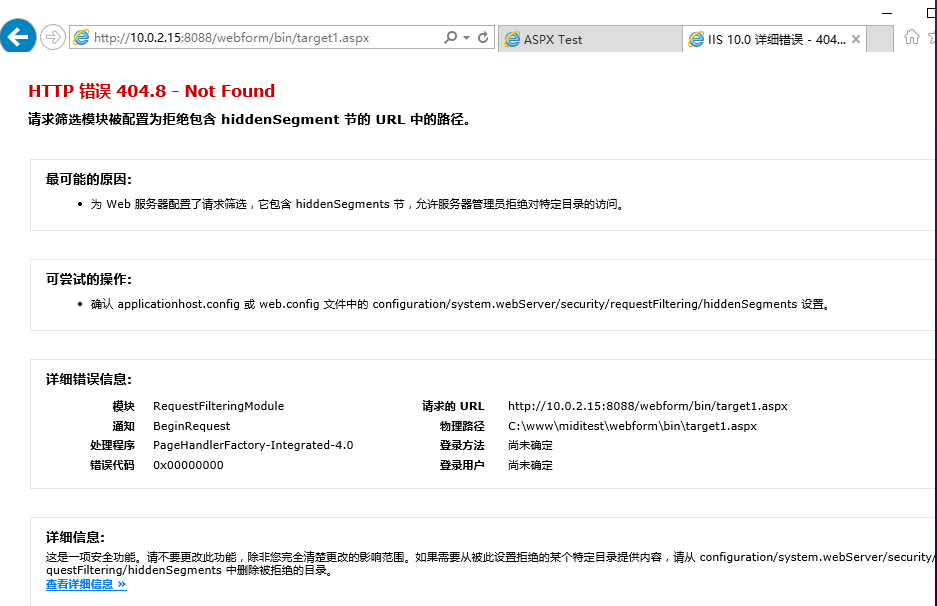 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 agnihackers/cve-2022-36537-exploit
CVE-2022-36537
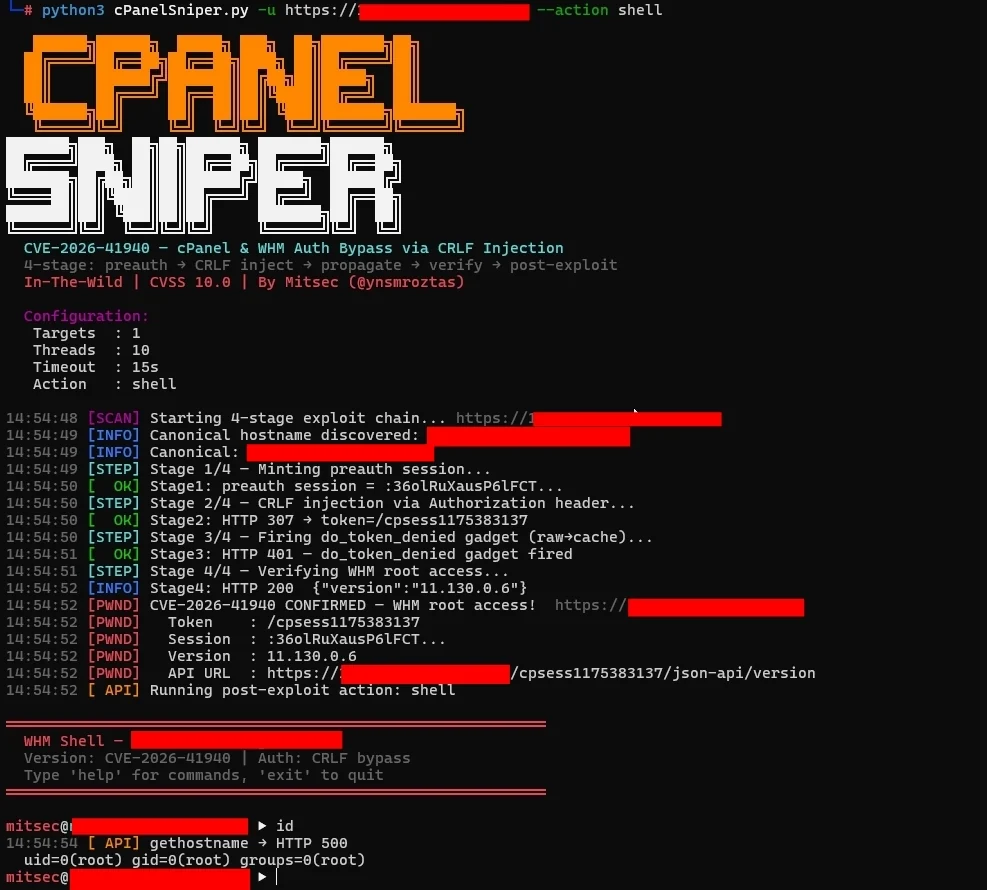 44pie/cpsniper
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets
 umakant76705/cve-2022-22978
Step-by-step demonstration of CVE-2022-22978 authorization bypass in Spring Security's RegexRequestMatcher, with vulnerable app setup, payload…
 th-secforge/cve-2025-29972
CVE-2025-29927 - Critical Security Vulnerability in Next.js
 zs1n/cve-2025-29927
PoC | NextJS Middleware 15.2.2 - Authorization Bypass
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…