
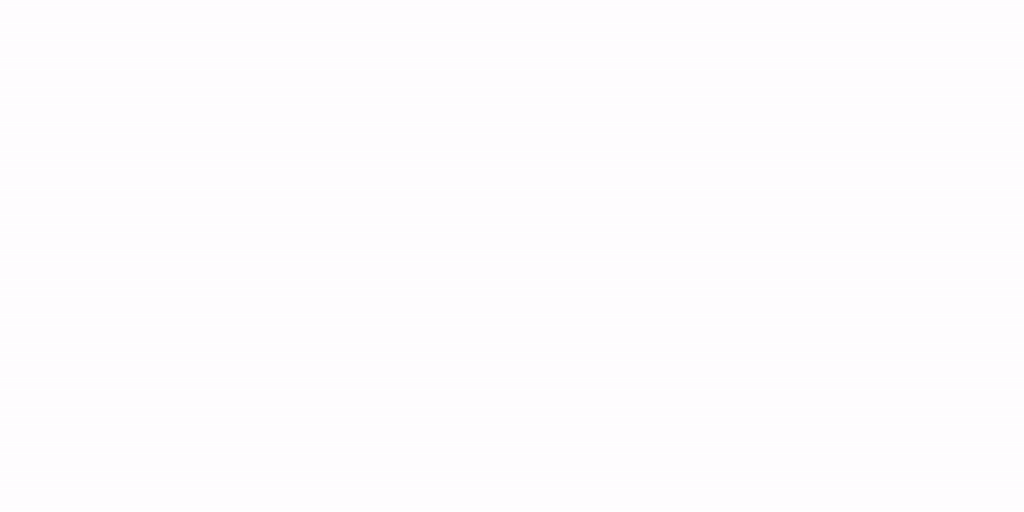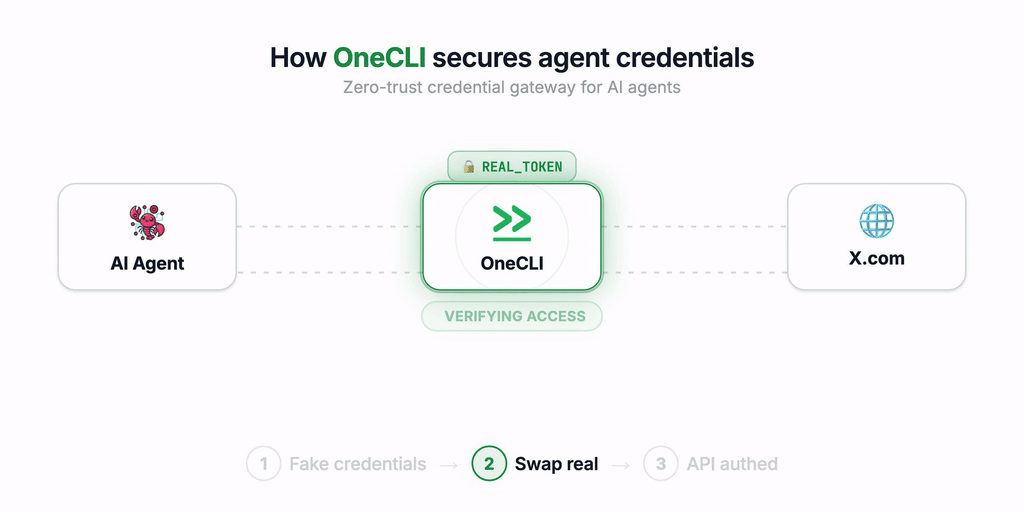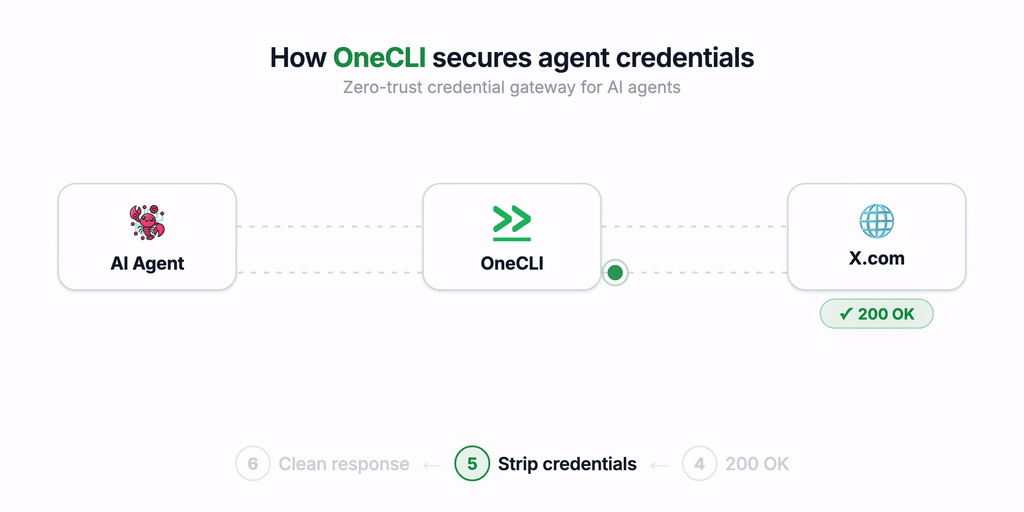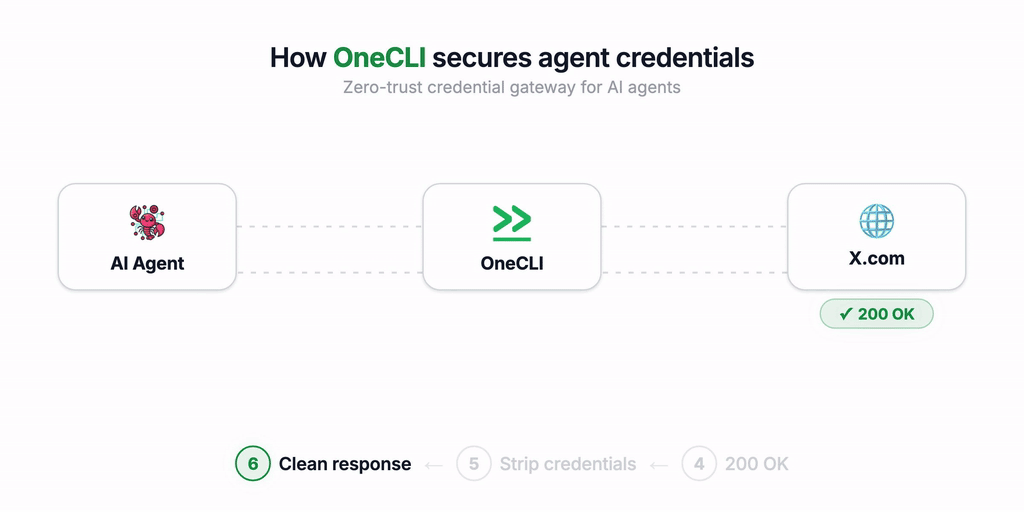
onecli
 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
ai-securityapi-securityauthentication-authorization+5
2.9k21h 34m ago
onecli/onecliOpen-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 ovh/the-bastion
Authentication, authorization, traceability and auditability for SSH accesses.
 cube0x0/nopac
CVE-2021-42287/CVE-2021-42278 Scanner & Exploiter.
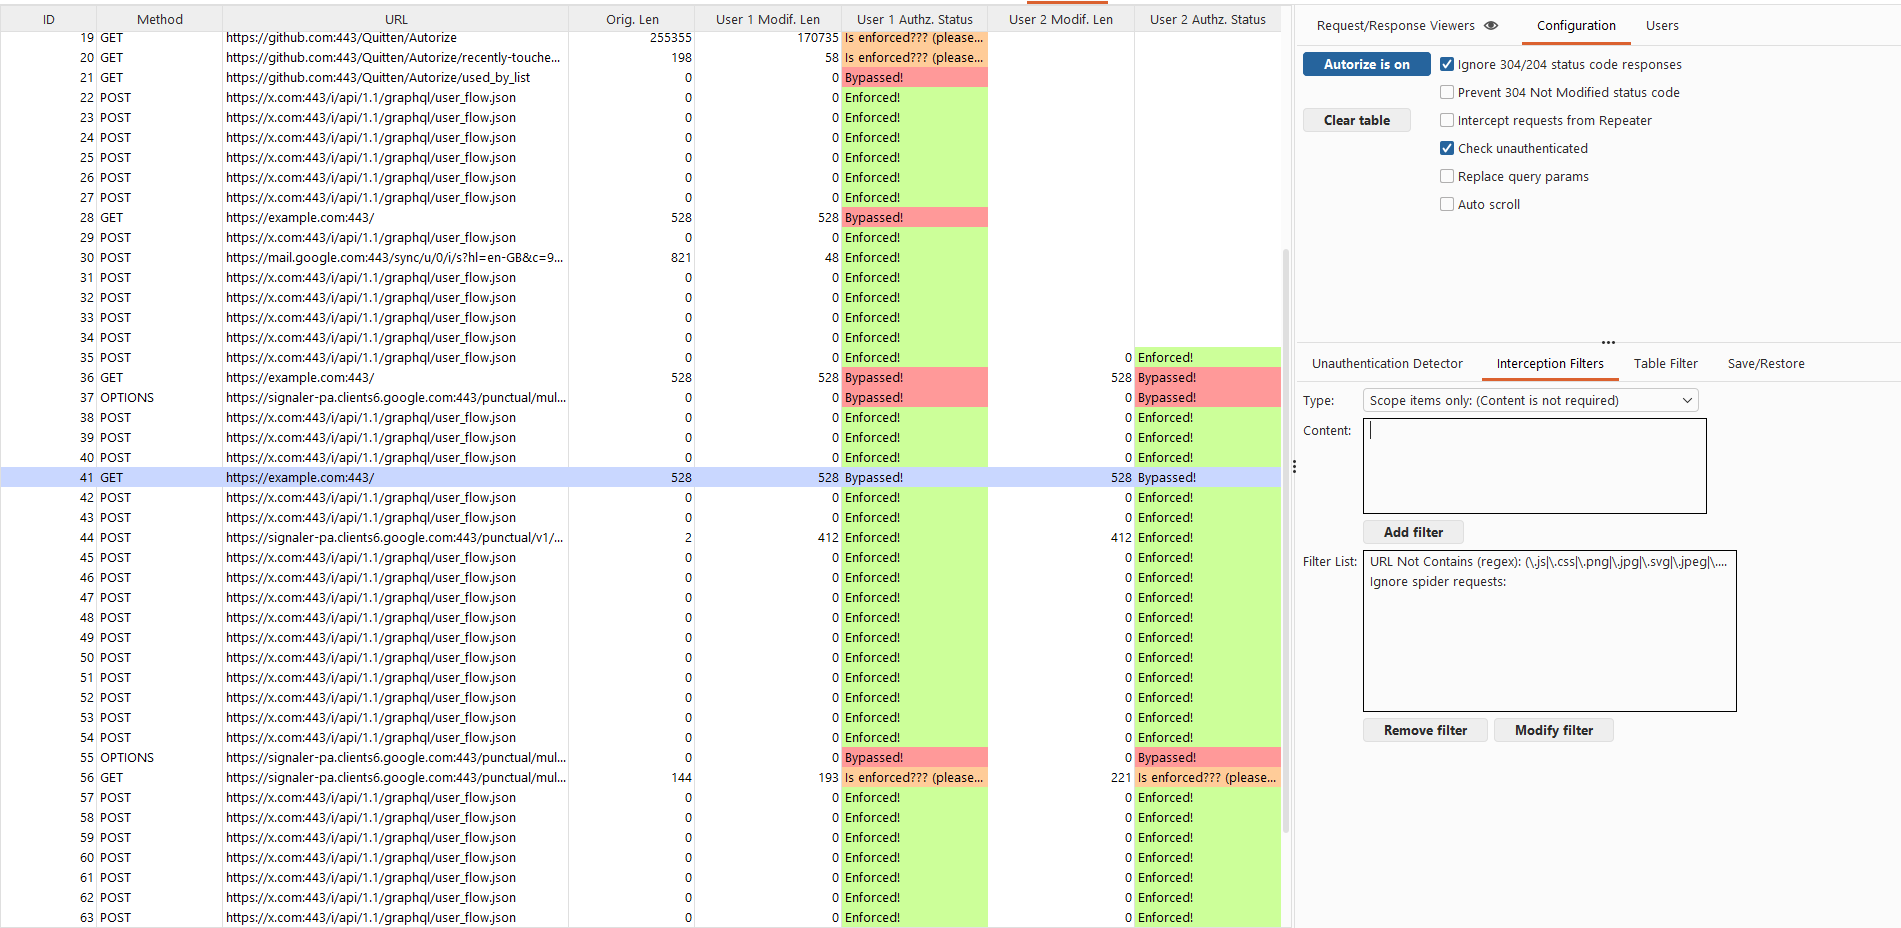 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 openbmc/bmcweb
A do everything Redfish, KVM, GUI, and DBus webserver for OpenBMC
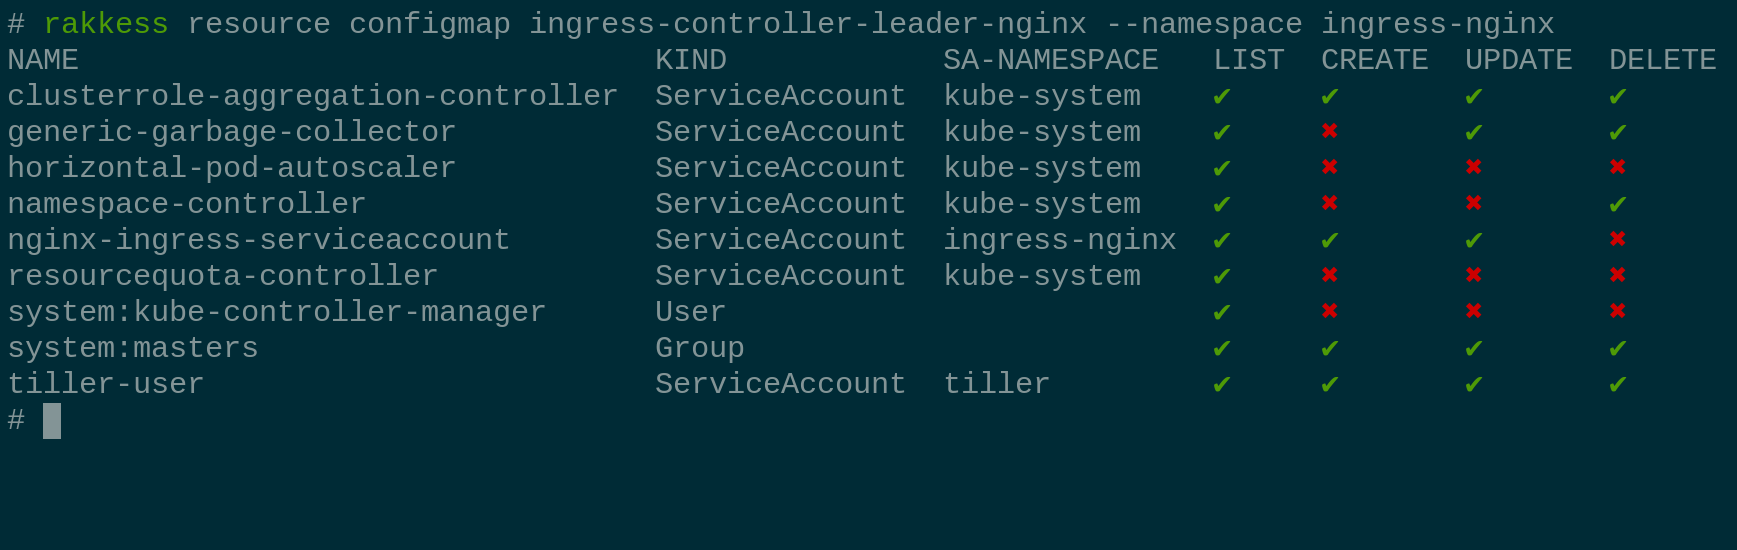 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
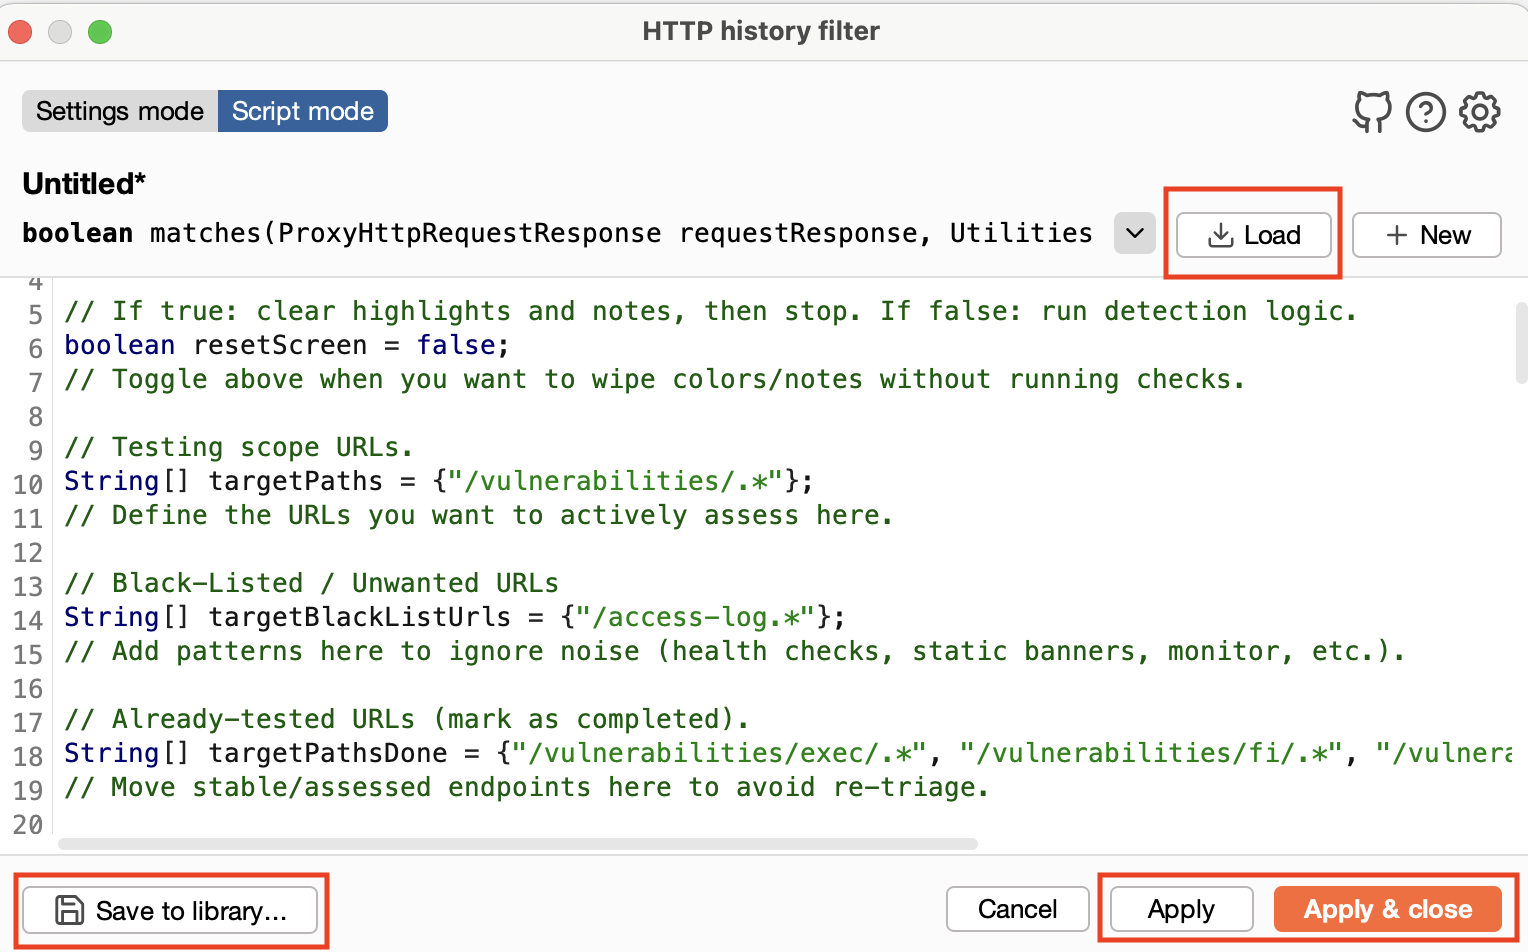 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 kontext-security/kontext-cli
Runtime security for AI agents: discover agents, map their permissions, and enforce what they can do.
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…