authentik
Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…

Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…

Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…

A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.

Squid Web Proxy Cache - Source Code

Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.

A reverse proxy like nginx, built on pingora, simple and efficient.

Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software

A security-first reverse proxy built to guard the free web.

Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…

CVE-2026-29000 – pac4j-jwt Authentication Bypass (CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…

🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…

A reverse proxy that provides authentication with Google, Azure, OpenID Connect and many more identity providers.

Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…

Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…

Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem

Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…

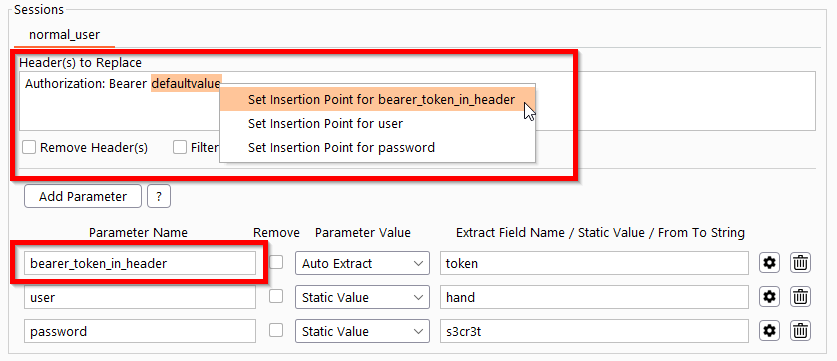
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.