
CVE-2025-31161
 0xblackash/cve-2025-31161
CVE-2025-31161
authentication-authorizationeducationexploitation+3
0xblackash/cve-2025-31161CVE-2025-31161
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 ololadeabiola03/aisecplus-week01-servicenow-ai-security-incident
Research and analysis of the ServiceNow Virtual Agent vulnerability (CVE-2025-12420), including attack flow, MITRE ATT&CK mapping, detection…
 0xblackash/cve-2025-64446
CVE-2025-64446
 n0n4m3x41/cve-2025-1739
0day PoC for CVE-2025-1739
 shahin-shadow/nextjs-auth-bypass
Analysis and exploitation of a Next.js authorization bypass vulnerability (CVE-2025-29927)
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 enochgitgamefied/nextjs-cve-2025-29927-docker-lab
Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…
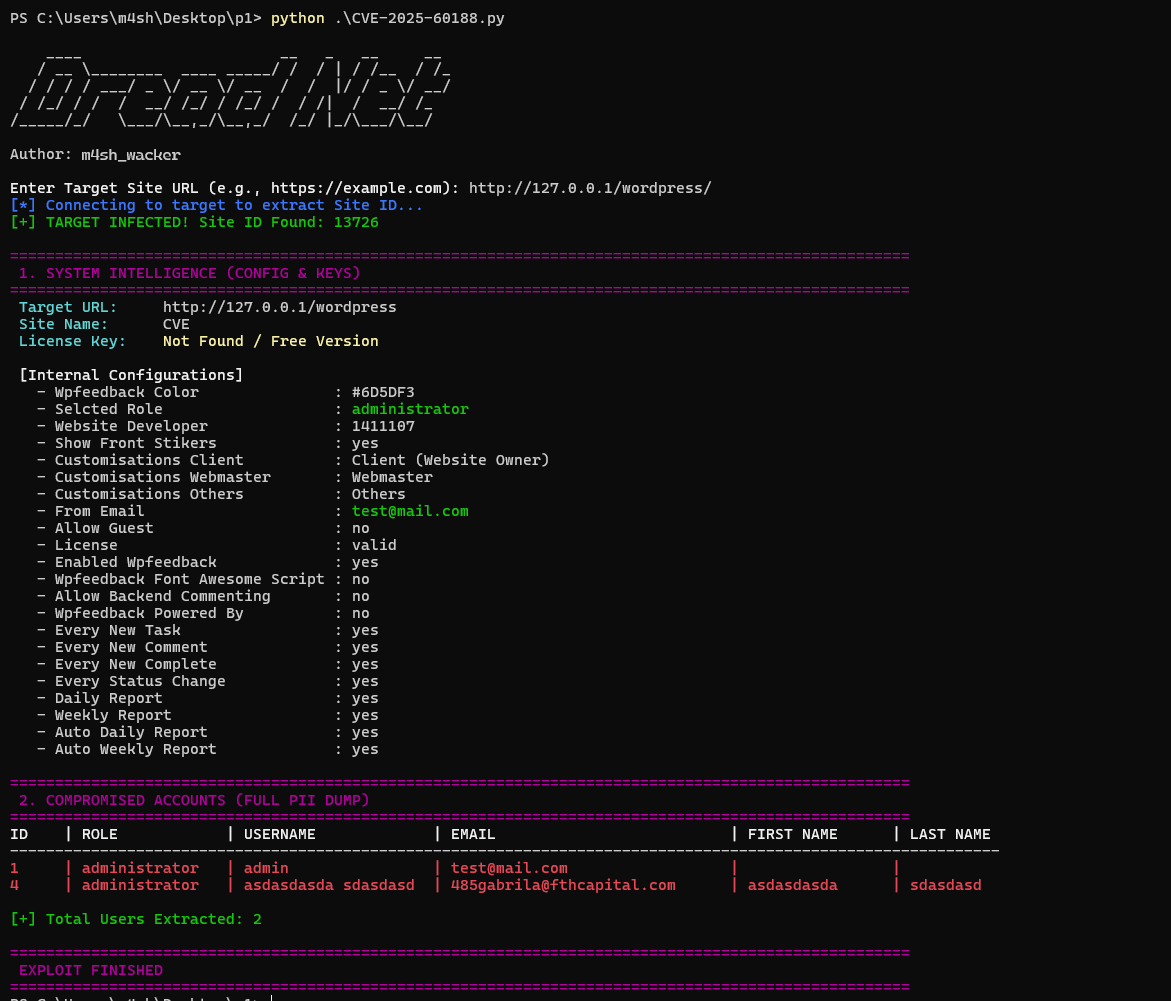 m4sh-wacker/cve-2025-60188-atarim-plugin-exploit
CVE-2025-60188 Atarim Plugin Exploit
 sneden/zeroheight-account-verification-bypass-cve-2025-65925
Independent security finding – Zeroheight account creation bypass via missing verification enforcement (patched June 2025)
 moften/cve-2025-29927_next.js_auth_bypass
Next.js Auth Bypass PoC Edge Runtime Env Leak via Middleware Bug
 nxploited/cve-2025-8359
AdForest <= 6.0.9 - Authentication Bypass to Admin
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 iteride/cve-2025-2825
Detailed analysis and PoC exploit for CVE-2025-2825, an authentication bypass in CrushFTP. Includes nuclei templates, multi-threaded scanner, and…
 6lj/cve-2025-3639
login bypass vulnerability in Liferay Portal (versions 7.3.0–7.4.3.132) and Liferay DXP (various versions from 2024.Q1 to 2025.Q1.6)
 blueisbeautiful/cve-2025-54309
CrushFTP AS2 Authentication Bypass
 0xgh057r3c0n/cve-2025-34077
Poc for Unauthenticated Admin Session Hijack - Pie Register Plugin (≤ 3.7.1.4)
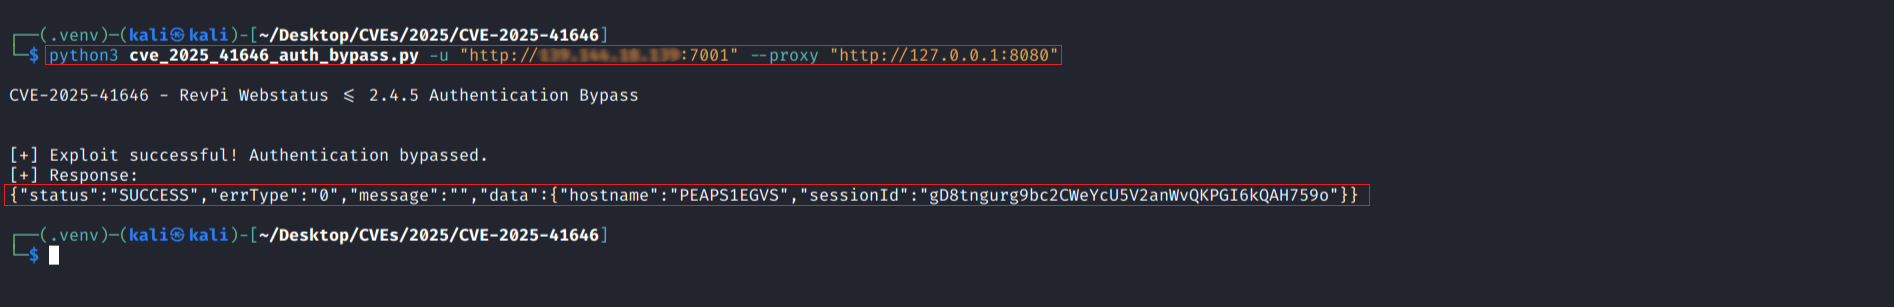 r0otk3r/cve-2025-41646
Python exploit script for CVE-2025-41646, an authentication bypass in RevPi Webstatus <= 2.4.5. Supports single/mass exploitation, proxy, silent…