

Aegis
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
android-securityauthenticationauthentication-authorization+5
13.1k
beemdevelopment/aegisA free, secure and open source app for Android to manage your 2-step verification tokens.
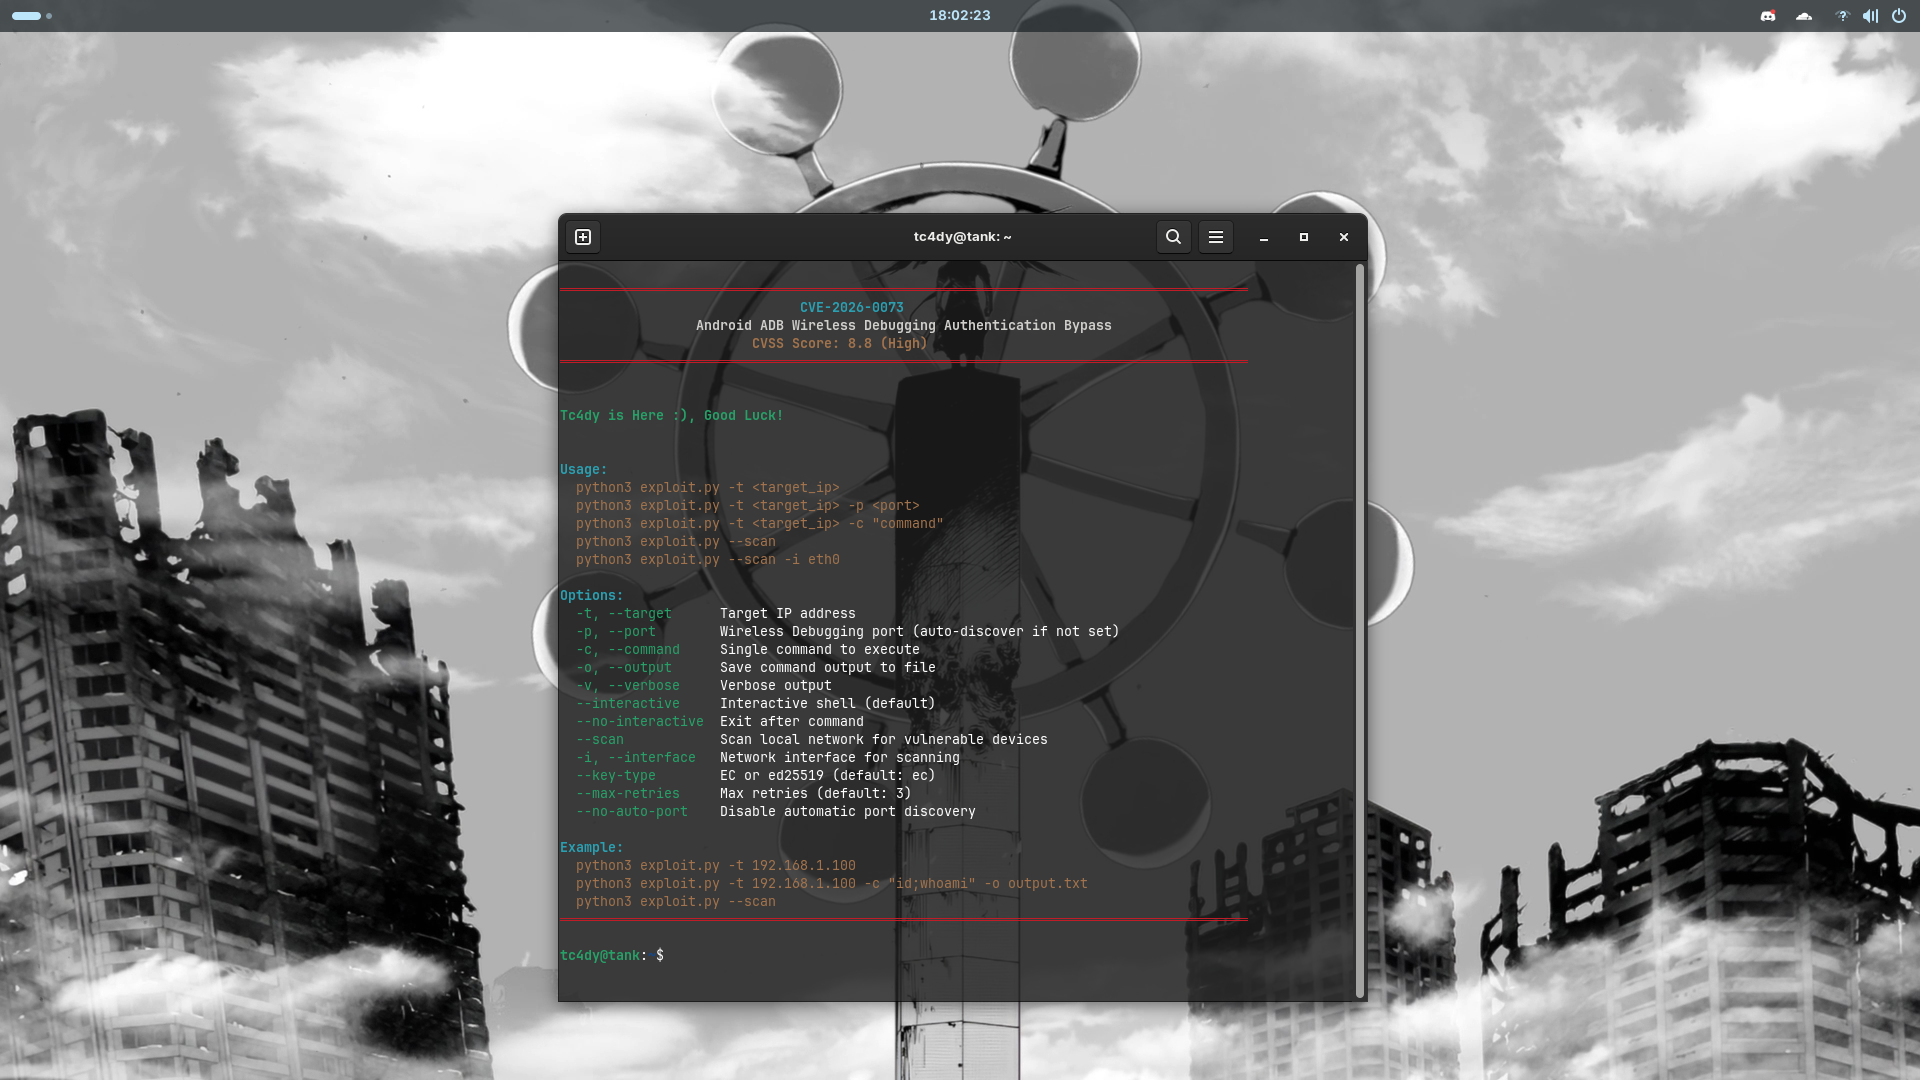 tc4dy/cve-2026-0073-poc-exploit
🚀 CVE-2026-0073 - Android ADB Wireless Debugging Exploit (CVSS 8.8) 🔓 Zero-click authentication bypass via TLS type confusion. Gain interactive…
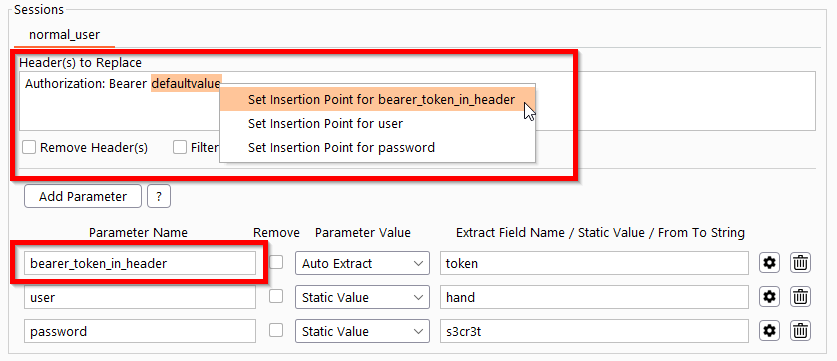 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 quarkslab/android-hardware-attestation-demo
An Android HW Attestation demo
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 foxer131/cve-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 horkimhab/cve-2026-0257
CVE-2026-0257 - PAN-OS
 bhanunamikaze/badhost-cve-2026-48710-exploit
Detection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 kill1234545/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 rachidafaf/bola-cve-2023-27524
Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…