

Aegis
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
android-securityauthenticationauthentication-authorization+5
12.9k
beemdevelopment/aegisA free, secure and open source app for Android to manage your 2-step verification tokens.
 quarkslab/android-hardware-attestation-demo
An Android HW Attestation demo
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
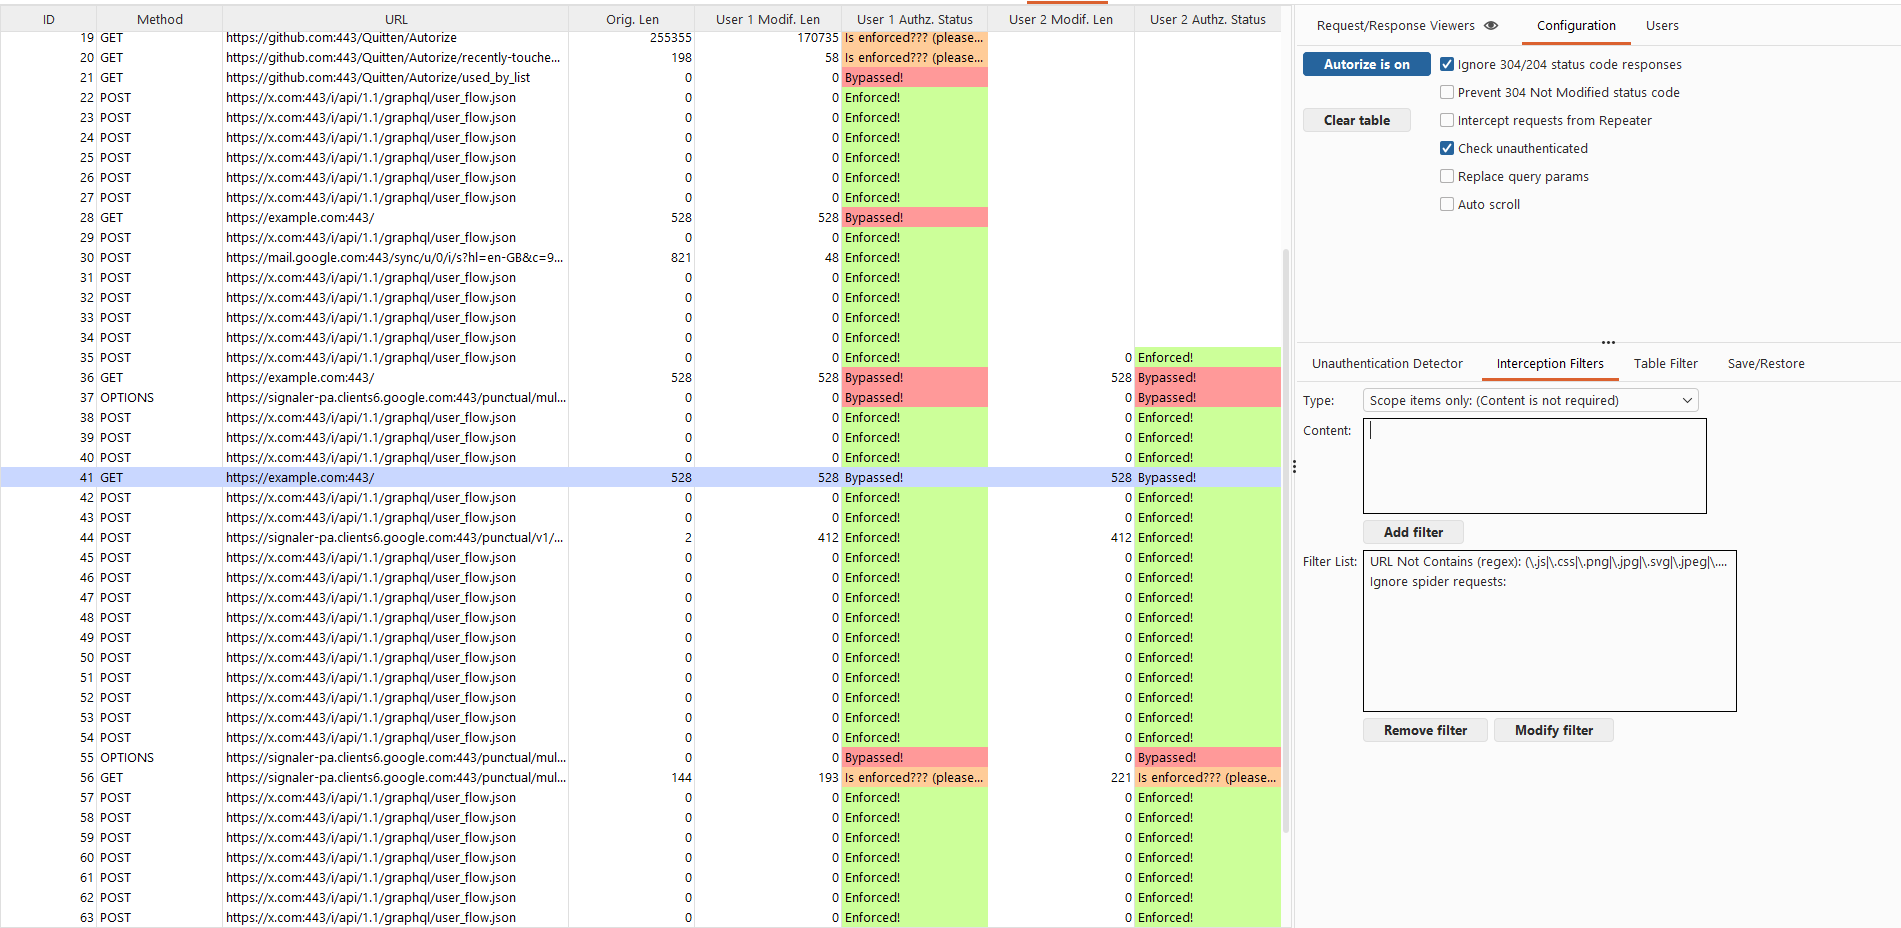 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 bhanunamikaze/badhost-cve-2026-48710-exploit
Detection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
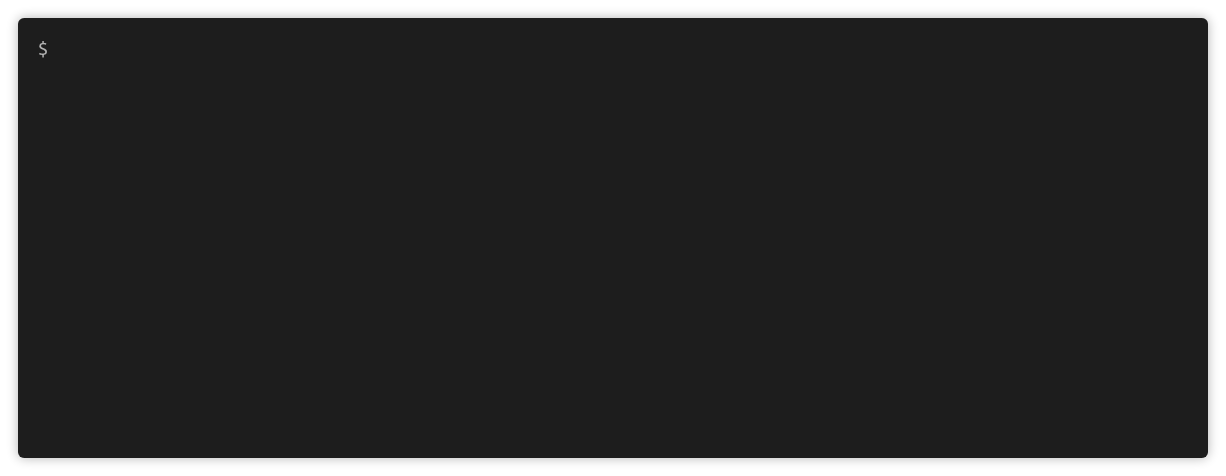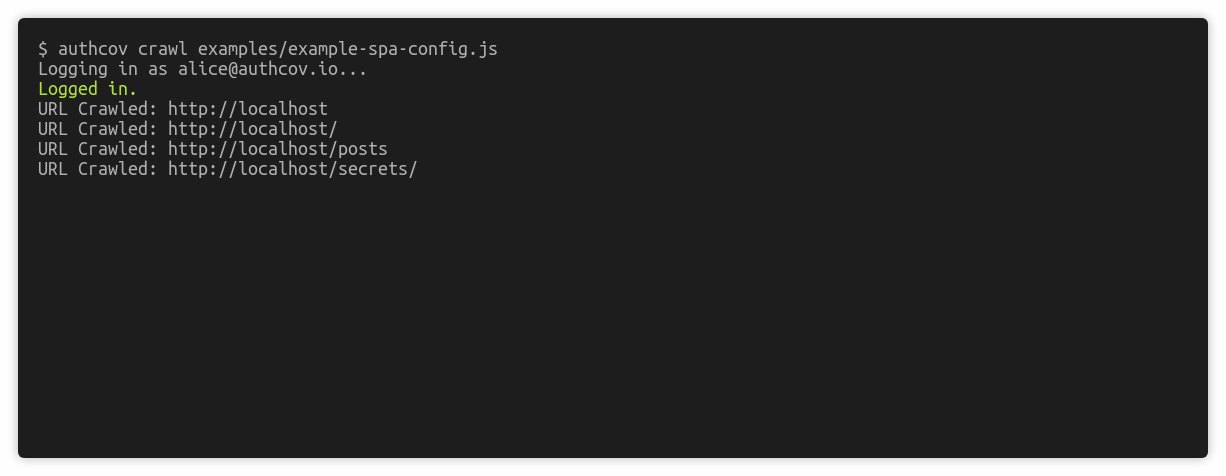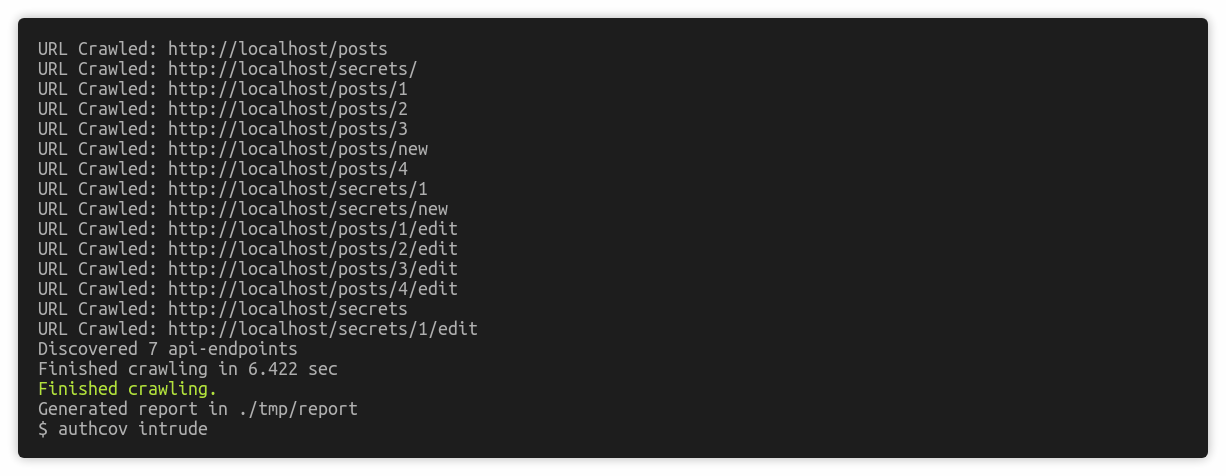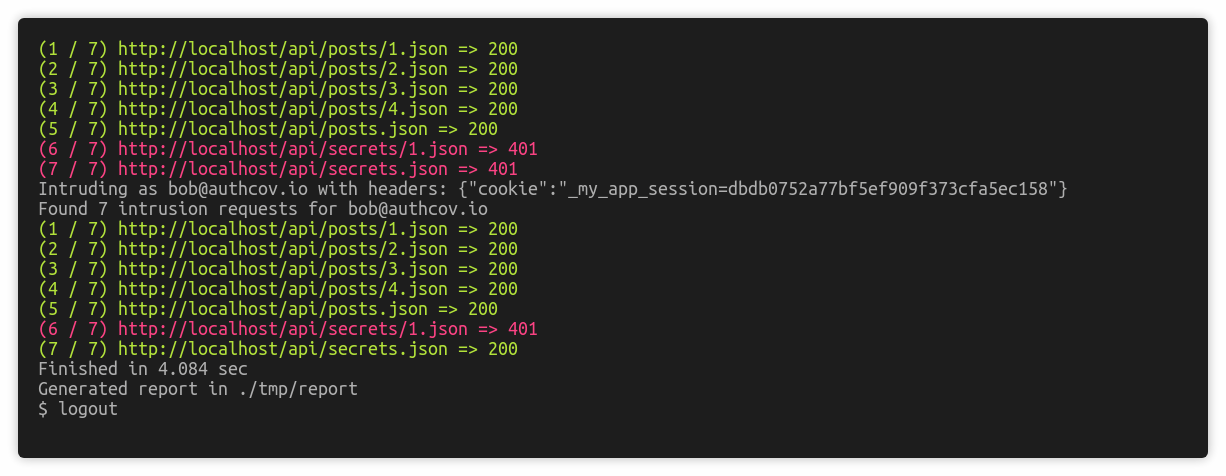 authcov/authcov
Web app authorisation coverage scanning
 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 0xsu3ks/cve-2025-29556
PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 lstudlo/nextjs-cve-demo
演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 ethicalgrey/phpbb-cve-2026-48611
Automated PoC for CVE-2026-48611 — phpBB OAuth login_link authentication bypass
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…