

raider
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
owasp/raiderOWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
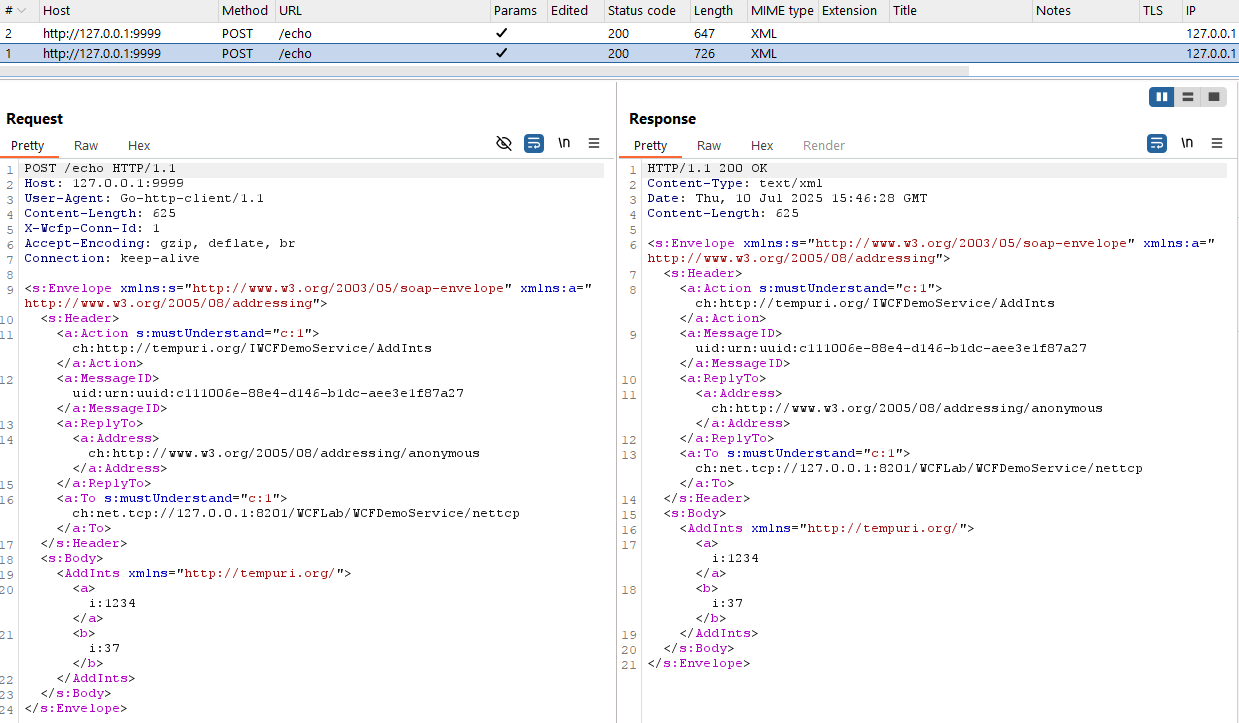 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
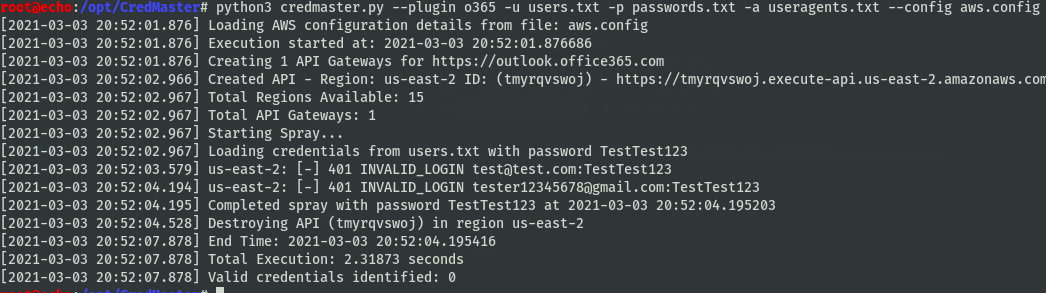 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 compasssecurity/samlraider
SAML2 Burp Extension
 logisek/huntcyberark
CyberArk Security Audit
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
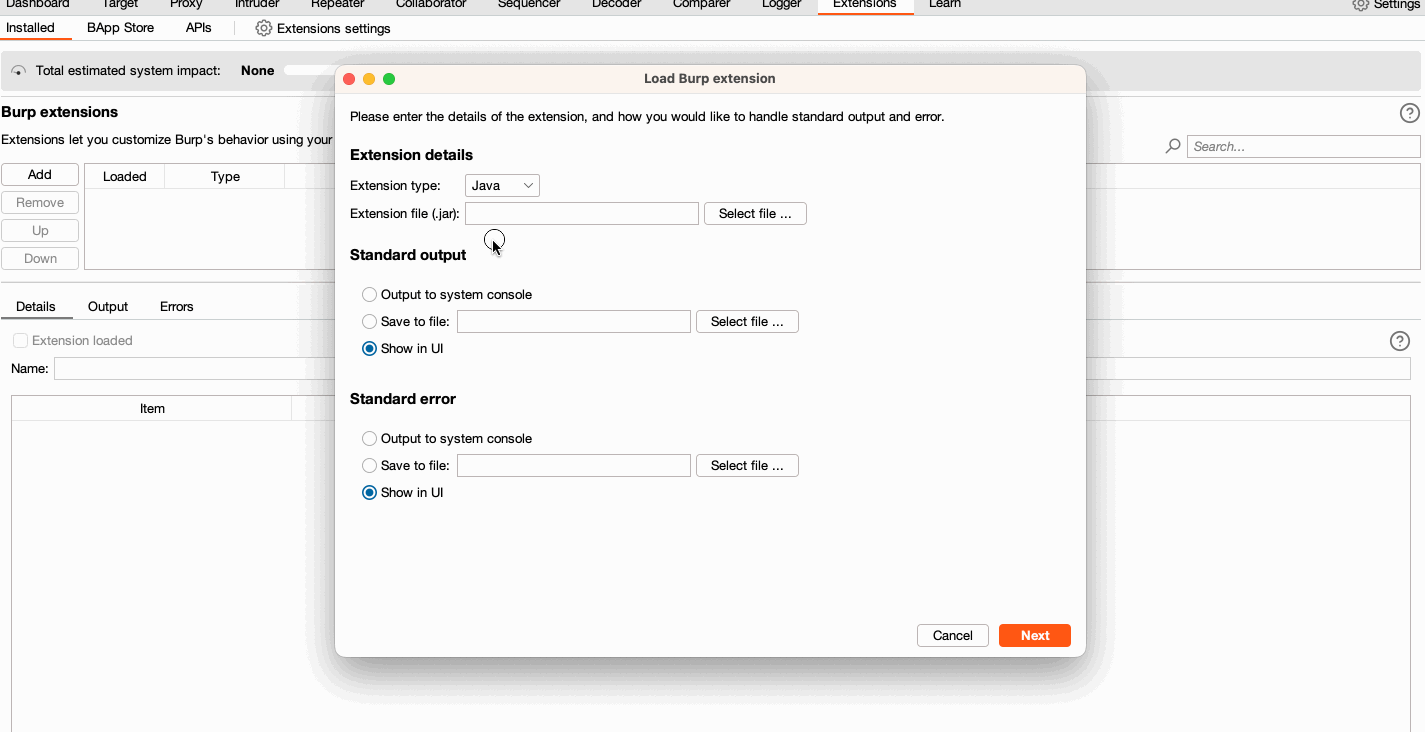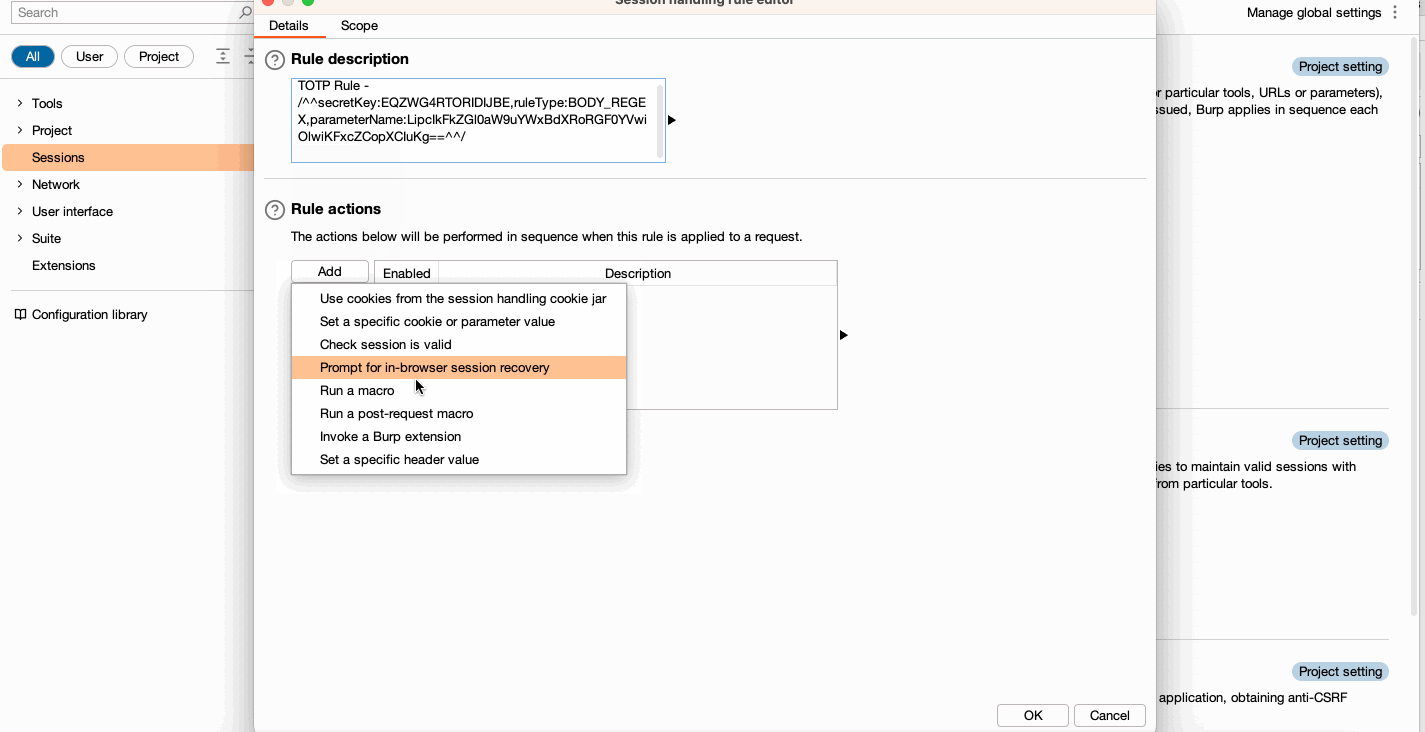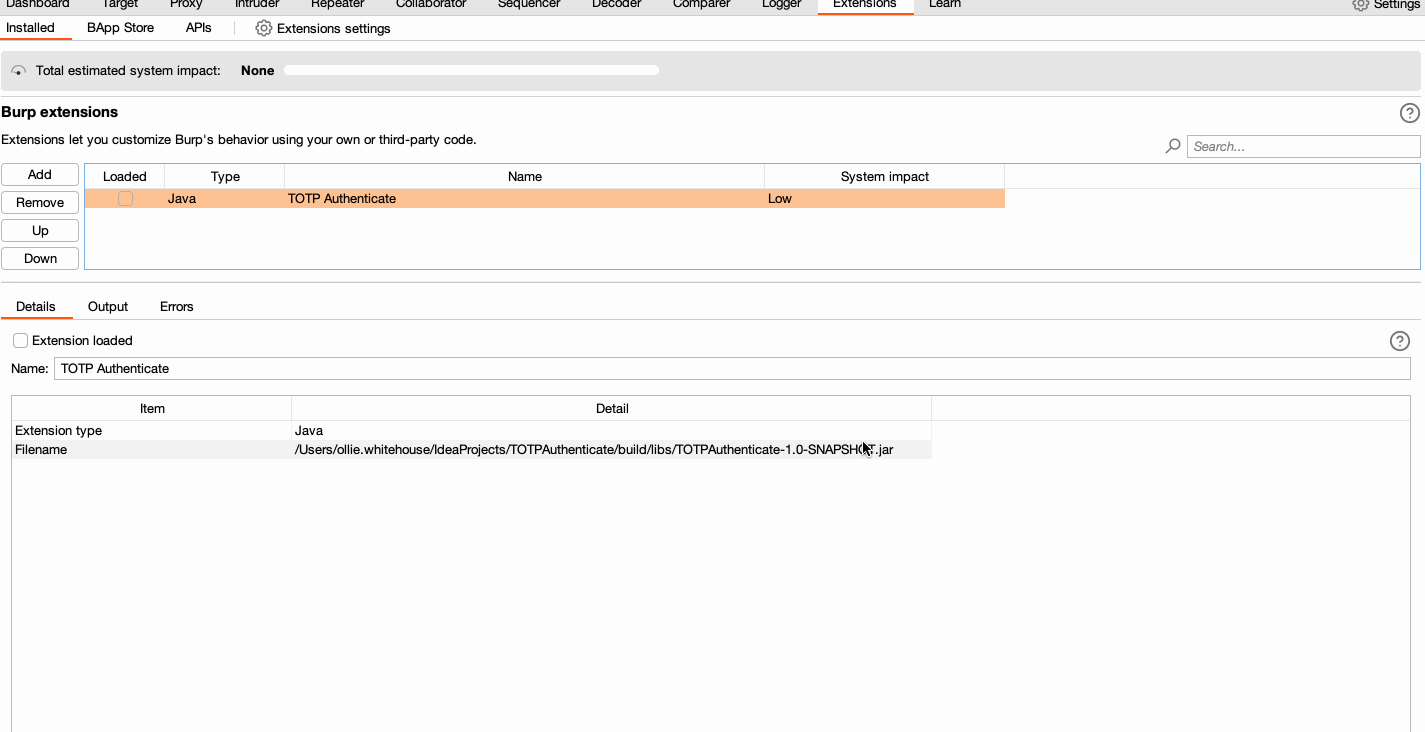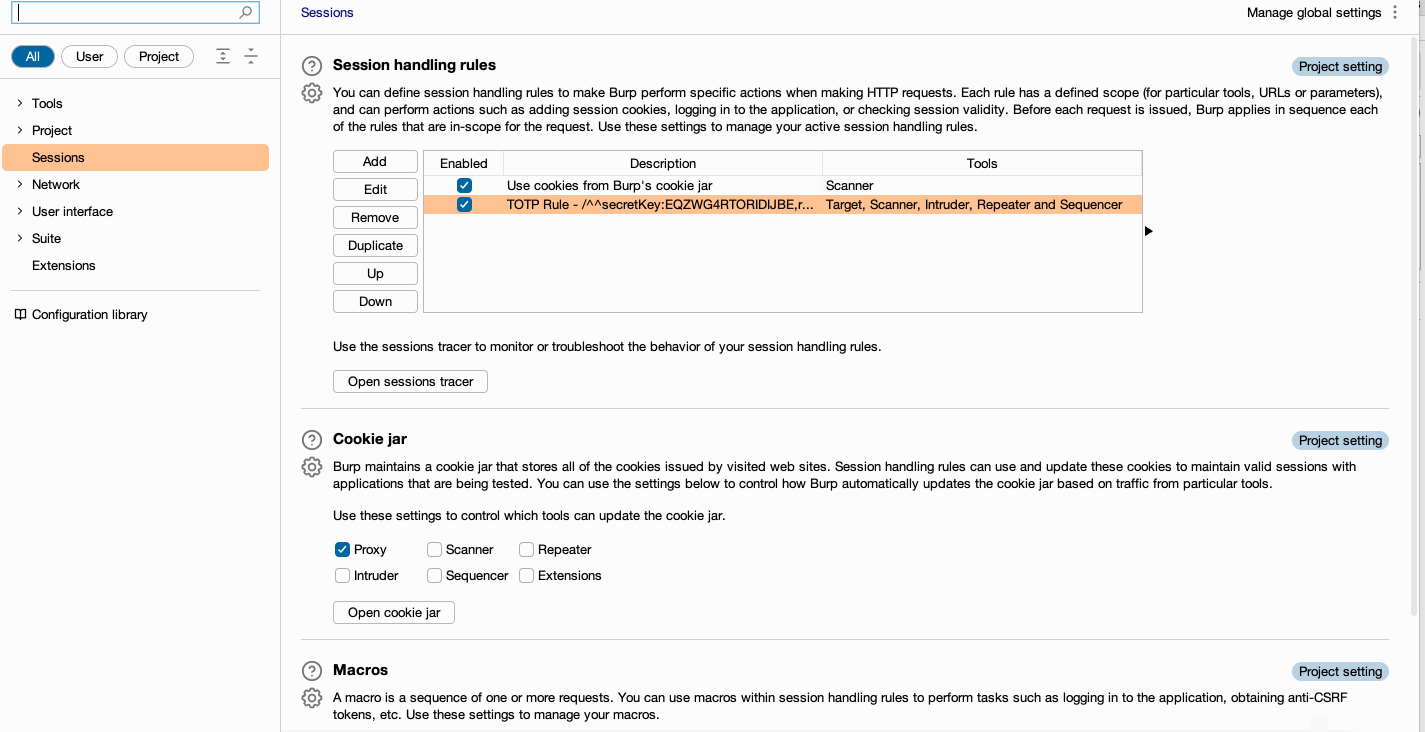 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 randomrobbiebf/cve-2023-45828
RumbleTalk Live Group Chat <= 6.1.9 - Missing Authorization via handleRequest