

raider
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
101
owasp/raiderOWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 logisek/huntcyberark
CyberArk Security Audit
 davidvrns/cve-2026-5430-wso2
Detection PoC for CVE-2026-5430 — unauthenticated JWT algorithm bypass (CVSS 10.0) affecting WSO2 API Manager 4.1.0–4.6.0. Read-only assessment tool…
 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 compasssecurity/samlraider
SAML2 Burp Extension
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 d0ge/xsw
XML Signature Wrapping Burp Suite Extensions
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
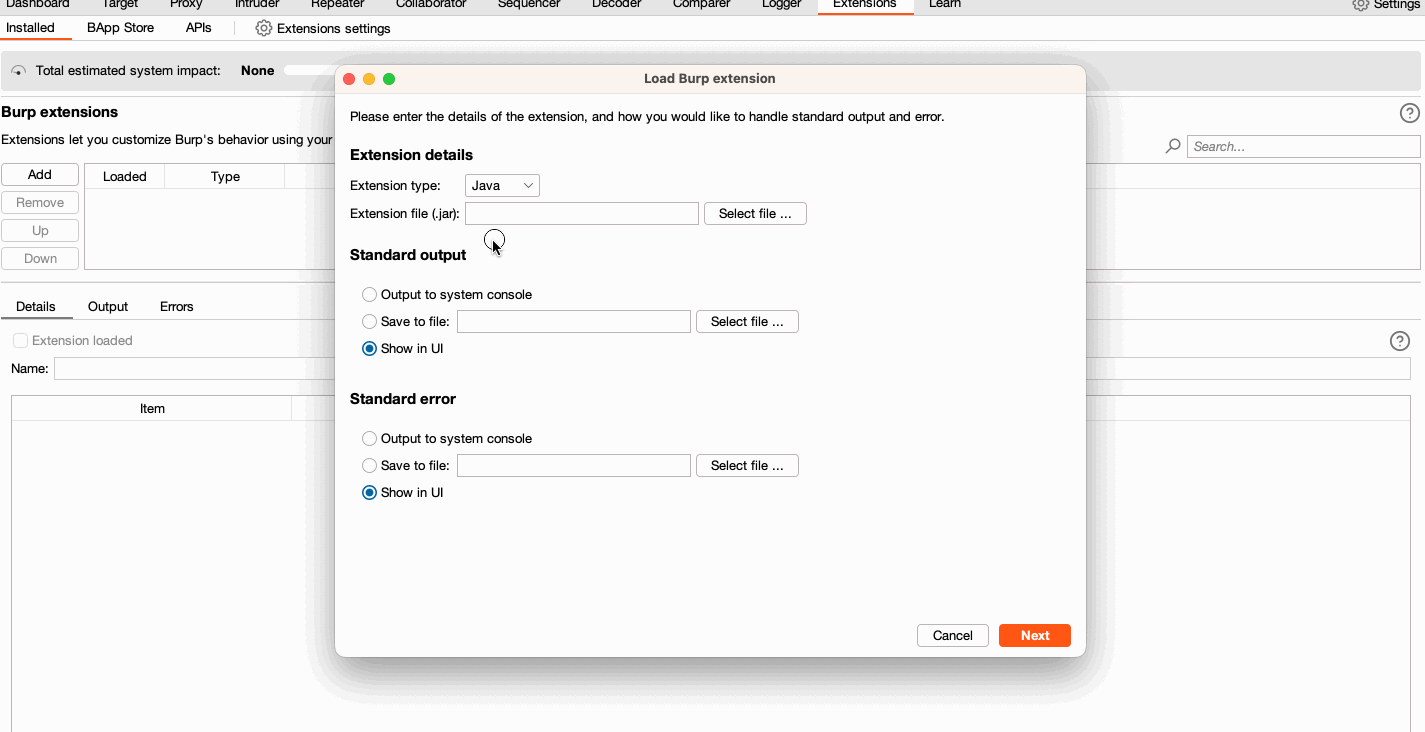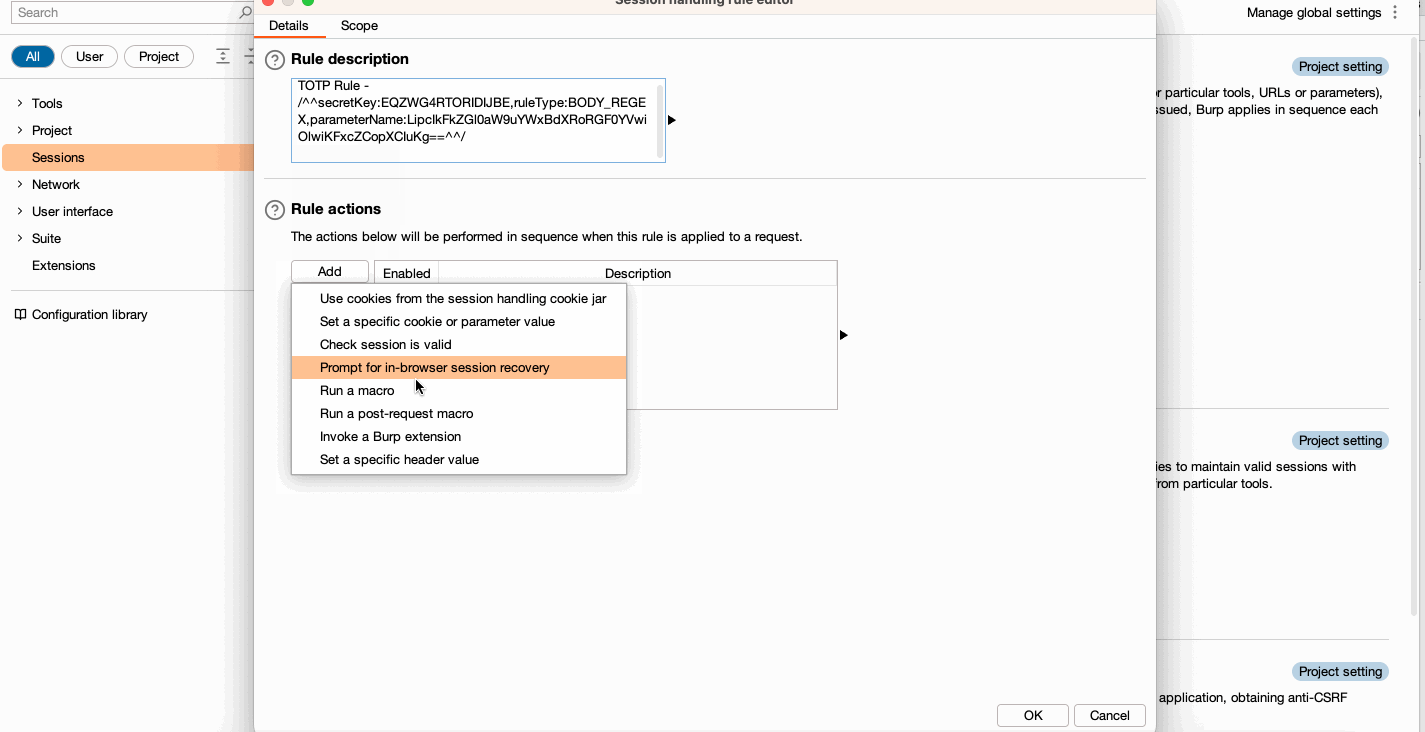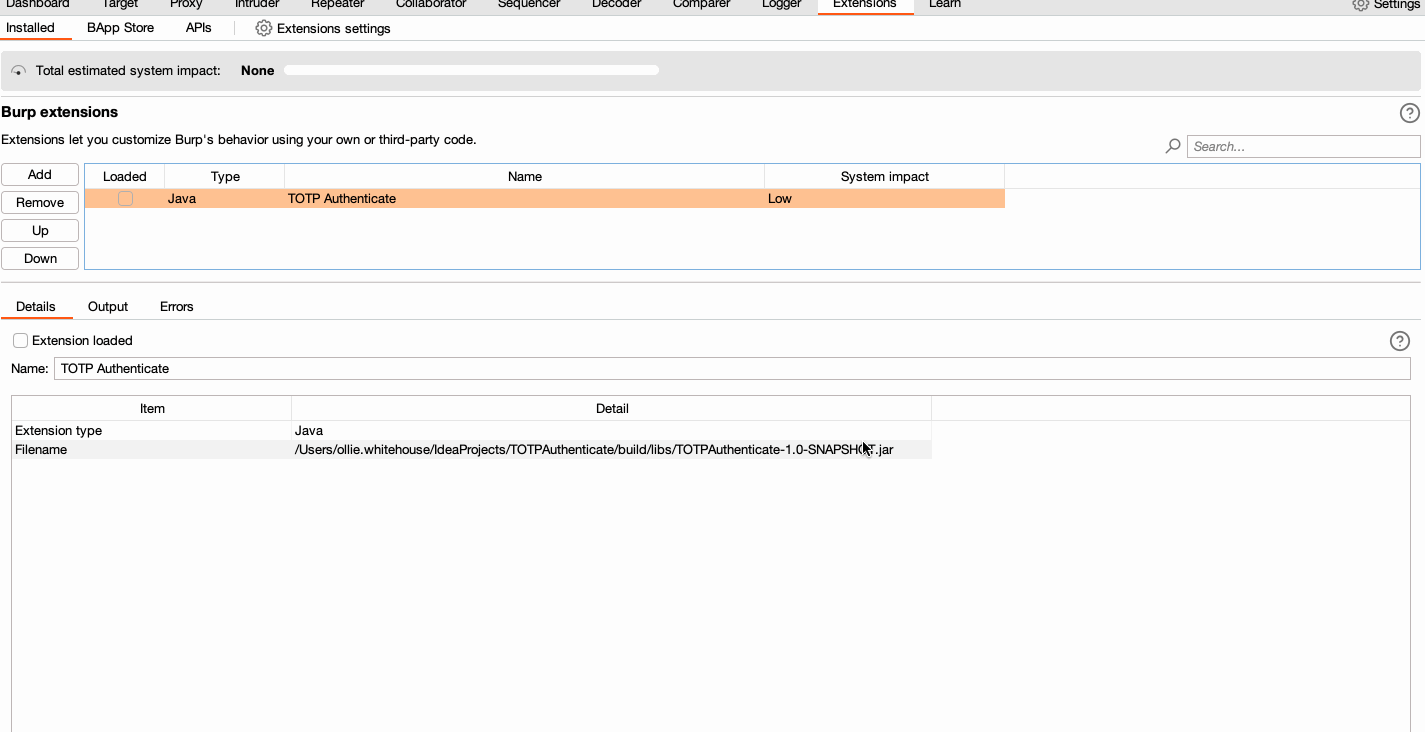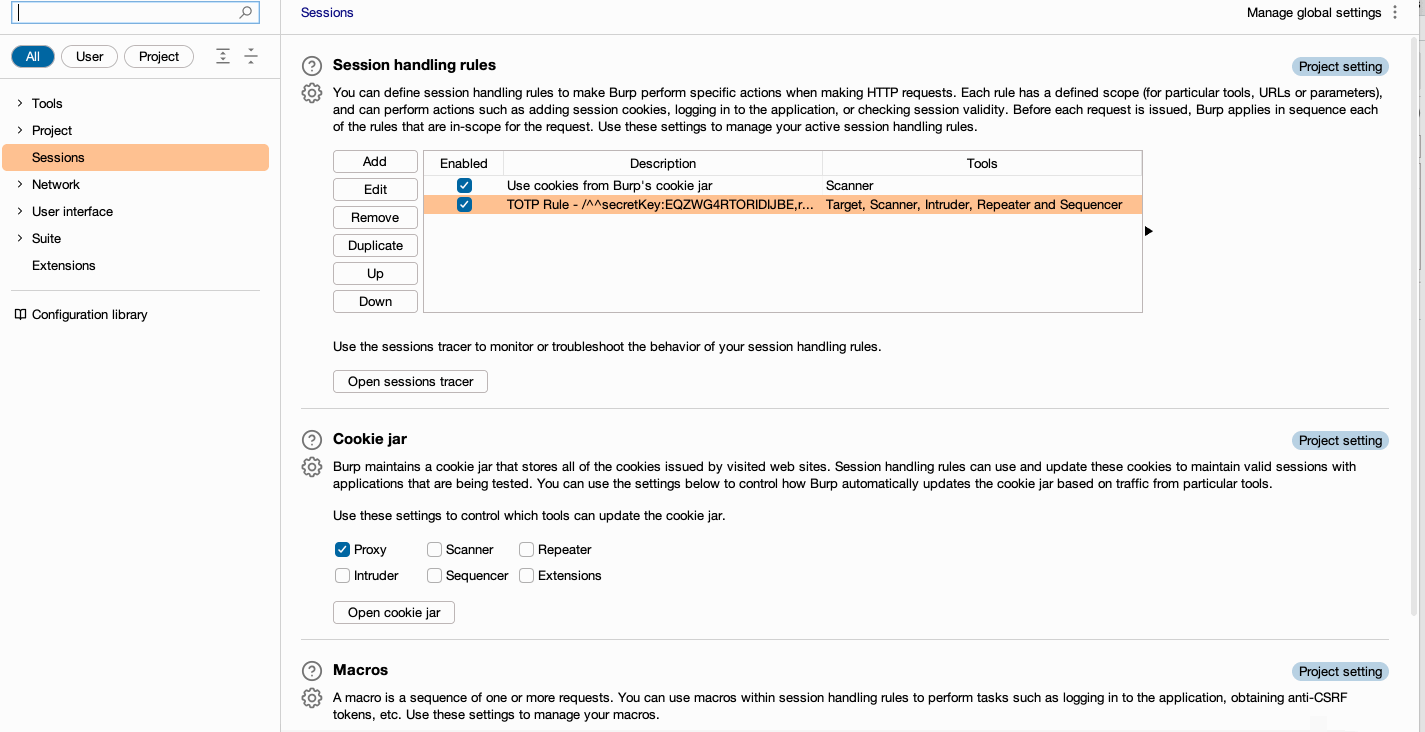 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 getdrive/wso2_cve-2026-5430_lab
Уязвимая лаборатория WSO2 API Manager 4.5.0 в Docker, сканер и эксплойт для CVE-2026-5430 (обход аутентификации через поддельный HS256 JWT)
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion