
CVE-2026-25253
 yym8538/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
authenticationdata-exfiltrationexploitation+6
1
yym8538/cve-2026-25253Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
 faceless0x7/cve-2026-93453
Python PoC for CVE-2026-93453, a SOGo password reset link poisoning flaw via attacker-controlled Origin header that enables reset token interception…
 muhammedhussein17/keycloak
Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 bombobombone/cve-2026-73310
Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 bombobombone/cve-2026-73312
Proof-of-concept and technical write-up for CVE-2026-73312, an OAuth2 refresh token replay vulnerability in XenForo before 2.3.13. Includes a Python…
 0xlyvio/cve-2026-1529-keycloak-exploit-tool
Keycloak: Unauthorized organization registration via improper invitation token validation
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
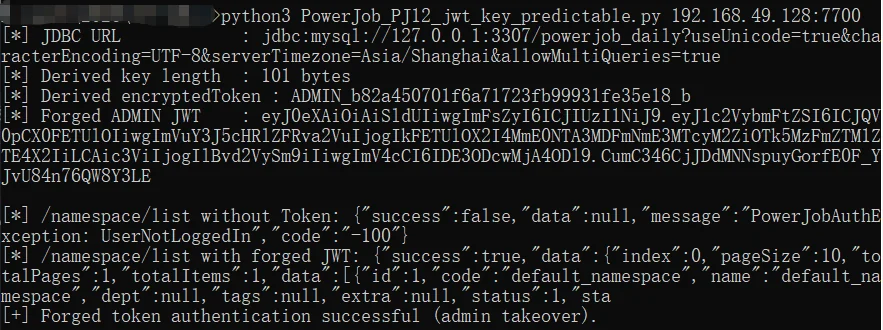 unpredictable21/cve-2026-75431_powerjob_jwt_key_predictable
Demonstrates a critical JWT signing key predictability vulnerability in PowerJob Server, allowing offline key derivation and token forgery for admin…
 vxssroott/cve-2026-78905-facebook-account-takeover
Social Media Infrastructure Vulnerability Research. CVE-2026-78905: OAuth token reuse and session hijacking in Facebook's Graph API.
 kaleth4/cve-2026-21858
Automated exploit chain for n8n achieving unauthenticated arbitrary file read, admin token forgery, and sandbox bypass to remote code execution via…
 dhammon/hoteldruid-cve-2021-42949
Exploit for CVE-2021-42949 in HotelDruid v3.0.3, demonstrating predictable session token generation and authentication bypass via brute force.
 ackemed/cve-2026-1529-poc-keycloak-unauthorized-registration-via-improper-invitation-token-validation
Exploit tool for CVE-2026-1529, demonstrating unauthorized organization registration in Keycloak via JWT token manipulation. Includes token…
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
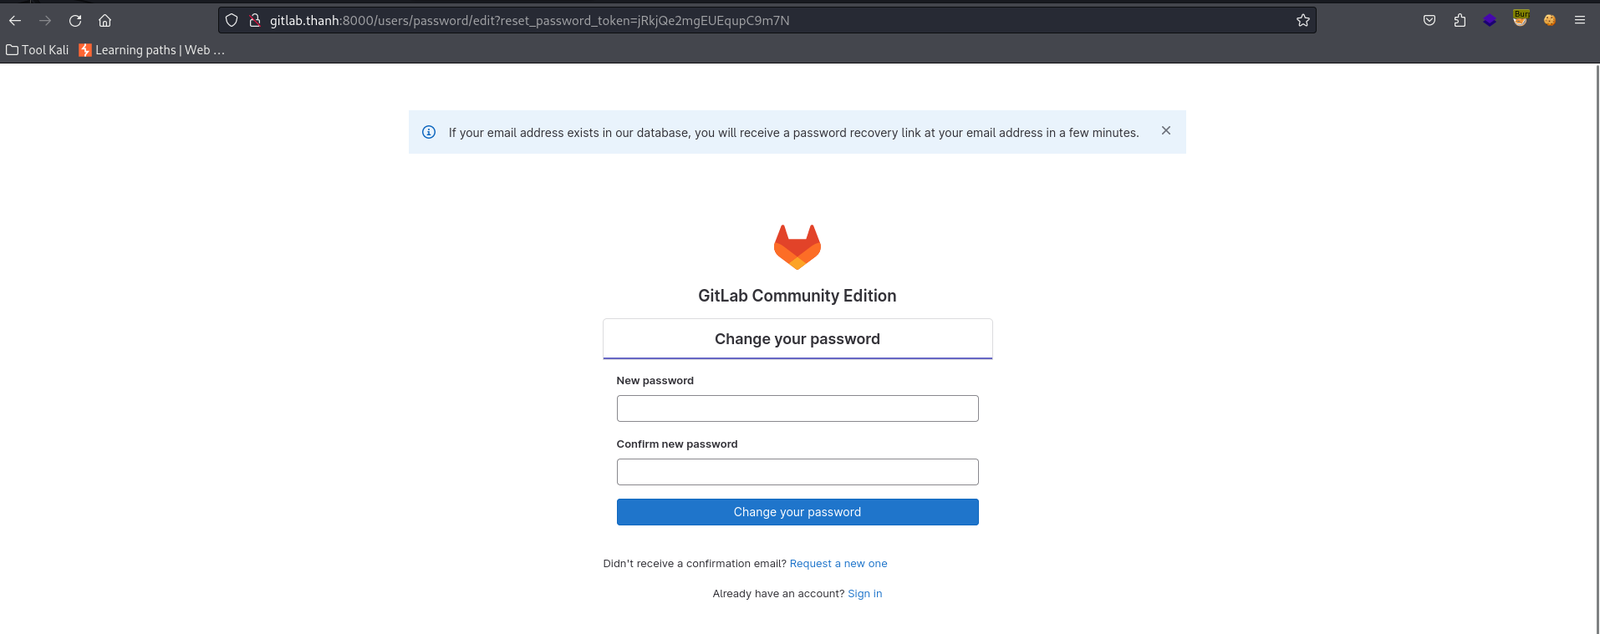 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 kagantua/cpanelwhm-authbypass
Go-based scanner and exploit tool for CVE-2026-41940, an authentication bypass in cPanel/WHM. Supports batch scanning, token leakage, and…