
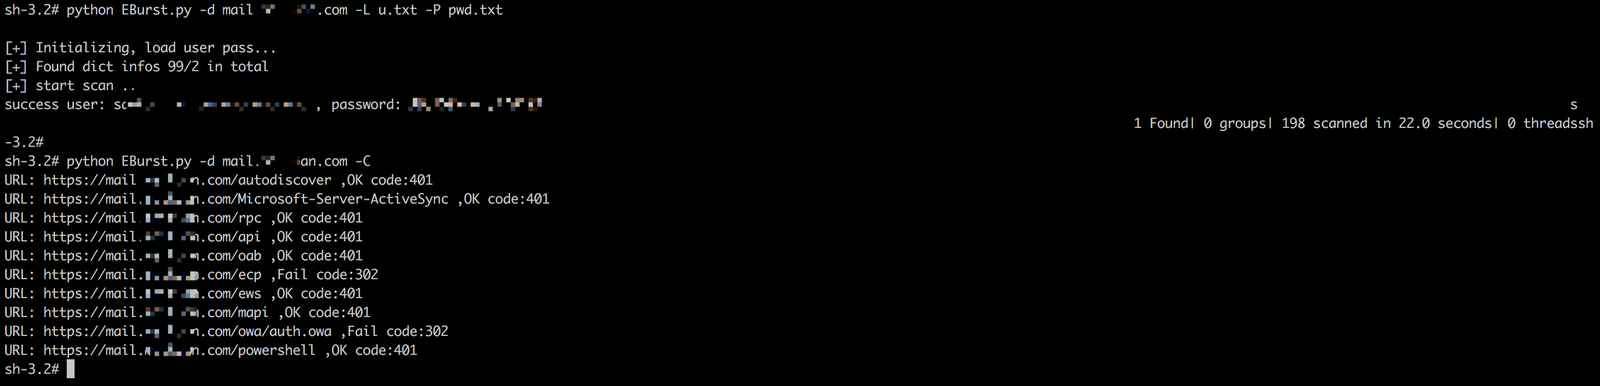
EBurst
 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
authenticationemail-securityinformation-gathering+4
grayddq/eburst这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 pervinzahidli/cve-2026-103977
Session-scoped TOTP rate limiting permits repeated verification attempts
 synacktiv/aadoutsider-py
Python3 rewrite of AsOutsider features of AADInternals
 christbowel/cve-2026-25050
Proof-of-concept exploit for CVE-2026-25050, a timing attack enabling user enumeration via GraphQL authentication. Measures response times to…
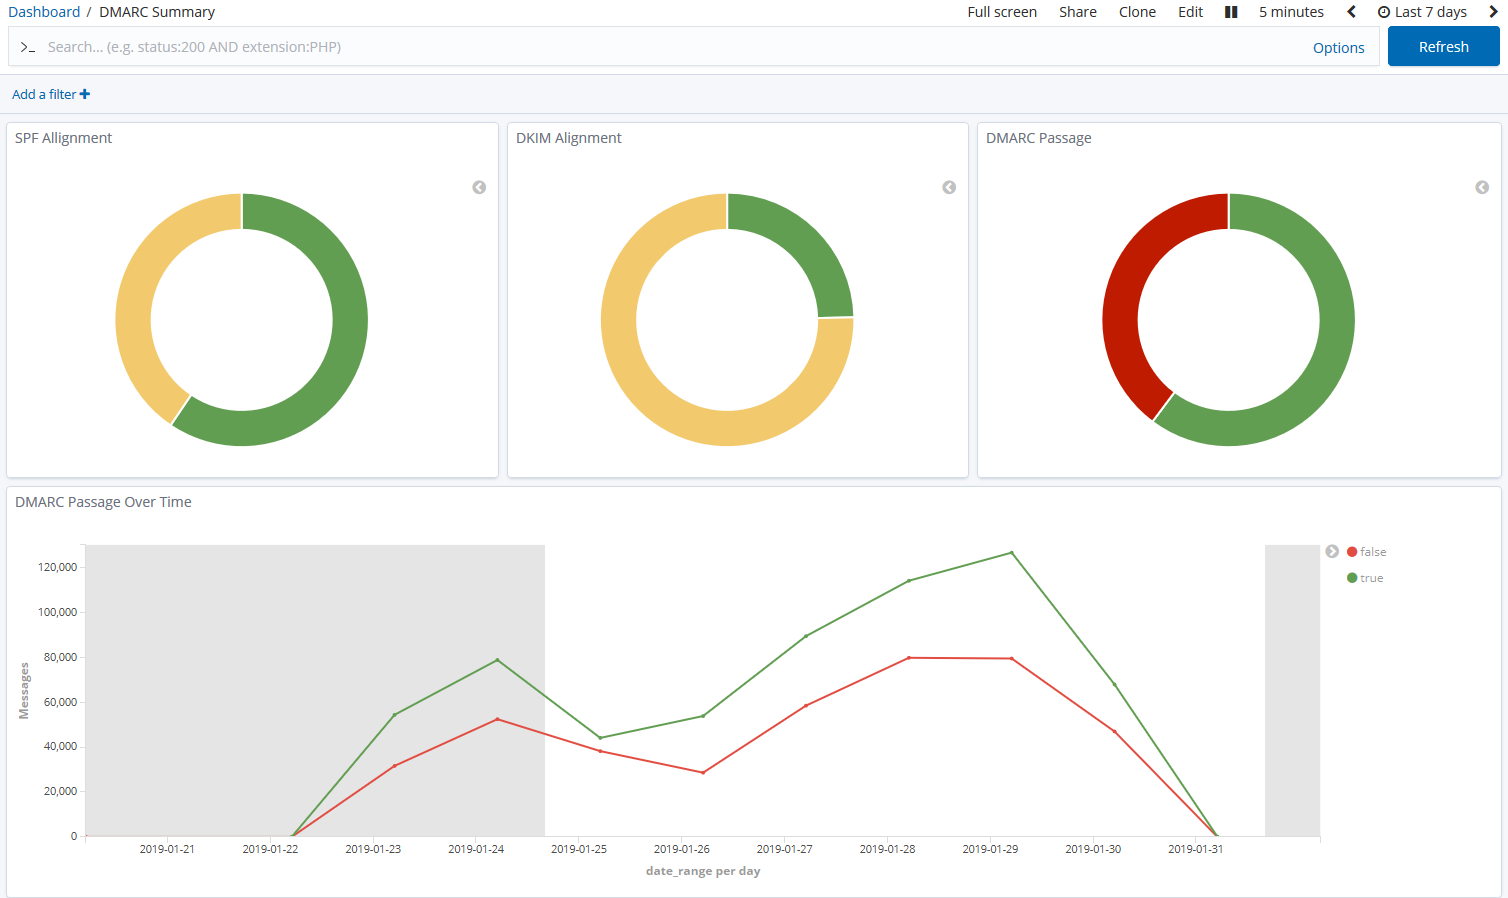 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
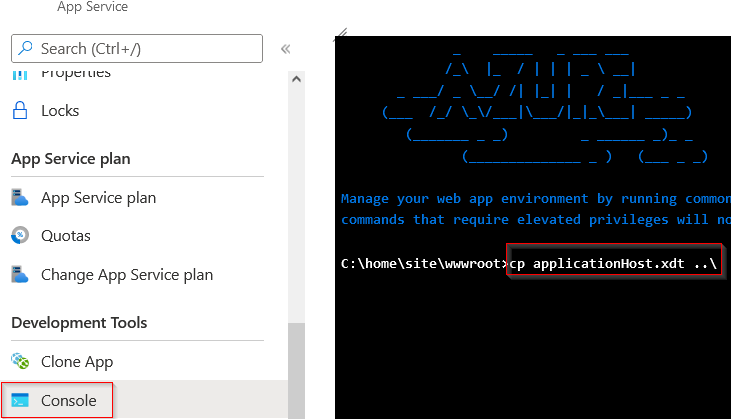 rvrsh3ll/azure-app-tools
Collection of tools to use with Azure Applications
 oriyomi12/otp-bot
Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…
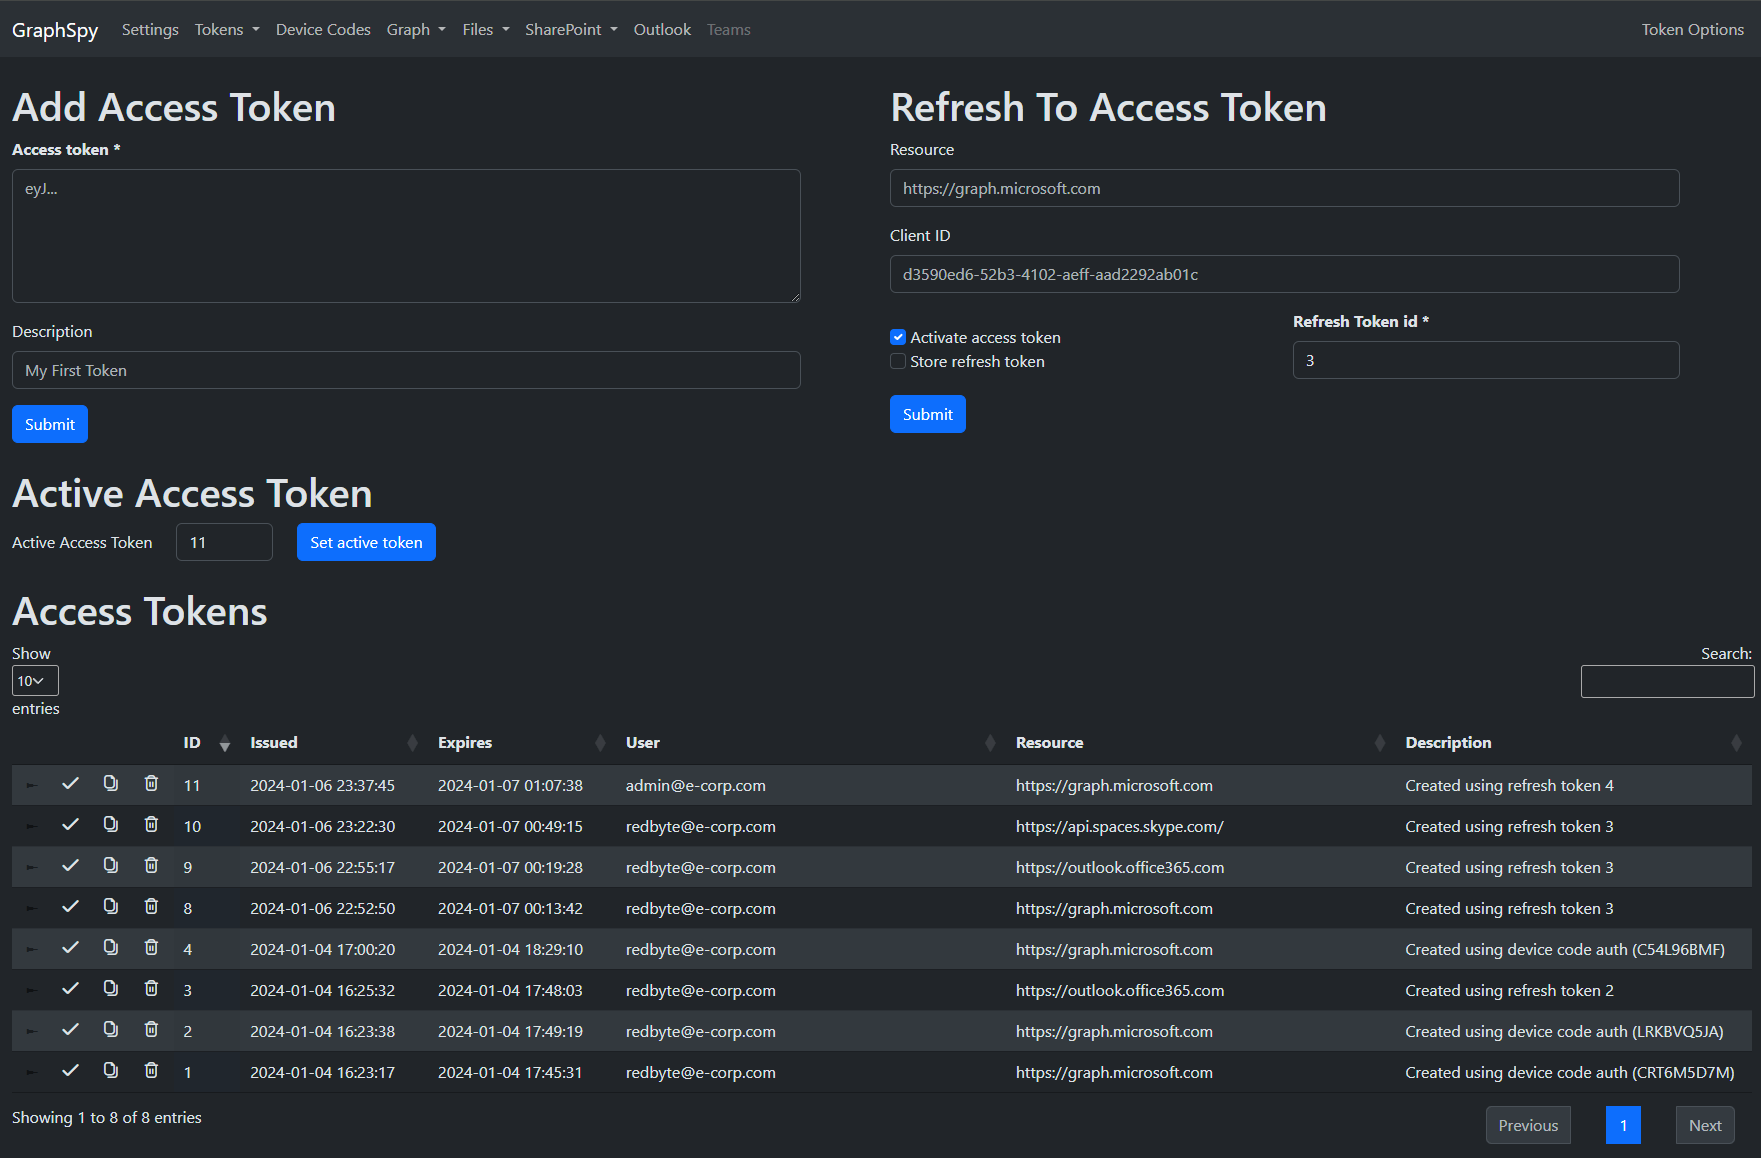 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 itres-labs/usbcoercer
USBCoercer turns an ESP32 development board with native USB-OTG into an Ethernet-over-USB gadget capable of coercing proxy configuration via WPAD.
 alessandrobertoldi/research
Published security research repository featuring academic papers on domain hijacking, 2FA bypass, and large-scale spoofing techniques, authored by…
 emerinohdz/facebrute
Facebook brute forcer script
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
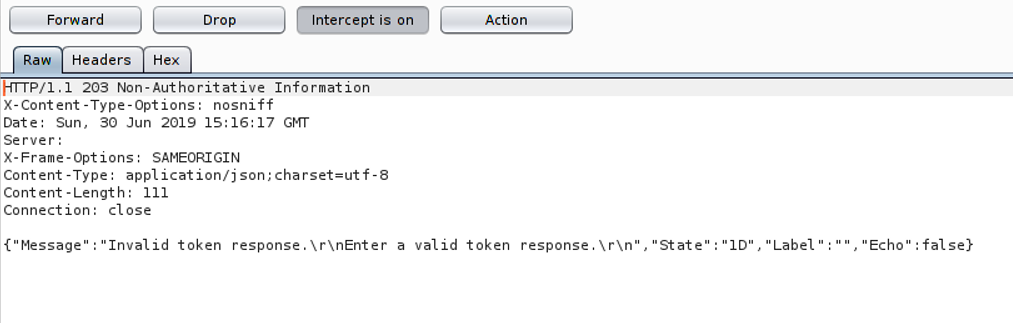 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.