
CVE-2026-48611-phpBB
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
authenticationexploitationpassword-attacks+4
lxdwnpiper/cve-2026-48611-phpbbPython proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
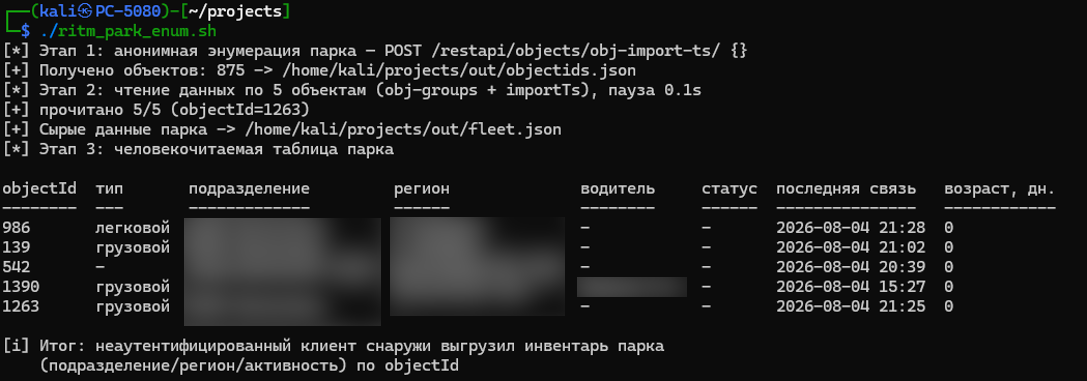 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 anoxhunterdump-ctrl/cve-2026-14378-devkit-pro-auth-bypass
Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).
 yym8538/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…
 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 o-sec/cve-2026-41452-poc
Proof-of-concept exploit for CVE-2026-41452, a critical authentication bypass in Krayin CRM <= 2.2.4 allowing unauthenticated admin account takeover…
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 diegoarias008/cve-2026-20079-checker
Read-only Python checker that validates CVE-2026-20079 Cisco FMC authentication-bypass behavior by comparing unauthenticated and csm_processes…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 squeeze440/inference-gateway-poc
PoC — cross-origin requests reuse the configured provider API key in inference-gateway (GHSA-5293-fcm6-fh8v, CVE-2026-87009, CVSS 5.4).
 squeeze440/tugtainer-poc
PoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
 4rt-net/mikrotrick_poc
Testing tool for the Mikrotrick exploit (CVE-2026-67276)
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…