

evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
406
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
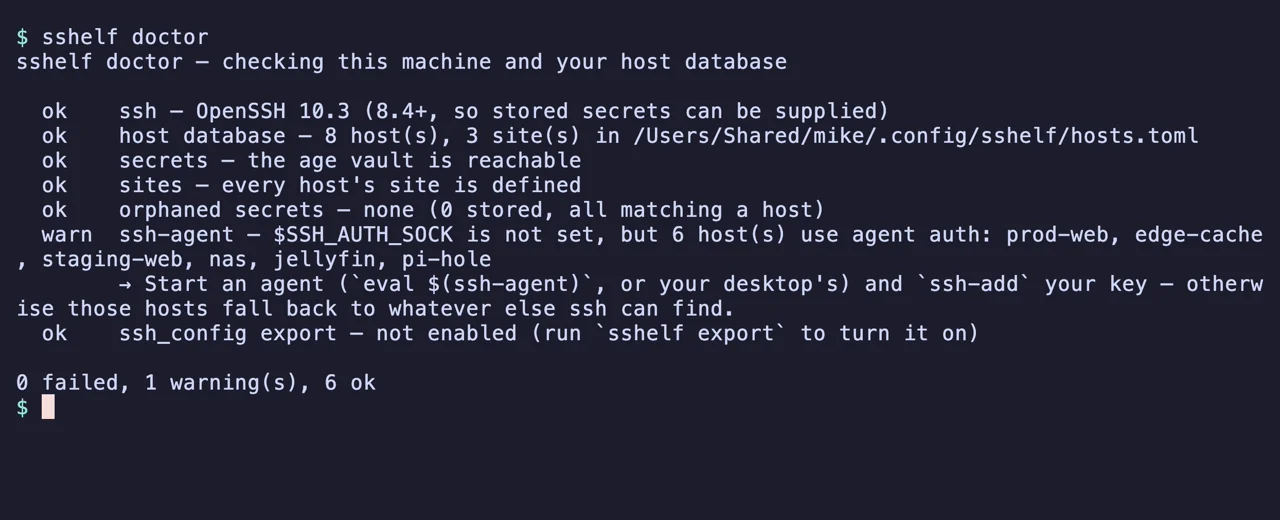 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 squeeze440/cve-2026-73519-wolfstack-poc
PoC for CVE-2026-73519 - WolfStack hardcoded cluster secret leads to unauthenticated RCE (CVSS 9.8)
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 cashapp/pivit
Manage x509 certificates on PIV-enabled YubiKeys, generate keys and certificate requests, and sign or verify git commits and files.
 rvrsh3ll/azure-app-tools
Collection of tools to use with Azure Applications
 netsecfish/dlink
Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…
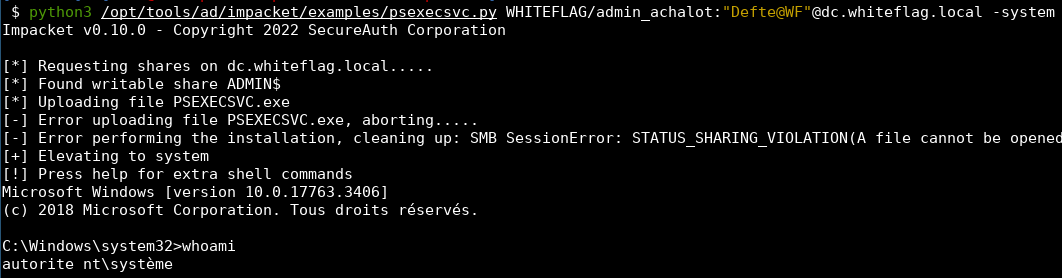 sensepost/susinternals
psexecsvc - a python implementation of PSExec's native service implementation
 mayyhem/maestro
Abusing Azure services over C2
 openssh/openssh-portable
Portable OpenSSH
 samyk/poisontap
Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…