
KrbRelay
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
authenticationexploitationlateral-movement+2
955
cube0x0/krbrelayKerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 yuriisanin/cve-2022-25262
PoC + vulnerability details for CVE-2022-25262 / JetBrains Hub single-click SAML response takeover
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 xmyronn/cve-2026-10288-auth-bypass
Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…
 h4zaz/cve-2026-8793
esponsible disclosure write-ups for CVE-2026-8793 - PaperCut NG 25.0.11
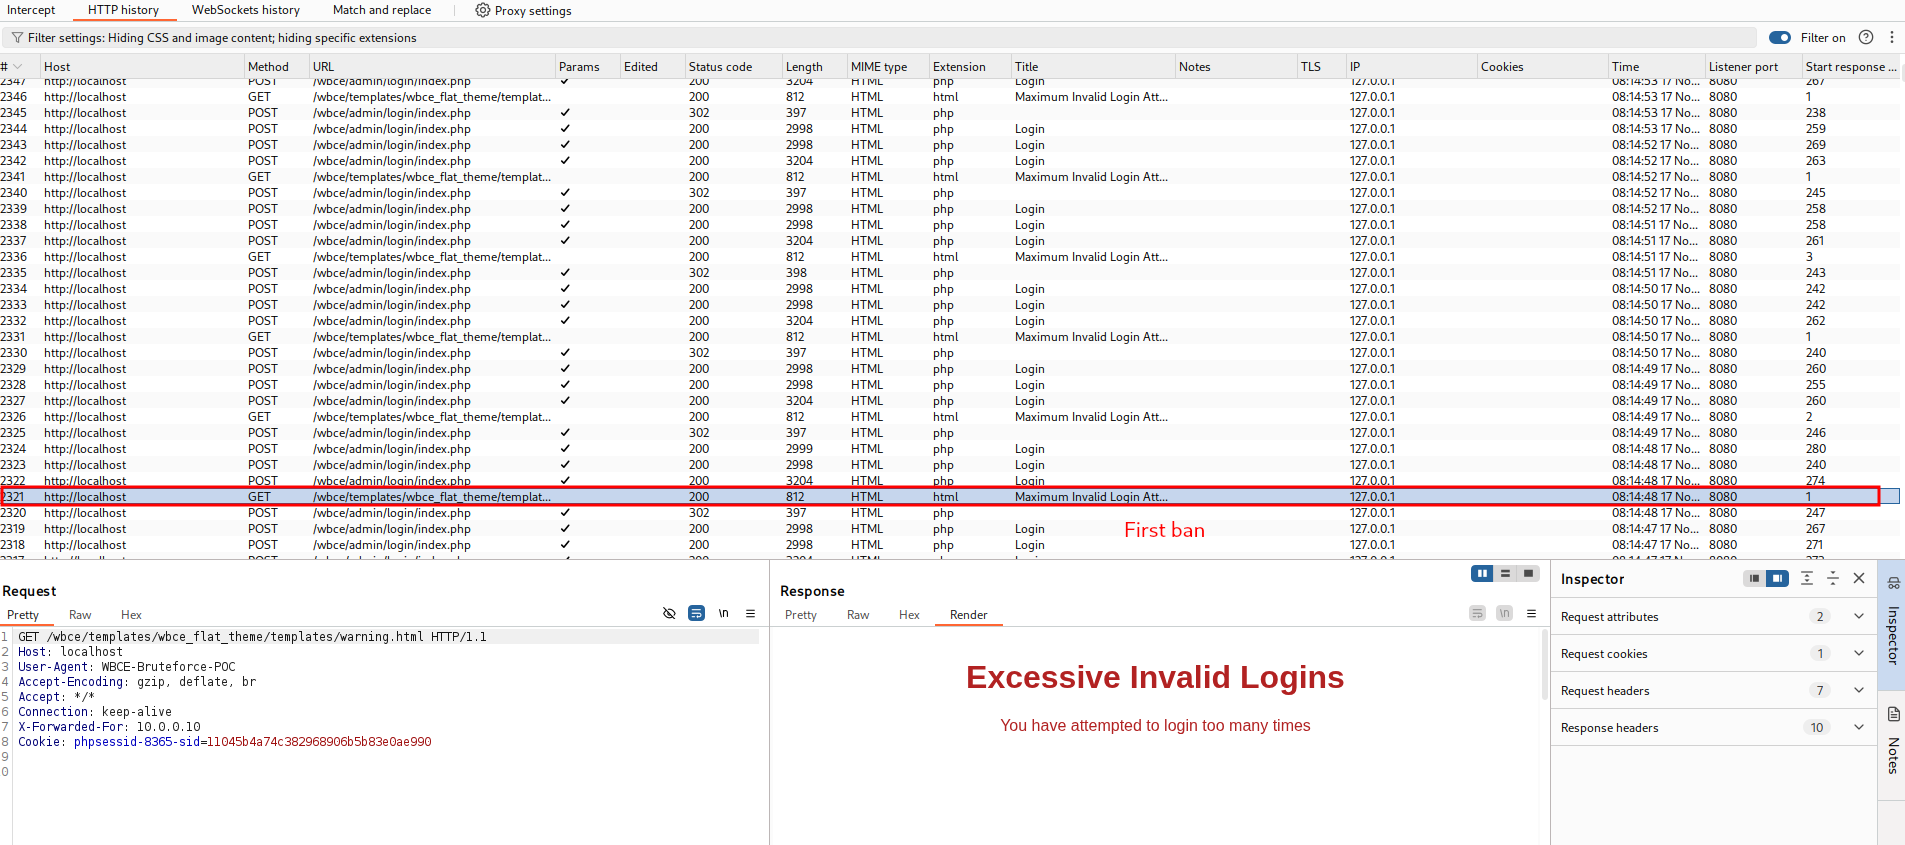 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
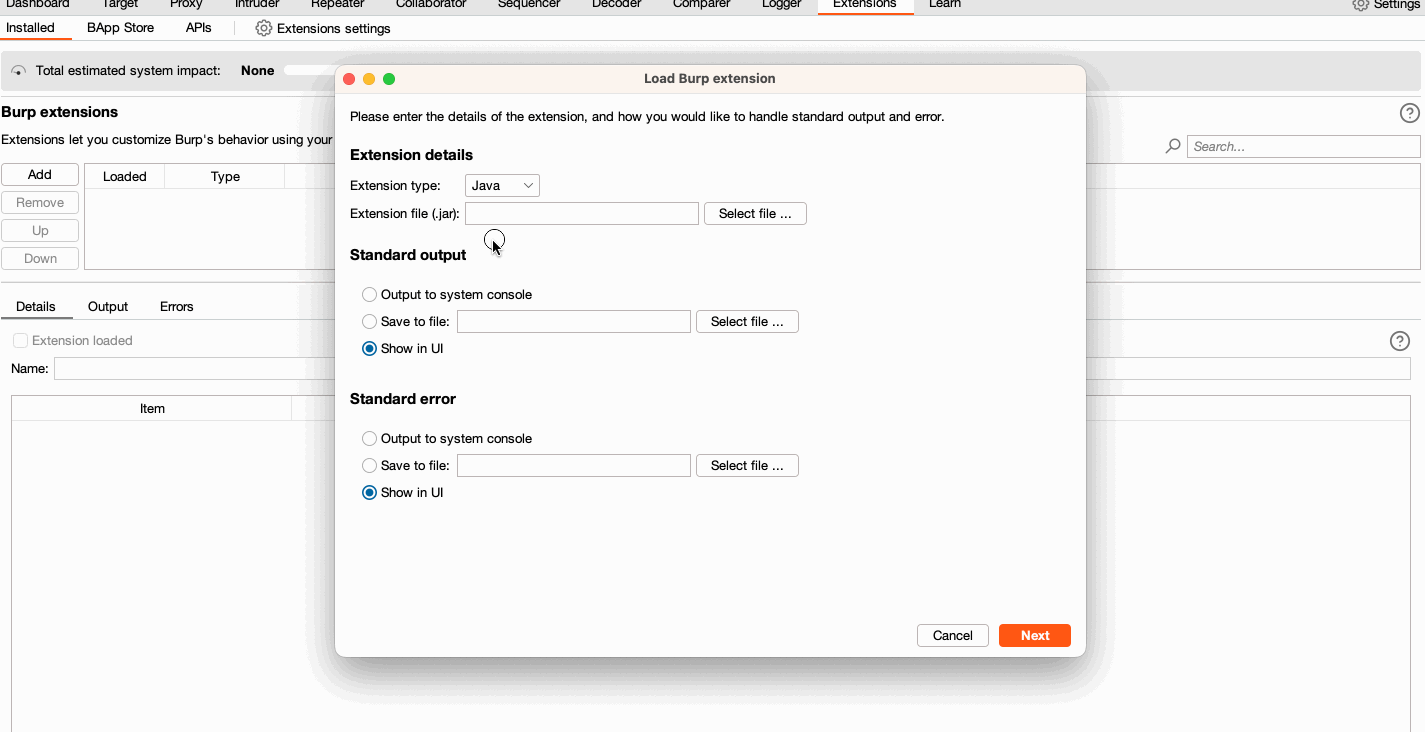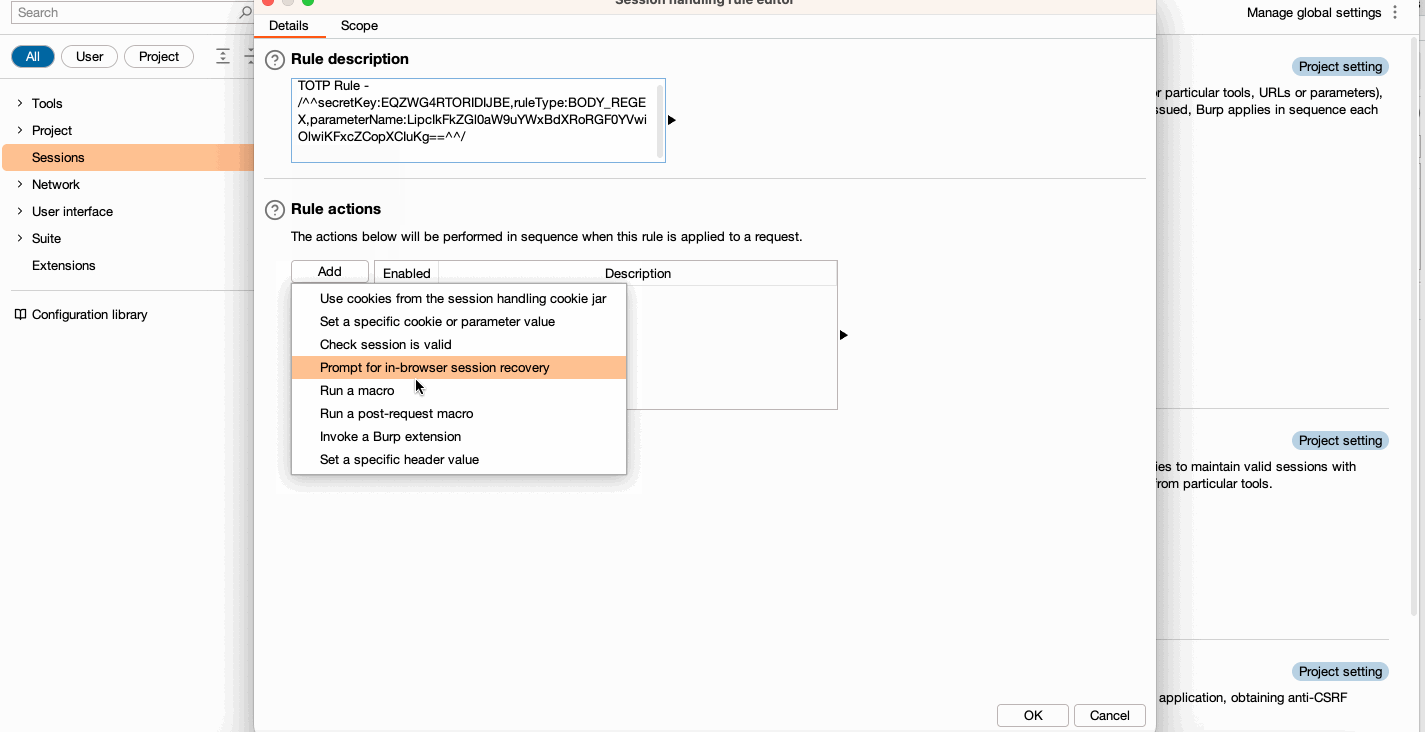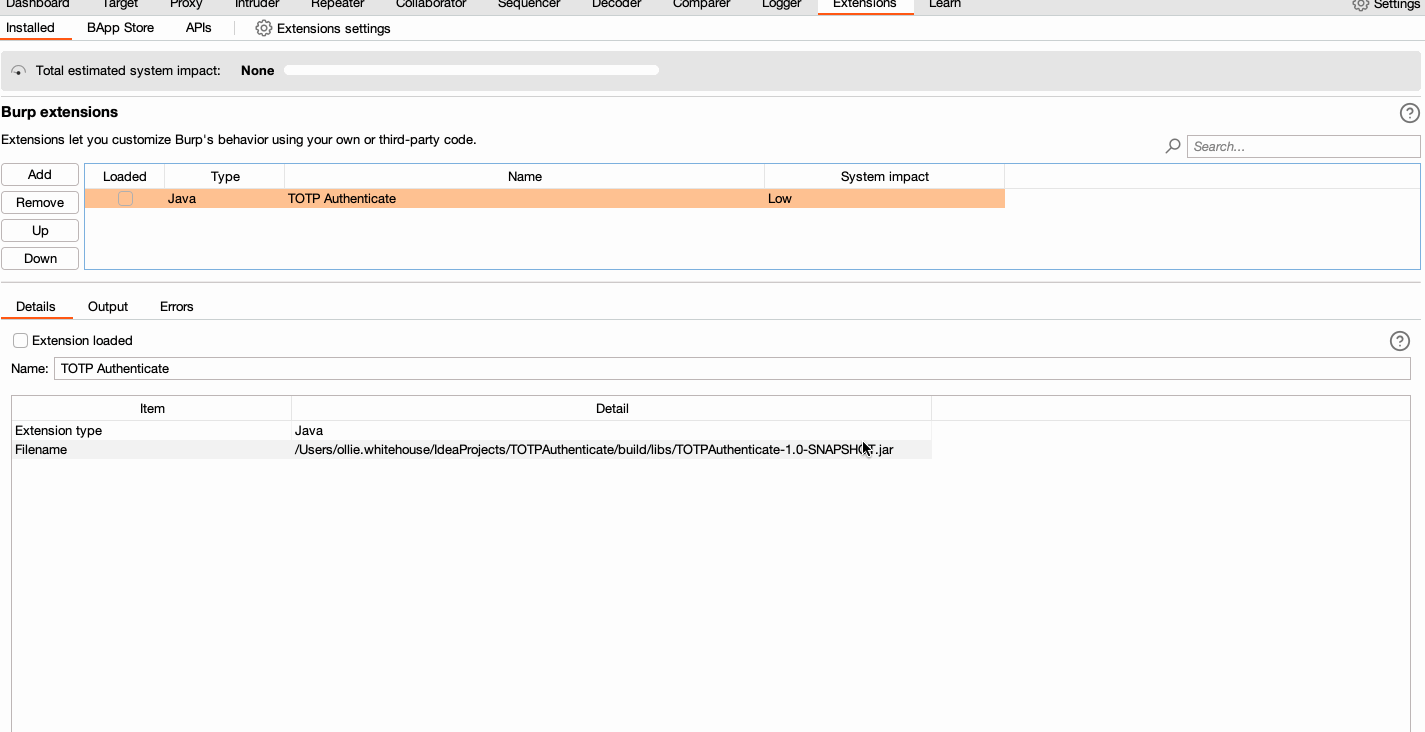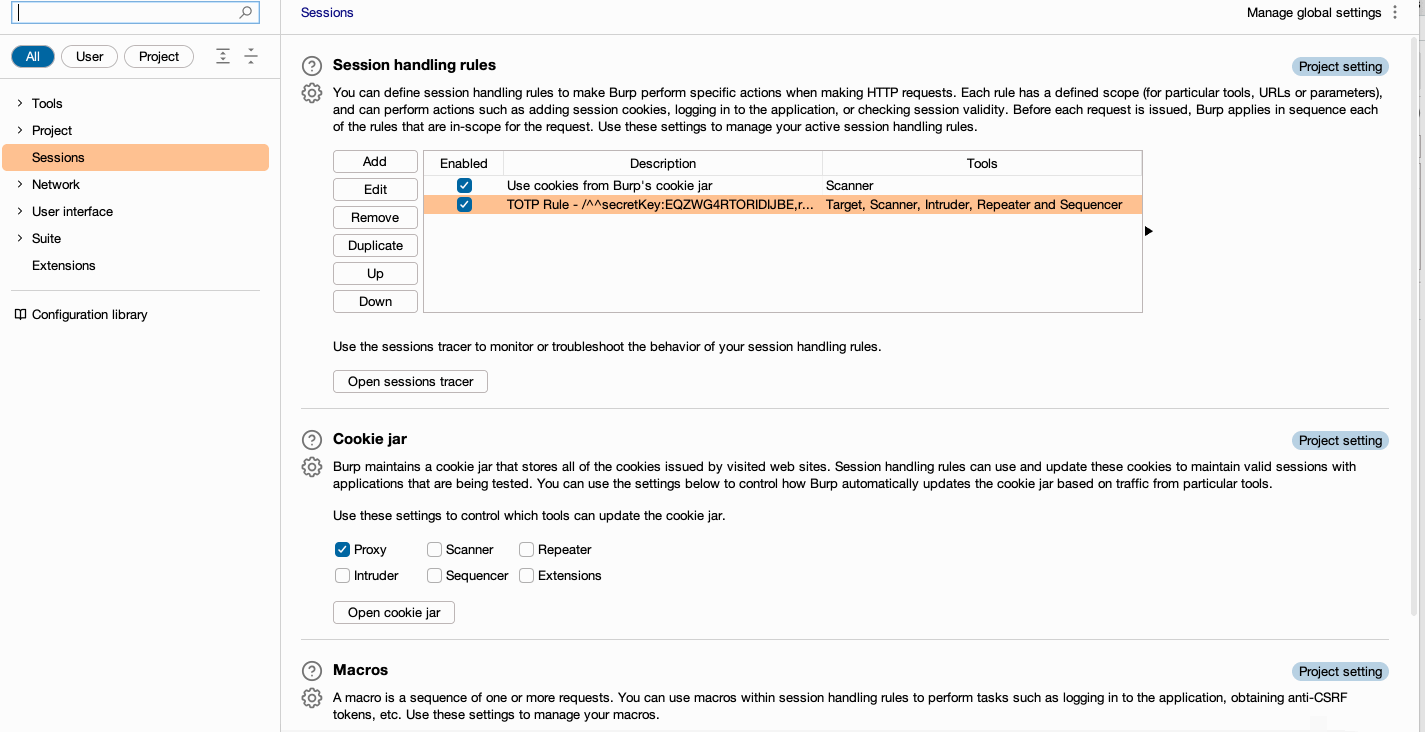 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 umair-aziz025/dahua-cve-research
Dahua IP camera CVE research toolkit (CVE-2021-33044/33045, CVE-2025-31700/31701)
 xmyronn/cve-2026-10243-auth
Proof of concept demonstrating unauthenticated access to critical admin functions in Smart Parking System 1.0, allowing account creation, data…
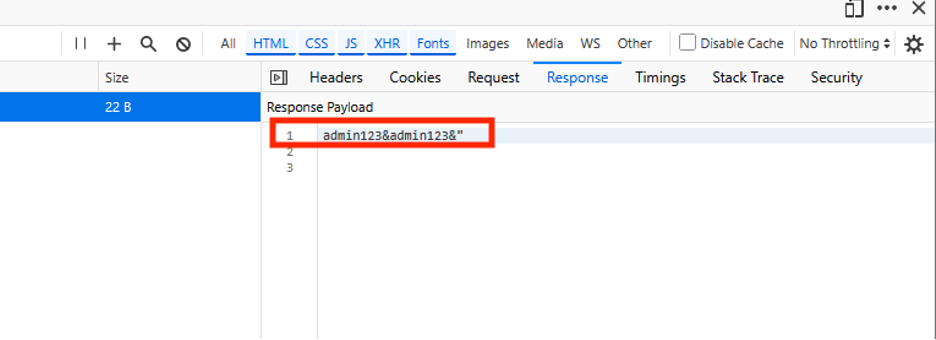 weedl/cve-2025-45620
Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 watchtowrlabs/watchtowr-vs-crushftp-authentication-bypass-cve-2025-54309
Proof-of-concept exploit for CVE-2025-54309, demonstrating an authentication bypass via race condition in CrushFTP WebInterface to enumerate users.
 7ragnarok7/cve-2021-3754
Vulnerability details and exploit for CVE-2021-3754