
CheatSheetSeries
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
api-securityauthenticationcloud-security+6
33.3k
owasp/cheatsheetseriesThe OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
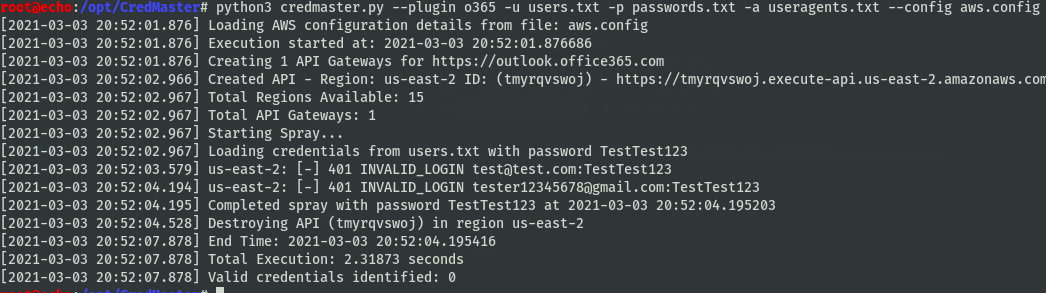 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 owasp/passfault
OWASP Passfault evaluates passwords and enforces password policy in a completely different way.
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 compasssecurity/samlraider
SAML2 Burp Extension
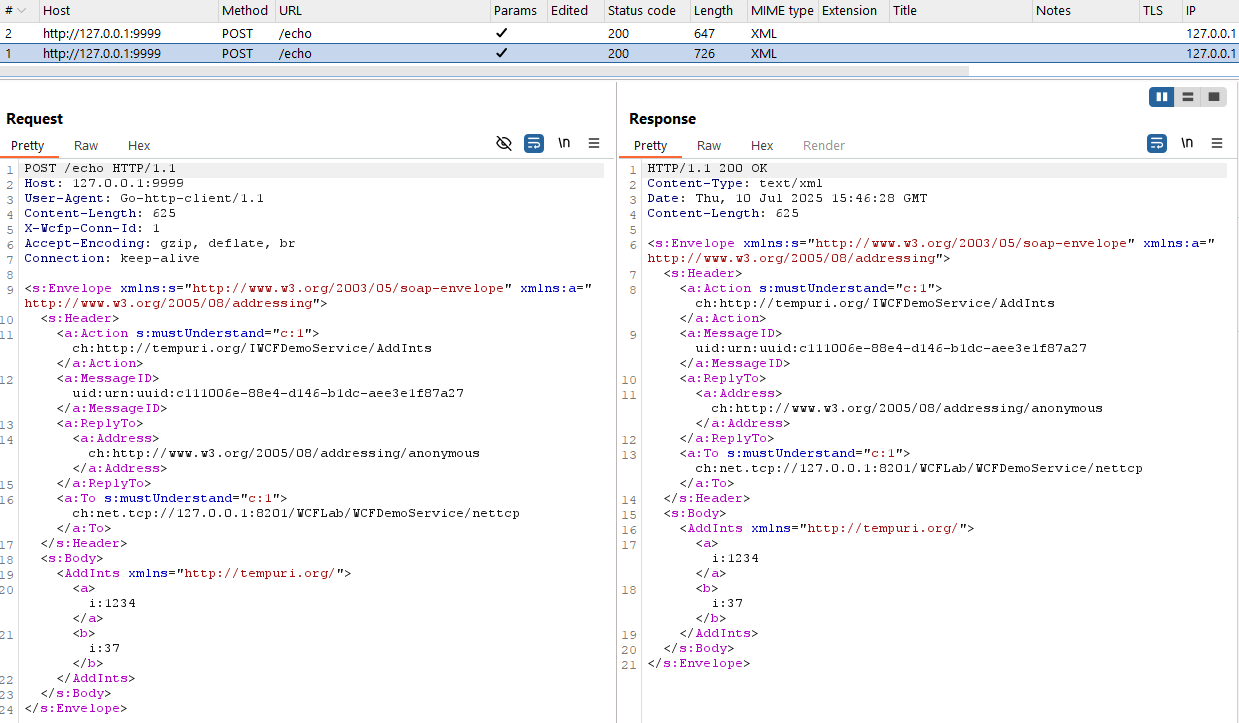 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 logisek/huntcyberark
CyberArk Security Audit
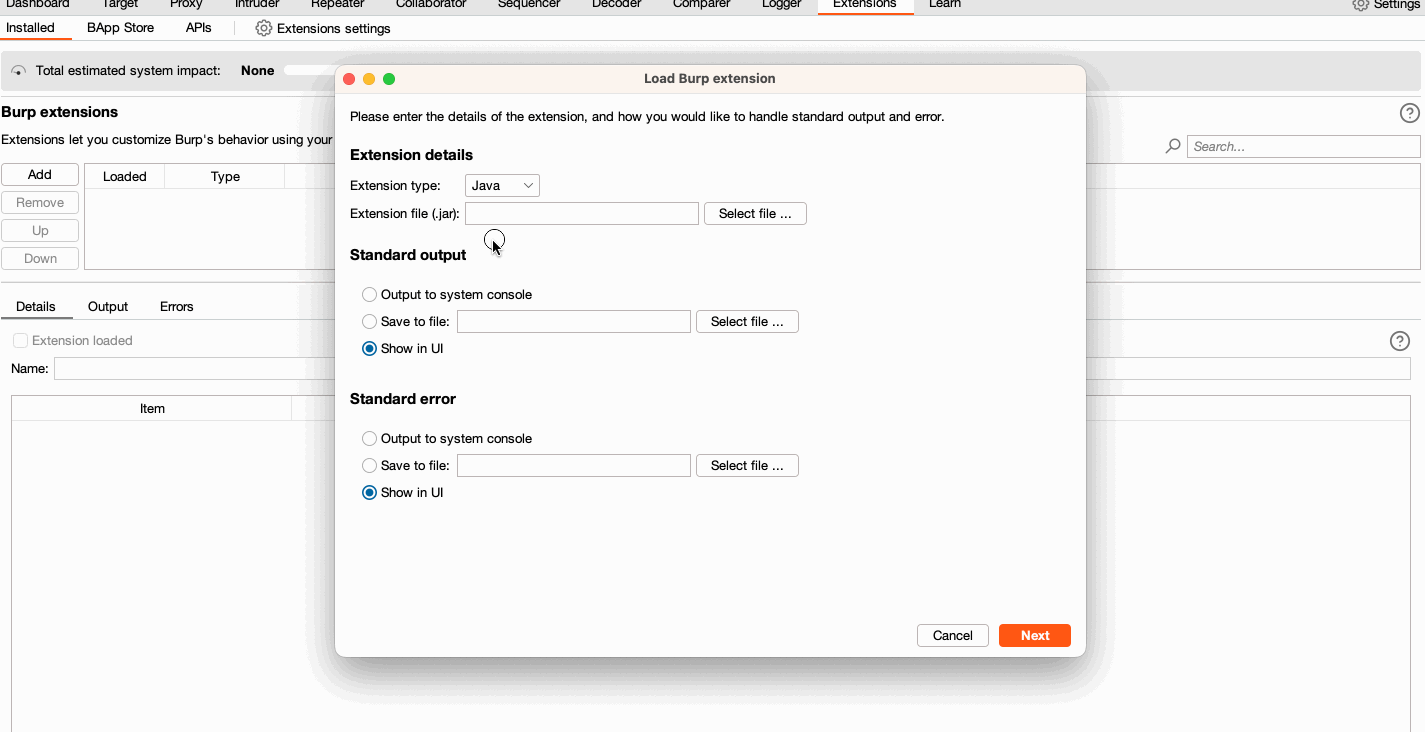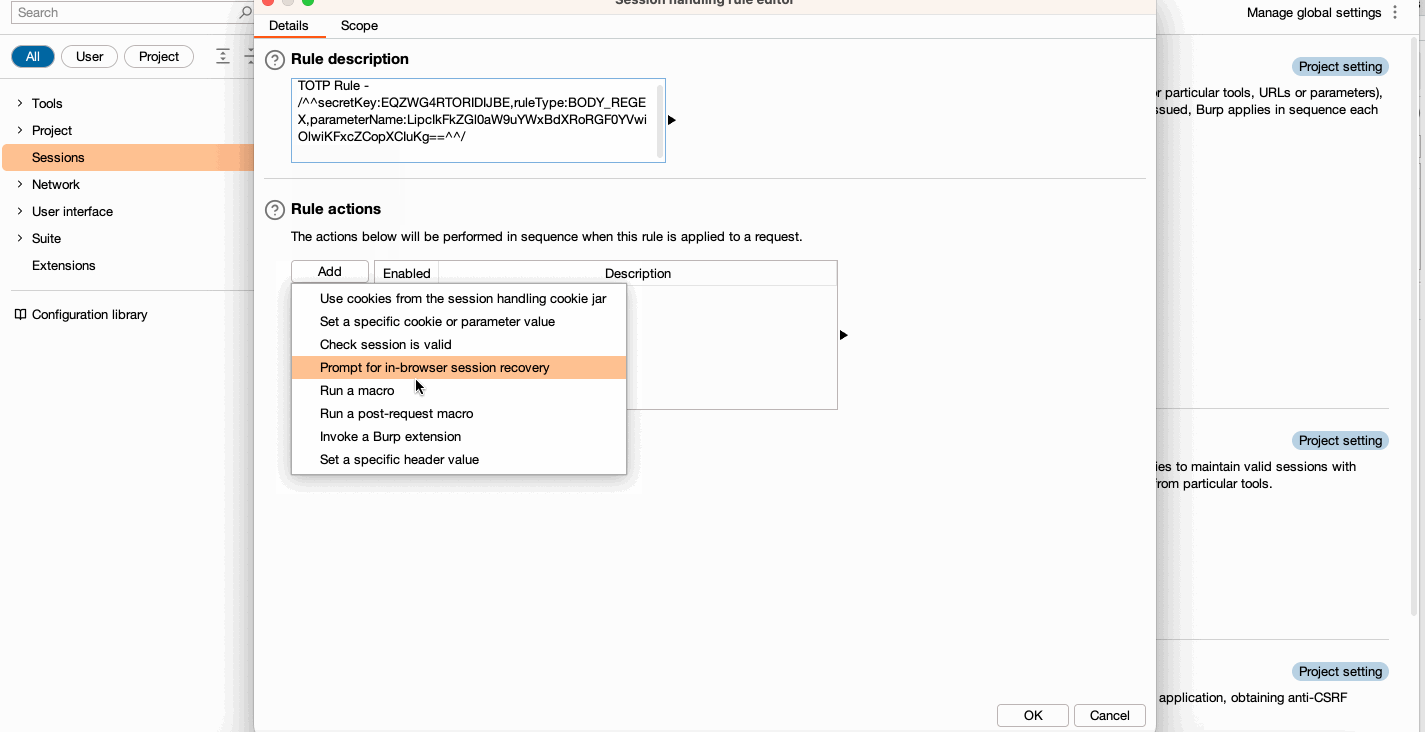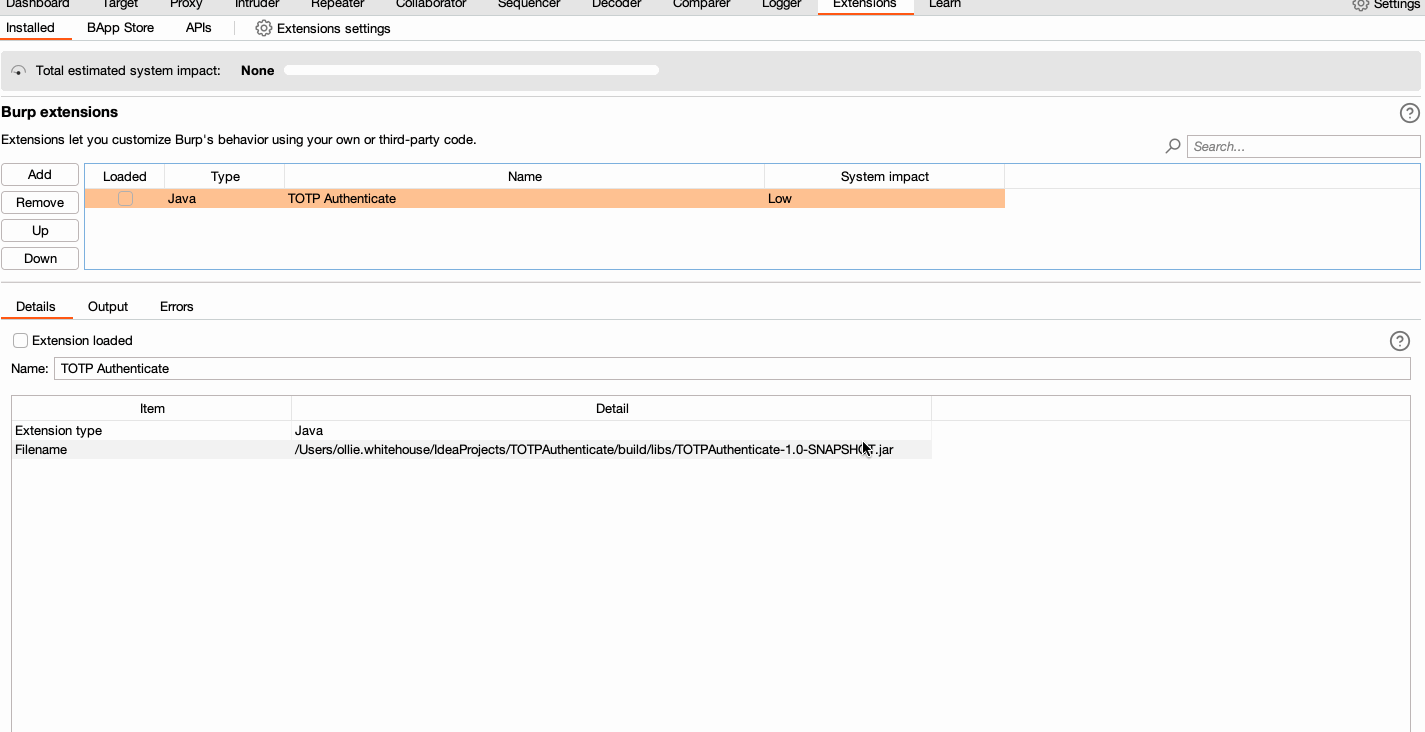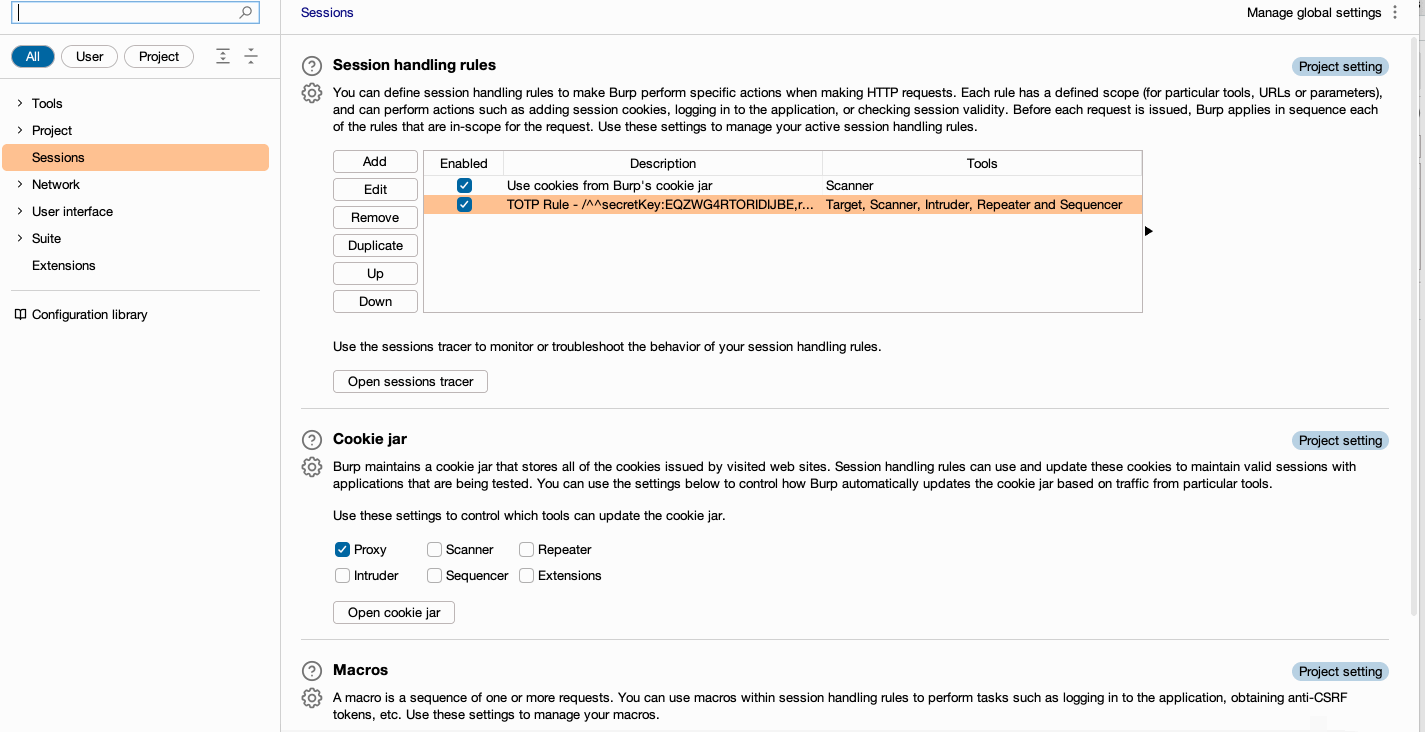 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.