
evil-winrm
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
authenticationexploitationpayload-generation+3
5.5k
hackplayers/evil-winrmThe ultimate WinRM shell for hacking/pentesting
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 doyensec/cve-2022-39299_poc_generator
A Simple CVE-2022-39299 PoC exploit generator to bypass authentication in SAML SSO Integrations using vulnerable versions of passport-saml
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 1beelze/cve-2026-5118
Automated exploit and mass scanner for CVE-2026-5118, an unauthenticated privilege escalation in WordPress Divi Form Builder <=5.1.2, enabling admin…
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 joshuavanderpoll/cve-2025-69985
Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…
 saladin0x1/cve-2025-53770
Proof-of-concept exploit toolkit for SharePoint ToolPane RCE (CVE-2025-53770) with scanner, payload analysis, and multiple exploitation methods for…
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…
 cyberauth/cve-2026-20079
Implements the CVE-2026-20079 authentication-bypass-to-root-RCE chain against Cisco Secure FMC using fingerprint, check, proof, and interactive…
 rvrsh3ll/azure-app-tools
Collection of tools to use with Azure Applications
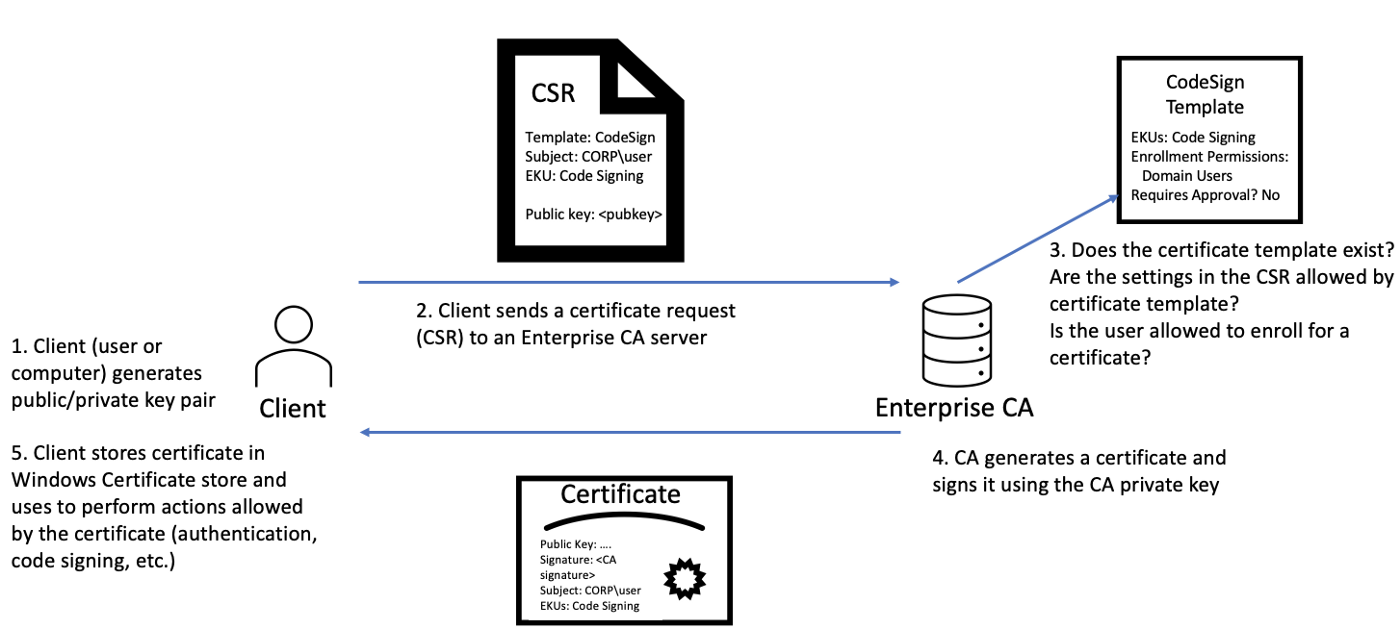 ghostpack/forgecert
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 kimdir01/cve-2026-9090-poc
PoC for CVE-2026-9090 — Casdoor SAML signature bypass (CWE-347). Reproduction-only; coordinated via CERT/CC VU#780781.
 rishuranjanofficial/jwtweak
Detects the algorithm of input JWT Token and provide options to generate the new JWT token based on the user selected algorithm.