
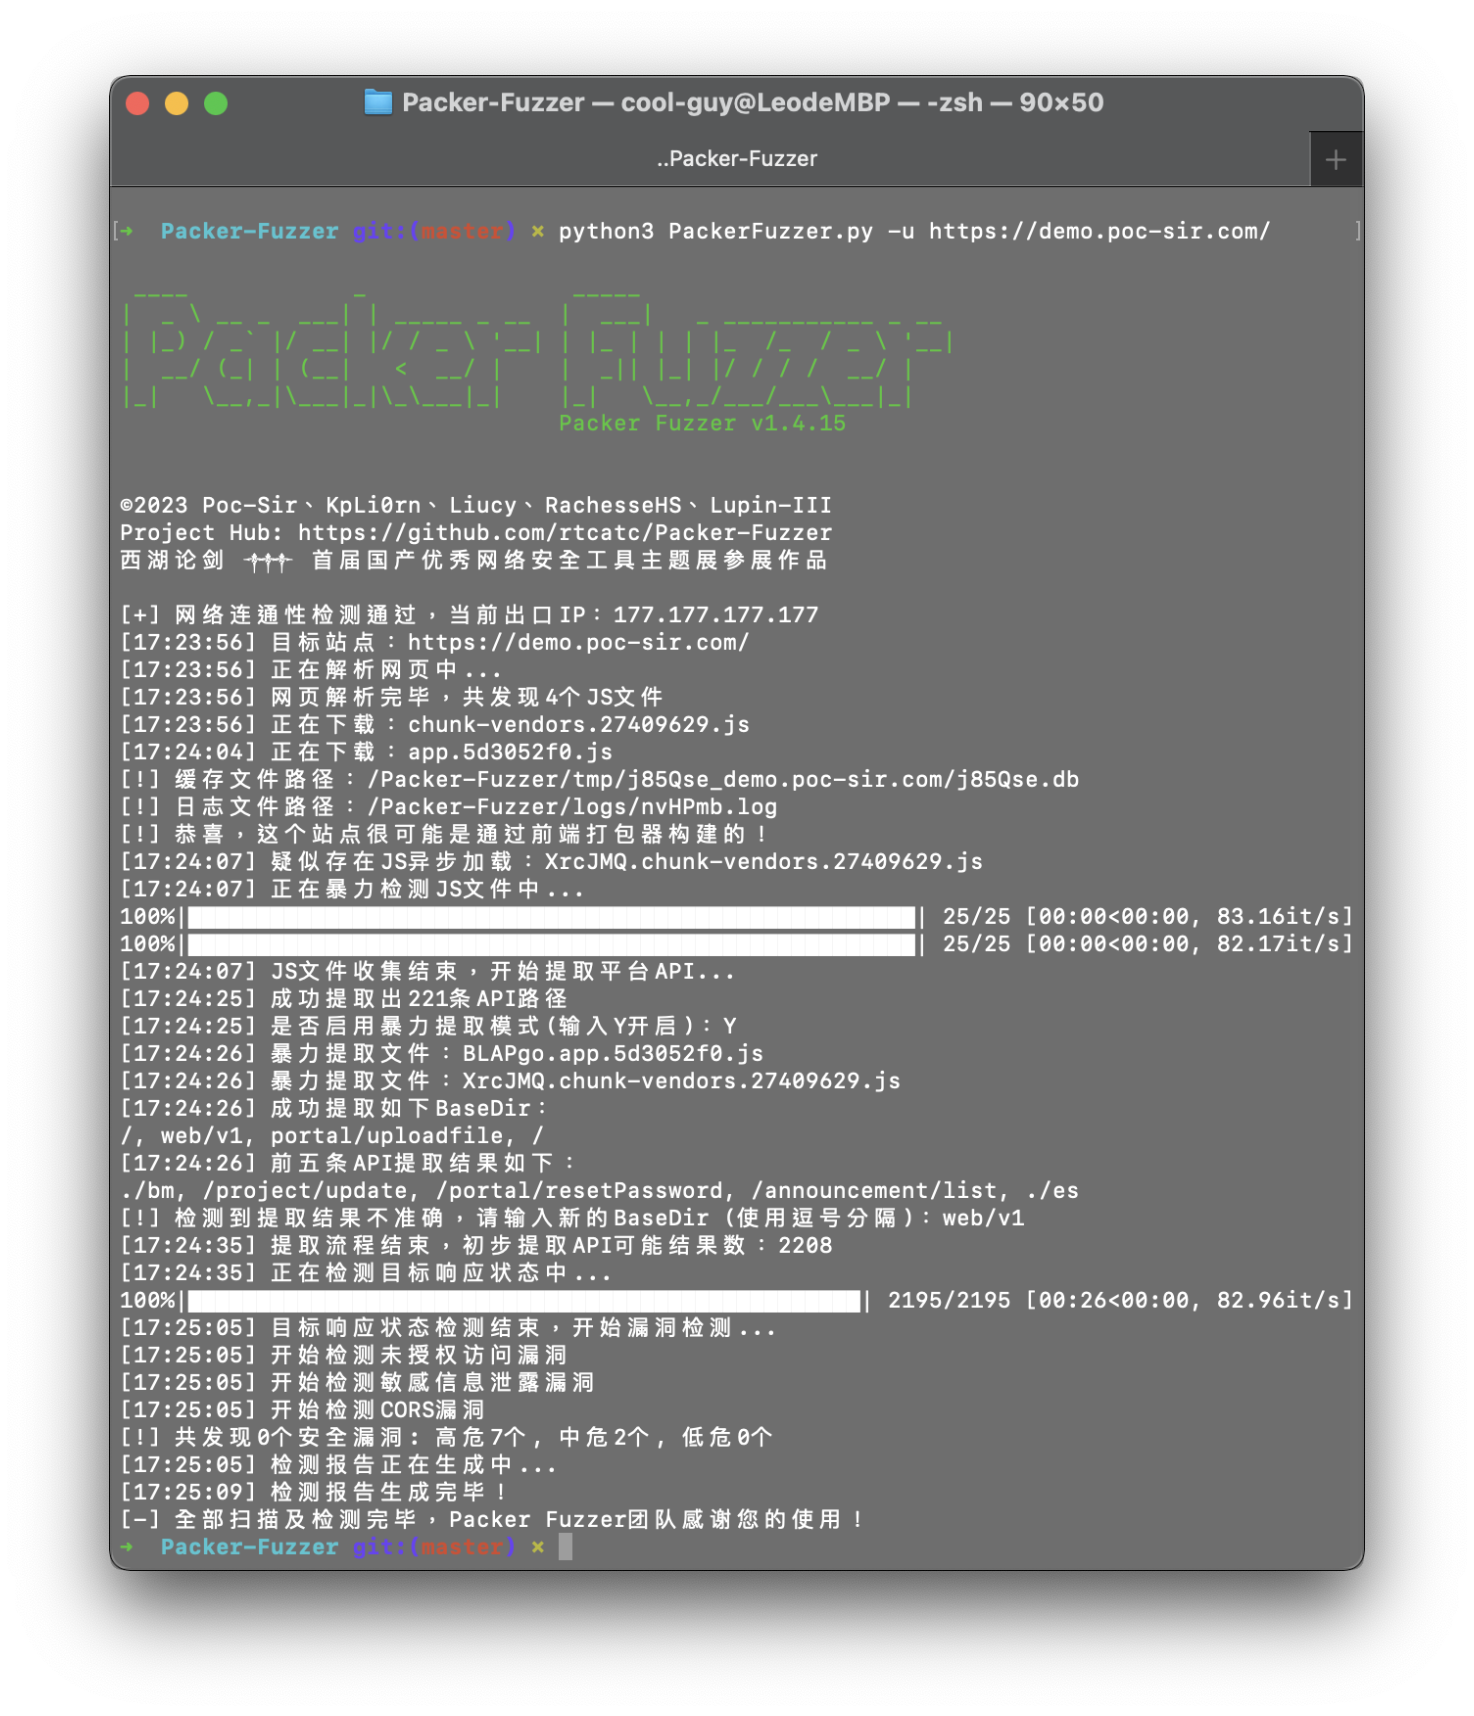
Packer-Fuzzer
 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
api-security-testingfuzzingvulnerability-scanners+1
3.3k
rtcatc/packer-fuzzerPacker Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
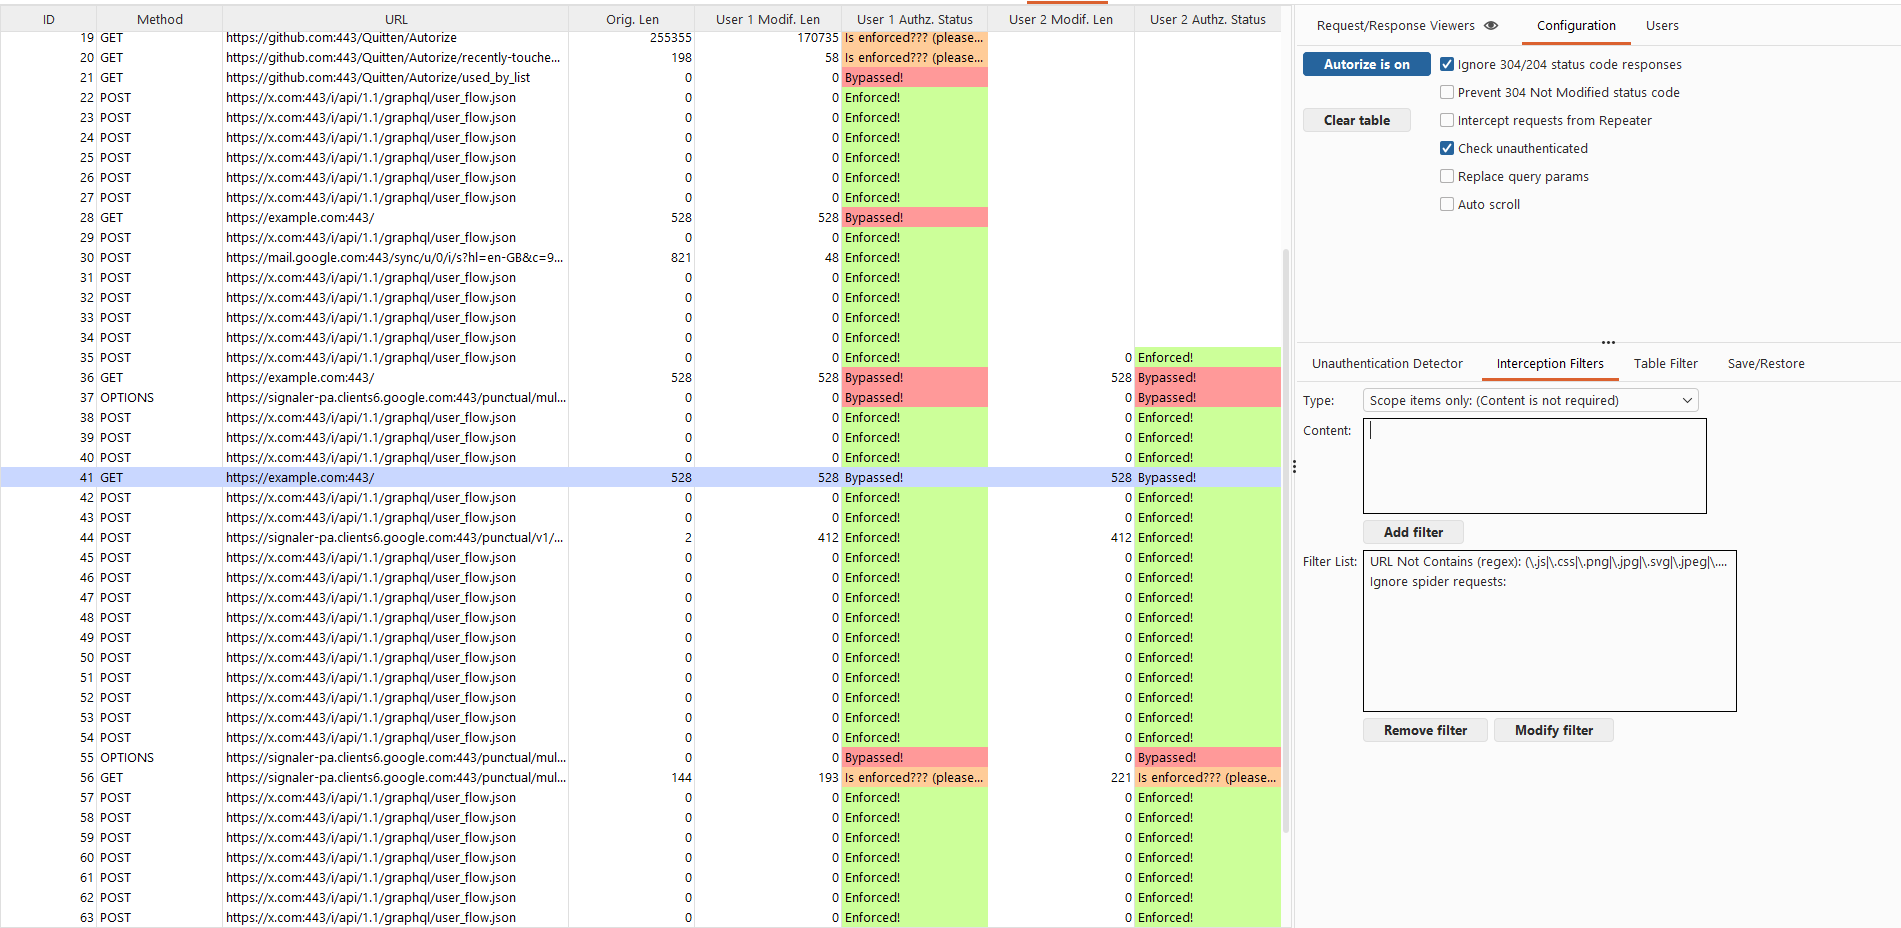 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
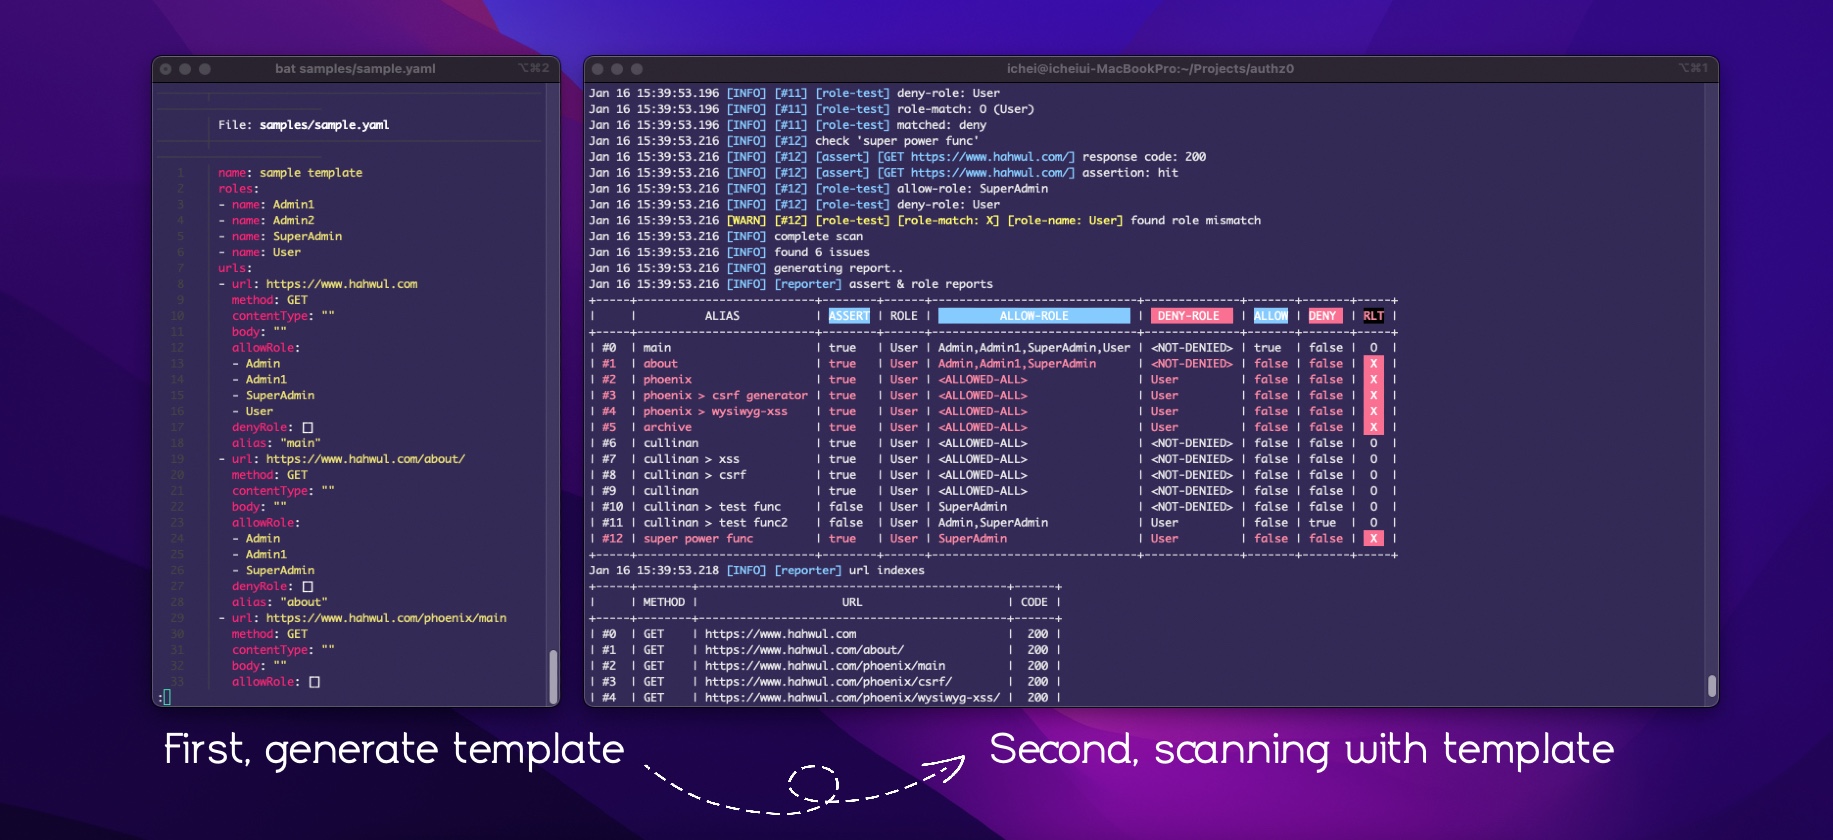 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 sn1r/mass-assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…
 ebrasha/abdal-cve-2026-63030
Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…
 0xmaximus/apache-commons-text-cve-2022-42889
Burp Bounty profile for detecting Apache Text4Shell (CVE-2022-42889), an RCE in Commons Text 1.5-1.9, by scanning HTTP requests.
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 kavishkagihan/cve-2022-24112-poc
Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
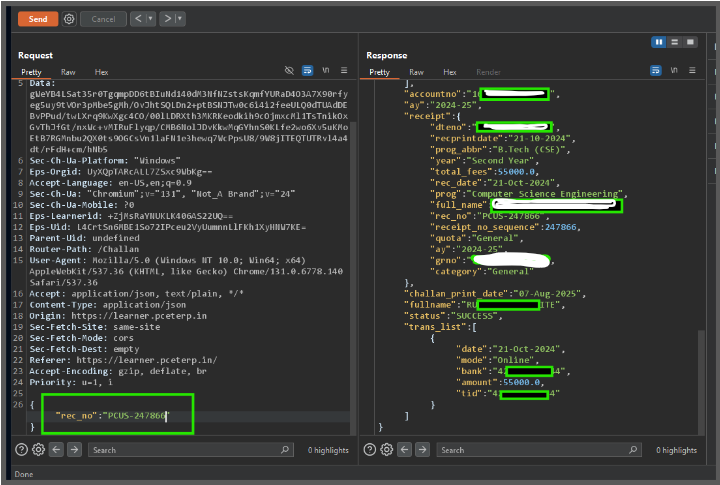 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.