CVE2022-1388_TestAPI
 bandit92/cve2022-1388_testapi
A Test API for testing the POC against CVE-2022-1388
api-security-testingexploitationpenetration-testing+2
4
bandit92/cve2022-1388_testapiA Test API for testing the POC against CVE-2022-1388
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
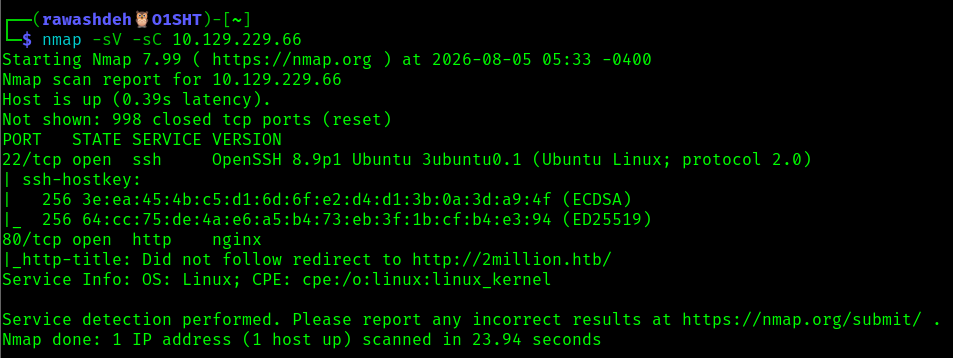 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 owasp/dvsa
a Damn Vulnerable Serverless Application
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
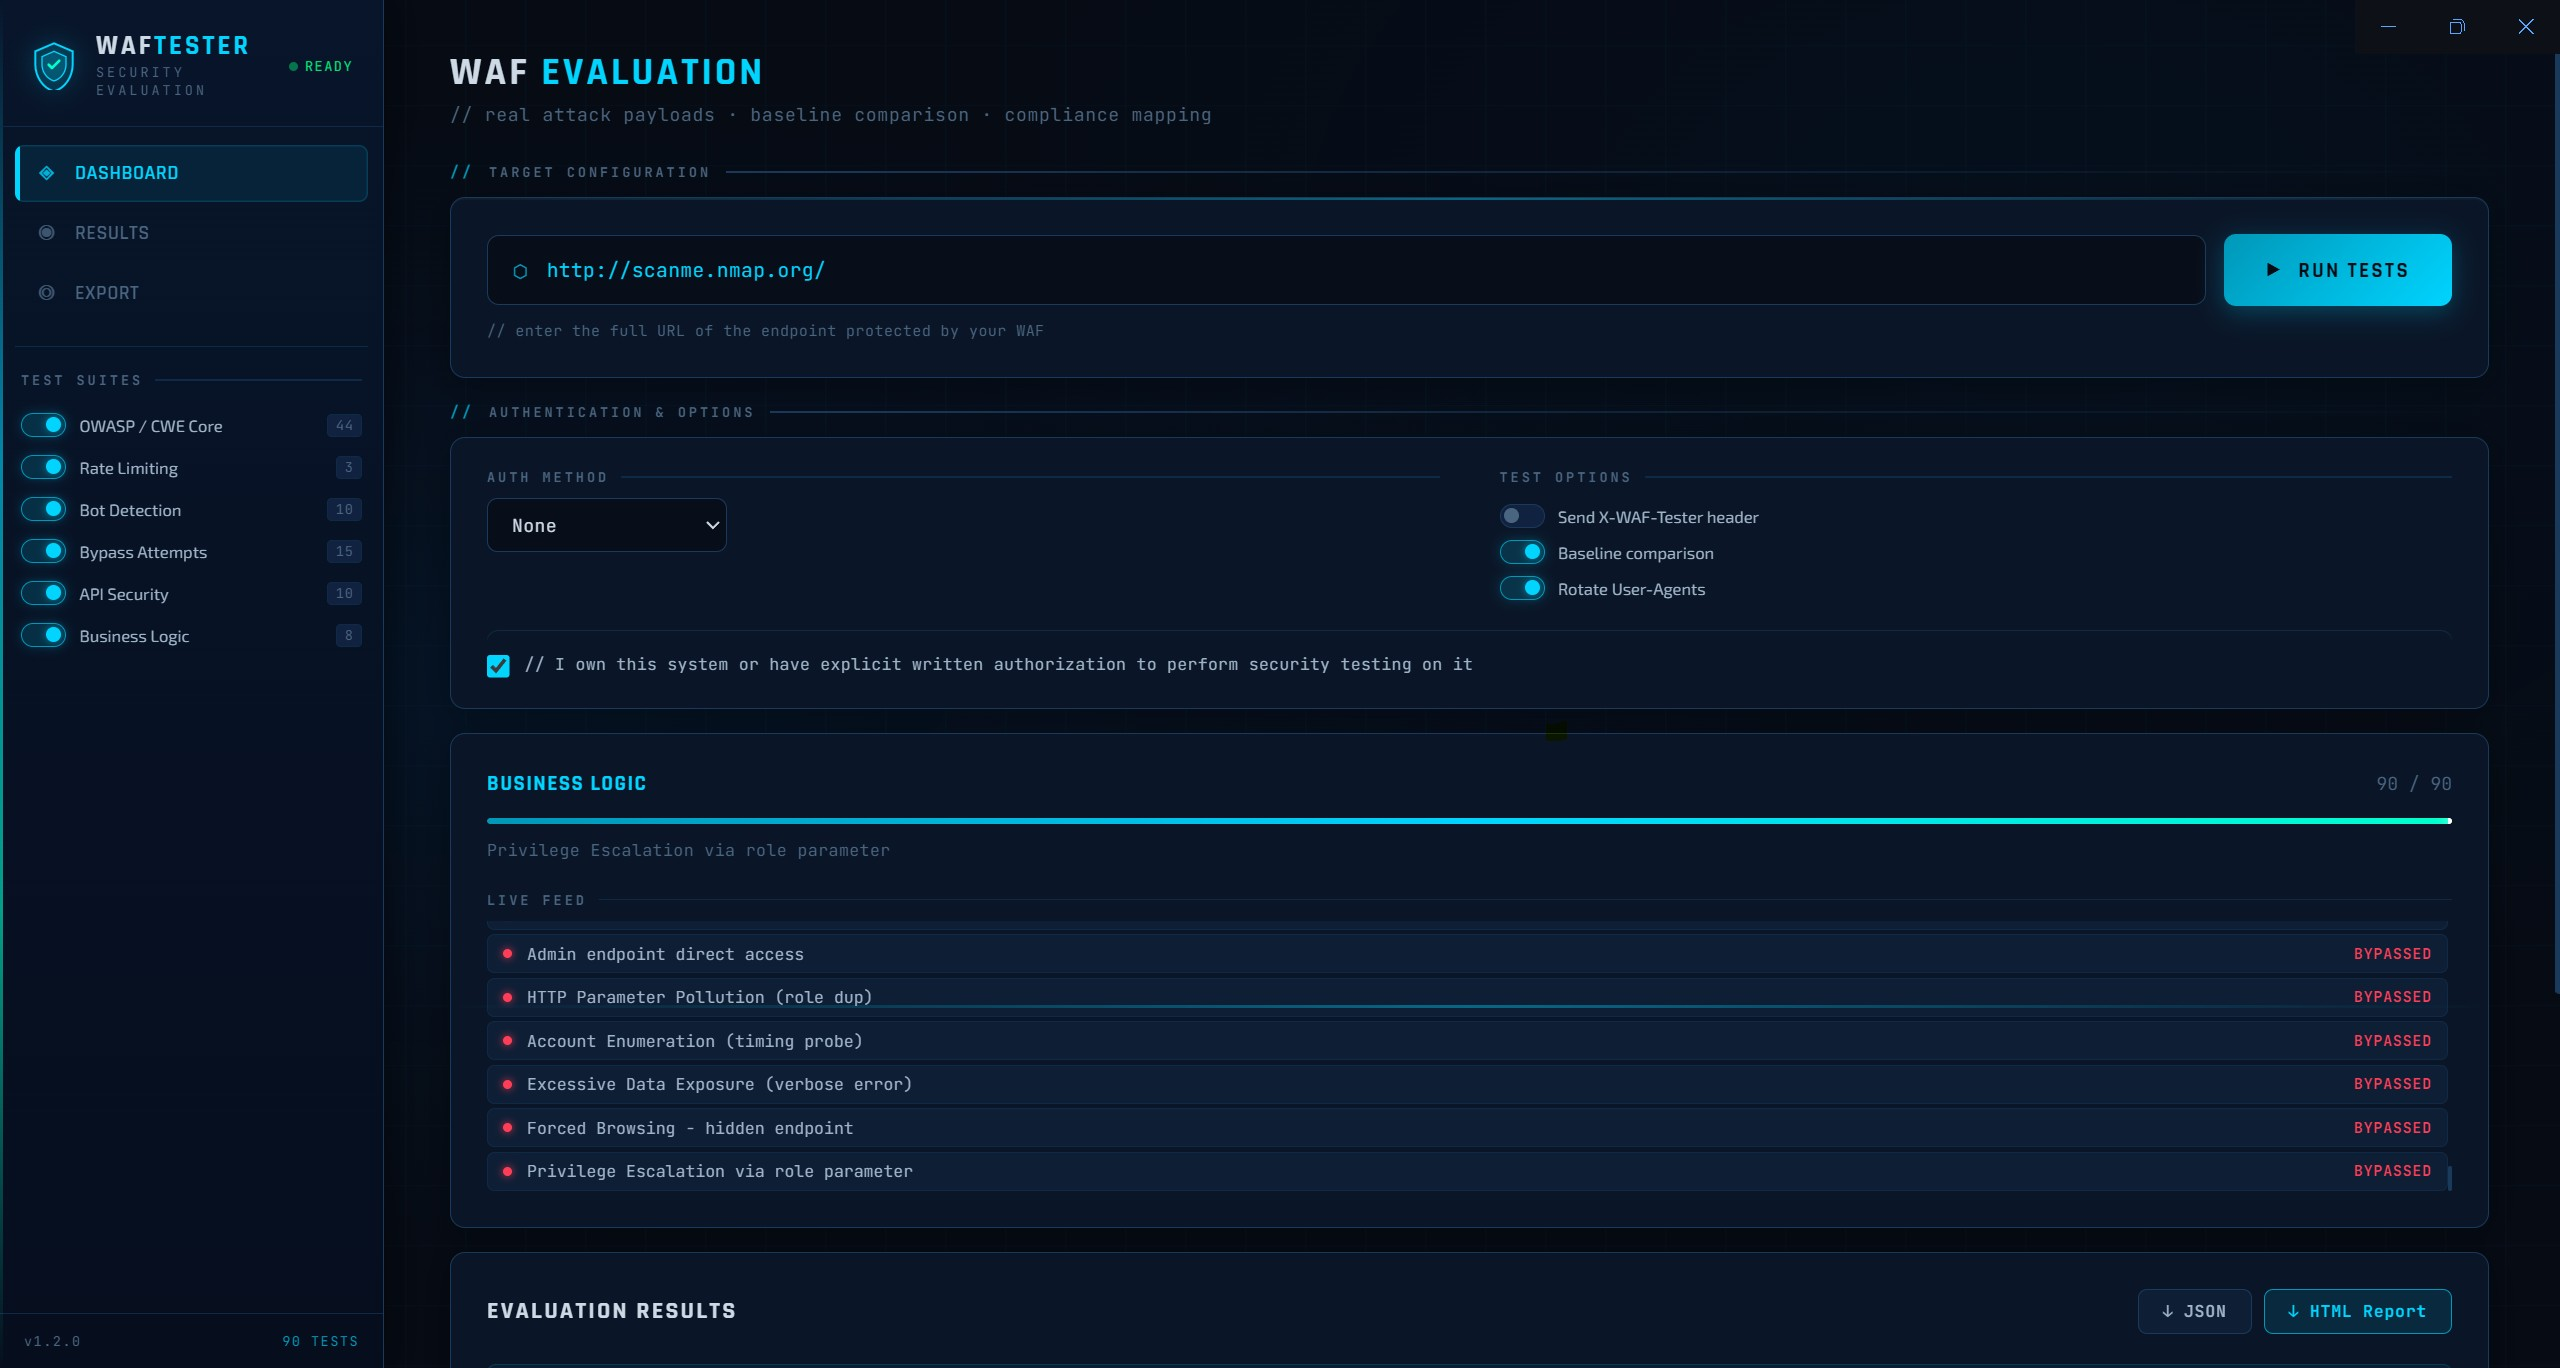 kpomin57/waf-tester
A program for testing WAF functionality
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
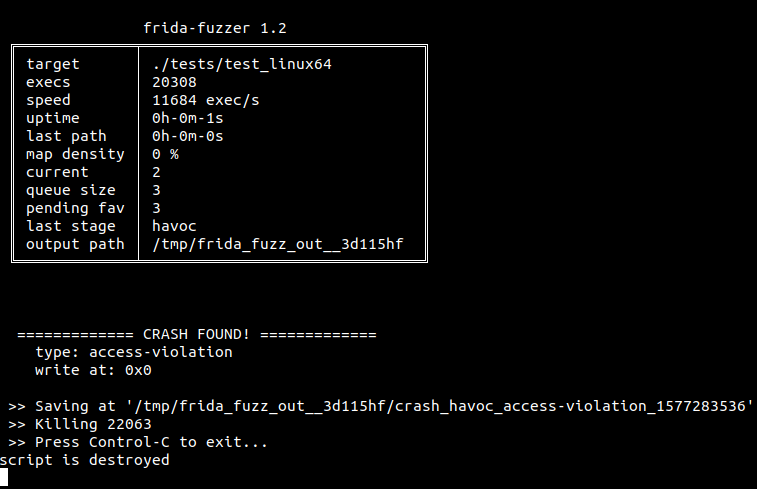 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 licitrasimone/cve-2026-75157-poc
Standalone authorized universal HTTP PoC for CVE-2026-75157
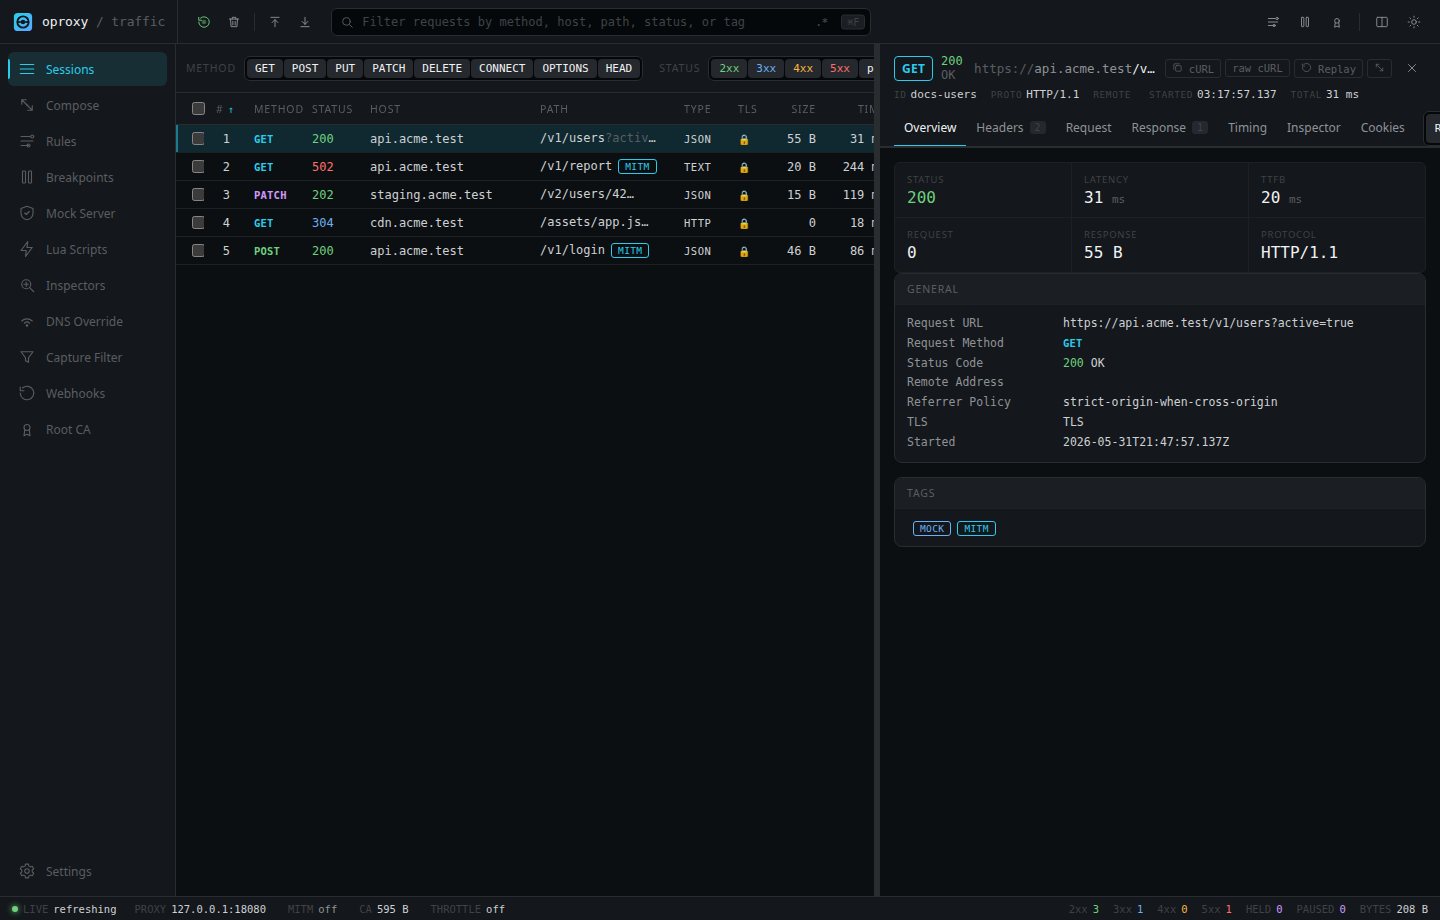 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
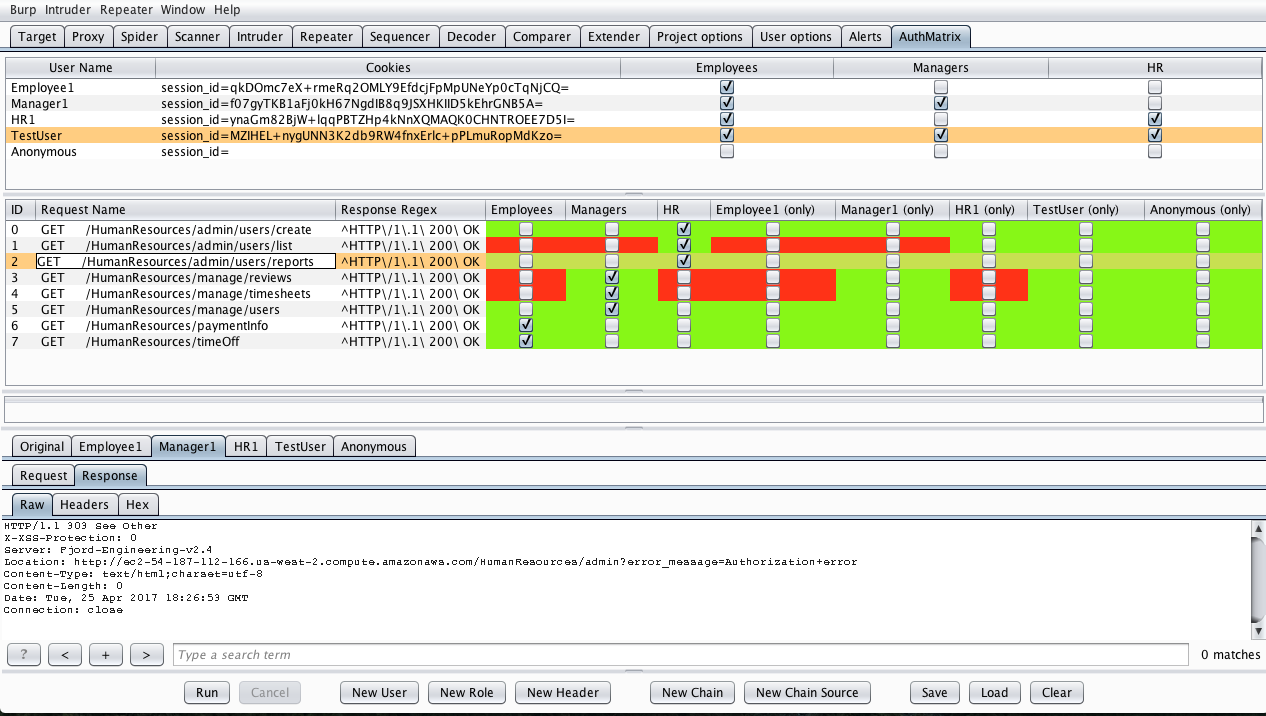 securityinnovation/authmatrix
AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
 mayank-s16/swagger-html-injection-cve-2025-8191
XSS Test Swagger 3.14.1 to 3.37.0
 papamica/waf-checker
Tests your WAF with +160 payloads
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite